Introducing the largest bug bounty in history 🦄
We're rewarding up to $15.5M to anyone that finds a critical vulnerability in v4 core contracts
Find a critical bug, become a millionaire 👀
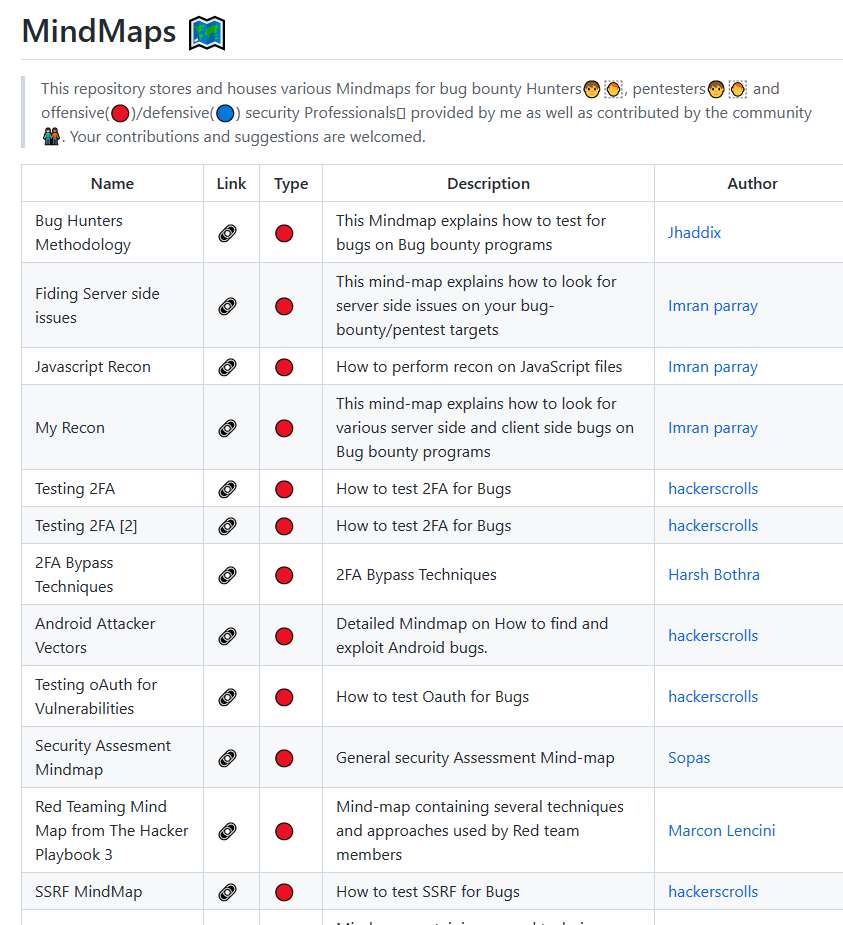
If you are preparing or want to prepare for the OSCP certification, I have a great cheat sheet suggestion❗️☺️ You should definitely add it to your bookmarks.🤞🏻🌸
Credit: @nullshock1🌟🙌🏻
Repo: https://t.co/bGgQW44j6b
#cybersecurity#offensivesecurity#oscp#offsec#tryharder
OS Command Injection 🕸️🔖
Allows an attacker to execute arbitrary operating system (OS) commands on the server that is running an application
leads to fully compromising the application and all its data.
Thread 🧵 : 👇
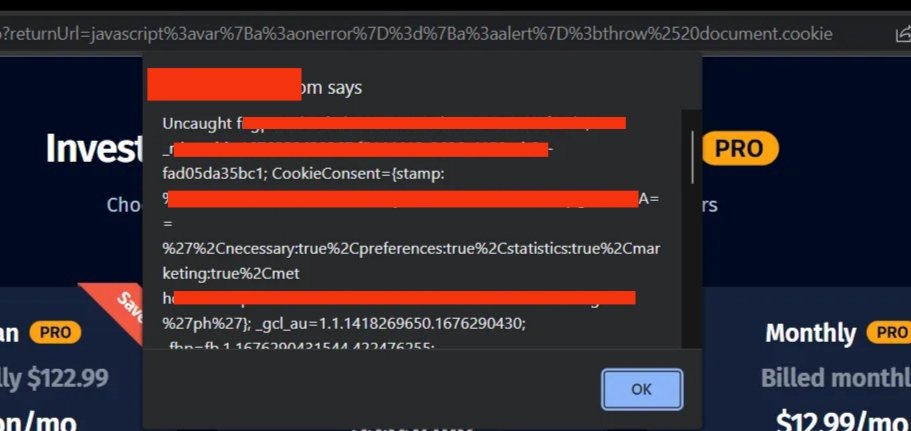
[Bypass Cloudflare] Open Redirect to XSS
Open Redirect
/login?redirectUrl=//evil,org --> redirect to evil,org
Escalate to XSS
/login?redirectUrl=javascript:alert(1) --> blocked by WAF
[1/2]
#bugbountytip#bugbountytips#infosec#BugBounty
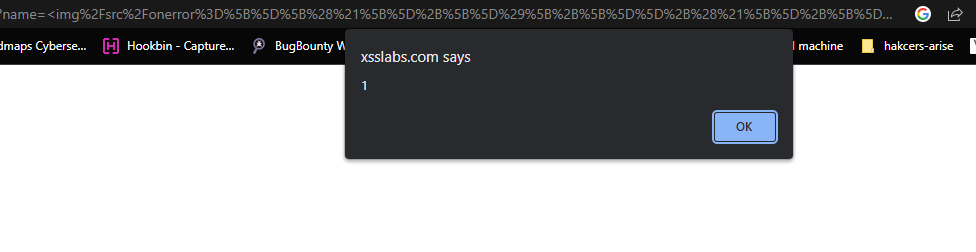
Use These Instead Of Alert and Prompt
In XSS Payload
Example : alert(1) can be encoded as
This leads to bypass waf or blacklisted words at input field
Check Out Below:👇
Time for another giveaway!
We are going to send a t-shirt and a few goodies to one person who follows @PentesterLab and retweets this tweet!!
And we are going to give a 12-month voucher to someone who follows @PentesterLab and likes this tweet!!
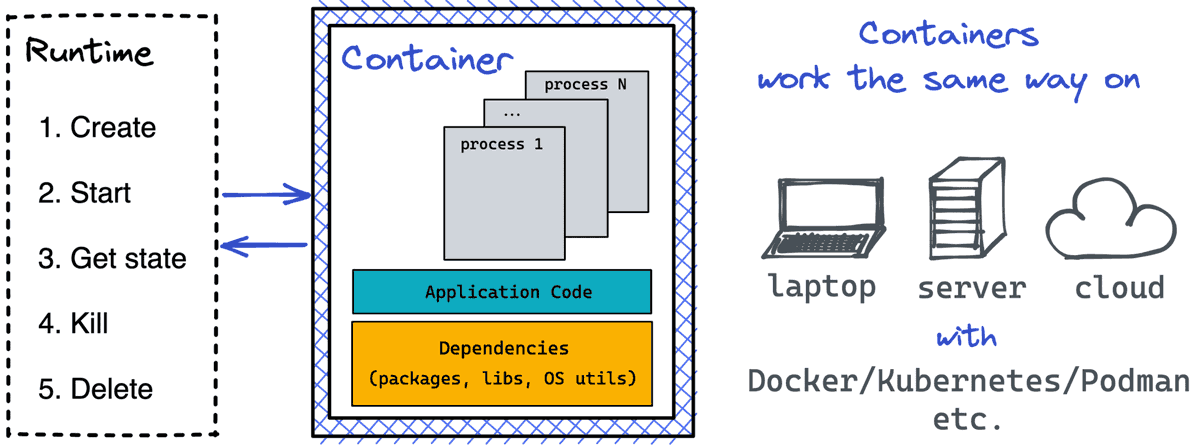
Want to master Docker and become a container expert
...but don't know how to even start? 🔽
Here is the learning order that helped me:
1. Containers: how Linux does them
2. Images: why they are needed
3. Managers: many containers, one host
4. Orchestrators: many hosts, one app
12 #bugbountytips you NEED to know about! 🧵
A #bugbountytip is a short trick that can help you find your next bug!
Here are some quick wins you can start implementing today to become a better hunter 👇
Time for another giveaway!
We are going to send a t-shirt and a few goodies to one person who follows
@PentesterLab and retweets this tweet!!
And we are going to give a 12-month voucher to someone who follows
@PentesterLab and likes this tweet!!