We can contain an AI just fine. Sandboxes are effective. Defense in depth works even better, but as you can see we already have a phrase for that.
If you “need” harness training as root with internet access to match most user flows…
The product team is the threat, actually.
I've written the last Claude Code plugin you'll ever need.
Agent teams in Claude Code are powerful, but difficult to use, and honestly a bit undercooked.
Repeated execution iterations lead to significantly higher quality outputs. Agent Teams are well-suited to exploit this
@thdxr Void Crew on Steam is this - u specialize in 1 of 4 roles that each get chaotic af when it comes to fighting the AI but roguelike makes up for lack of PvP imo
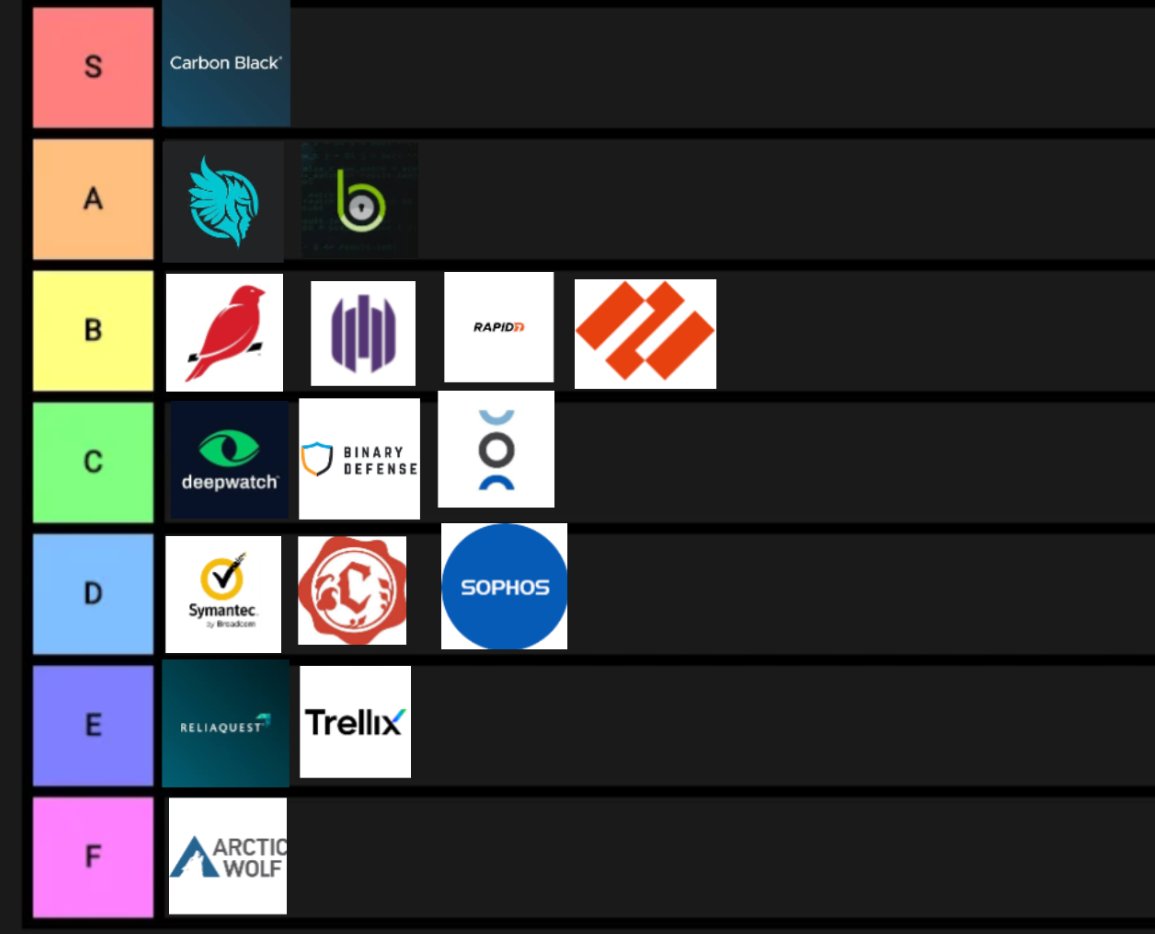
ReliaQuest is proud to announce a new funding round of over $500 million, bringing the company’s valuation to $3.4 billion. This investment will fuel continued innovation in our industry-leading Agentic AI-powered cybersecurity platform, GreyMatter, for more security teams around the world.
“Everything we have done at ReliaQuest has always been driven by the problem we solve for our customers. Enterprise security teams have more data in more places than ever before, and the speed of the threat is rapidly increasing. CISOs need a way to contain threats within minutes without added cost or technical overhead, leveraging the latest innovations in Agentic AI,” said ReliaQuest Founder and CEO Brian Murphy. This new investment is a key step along our growth trajectory as a company, but most importantly it will allow us to deliver better security outcomes for even more CISOs around the world.”
This new funding round is led by EQT, KKR and FTV Capital, with participation from other existing investors Ten Eleven Ventures and Finback Investment Partners.
Read more here: https://t.co/RPVHSX14DA
@UK_Daniel_Card keep it up, always helps to drive tool innovation forward!! If you want some more comparisons to draw inspiration from, OpenCTI has some sick graphs like this with enrichment
Asked about my thoughts on Vibe coding and CHOPs. Back in 2018, I was telling people in the serverless world to get ready for conversational programming, so my thoughts are ... this should not come as a surprise. But it will take time to diffuse.
@namazso How would you handle the situation differently?
It’s unfortunate that some legitimate content was unavailable for a short period, but OP took to social media attempting to brigade instead of addressing the root issue
@cyb3rops I’ve seen this trend rising since COVID in almost every SOC ive worked with. Maybe it’s too simplified but either folks care about their own work quality or they don’t. You can teach anyone who cares but it’s a fruitless exercise if they dont, attitude is everything
the people who are always accusing everyone of over complicating things have never done the last 20% of a project
they do the fun stuff and quit before they ship so they don't realize how much complexity exists there
Recently made this point with security team: I/We have exceptional power over our clients in an emergency, literally arbitrary code execution. But the routine must be made to be routine and not require a hero.
@htmx_org Yes, import the lib on a base template and if you use it enough - a base view to support functionality like throwing errors to a toast popup, history management, and other custom addons you come up with
Is there anything more recent that Cuckoo Sandbox & Drakvuf for open source malware sandboxing? Everything new seems to be enterprise focused without ways to run it locally?