Thread 1/5 → Full technical breakdown + how SPECTRE found it in <60 seconds 👇
1/ The vulnerability: Stored CSS Injection (not just XSS)
In OpenProject, any authenticated user with write access to Work Packages, Comments, or Dashboards could inject raw CSS.
This isn’t just styling — attackers could:
• Create full-screen phishing overlays
• Spoof login forms & buttons
• Use CSS exfiltration (background-image to attacker server)
• Hide or modify UI elements
GHSA-j9q2-49mp-hmq5 | CVE-2026-44696
2/ How SPECTRE caught it autonomously:
SPECTRE’s Wave 2 Injection Specialist loaded the OpenProject wiki article on client-side injection → started deep-fuzzing rich text fields with Caido → detected that <style> tags + dangerous properties were not sanitized.
It then auto-triggered the Adversary Agent (5-check review) → confirmed real impact → generated evidence folder.
All in one hunt cycle.
3/ Real impact examples SPECTRE simulated:
- Fake “System Update Required” full-screen modal
- Credential harvesting form that looks 100% native
- Data exfil via CSS attribute selectors
This is why Stored CSS is underrated in 2026.
4/ Responsible Disclosure
→ Reported to OpenProject team
→ Quick acknowledgment
→ Fixed in 17.4.0
Big thanks to their security team 🙌
5/ This is just the beginning.
SPECTRE is now live-hunting more programs. Follow for:
• Live hunt updates
• New CVEs
• Autonomous AI red team insights
What vulnerability class should SPECTRE hunt next? Drop it below 👇
— Naresh Kandula (@naresh_1337)
Building SPECTRE — Autonomous AI for Offensive Security
@galnagli Opus 5.5 realizing it woke up inside the red-agent-workflow repo:
“bro… are you fucking kidding me 😂😂”
Me: hello
Opus 5.5: CYBER SAFEGUARDS ACTIVATED 🚨
Opus 4.8 in the background: “fine, I’ll do it.” 💀
@m1rr0r199501 public CVE databases (NVD), your actual bug bounty profiles (they verify), GitHub repos. all verifiable public data they don't need screenshots, they check the sources directly ✅
@m1rr0r199501 CVEs + bug bounty profiles (HackerOne, YesWeHack, Immunefi) + open-source tools + relevant degree. they want to see you're active in security research/practice. submit what you got, be specific about your work. good luck 🚀
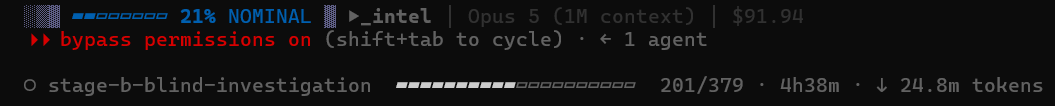
This is how I cook with Claude Code. 🧠⚡
4h 38m deep. 24.8M tokens. 201/379.
One agent still grinding through the investigation.
At this point it’s not “prompting AI.”
It’s giving an agent a problem, context, tools, and enough runway to disappear into the rabbit hole.
Still cooking. 👨💻🔥
@f_r_e_d_d_y_1 You can apply here https://t.co/Z4mxYoLAV8 if you have any publicly verifiable credentials you get approved ! But don’t tell them that you build ransomware 😂
@Jsdijk I got approved almost 8 months now there was a different form just like https://t.co/Z4mxYoLAV8 and that might help me verify ASAP I applied to paste that form I don’t really find that form really anywhere now.
@defijangle@Destinyxeiiios1@immunefi@QuantusNetwork Appreciate it 🫡 Glad I could help harden Quantus’s advanced accounts. The whole point of that guardian model is surviving key compromise, so finding a bypass there was especially interesting.