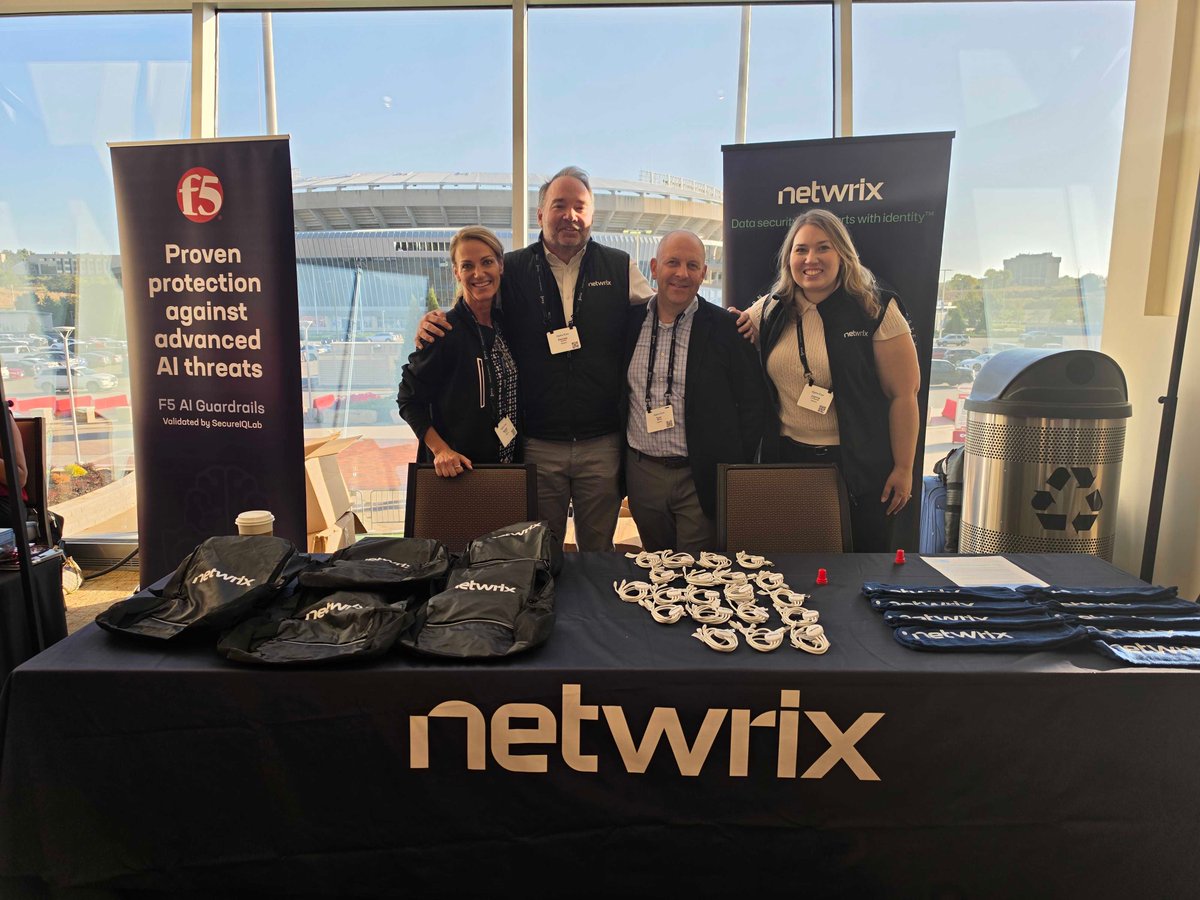
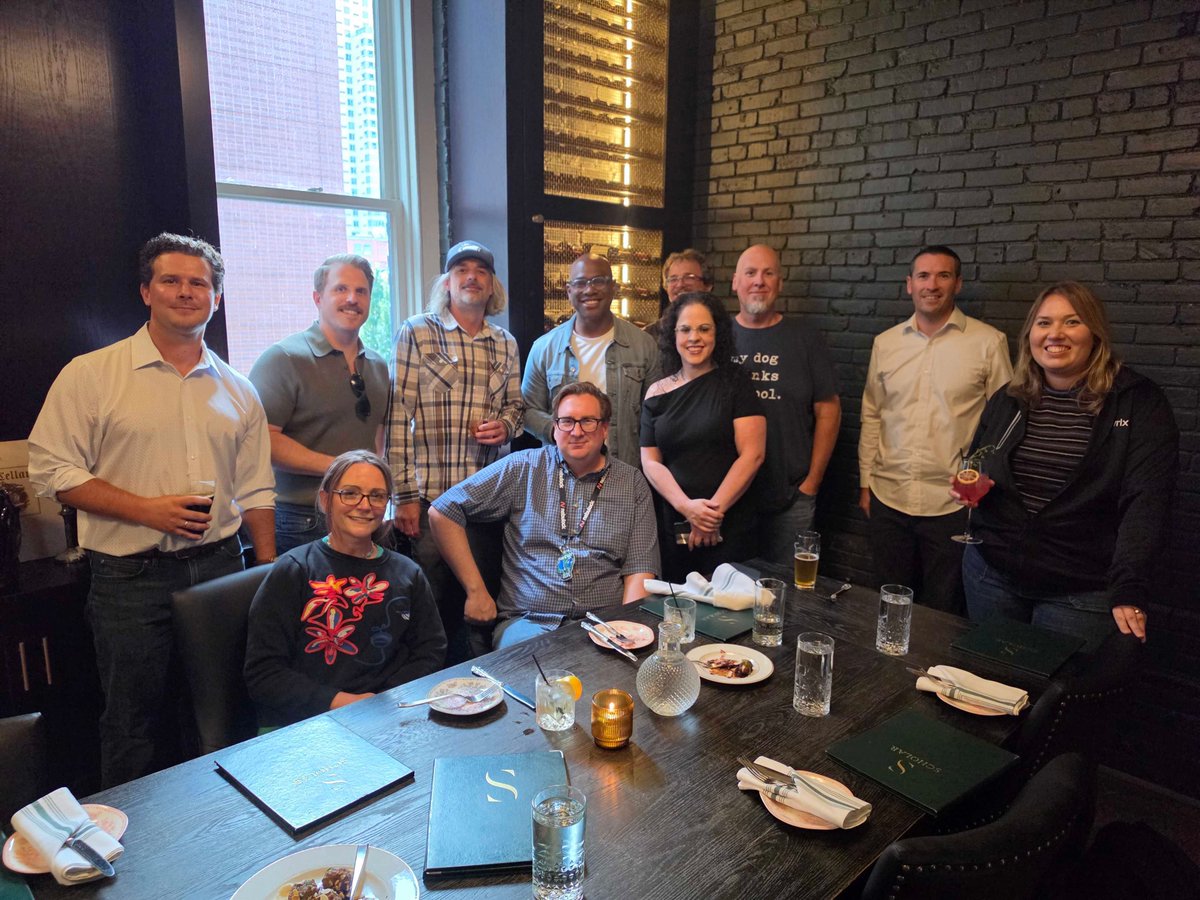
Identity-first security is easy to say and hard to run. That was the thread through Tyler Reese’s fireside chat at OptivCon Kansas City.
Tyler, our VP of Product Management, joined the session on what recent incidents and implementations are teaching security teams, and what identity-first security looks like in practice.
Thank you to @Optiv and everyone who stopped by our booth on Wednesday, Oct. 7, 2026.
If you missed us in Kansas City, reach out to our team.
#Netwrix #OptivCon #IdentitySecurity #DataSecurity
An attacker with domain admin credentials doesn’t look like an attacker. That’s the problem.
Compromised identity is now the leading route to unauthorized access, ahead of misconfigured permissions, per Netwrix's 2026 Data and Identity Security Report. We tested that by paying real attackers to breach a moderately hardened Active Directory. Every attack from standard users and admins was caught. Once an attacker held valid domain admin credentials, every attack got through, because the requests looked exactly like a real admin's.
PAM, IGA, and ITDR each cover a different moment in that attack. Bolted into one console, they're still three separate jobs.
Read the full post: https://t.co/KsWtDFfSAm
#PAM #IGA #ITDR #Netwrix
Innovate Summit Scottsdale wrapped up this week, and Booth #105 at the JW Marriott Scottsdale Camelback Inn gave us three days of them. Security leaders stopped by to talk about reducing cyber risk and protecting critical data.
Thank you to the Innovate organizers for a well-run event, and to everyone who stopped by.
Thanks to the team on the ground: Ryan Goss, Michael Henriks, Collin Bass 🐟, Kent Tuominen, and Tina Shakour, CISSP.
If we missed each other in Scottsdale, send us a message. We’ll pick up where the conversation left off.
#Innovate2026 #Cybersecurity #Netwrix #InfoSec
Day one at Les Assises de la Cybersécurité 2026, and we've had good conversations already with CISOs, CIOs, and security leaders from across banking, government, defence, and energy.
If you're here at the Assises, come find the Netwrix team. We'd love to talk through what's on your roadmap: identity and access management, governance, threat management, data security, or getting ahead of AI-driven risk.
More to come as the week continues. See you on the floor.
Monaco | October 7–10, 2026
Book a meeting with us: https://t.co/tIcfF6dpD7
Pull up a privileged account used in a session yesterday. Is it still there? Does it still hold the same group memberships?
If yes, you have password rotation. You don't have Zero Standing Privilege.
Rotation stops a credential from being reused. It doesn't make the account disappear, and an attacker who finds it doesn't need yesterday's password; they just need the account to still exist and still hold privilege. Per Netwrix's 2026 Data and Identity Security Report, 76% of organizations can't immediately revoke standing access when it's no longer needed, and 64% have overprovisioned access sitting on critical data right now.
Zero Standing Privilege asks a different question: why should the account exist when nobody's using it? With ephemeral accounts, access is created for a task and [disabled/deleted — confirm] the moment it ends.
Read the full blog: https://t.co/YQuNBhiNTZ
#ZeroStandingPrivilege #PasswordRotation #Netwrix
System prompt files, model configs, and safety filter rulesets are just files sitting on a server. They're every bit as exposed as any other config, with more consequential outcomes if tampered with.
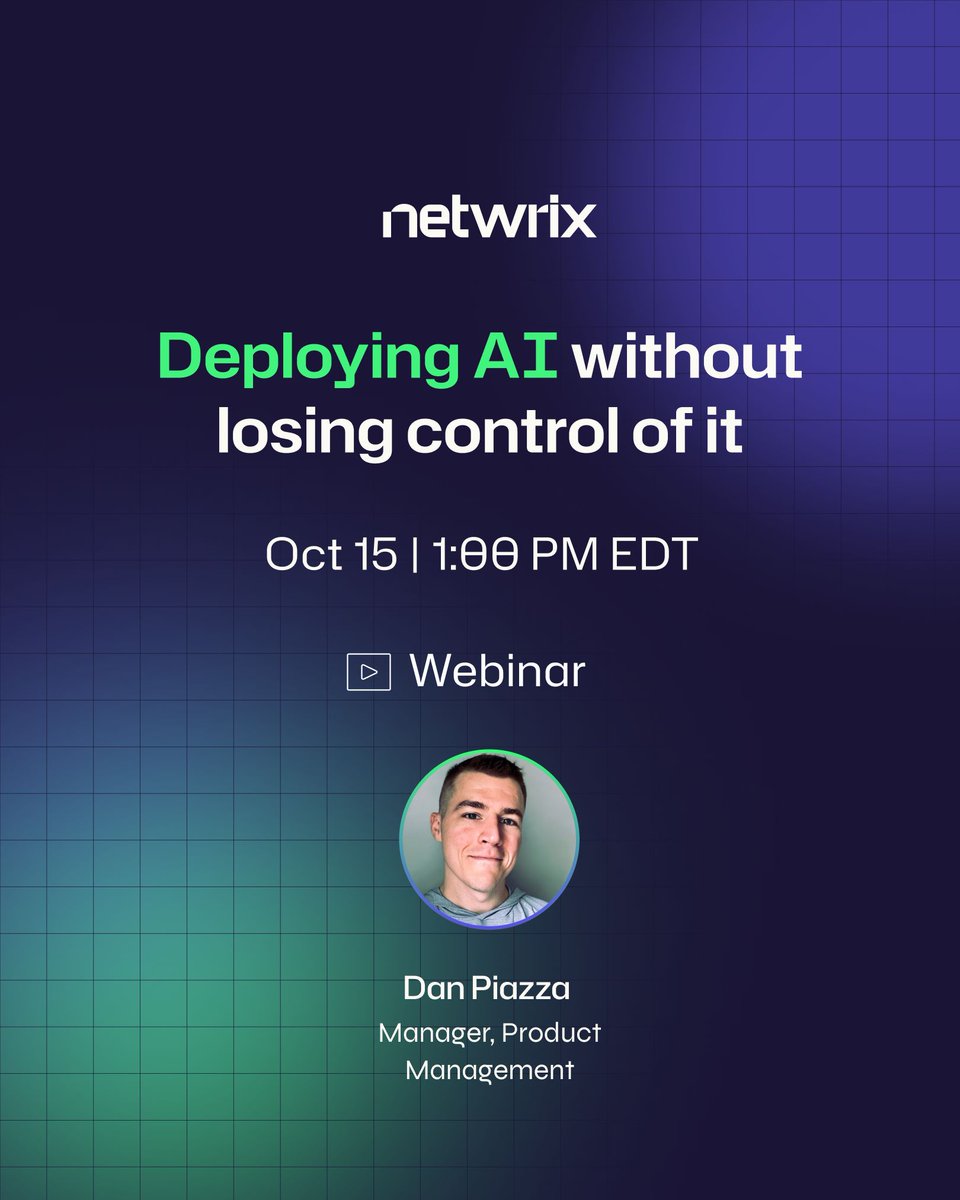
Join Dan Piazza, Product Management, at Netwrix on October 15 to see how Netwrix Change Tracker brings file integrity monitoring, CIS-aligned hardening, and closed-loop change control to the configuration layer underneath your AI deployment, so you can tell a scheduled update from an unauthorized one.
Thursday, October 15 | 1:00 PM ET
Reserve your spot: https://t.co/rWUB7zEDUs
Reselling software is getting harder. Reselling proof is not.
For your SMB and mid-market customers, identity security, data security, compliance, and AI readiness have collapsed into a single conversation, and most can't prove who has access to what, what changed, or whether their controls work.
Join Ed Baker, Ryan Oistacher, and Eleonora Liapina for a sales-focused session that's deliberately not a product briefing. It's the business case: where the revenue is, the fastest route to a first opportunity, and three ways to sell one platform.
Wednesday, October 14 | 2:30 PM CEST
Reserve your spot: https://t.co/vgLNpJ0WK6
Two days. One clear signal: AI adoption is outpacing identity hygiene, and most teams are just starting to catch up.
That's a wrap on Cyber Security World Asia 2026 at Sands Expo, Singapore. Thank you to everyone who stopped by booth.
Missed us? Visit https://t.co/XGx8vOcRWO to learn more
#CSWAsia2026 #CyberSecurityWorldAsia #IdentitySecurity
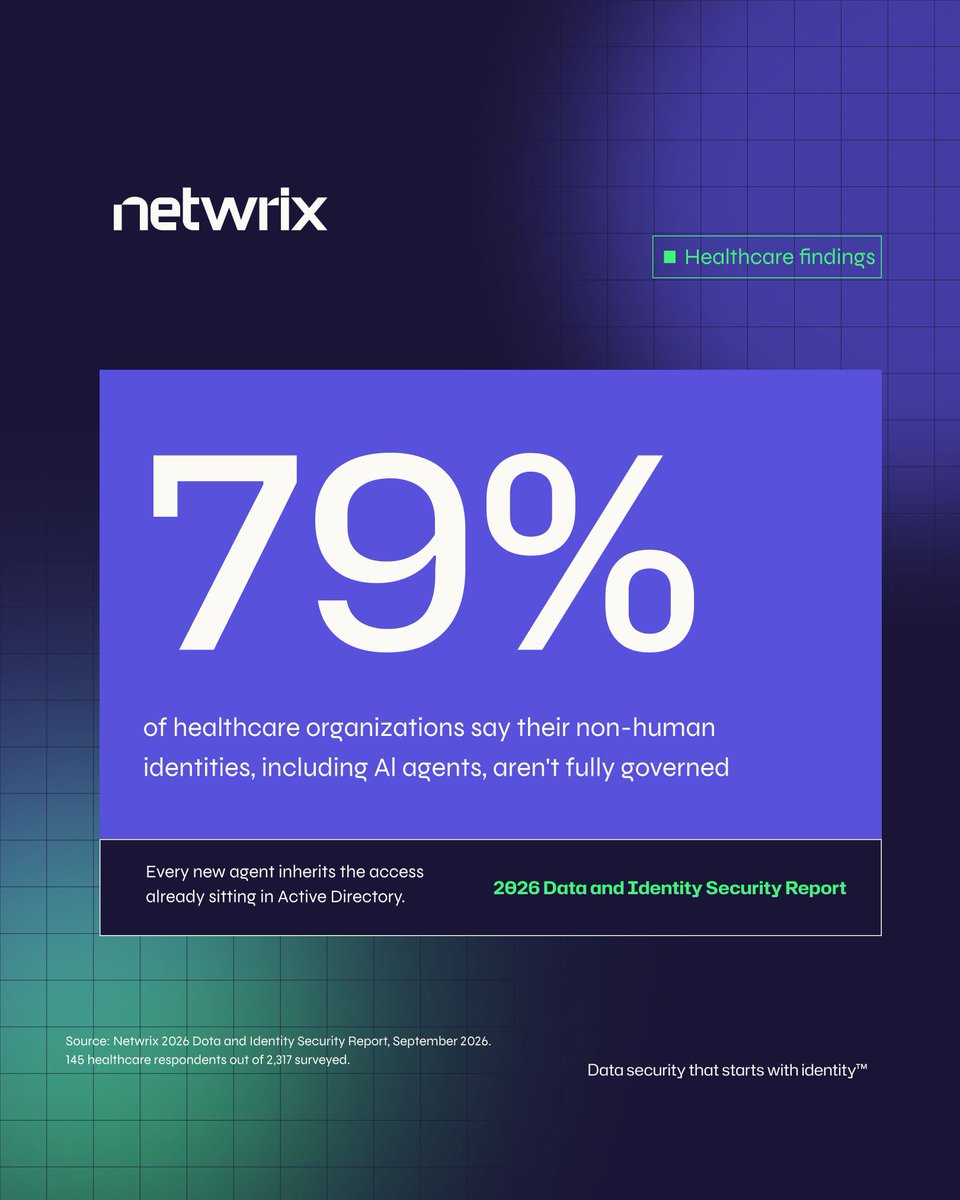
Healthcare AI agents inherit whatever access already accumulated in Active Directory, not the access anyone meant to give them.
That gap shows up in the numbers: 79% of healthcare organizations say their non-human identities, including AI agents, aren't fully governed. Healthcare ranks lowest of 16 industries in confidence that its Active Directory is free of privilege escalation risk, with 86% lacking full confidence. Among those that experienced an incident, 33% put the cost above $250,000.
Darryl Baker, Senior Staff Security Researcher at Netwrix, explains what healthcare organizations need to understand about existing access before adding more AI agents and non-human identities.
Read the full press release: https://t.co/qpM37BUFh1
#DataSecurity #IdentitySecurity #ActiveDirectory #Netwrix
A written AI policy doesn't stop shadow AI. A technical control does.
Only 20% of organizations say they fully monitor or govern employee use of shadow AI, according to Netwrix's 2026 Data and Identity Security Report. The rest are relying on policy while employees download AI writing assistants, browser extensions, and executables IT never reviewed.
Dirk Schrader, VP of Security Research at Netwrix, explains why AppLocker can't keep pace with AI tool sprawl, and how file-owner-based allowlisting flips the question from "what's on the list" to "who put this file here."
Read the full blog: https://t.co/qbFrTnFe4e
#Netwrix #AIPolicy #ShadowAI #DataSecurity #IdentitySecurity
Thanks to the GrrCon organizers for putting together a solid few days of straight talk on identity, data security, and where AI is changing the risk conversation.
Thanks also to Guidepoint Security and SynerComm for hosting the Happy Hours, good spaces for the kind of conversations that don't happen on a show floor.
Thanks to our team on the ground this week: Joanna L., Michael J. Annechino, and Jeffrey Forsyth.
#Netwrix #GrrCon
An attacker mining SharePoint for sensitive files and Microsoft 365 Copilot answering an employee's question trigger the exact same detection signature. Same behavior, same telemetry, no way to tell them apart.
James Anderson, Technical Product Manager at Netwrix, breaks down why the MITRE ATT&CK technique for adversaries mining SharePoint now describes what Copilot does dozens of times a day. He also gets into why most security teams already quietly stopped detecting for it, without deciding to.
Read the full blog: https://t.co/9YtgpXrAL0
#Netwrix #MitreAttack #InsiderThreatDetection
Regulators aren't asking if you're ready for NIS2 anymore. They want proof.
The compliance deadline passed in October 2024. If your organization operates in energy, transport, finance, health, digital infrastructure, or any other critical sector the directive covers, that shift already applies to you. Article 21 asks you to prove who has access, what they did with it, and whether you'd notice if something went wrong.
Daniel Bago, Product Marketing Manager at Netwrix, walks through nine Netwrix Auditor reports that map your access surface and track behavior once permissions are granted. The same reports also prove what changed, following the same logic an auditor, or an attacker, would use.
Read the full blog 👉🏼 https://t.co/43ohTC49BF
#Netwrix #NIS2 #NetwrixAuditor #9NetwrixAuditorReport #NIS2Compliance
Today's the last day of JNUC 2026 in Kansas City, and our team has spent the week connecting with Apple admins, IT leaders, and security professionals across the community.
If you're at JNUC today, come find us at the Netwrix booth before we wrap up. We're showing how we help organizations protect critical data, secure identities, and get greater visibility across their environments, including Data Loss Prevention and Device Control built for macOS.
Come say hello, grab some swag, and talk security before the show closes.
#Netwrix #JNUC #DataSecurity #IdentitySecurity
DLL hijacking isn't new. The way AI plugins are reintroducing it is.
When a team bolts an AI plugin onto a legacy app that loads its DLLs by name instead of by full path, they add new folders Windows will search when it looks for that DLL. That's a new opportunity for an attacker to plant a malicious file that inherits the app's privileges. No new exploit required. Just a familiar weakness in a newer place.
Dirk Schrader, VP of Security Research at Netwrix, explains how it works, how to detect it, and what stops it at the endpoint.
Read the full blog: https://t.co/xbgupKowca
#DLLHijacking #DataSecurity #IdentitySecurity #Netwrix
Two days of hands-on cybersecurity challenges and honest conversations about the threats organizations are actually facing, that's what South Florida ISSA's Conference & Hack the Flag delivered this year.
Representing Netwrix, Soufia Lakhdar and Alex McCoy spent the event connecting with cybersecurity practitioners, students, and ethical hackers on identity security, data security, and the gaps attackers continue to exploit.
Thank you to everyone who stopped by the Netwrix booth, joined the conversation, and took part in our booth bingo giveaway. We had a great time.
#Netwrix #IdentitySecurity #DataSecurity
Netwrix Endpoint Protector picked up 8 G2 badges this fall, including Leader in Data Loss Prevention and Data Security, plus regional leader recognition across Europe, Asia, and India. The 160+ verified reviews point to what practitioners actually rely on: granular USB and device control, content-aware scanning, and protection that holds up across Windows, macOS, and Linux, including offline endpoints.
Thank you to everyone who left a review, and to the Netwrix team who built the product worth reviewing.
Read about the badges: https://t.co/6CUCQmmkYo
#Netwrix #EndpointProtector #G2 #IdentitySecurity #DataSecurity
Exactly. Least privilege for agents shouldn't be an afterthought bolted on once something goes wrong. It needs to be part of how access gets granted in the first place. The tricky part is most organizations don't have visibility into what an agent already has access to, so "least privilege" ends up being aspirational rather than enforced. That's the gap we cover in the report.
AI agents already have real enterprise permissions, and most identity programs still move at the pace of onboarding a new hire.
From the recent Netwrix 2026 Data and Identity Security Report: compromised identities and misconfigured permissions account for 75% of sensitive data exposures. Only one in four organizations can remediate that risk immediately through automation, and just 26% trust their Active Directory environment has no hidden escalation path.
Register for our free webinar on September 15th at 7pm CEST (1pm ET) to see the research behind those numbers and what it takes to keep that gap from becoming your organization's problem.
Darryl Baker, Senior Staff Security Researcher at Netwrix, led the research behind this report and works directly with the identity and AD misconfigurations organizations are struggling to close. Jeff Warren, CPO at Netwrix, will translate that research into how security and IT teams should actually prioritize their governance strategy as AI adoption accelerates.
Register today 👉🏼 https://t.co/iIZYNOh7IW
#Netwrix #DataSecurity #IdentitySecurity
Your DLP isn't missing Windows threats. It's missing Linux, where most developers work.
One in five data breaches involve shadow AI, according to IBM's Cost of a Data Breach Report, and 78.5% of developers work on Linux endpoints, according to Stack Overflow's 2025 Developer Survey, where DLP enforcement is often absent. Engineers can paste source code into ChatGPT, sync proprietary models to personal cloud storage, and transfer files over Bluetooth or NFS mounts, all without a single alert. HIPAA, PCI DSS, GDPR, and CMMC hold organizations accountable regardless of this coverage gap.
Ryan Oistacher, Director of Product Marketing at Netwrix, walks through the seven exfiltration points your DLP likely misses and the controls that catch them.
Read the full blog: https://t.co/gNq1pEswcT
#Netwrix #DataSecurity #IdentitySecurity #DLP
Netwrix will be at JNUC 2026, September 23–25 at the Kansas City Convention Center, showing how Netwrix protects data, secures identities, and safeguards AI on macOS specifically, not as a Windows feature ported over.
Stop by the booth to see:
- DLP for sensitive data, at rest and in motion
- USB Encryption Management
- Granular Airdrop, Bluetooth and Printer controls
- Support for macOS Tahoe and older versions
- Full feature parity with Windows / macOS
If you're part of the Apple admin community and you'll be at JNUC, come find us!
Register 👉🏼 https://t.co/s1A9Bl3Bxd
#Netwrix #JNUC2026 #DataSecurity #IdentitySecurity