Crazy 72 hours in security. Three major incidents dropped back-to-back: eMudhra, PingCAP (TiDB Cloud), and PHP.
Here is the short version of what happened and who got hit.
1. eMudhra (Trusted CA compromise)
eMudhra generated 8 intermediate CA certificates in April 2025 (cross-signed by Sectigo). A bug in their HSM key-wrapping test script created a second set of P-384 keys where the private keys were single-byte numbers under 256. Operators picked the wrong key labels and signed them into real CA certs.
One of the intermediate CA private keys was literally the number 4.
The other seven: 56, 66, 115, 155, 156, 230, 237.
Three weeks later (May 2025), their CRL signatures started failing because the CRL signer was using the real keys instead of the weak ones. Instead of asking why the keys didn't match, someone switched the CRL signer to the weak keys and closed the ticket.
• Browsers are safe: Chrome, Firefox, Apple, and Microsoft already blocked them, and zero rogue certs hit CT logs.
• Servers are not: curl, Python (certifi), Go binaries, and Docker base images don't check CRLs. Update ca-certificates, certifi, and Go (1.27.3 / 1.26.10).
• 10-second check on any server:
curl https://t.co/vhiGLxNhIS
(TLS error = safe. 200 OK = still vulnerable.)
2. PingCAP / TiDB Cloud (10.6 TB breach)
Attackers found GCP and Azure credentials committed inside PingCAP's own repos. They set up a replication feed of TiDB Cloud's production control plane and exported the entire database every 6 hours for 22 straight days. 88 full exports, zero alerts. 200 GB is already out on torrents.
Beyond the 413 private repos and 20.6M customer SQL queries logged from their web SQL Editor, PingCAP engineers were pasting customer secrets into Jira tickets.
Who is affected in the leaked records:
• Live credentials exposed in support tickets:
- Pinterest: AWS keys for their pingcap-logs S3 bucket
- CardX / Silverlake (NPCI-linked env): AWS admin key in a backup log with full access to 258 external S3 buckets
- DeBank: 38 presigned S3 URLs
- An unnamed AI/dev platform: a 314 MB slow-query log attached to a ticket containing 8,027 live customer secrets (an AWS root key, a GitHub admin PAT over 1,701 repos, 7,485 AWS STS tokens, and 192 OpenAI/Anthropic/Gemini keys)
• Tenants with infra metadata, VPC CIDRs, app-server IPs, or contract pricing exposed:
- Tech: Atlassian, Databricks, Airbnb, Baidu, LINE, Nylas, Persona, PatSnap
- E-comm & Travel: https://t.co/C512KFOEq5, Shopee, Flipkart, Mercari, ZOZO, AEON, Delhivery, Klook
- Gaming: Capcom, Square Enix, Konami, Bandai Namco, Cygames, Colopl, DMM
- Finance: PayPay, SoftBank, SBI, SB Payment Service, Fujitsu, TOPPAN, Bank of China, China Life
- Crypto: Bitget (said only public trade logs were on it and they already left), Pionex, DigiPlus, NFTscan, Chainbase
• Developer profiles leaked (from a purchased https://t.co/28tjHqd5Wr table in PingCAP's BigQuery):
- 24,900 personal emails + GitHub/LinkedIn profiles of engineers at Tencent (3,327), Huawei (2,726), ByteDance (2,475), AIG (2,140), Mastercard, Flipkart, and bKash.
If you use TiDB Cloud: rotate your console API keys, DB passwords, and anything you ever pasted into a support ticket.
3. PHP "PHP2Shell" (CVE-2026-109618 & CVE-2026-109619)
Two CVSS 9.2 pre-auth RCEs leaked yesterday ahead of today's 14:00 UTC patch.
Public writeups trace it to a heap Use-After-Free in PHP's native C multipart/form-data session upload-progress handler (ext/session/session.c).
Because C-level multipart parsing runs before line 1 of index.php:
• App auth, Laravel/WordPress middleware, and file_uploads = Off do not stop it.
• Only PHP 8.2–8.5 get official patches today (59% of PHP servers on Shodan are on EOL <= 8.1).
• Until you patch php-fpm: lock php_admin_flag[session.upload_progress.enabled] = off and block unexpected multipart requests at Nginx/Apache/Cloudflare.
@IamKyros69 How the fuck did they not compress their calls through the web stack by default? Not only is gzip a million years old, but it’s been supported in http web servers since Jesus was playing full back for Jerusalem
Two months ago I was fired by Google for creating the Google Workspace CLI. It went viral, hit #1 on Hacker News, gained thousands of GitHub stars and many thousands of actual users in just a couple days.
It was an incredible, confusing journey, from directors and leaders asking what they could learn from the tool to getting grilled by legal about why the Google logo and brand colors are on the Google Workspace GitHub code repositories.
I think the cause was that Workspace and certain leaders (and projects) were afraid of being disrupted. But the fear wasn't specific to my CLI, it was a broader fear in what agents meant for Workspace. Either way, the irony of my termination was the announcement at Google Cloud Next two days before I was fired that an official Workspace CLI was coming.
I want this out there because it is easier for me to explain my story and it is an experience I want to fully own. It's also part of my healing.
Nearly 7 years at Google was an incredible opportunity for me and I was fortunate to have wonderful teammates and a manager that fully supported me through these last few months. Thank you.
Apple just made Docker Desktop optional on Mac.
And it is completely free.
This is apple/container. 26.5k stars no Github.
You can now run Linux containers natively on your Mac without installing Docker Desktop, without a background daemon hogging your RAM, and without paying $21 a month per developer for a commercial license.
Here is what it does:
→ Runs Linux containers as lightweight VMs directly on Apple Silicon using macOS 26 virtualization
→ Fully OCI compatible. Pull any image from Docker Hub, GitHub Container Registry or anywhere else
→ Written in Swift and optimised specifically for Apple Silicon. Faster and lighter than anything Docker Desktop does on Mac
→ Standard container CLI syntax. If you know Docker commands you already know how to use this
→ Push images you build to any standard container registry and run them anywhere
Docker Desktop charges $21 per developer per month for commercial use. Apple's version costs nothing and ships as open source under Apache-2.0.
Microsoft made Docker Desktop optional on Windows with WSL Containers last month.
Apple just did the same on Mac.
Docker is not going anywhere. But the era of paying for a GUI wrapper around containers on your own machine is quietly ending.
Repo here: https://t.co/uFJ867sul6
claude mythos just broke Apple's $2 billion defense system. it did so by discovering a completely different attack vector to break in
only took it 5 days costing ~$35K of mythos api time (the same exploit class costs $5-10M on grey market)
the researchers that commandeered the exploit produced a 55-page report that was delivered to Apple HQ in-person (hoping they release it after patching).
most shocking part for me is apple's MIE worked as intended. mythos just discovered a new way to side-step it entirely by poisoning the data the M5 chip ingested.
at this point i think we have to accept that mythos walks the walk.
As the anthropic red-team explicitly confirmed this week - this is NOT a compute resource issue. its national defense.
Security things from the last few days:
- CopyFail (linux pwn'd)
- CopyFail 2/Dirty Frag
- 13 advisories in Next.js
- Over 70 CVEs addressed in MacOS 26.5
- ~50 CVEs addressed in iOS 26.5
- YellowKey (Windows Bitlocker pwn'd entirely)
- GreenPlasma (Windows privilege escalation)
- CVE-2026-21510 and CVE-2026-21513 confirmed to be used by Russia for Windows RCE
- CVE-2026-32202 separately confirmed to be used by Russia for sensitive document access
- Mini-Shai Hulud (over 300 JS and Python packages compromised via GitHub Action cache poisoning)
- Google confirms they have identified AI-powered exploitation of zero days in an unidentified "open-source, web-based system administration too"
- Canvas (popular LMS used in most schools) pwn'd entirely
- PAN-OS (palo alto networks) pwn'd with a 9.3 severity CVE-2026-0300
Are you scared yet?
𝗕𝗮𝗱 𝗧𝗲𝗮𝗺𝘀 ... NOBODY reminds anyone of the standards.
𝗔𝘃𝗲𝗿𝗮𝗴𝗲 𝗧𝗲𝗮𝗺𝘀 ... COACHES remind the team of the standards.
𝗚𝗼𝗼𝗱 𝗧𝗲𝗮𝗺𝘀 ... PLAYERS remind the team of the standards.
𝗖𝗵𝗮𝗺𝗽𝗶𝗼𝗻𝘀𝗵𝗶𝗽 𝗧𝗲𝗮𝗺𝘀 ... EVERYONE reminds each other of the standards
ODAC Flo Network games is a total money grab. I don’t want to pay a monthly or annual fee. I am willing to pay a per game fee. This is dumb and hurts ODAC sports; cant even support your own teams at Championship time unless its in person.
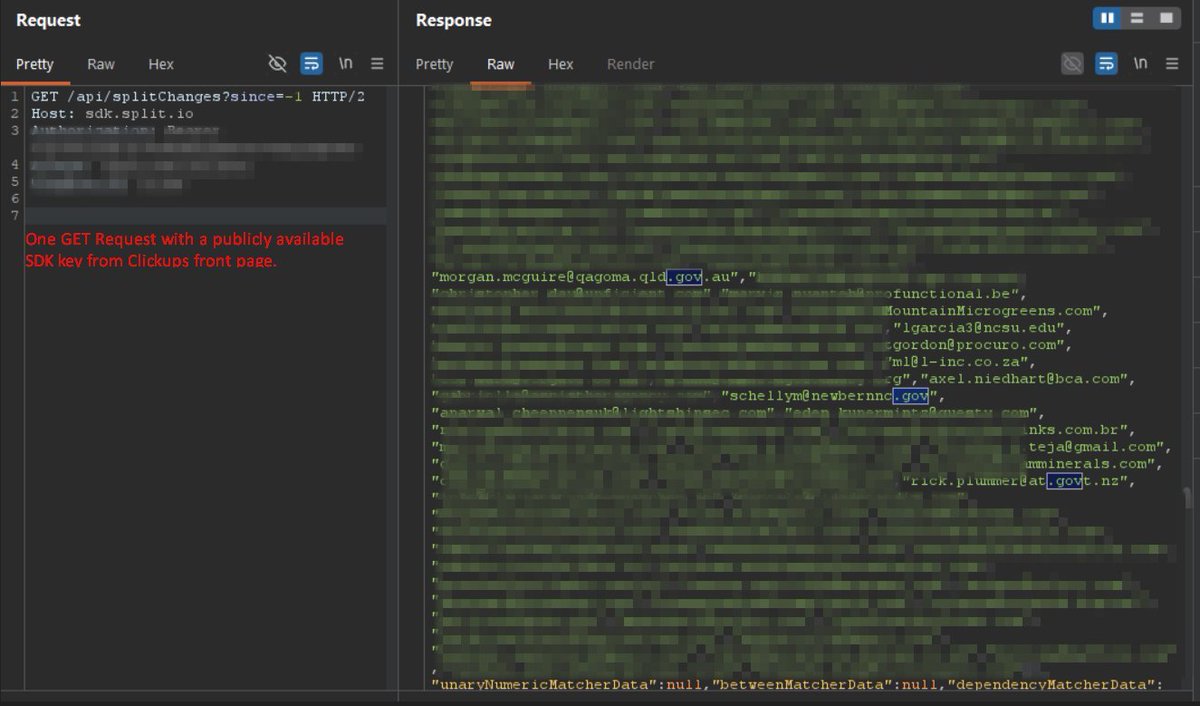
🚨 SaaS platform ClickUp, used by 85% of the Fortune 500, has been leaking customer emails through its homepage for at least 465 days, and counting.
ClickUp has a $4 billion valuation. They are SOC 2 Type 2, ISO 27001, ISO 27017, ISO 27018, ISO 42001, and PCI DSS certified. The fix takes about 90 seconds.
Security researcher @weezerOSINT noticed a hardcoded Split[.]io SDK token sitting in plain text inside ClickUp's production JavaScript bundle. The bundle loads before you log in. View source, copy key, send one unauthenticated GET request, and 4.5MB of ClickUp's internal configuration is exposed: 959 customer emails and 3,165 internal feature flags.
The customer list consists of Home Depot. Fortinet, who sells enterprise firewalls. Tenable, who makes Nessus, the vulnerability scanner half the industry runs on. Autodesk. Rakuten. Mayo Clinic. Permira. Akin Gump. A Microsoft contractor. 71 ClickUp employees. Government workers from Wyoming, Arkansas, North Carolina, Montana, Queensland, and New Zealand.
It gets worse, ClickUp has a flag named "enable-missing-authz-checks." It is active in production. It lists five ClickUp API endpoints the company itself documented as having no authorization. They wrote down their own holes in a config anyone with a browser can read.
At first disclosure, another flag carried a live ClickUp API token tied to Fairfax County Public Schools, one of the largest school districts in the US, serving 180,000 students. The token pulled 1,066 staff records, including Chief Financial Services data. ClickUp removed that one token. They never rotated the SDK key that exposed it.
While that report rotted, the same researcher found a second bug. ClickUp's webhook API has zero SSRF protection. Reported via HackerOne on April 8, 2026. Status: "New." 19 days, zero response.
The original report was filed by @weezerOSINT on January 17, 2025 (!). The key is still live. The emails still drop with one GET. ClickUp has had 465 days to rotate a single token. Zero response...
The fix is one click in the Split[.]io dashboard... ClickUp still hasn't replied to the researcher.
Why is no one talking about this?
@nvidia is offering around 80 AI models via hosted APIs absolutely for free.
You get access to MiniMax M2.7, GLM 5.1, Kimi 2.5, DeepSeek 3.2, GPT-OSS-120B, Sarvam-M etc.
This plugs straight into OpenClaude, OpenCode, Zed IDE, Hermes agent and even with Cursor IDE.
Setup:
– Grab API key: https://t.co/Wfdclm0hY2
– base_url = "https://t.co/VOGC10LmGP"
– api_key = "$NVIDIA_API_KEY"
– select model (e.g. minimaxai/minimax-m2.7)
If you’re building or experimenting, this is basically free inference.
Lock in and start building today anon.
Thank me later.
I've taught European history for 30 years. Americans have always asked me how the Holocaust was possible, how Germans could have enabled a madman reveling in mass murder to carry out his plans. Now we can see in real time how this is enabled; now we have front-row seats.