@database_camp Drizzle catching strays in the ORM obits while quietly building a *decent* business, by being the ORM for people who hate ORMs 😠 @DrizzleORM
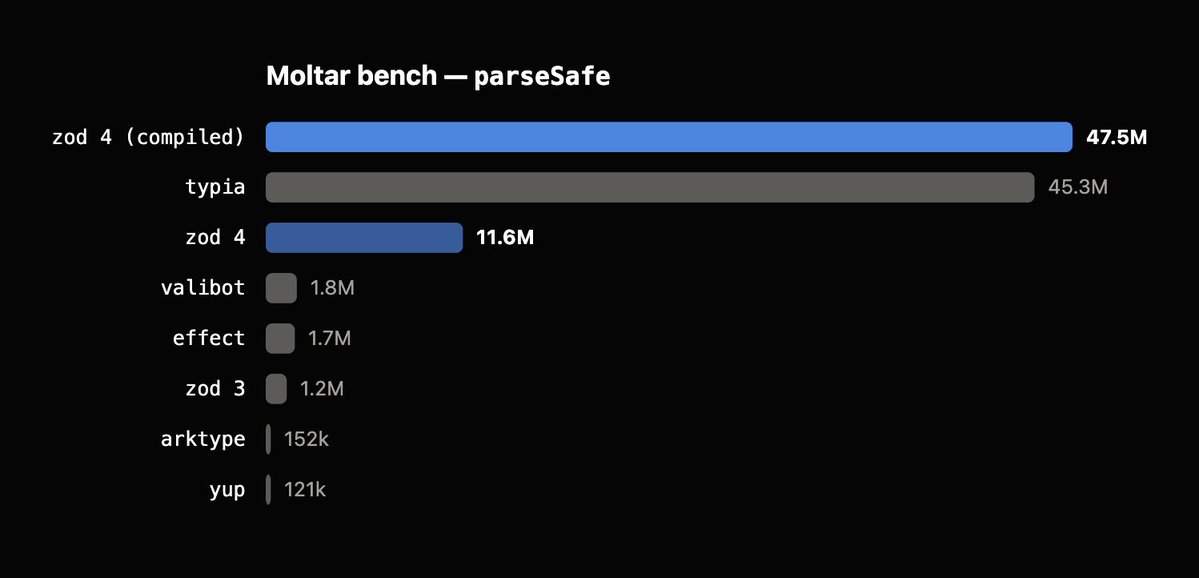
New in Zod 4.6 — .validate()
Unlike .parse(), this method returns a boolean, aborts early when it encounters the first error, and instantiates no issue objects. It is 13-39x faster than `.safeParse().success` on invalid data.
z.compile() walks the schema once at runtime, emits a flat, loop-free new Function() validator for the happy path, and falls back to the normal parser only on failure.
Yesterday, the npm was hit by the third-largest supply chain compromise in its history, a new Shai-Hulud (named for Dune sandworms). Diving into the code we find that—as in Heretics of Dune—the danger is not so much the worm itself as the ecology that has evolved around it:
Yesterday, the npm was hit by the third-largest supply chain compromise in its history, a new Shai-Hulud (named for Dune sandworms). Diving into the code we find that—as in Heretics of Dune—the danger is not so much the worm itself as the ecology that has evolved around it:
🚨 Breaking: 31 npm packages from @RedHat have been compromised.
100,000+ weekly downloads affected. The upstream CI/CD pipeline was compromised, with all packages published via GitHub Actions OIDC.
The payload:
⚠️ Reads GitHub Actions runner process memory to extract masked secrets
⚠️ Sweeps credentials across AWS, GCP, Azure, K8s, Vault, and npm
⚠️ Self-propagating worm that republishes backdoored packages using stolen npm tokens, bypassing 2FA
⚠️ Persists on dev machines via Claude Code settings hijack and VS Code task injection
⚠️ Exfiltrates data through GitHub API commits, blending in with normal git operations
We have responsibly disclosed the incident to the maintainers.
Full technical analysis: https://t.co/63nZYH1cMO