Une société qui oblige une personne de 90 ans à utiliser un smartphone pour accéder à ses droits n'est pas une société moderne. C'est une société qui oublie progressivement ses anciens.
En 2026, tout passe par une application, un mot de passe, un QR code ou une plateforme en ligne.
Pourtant, ceux qui ont bâti ce pays de leurs mains se retrouvent aujourd'hui démunis face à des outils qu'ils n'ont jamais appris à utiliser.
Quand une personne âgée est contrainte de demander de l'aide à son fils, sa fille ou ses petits-enfants simplement pour prendre un rendez-vous, régler une facture ou effectuer une démarche administrative, c'est que quelque chose ne fonctionne plus.
Le progrès n'a de sens que s'il profite à tous. Lorsqu'il exclut les plus fragiles, ce n'est plus un progrès, c'est une régression.
La technologie devrait rendre la vie plus simple, pas transformer l'autonomie en privilège réservé à ceux qui maîtrisent le numérique.
Une société qui laisse ses anciens sur le bord du chemin ne devient pas plus moderne. Elle devient simplement moins humaine.
0-Day Used by Lazarus in #DreamJob Campaign Against Defense Sector:
💥LPE vulnerability in Microsoft’s Afd.sys driver (CVE-2026-68820)
🧰New tools, including #Troy backdoor
🌍Compromised Roundcube servers (CVE-2025-49113) as infrastructure
Read More :
https://t.co/GDI2Ze7CRH
Sample is now on VT!
🚩Hash: 37b485ed8d150d022c41e5e307b8c54c34ef806625b44d0c940b18be7d5b29ce
🎯Actor name: Silver Dragon
🔹Comment: This report details the operations of Silver Dragon, a sophisticated APT group assessed to be Chinese nexus and targets high-profile organizations in Southeast Asia and Europe, with a particular emphasis on government entities. Silver Dragon primarily ga
🌐URL: https://t.co/b2bpazqZlM
🔎OnVT: https://t.co/vzGHwptAav
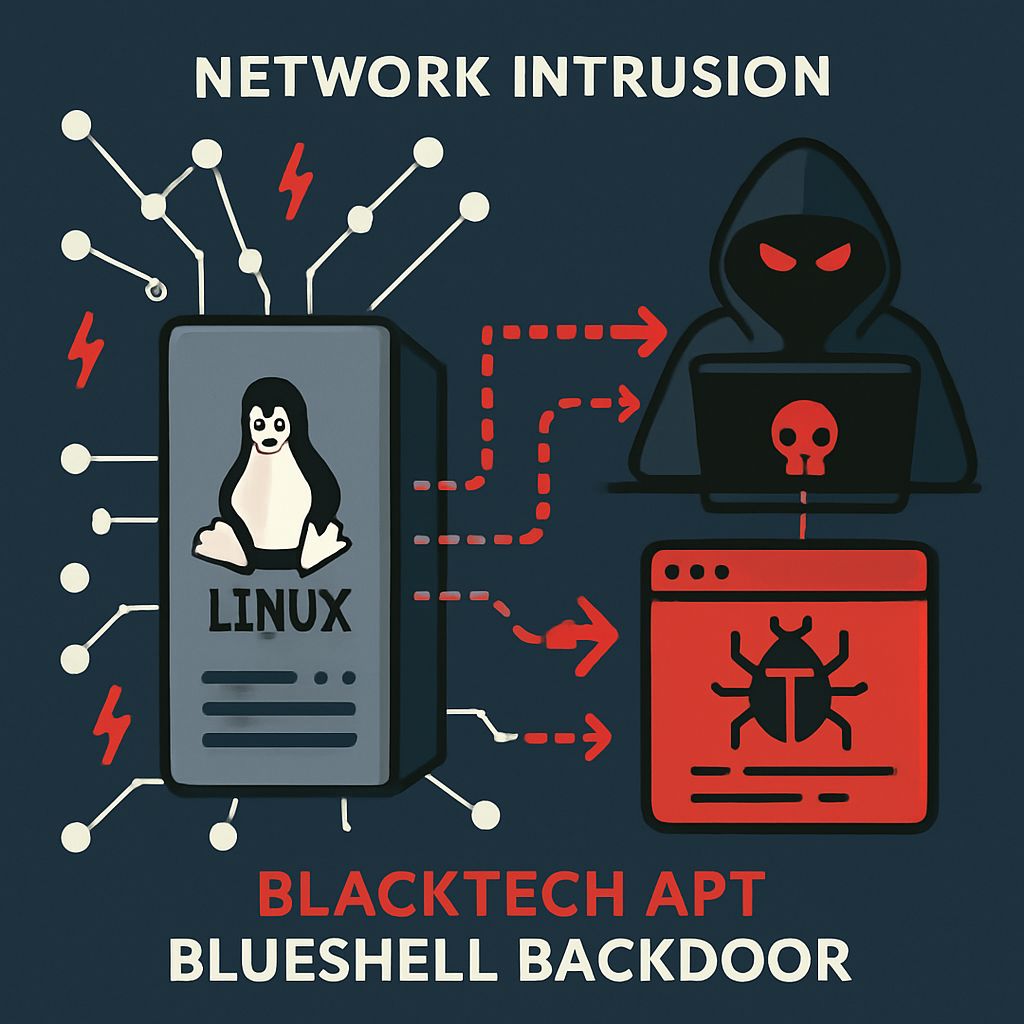
BlackTech APT group has been identified deploying the BlueShell Linux backdoor against Japanese organizations. This malware enables attackers to execute commands, transfer files, and route network traffic within compromised systems, significantly elevating the risk to internal infrastructures and sensitive data. The attack sequence initiates with BlackTech gaining initial access, followed by lateral movement through SSH protocols. Subsequently, they deploy a loader designed to activate the BlueShell backdoor, aligning with their established pattern of seeking stealthy network access. Organizations are advised to monitor for unusual SSH activity, unexpected proxy usage, and anomalous encrypted sessions to counter such sophisticated cyber threats.
#CyberSecurity #APT #LinuxBackdoor #BlackTech #BlueShell #Japan
https://t.co/bcnBAhedH4
Suspicious files uploaded from #India and #Japan, likely associated with an #APT group:
Initial Payloads (MD5):
0574d29601bbc751f2664333288b75a8 3a092bdaa2079ff14c7acb4c72afc6e9
C2:
204[.]194.50.231
Final Payload (Masquerading as PNG):
MD5: dd84762605e60ce9ed16857eca592a6a