Special shoutout to @albinowax 🫡 His protocol research, especially HTTP/1.1 Must Die, sent me down the rabbit hole of parsers and handshakes. Legend. Might be partly responsible for what happened next. 👀 😁
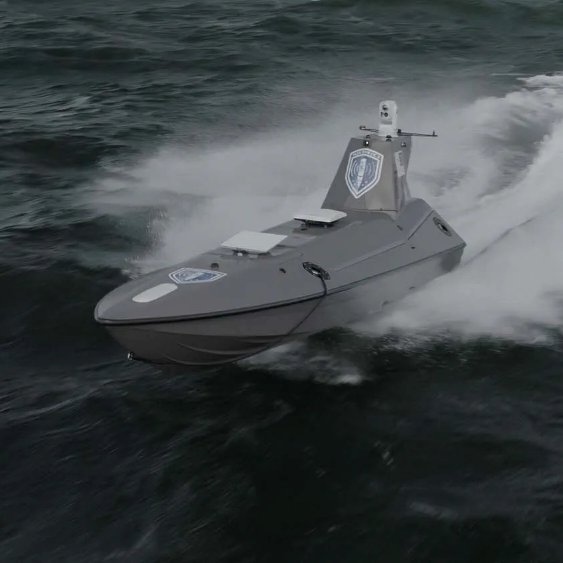
‼️ BREAKING: Cameras on the Royal Navy's K3 Scout sea drones were sending "heartbeat" signals to an IP address in China. The MoD has stripped the cameras of internet connectivity and says no data was accessed.
The £12m K3 Scout fleet has operated with the Royal Marines since March. Supplier Kraken Technology Group says the parts came from a third party and that any vulnerabilities are now closed.
DEF CON 33 - Turning your Active Directory into the attackers C2.
TL;DR: GPOs can turn Active Directory into a powerful C2 primitive. This talk dives into GPO internals, enumeration, persistence, privilege escalation, and advanced exploitation techniques.
I sat down and did some schizo ranting for my attempt at a book I might name "Malware 4 Noobs" (no idea yet).
Here is my introduction segment, part zero (no reforms or changes made yet).
If you're noob, please read and give feedback.
https://t.co/h3p0gVpeRR
@WeirdQuadratic Sorry I didn't knew much about your work. Having done all the hard work and still not getting anything is disheartening, for some parts I get it, kind of on the same boat but, man your skills look amazing, keep moving. Better time is definitely up ahead! 😅
@WeirdQuadratic Maybe having more visibility would help like blogs , technical walkthroughs , new techniques or something that wasn't used like your techniques might be using
Found an Insecure deserialization in 1 of Google OSS and after reporting it got marked duplicate in just 4 mins. The best part is I can't access that report and my bug is dismissed. BB is damn toxic sometimes 😂
The original issue could be very old judging but its tracking id 🤷🏻♂️
Found an Insecure deserialization in 1 of Google OSS and after reporting it got marked duplicate in just 4 mins. The best part is I can't access that report and my bug is dismissed. BB is damn toxic sometimes 😂
The original issue could be very old judging but its tracking id 🤷🏻♂️
> Peter Stokes
> Scattered Spider guy
> Arrested
> Microsoft helps FBI
> Read court documents
> Page 12
> Microsoft tracks Stokes from GDID
> Microsoft Global Device Identifier (GDID)
> Stokes used Windows
> Page 34
> GDID assigned to each OS install
> GDID unique to each device
> GDID only change if OS wiped
> Stokes GDID 6755467234350028
> GDID reported internet activity to Microsoft
> GDID showed Stokes using Ngrok
> GDID reported Stokes IP address
> GDID showed Stokes web activity
> GDID showed timestamps of web activity
> GDID mapped with video game activity
> GDID showed games played
> GDID undocumented
> GDID only mentioned in one MSDN document
> Azure UCDOStatus
> Azure Monitor Logging
Kernel-Exploit-Dojo 📍
Curated archive of 100+ Linux kernel exploitation CTF challenges, organized by bug class, exploitation primitive, final technique, difficulty, and solve count.
The goal is to organize practical kernel pwn techniques such as UAF, heap spraying, pipe_buffer abuse, msg_msg, modprobe_path overwrite, and cred overwrite.
Resource: https://t.co/h1F2CD70Oc
Just rolled out a new portfolio + blog website.
Will try to put the past web vulns chains , ethically hacking and securing different governments, militaries , VDPs and anything "cool" would be updated here. Till then, pls have this cat pic for your time reading this. Thanks!!
> fable has heavy guardrails
> Fable processed my request to find bugs with a little twisted prompt
> Fable gave results in my mentioned format
> Fable has heavy guardrails
Not sure about the "heavy guardrails" lol