Pick the SAST for your open-source repo by where the finding lands. A SARIF upload puts it in the GitHub code scanning tab and on the PR. Our free token for public repos does exactly that. https://t.co/umOWcSs1f6 #OpenSource#GitHubActions
A zip header's uncompressed size is attacker-controlled. Enforce expansion limits on bytes you actually write, canonicalize each entry path against the target dir, and cap entry count and time too. https://t.co/0LQvdPh8IN #SecureCoding#AppSec
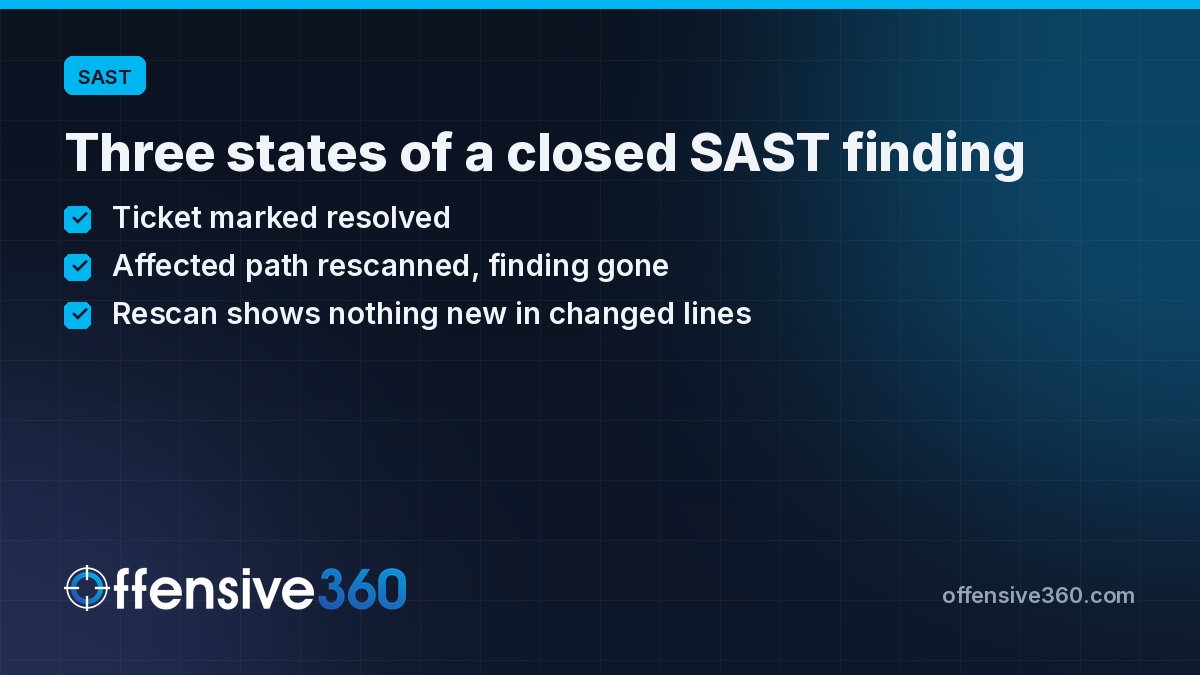
Ticket closed and rescan clean are different states for a SAST finding. Only one is evidence. Evaluation check: apply the fix, rerun on that file, confirm nothing new appeared. Worksheet: https://t.co/AshttveKOR #SAST#AppSec
Your access review lists the humans who can deploy to production. The CI service account that actually deploys is usually missing. Start with who can edit the pipeline config. https://t.co/OHlcfyyJzp #Compliance#AppSec
A control marked implemented and open scanner findings on the same code can both be true. Pick one control: who owns it, which evidence version was reviewed, what is still open? GRC early access. https://t.co/414V7S5XPx #AppSec#DevSecOps
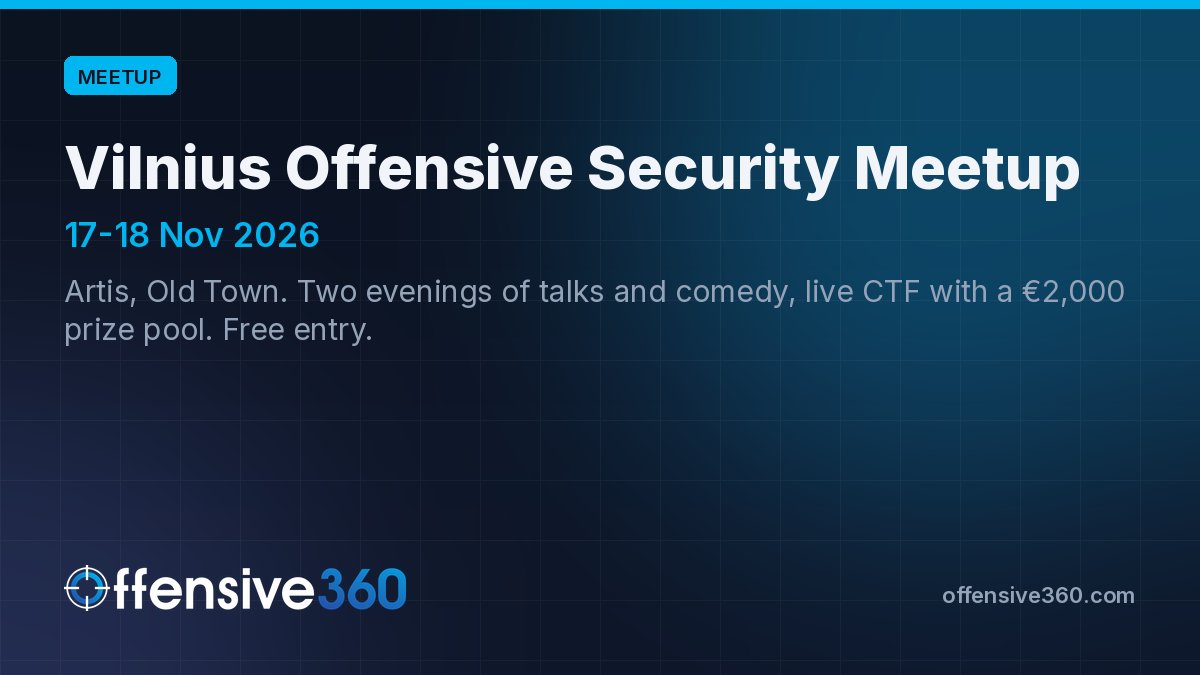
Conference budgets cover two seats. The Vilnius Offensive Security Meetup is free: two evenings of talks and comedy plus a live CTF with a €2,000 prize pool, 17-18 Nov 2026, Artis, Old Town. https://t.co/UdMuI1wuQU #Vilnius#CTF
Your DAST scope lists the hosts someone claimed. The unowned host never gets listed. Our ASM records each external asset with an owner, discovery evidence, last seen, exposed service, next action. https://t.co/E6Zo6jJF3s #AppSec#AttackSurface
CVE-2026-53983: Ground Station <0.6.0, unauthenticated https://t.co/Ur0g7UNJCb path leads to blind SSRF toward internal services and cloud metadata. Check which of your socket handlers skip the auth wrapper. https://t.co/WHs4sQL03X #CVE#AppSec
A finding in a scanner dashboard waits for a login. The same finding in the pull request gets read today. Offensive360 plugs into GitHub Actions, GitLab CI and more. Unlimited scans, flat price. https://t.co/CiKwYtb4WN #DevSecOps#SAST
A vendor risk review for a cloud SAST can run three months. Importing our OVA and finishing the first scan takes under an hour, and the source code never leaves your network.
https://t.co/1K71Ec9Tet #AirGapped#OnPremise
Most CTFs are built so the regulars win. The one at the Vilnius Offensive Security Meetup starts where a first-timer can solve a challenge. Free evening, talks, no vendor pitches. Nov 2026. https://t.co/h90G0ul9gH #Vilnius#CyberSecurityCommunity
Bind parameters protect values, not the ORDER BY clause. The sort column from ?sort= still gets concatenated, and SQL injection survives the fix. Allowlist column names in code.
https://t.co/YIhpAAvmrt #SecureCoding#AppSec
The auditor reading your pentest report skips the finding count and looks for the authorization record. Six days into live CRA reporting, that trail is the evidence. https://t.co/nbjkvBp87c #DORA#Compliance
GL.iNet WebDAV checks auth on GET and PUT, not on COPY and MOVE. CVE-2026-19979, 17 router models, restricted filesystem paths readable remotely. Our write-up on the missed verbs: https://t.co/0Gd2u4SKKm #CVE#VulnerabilityResearch
The endpoint an attacker probes tonight is a live URL behind a proxy with real cookies, not the branch your SAST read. Our DAST crawls the running app and APIs from outside, LLM checks included. https://t.co/VOePP0Mm8G #DAST#AppSec
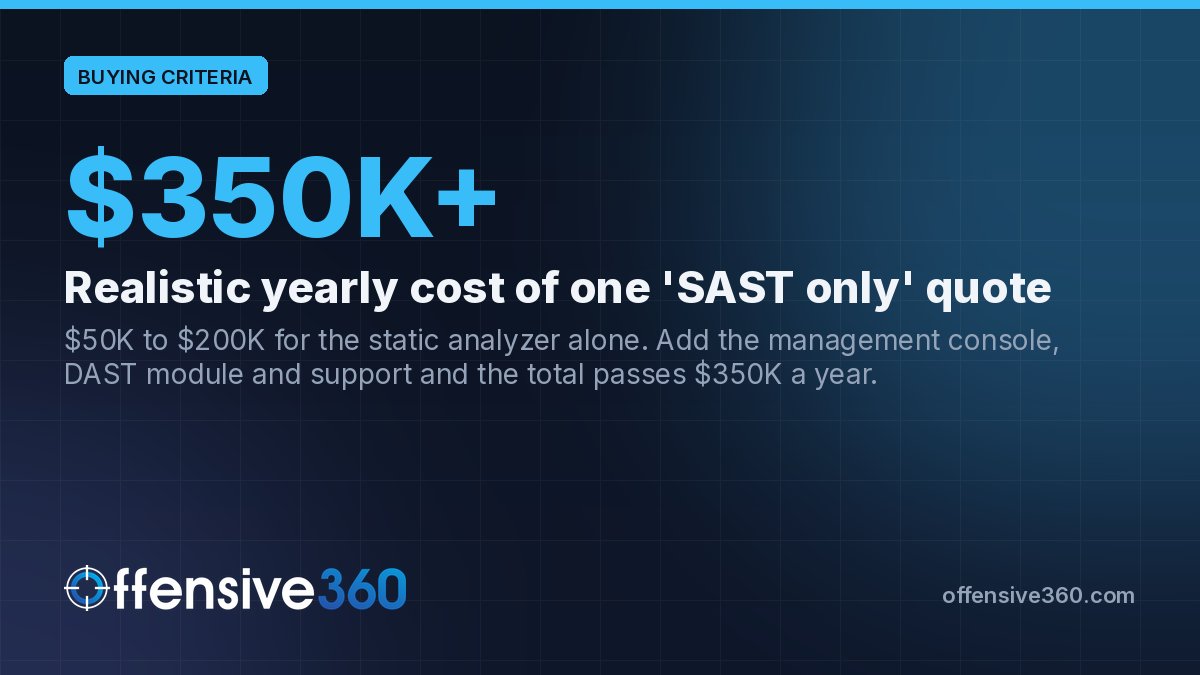
The SAST line on the quote is roughly a third of what you pay by year three. Console, DAST module, support: $50K to $200K becomes $350K+. Ask for the all-in total before comparing features. https://t.co/VBMXoIGVBO #AppSec#CISO
An autonomous pentest with no kill switch is a liability, not a test. Ours: signed authorization gate, human approval before each exploit, DoS force-disabled, on-prem or air-gapped. https://t.co/6UBu0QrsR6 #AppSec#DAST
Tests, linting and builds run free in most OSS repos. Static analysis is the paid step, so it is the missing one. Public repos get free SAST tokens, SARIF into GitHub code scanning. https://t.co/I7ql6nibND #OpenSource#GitHubActions
Wrapping user input in quotes before exec() is not a command injection fix. Pass argv as a list, never a shell string, then reject arguments that start with a dash. Per-language fixes:
https://t.co/0khmkJwfij #SecureCoding#AppSec