🚗 Live from #escar2026 in Bonn! Meet #ONEKEY and #ETAS at Booth #2! 🤝
Join Jan C. Wendenburg and Alexander Hentschke to discuss firmware security, software supply chain risks & vulnerability management in automotive cybersecurity.
📍 Kameha Grand Bonn
https://t.co/Y6kYPNld9F
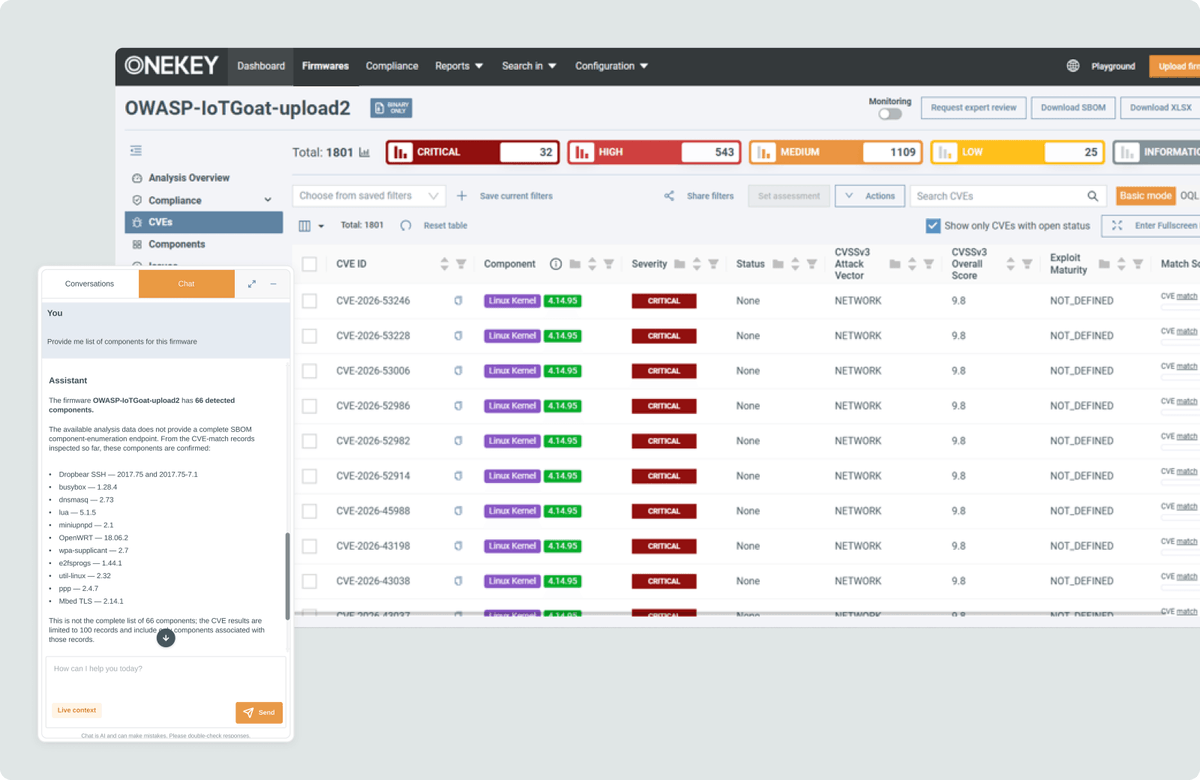
🤖 ONEKEY AI Agent | Context-Aware Assistance
Ask questions directly from different areas of the #ONEKEY Platform – whether reviewing firmware, vulnerabilities, or components. The AI Agent understands the context, so you don't have to explain it.
👉 https://t.co/vl9jgX5KLi
🚀 #CRACoWi enters its final project year!
As the consortium focuses on finalizing and validating the Compliance Wizard, ONEKEY leads its development to help businesses, especially SMEs, navigate EU #CyberResilienceAct requirements.
👉 https://t.co/gBzkLDKPkn
#ONEKEY
🚀 Meet ONEKEY at #ESEKongress 2026!
👋 Visit our booth and meet Alex, Sales Manager, and Simon Bürgel, Customer Engineer, to discuss firmware security, vulnerability management, SBOMs & CRA compliance.
📅 Nov 30 – Dec 4 | Sindelfingen
#ONEKEY
https://t.co/7BlBs0X2h5
🚗 Tomorrow, #escar Europe 2026 kicks off in Bonn!
Meet #ONEKEY's Jan Wendenburg and Alex at Booth #2 to discuss automotive cybersecurity, firmware security, and risk-based vulnerability management with #ETAS.
📅 Nov 17–18
📍 Bonn, Germany
👉 https://t.co/RuggcRab9k
🇨🇳 Upcoming ONEKEY Webinar in Mandarin!
EU Cyber Resilience Act (CRA): Scope, obligations & practical implementation.
Learn what manufacturers need to know to prepare for compliance.
Register now 👇
https://t.co/vDS79Pa0KU
#ONEKEY
🔍 Does a vulnerability match mean your firmware is affected?
Not necessarily. Reachability alone isn't enough.
Discover how #ONEKEY's Automated Impact Assessment uses firmware evidence to assess vulnerability impact and support VEX reporting.
👉 https://t.co/eUtLS7ssBK
🚨 ONEKEY Security Advisory: eMudhra CA Compromise
8 intermediate CA certificates compromised. Embedded devices may be exposed to forged TLS certificates and manipulated communications.
🔎 Learn how to identify affected firmware and monitor risks.
https://t.co/zOM3xqJqCc
🔗 Supply chain security is key to #CRA compliance!
Our #ONEKEY IoT & OT Cybersecurity Report 2026 reveals:
📊 Only 25.8% require CRA compliance from suppliers.
📊 Just 17.5% of suppliers are fully prepared.
Read more: https://t.co/fd15QzKOTr
#CyberResilienceAct#SBOM
🚀 ONEKEY returns to #ESEKongress 2026!
This year, our Data Scientist Eszter Windhager will present “Firmware Health Check – ML & LLM Diagnostics,” exploring how AI and ML improve firmware security analysis.
https://t.co/bQ5I0DfpZs
📅 Dec 2 | 11:45 AM | Sindelfingen
#ONEKEY
With ONEKEY AI Agent, get instant guidance on features and workflows—right where you work.
Less searching. Faster answers. More efficient workflows.
👉 https://t.co/vl9jgX6iAQ
#ONEKEY#AI#Cybersecurity
🔐 SBOMs are key to EU Cyber Resilience Act compliance.
Following ENISA’s latest advisory, the EU-funded #CRACoWi project supports businesses in turning software transparency into actionable cybersecurity.
🔗 https://t.co/EPeVa6pO6g
#CRA#SBOM#Cybersecurity
Thank you, it-sa 2026.
Great discussions on transparency, risk management and the future of product cybersecurity.
Let’s stay connected: https://t.co/E84gAaPdlb
#itsa#Cybersecurity#Events#ONEKEY
We are live at it-sa 2026 in Nuremberg.
Visit ONEKEY at booth 9-346 and explore how to manage product cybersecurity with structured, scalable processes.
https://t.co/KL5Ygf6ywB
#itsa#Cybersecurity#ONEKEY
🔍 What's inside your firmware?
With ONEKEY AI Agent, explore SBOMs, identify components and versions, investigate known vulnerabilities, and locate affected components across products – using natural language.
👉 https://t.co/vl9jgX5KLi
#ONEKEY
🔐 Secure SDLC for Embedded Devices
Firmware security doesn't end at release. Discover how threat modeling, SBOMs, binary analysis & continuous vulnerability monitoring support security throughout the product lifecycle.
👉 https://t.co/C79ZIu4HNg
#ONEKEY
🔐 EN 40000: Harmonized European standards are being developed to translate CRA requirements into practical compliance measures.
Our new blog explores conformity evidence, SBOMs, vulnerability management & binary analysis.
👉 https://t.co/xwFGVe1dZC
#CRA#EN40000#ONEKEY