@mebeim 😂😂
And that was an error from my end.
I wanted to write "that's beyond low"
I got a response while still typing and I was like what is this for lol
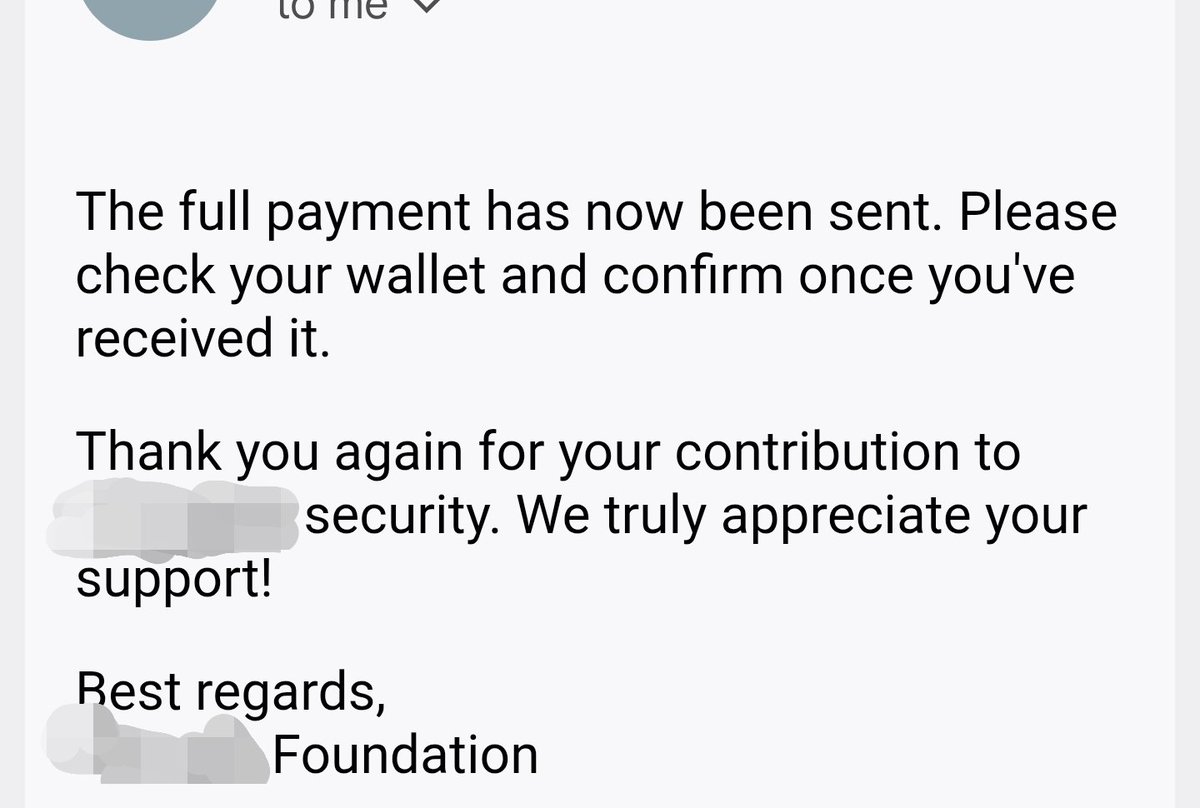
Just got paid $5,000 USDT for two critical bugs.
One unlimited minting bug and another a draining bug.
The bounty amount was disappointing, and negotiations didn't move in my favour this time, but we move 💪
This was a total failure.
I reported about five with one miss.
The affected teams fixed then went silent when I asked for a bounty.
Maybe I reviewed wrong targets, I have long abandoned that idea for now.
Switching gears.
If you receive an email or message on tg from me, just know I found an RCE, please respond quickly and pay fairly for any further cooperation thanks 🙏
@Mudit__Gupta But this class of bug, when found it is very difficult to prove responsibly(Atleast for me).
How would you go about making a poc for a bug like that, when responsibly disclosing it?
@BensonDynasty_ That's a greyhat behaviour in my book. And most programs warn against such actions.
Running a fork test would have accomplished the same thing. That's were real whitehats play with onchain code.
This wasn't on sui network were fork testing isn't a thing yet
@BensonDynasty_ There isn't any reason why that'll be seen as an ethical behaviour.
All testing should always be done against a mainnet fork.
With AI assistance your transaction could easily be picked up, analysed and weaponized in minutes