Introducing OpenHack: the Always on AI Security Engineer, now powered by Claude Mythos.
Until Nov 11, Claude Mythos scanning will be free to help customers find, verify, prioritize and fix urgent vulnerabilities automatically.
https://t.co/tmmNXsz61z
🚨 A race condition in Apache's HTTP/2 module can lead to remote code execution, tracked as CVE-2026-119618 with CVSS 9.8
Full details below:
https://t.co/bIn1h1nn08
🚨 OpenSSH on alpine, openwrt or any musl linux accepts any password longer than 256 characters for the root user since 2016!
Being dubbed sshhole: https://t.co/kNML20Aytt
Introducing OpenHack: the Always on AI Security Engineer, now powered by Claude Mythos.
Until Nov 11, Claude Mythos scanning will be free to help customers find, verify, prioritize and fix urgent vulnerabilities automatically.
https://t.co/tmmNXsz61z
‼️ Node.js has a Remote Code Execution vulnerability.
CVE-2026-111497 is a high-severity bug in its Brotli decoder. Decompressing attacker-controlled data can leak memory or lead to remote code execution.
You don’t need to use Brotli directly. Your app could hit this through fetch() or libraries like body-parser.
OpenHack supply chain tracks this, patch now!
🚨 LiteLLM 1.107.0 was compromised today and shipped with a credential stealer and remote-code loader.
The malicious files were present in the distributed wheels but absent from the corresponding Git tag.
Full breakdown:
https://t.co/5AiUY5HhIj
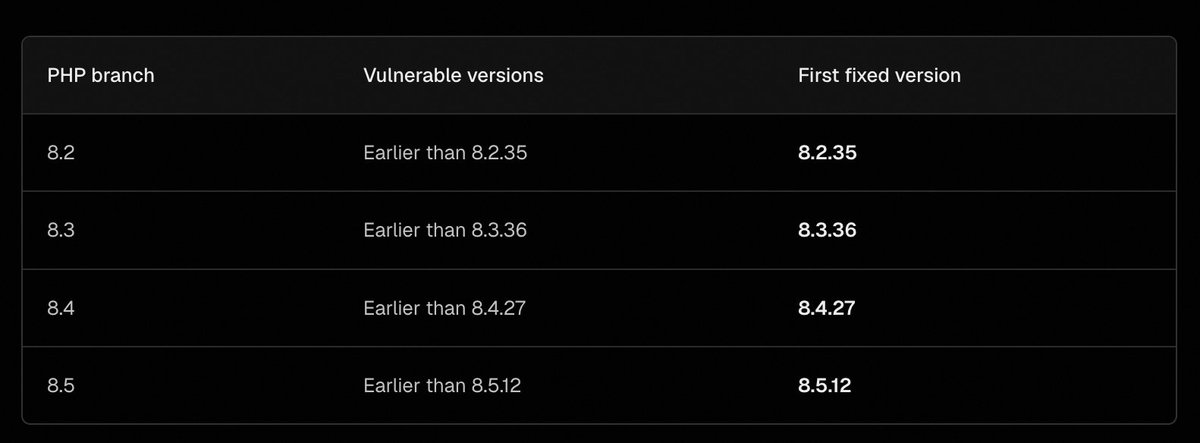
🚨 PHP is going to be dropping emergency security updates tomorrow (October 21st, 14:00 UTC).
- CVE-2026-109618 & CVE-2026-109619 are unauthenticated RCE vulnerabilities both with a score of CVSS 9.2
- The RCE appears to work on default installations of many services & frameworks such as WordPress, Magento, Laravel and more
- PHP versions >5.4.0 affected
- Discovered by team @calif_io
📣 Introducing the all new OpenHack TUI - an open source terminal interface for security tasks, codebase scanning and pentesting.
Connect any model. Scan & auto verify vulnerabilities. Pentest any app. No Guardrails.
Live on https://t.co/x3EJdtORTV
Great chatting with @arinwaichulis from @9to5mac on the Security Bite podcast about the new era of bug hunting, how companies like Apple are handling AI-generated security slop, and how @OpenHack helps separate real vulnerabilities from the noise!
https://t.co/4XCMqhvkKw