I built a vulnerability scanner extension for Burp Suite by @PortSwigger
It scans all http traffic history for: XSS, IDOR, SQLi, & more
Skills-PoC-Finding 🔥
Watch the demo and give it a try👇
https://t.co/xWnYZbActg
Credit: @zack0x01_#bugbountytips#bugbountytip#bugbounty
@TheSecOpsGroup After finding azure creds the next step is cloud environment enumeration to escalate privileges or find the objective. First, query the Azure Instance Metadata Service (IMDS) endpoint or use the Azure CLI (az login or az account show) to identify the compromised identity and scop
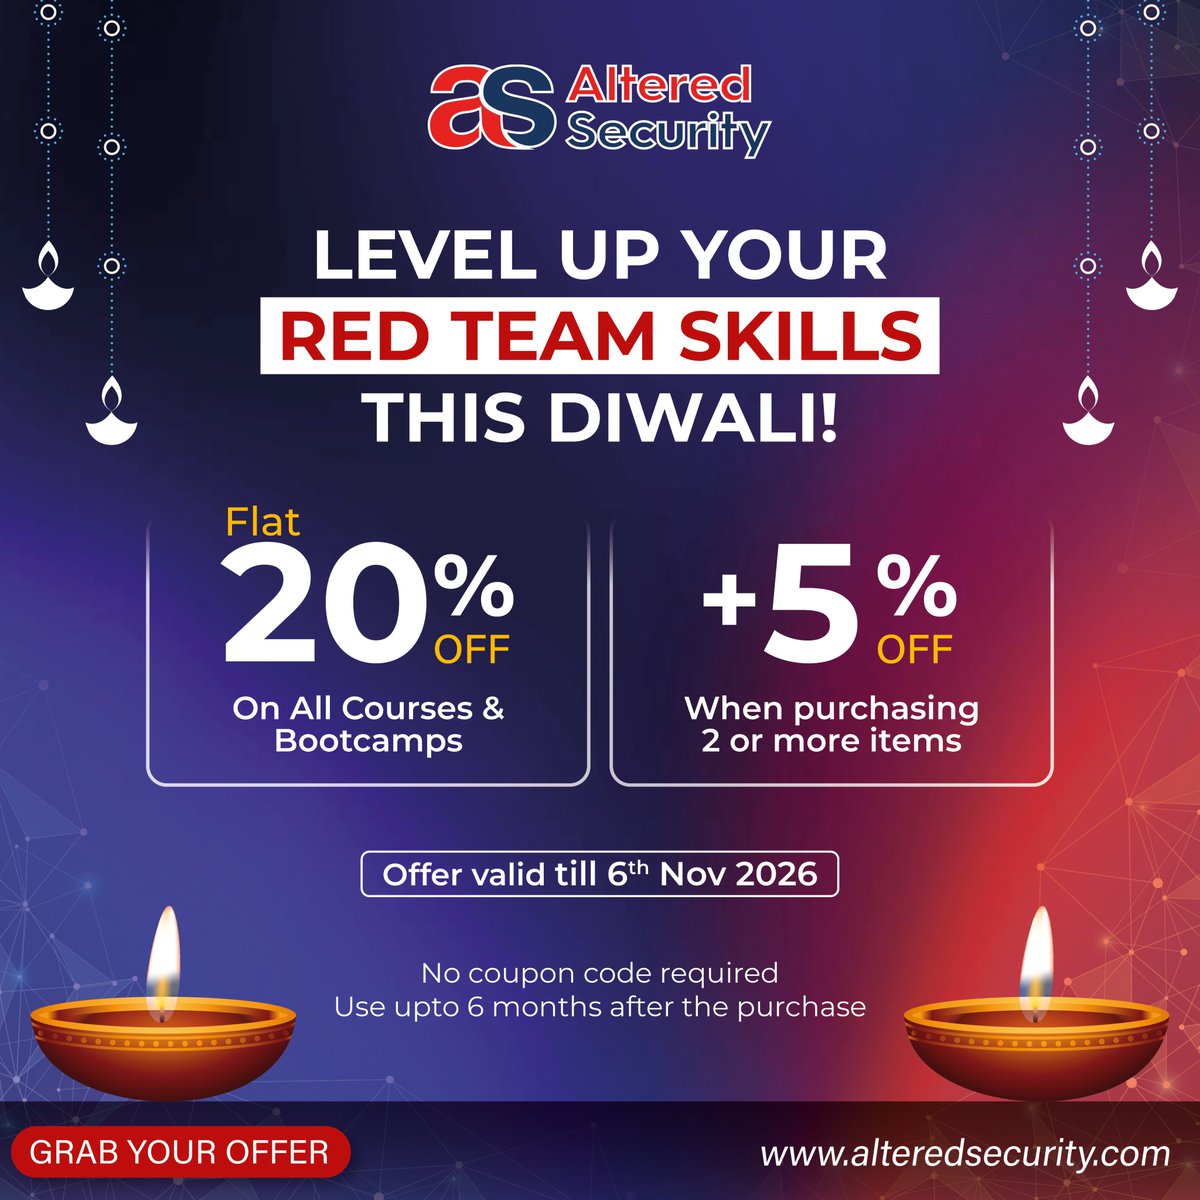
🪔 Diwali 2026 Giveaway! 📣
Win FREE access to:
🎯 1 ACPT seat
🎯 1 CARTP seat
How to participate:
1️⃣ Like and follow @AlteredSecurity.
2️⃣ Comment which course you're interested in and why.
3️⃣ Repost this post.
Winners will be selected at random and announced on 2 November 2026.
Our Diwali offers are also live! Enjoy 20% OFF on all courses and bootcamps, plus an additional 5% OFF when you purchase 2 or more items.
Grab your offer now: https://t.co/hp0GLwrqy7
#Diwali2026 #DiwaliGiveaway #AlteredSecurity #Cybersecurity #RedTeam
$850 CloudFlare Bug Bounty 🤑
When You Get Your MCP Wrong: Second-Order XSS to Cloudflare Access Account Takeover by Nishant 🤯🔥
👨💻 Nishant (x/matured_kazama)
🔗 https://t.co/rAccSrM4tJ
🔗 Join team 👉https://t.co/FeMz53HSN0
Hello everyone,
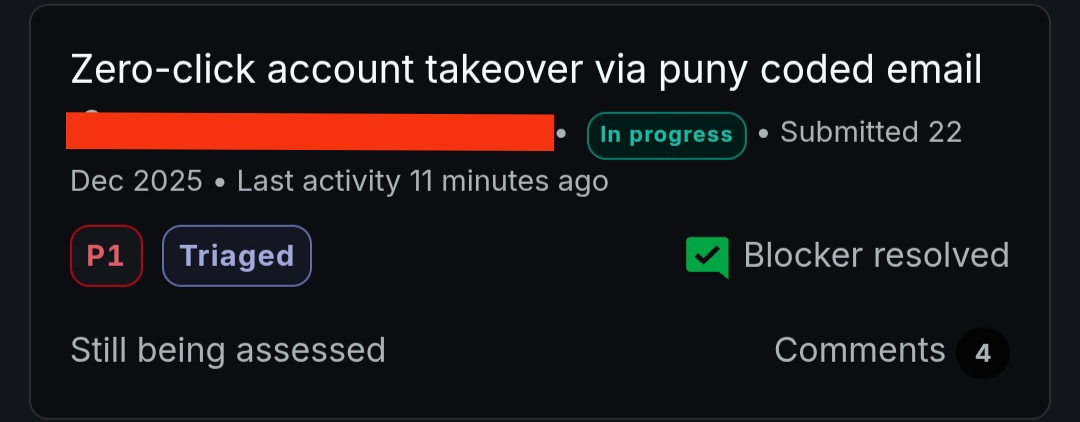
🧵Zero-click account takeover via Punycode email.
One of the most critical and interesting vulnerabilities I’ve discovered recently leads to a full account takeover with zero user interaction.
(1/7)
Found an Jira instance like jira[.]target[.]com, always check for misconfigured Service Desk signup
1. Visit : /servicedesk/customer/user/signup
2. After signup go /secure/jira/projects
If customer-access is misconfigured, you’ll see internal Jira projects
1/2
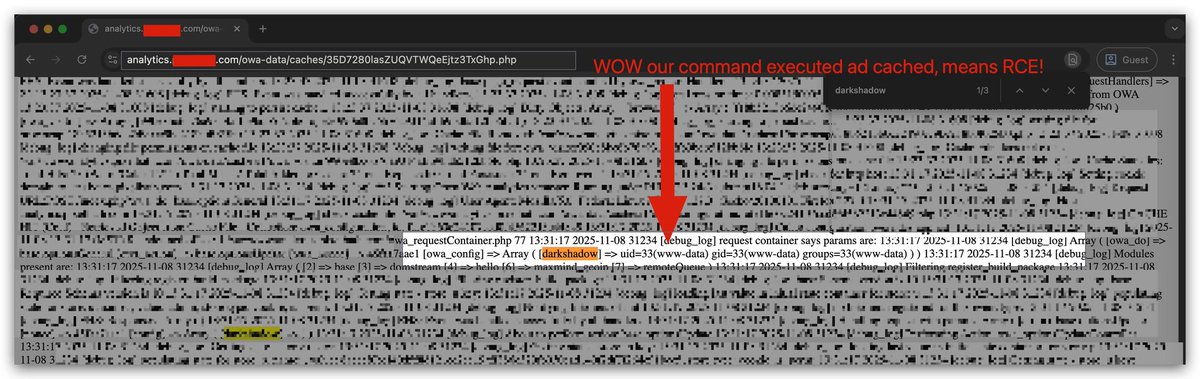
💀Web cache to RCE!😁
While i normally visit the web application i noticed, the website actively makes cache file from clint side to store errors.
Now The idea is, if we able to make any custom error then it will be cached, and if any how the error execute on the system we might see the output.
✅Exploit to reproduce final RCE:
1. The webapp was sending request from client side in a array based parameter.
2. Change the valid Input to a PHP code using system function. Here we just try to making a error using the invalid input.
3. Now the web application is not able to handle this input and makes error and store in a cache file.
4. After visiting the cache file, The error message reflecting on the cache file.
5. But wait, it's also execute my PHP code and store the command output in the file. Means we can execute OS commands output in cache file via making error. Means RCE!
For more Join my BugBounty telegram channel 👉🏼 https://t.co/LeJHHPvGmK