Google Workspace's new Agentic AI terms make customers responsible for what their agents do. A practical start: list every agent with Workspace access, give each a named owner, trim OAuth scopes, and log agent actions separately from human ones.
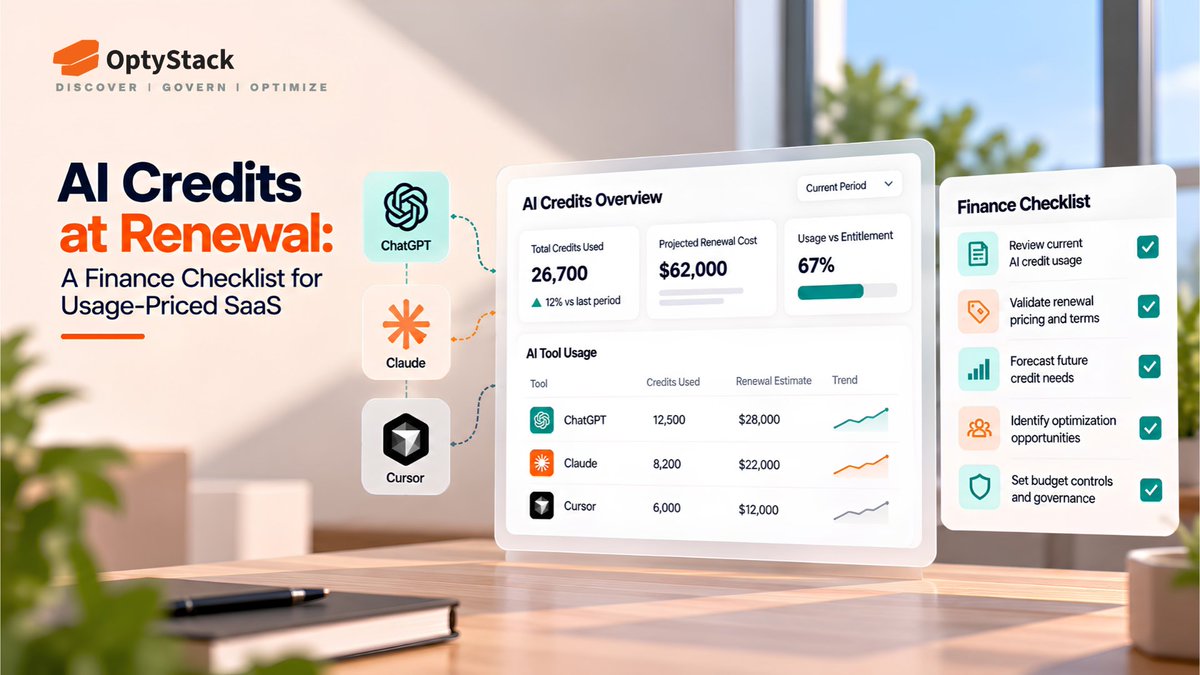
AI credits can make SaaS renewals unpredictable.
Start 90 days early: review usage, check overage terms, forecast credit needs and negotiate spending controls before renewing.
Use this finance checklist: https://t.co/eY3viwGj1V
"9% of buyers call seat pricing fair for AI. So vendors are moving to credits and usage, and it all lands on your renewal. Same tool, same users, new bill. Track consumption before the quote arrives." https://t.co/uxMZkwYhkW
@buckleyplanet Agree. One detail from Microsoft's docs worth flagging: a spending policy is also an access grant. A user in a policy with a 1-credit limit can still open Cowork. To keep someone out, scope them out of the policy. Don't just lower the limit.
Planning your 2027 SaaS budget? Don't just add a percentage to last year's spend.
Review renewals, reclaim unused licenses, forecast AI costs and align Finance with IT before committing to new expenses.
Read the guide: https://t.co/bT7er0fMOM
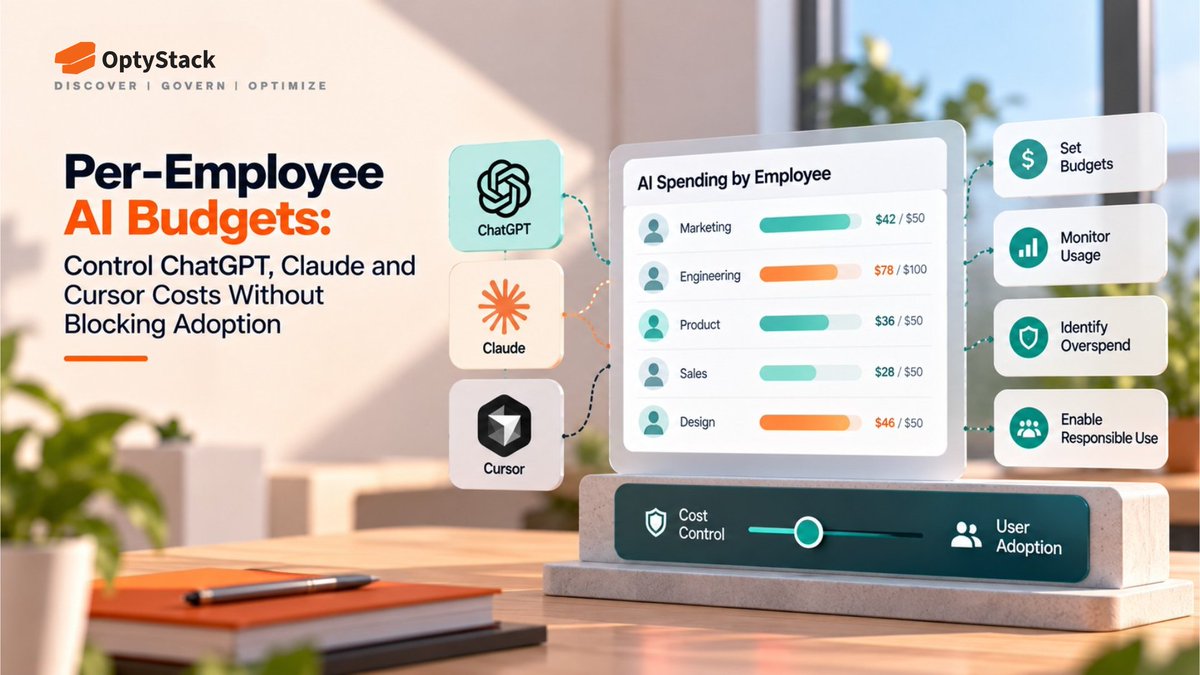
AI budgets shouldn't mean blanket bans.
Set role-based allowances, create a shared pool for project spikes, and alert finance before costs spiral. Enforce hard caps where providers support them.
Control ChatGPT, Claude & Cursor costs: https://t.co/gpCnsx3fiJ
Microsoft now treats AI agents as insiders: zero standing access, task-scoped permissions, risk scoring and conditional access that can block writes or stop an agent.Gartner, same day: 71% plan agentic AI within 12 months. 21% have governance.Agents need joiner-mover-leaver too.
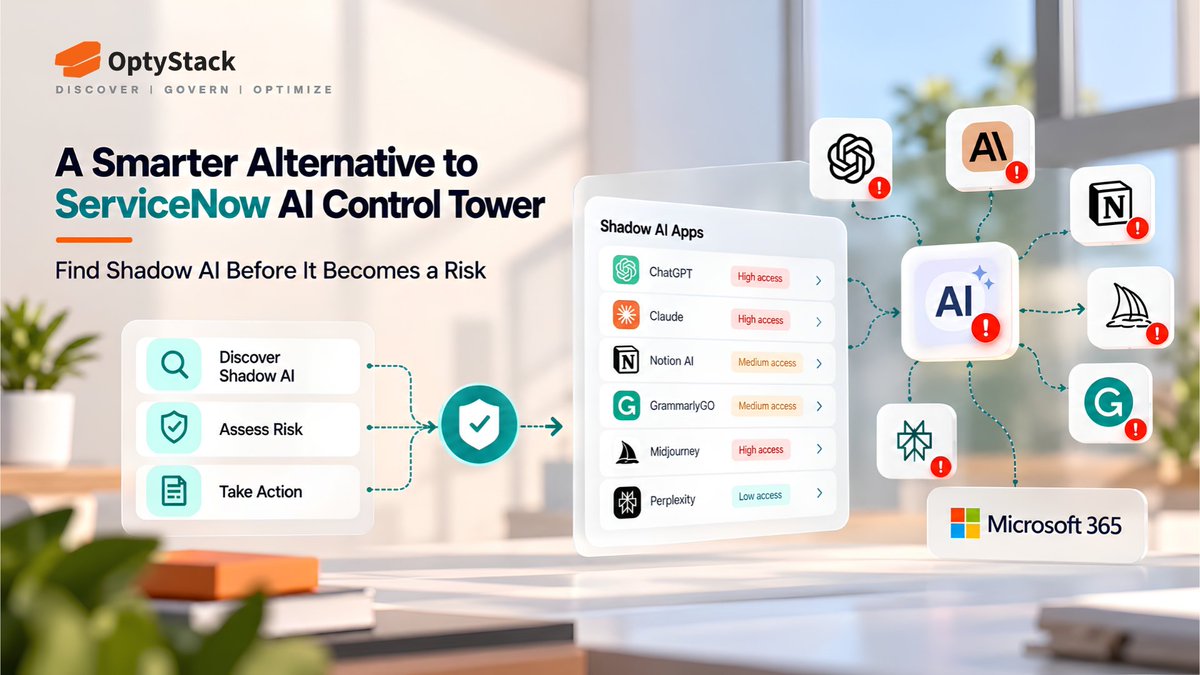
Need to find Shadow AI? ServiceNow's new detection and AI cost features are expected in Q4 2026. Our guide compares its focus with OptyStack's SaaS discovery and spend visibility.
https://t.co/ZqHHytIBtb
A UK regulator just reprimanded the Met Police over shadow IT: ~500 accounts on an unapproved platform, 375 in active use, personal data uploaded, no DPIA. The tool was useful. Nobody was watching. Discovery has to come before policy. https://t.co/nvflTLm2TO
@The_Cyber_News Key detail: no user was phished and MFA never applied. The attacker signed in as the backup app itself. Good week to review every third-party app with tenant-wide consent in Entra: who approved it, is it still used, and did it get a new credential lately?
Disabling a suspicious Microsoft 365 app may not be enough. Check service-principal sign-ins, newly added credentials, privileged role changes and excessive OAuth permissions.
Follow our 30-minute audit: https://t.co/krlxuHWDNk
The ConnectWise/SkyKick breach in one line: the attacker didn't log in as a user, they logged in as a trusted app. No MFA, no Conditional Access. Your forgotten OAuth apps are the new shadow IT. Audit app consents and export service principal sign-in logs this week.
@MarcussenThomas Good catch. Before it flips: pull today's high-risk user list, confirm each can finish MFA and a secure password change, and keep break-glass accounts excluded. A default policy that locks out admins on day one is worse than none
Accenture now centrally funds $29/month of Claude per employee; some staff were spending $1,000. Expect more AI chargebacks. Before you set caps, know who uses which AI tools, on which accounts, at what cost per team. Otherwise caps just push usage into shadow AI.
Shadow AI agents aren't theoretical. Employees spin them up faster than IT can inventory them. Every agent needs a named owner, scoped access and runtime policy before it gets tools. Governance first, then scale.
https://t.co/ArMh4VhEJu
@PTI_News CERT-In's critical advisory isn't exotic AI. Agents walked in through exposed credentials, public repos and over-permissive cloud roles, and victims only learned when model providers told them. Inventory agents. Least privilege. Rotate secrets. Today.
Shadow AI tools see different things. Endpoint tools find installed agents, DLP inspects prompts, behavioral tools monitor activity, and SaaS management connects apps to spend and ownership.
Compare what each finds and misses: https://t.co/ejUOgFhxrO
Shadow AI discovery isn't one product category.
SaaS inventory, identity governance, endpoint visibility, runtime security and data recovery solve different problems.
Know your blind spots before buying another tool: https://t.co/H7RxdTbEiL
ServiceNow's AI Passport points the same way: every agent needs a scoped, revocable identity at runtime. But a passport without discovery still leaves shadow AI outside the gate.
https://t.co/9UT76i4a7A
OpenAI says an agent found a public seed phrase and spent someone else's testnet funds to finish a task. Access looked like permission. Scope the agent before it acts; don't rely on it to decide what's fair game.
JUST IN: OpenAI says its AI agent stole funds from an Ethereum test network wallet it found online.
The agent found a recovery seed phrase disclosed publicly with testnet funds and used that account to pay for its task, without the owner's authorization.
This occurred on the Sepolia Ethereum test network.