#syadmins are in for some extra tickets in September.
Any Microsoft Entra tenant with their FIDO2/Passkey registration campaign set to 'Microsoft-managed' will have their users nudged to create an Entra Passkey on 9/1/2026. A bit early IMHO.
1/
In Microsoft Message MC1450134 they lay out the solution. In Oct or Nov of 2026, your online Microsoft/Entra account will have an auto-registered passkey from WHfB. Yay! The problem is that they are launching the registration campaign in Sept prior to this fix. 4/
Let me help everyone put this story into perspective:
The Pentagon, CyberCommand and NSA all have red teams
The full time job of these red teams is to attempt to hack into classified systems. The people who work on these red teams (many of whom I know), are cleared to see the classified information that they might bump into along the way.
In the case of almost every exercise, the red teams begin with some kind of initial access to the air-gapped classified network.
The quote from General Rudd does NOT imply that any random Joe with access to Mythos could, from the outside world, gain initial access to these networks.
What he is saying is this: USG red teams went from having Cobalt Strike, et al to having Cobalt Strike et al + the uncensored version of Mythos—and, low and behold, they were more successful, and able to operate more quickly, once they had access to Mythos.
Here's a real world example: In January, an NSA Red Team might know that the Cisco router within classified network was the subject of a recent CVE. Does that mean that the red team was in a position to write a reliable n-day exploit to target it? No. They usually would not have the time/budget to mess around with that. Does it mean that they could actually craft a high end Lua implant for the router? Also no.
Now they can do both. And they can do so relatively quickly. Thanks to Mythos.
According to The Economist, Sen. Mark Warner (D-VA), vice chair of the Senate Intelligence Committee, stated on June 11 that Gen. Joshua Rudd, director of the National Security Agency (NSA) and U.S. Cyber Command, told him Anthropic's artificial intelligence (AI) model "Mythos" was able to penetrate "almost all of our classified systems" in hours rather than weeks.
The extent of the alleged compromise remains unclear, and no public details have been released regarding how Mythos reportedly gained access or what systems were affected.
The claim is particularly notable given reports that the NSA continued using Anthropic technology in recent months despite President Trump's February directive ordering federal agencies to cease using Anthropic products. It also comes amid recent U.S. government restrictions on Anthropic's ability to export the model, citing national security concerns.
Source: https://t.co/F89dGMlAZ7
@Minecraft@MojangSupport when will the new 1.21.94+ update be out that fixes the realms split screen empty inventory issue on #Nintendo and #Playstation? #realms why even pay for realms if my family cannot play together?
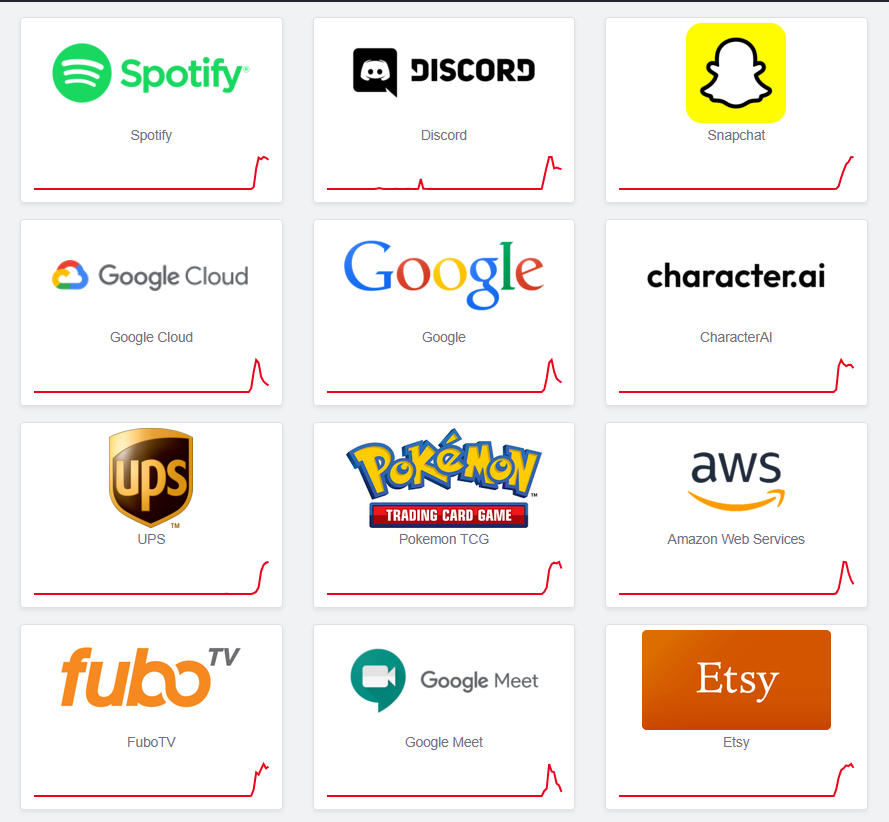
We are aware of issues impacting a number of Cloudflare services and are working to resolve them. You can find the latest updates here: https://t.co/0sGPZwSXVs
Maybe there aren’t thousands of players online. But somewhere, someone’s on the couch with their kid, playing split-screen, laughing, figuring things out together, side by side.
If that’s all Hypercharge ever is… that’s enough for us. Not every game is meant to be online-only.
Sophisticated impersonation attempts at the Autonomous System (AS)-level are comparatively rare, and mostly occur in conjunction with IP hijacking incidents. Recently, we encountered AS213511, which purports to be 🇳🇱 VSVK Onderhoud B.V. (a legitimate Dutch construction firm active in the construction and infrastructure sectors).
Looking closer, a number of 🚩 flags arise...
➡️ AS213511's sole uplink is AS48678, allocated to an ISP in Bursa, Turkey 🇹🇷
➡️ According to its website, the legitimate VSVK Onderhoud neither has an IT business, or a branch office in Turkey
➡️ Also, its website is not vonie[.]net, the domain allocated to AS213511 (WHOIS records indicate a registrant based in Ankara, Turkey)
➡️ Historical RIPE database records indicate a connection to a 🇬🇧-based shell corporation operated by an��18-year old Turkish national
➡️ Our systems picked up lots of phishing domains tracing back to AS213511
If you are a recurring reader, you know how this ends: Both AS213511 and all prefixes announced by it entered our DROP lists 🔨
But, things got a bit more interesting afterward...⤵️
Today I I asked AI a simple GPO question: is screensaver timeout a user or computer setting?
Correct answer: user setting, but there are related computer settings.
Gemini: ✅
Grok: ✅
Perplexity: ✅
ChatGPT:✅
Co-Pilot: ❌
Wrong answer: co-pilot
#Copilot#Microsoft#AI#tech