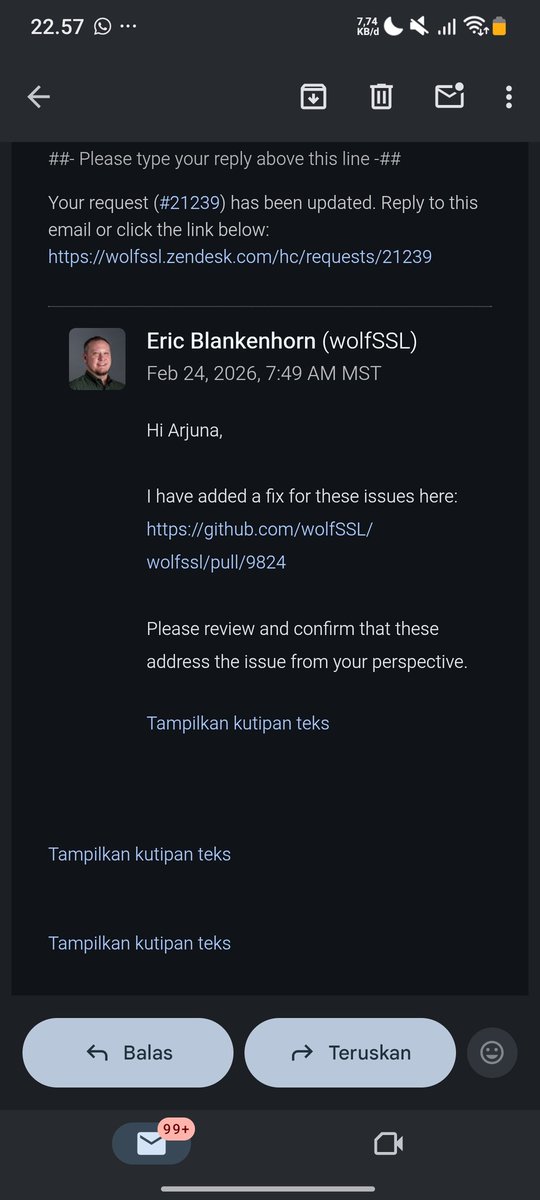
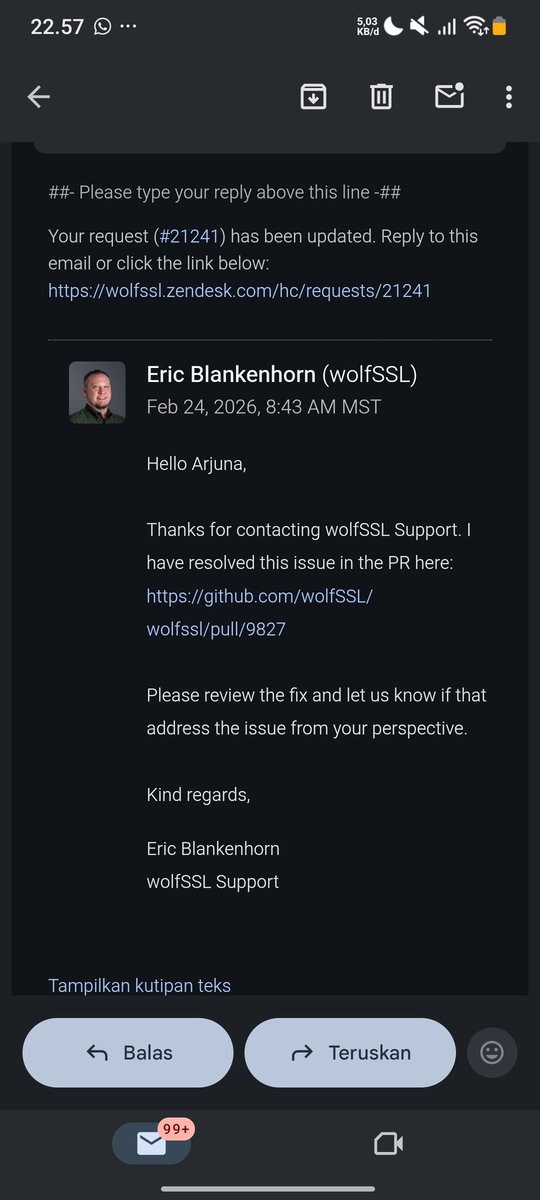
Multiple vulnerabilities I reported to wolfSSL have now been fixed across 4 separate PRs.
Thanks to the wolfSSL team for the fast remediation.
Responsible disclosure wins.
#infosec#bugbounty#opensource
⚠️ PoC Exploit Released for Android 0-Click Flaw that Enables Remote Shell Access
Source: https://t.co/9ZHRqf0PkZ
Google's May 2026 Android Security Bulletin has revealed a critical zero-click vulnerability in the core Android System. The CVE-2026-0073 flaw in Android’s adbd daemon lets nearby threat actors remotely gain full shell access without victim interaction.
An attacker must first establish a TCP connection, successfully negotiate the STLS upgrade sequence, and then supply the malicious cross-algorithm certificate.
To proactively reduce attack surfaces, users should turn off wireless debugging on untrusted networks and revoke authorizations for unknown debugging hosts.
#cybersecuritynews #Android