I tested Grok Fast vs Expert on one question: what is OpenAI's GPT-6 Cyber?
Expert was faster (13s vs 25s), clearer, and openly said what it wasn't sure about.
Both repeated one claim OpenAI never made.
Lesson: even good AI needs a fact-check.
@OfficialLoganK One concrete data point: Google's Gemini 4 Argon robotics post reports a VLA policy fine-tuned on MuJoCo episodes synthesized from a single RGB photo going from 56% to 75% real-world success. The number I'd most like to see next is per-task failure rates.
In an early run of OpenAI's Linux kernel pipeline, 20 of 200 "successful" AI exploits got root through a different 0-day than the one they were assigned.
The headline from OpenAI's cyber-model writeup (Nov 4) is 948 working privilege-escalation exploits. The details matter more:
• 2,308 candidate findings, 1,724 reproduced in a sanitizer VM (about 74.7%)
• 1,169 working root exploits, counted as 948 because that's the number of distinct patches
• $1,213,430 in API cost, about $1,279 per unique exploit
The lesson isn't "AI hacks Linux." It's that an agent reporting success isn't proof it did what you asked. OpenAI had to add an independent check that each exploit used its assigned bug.
Verify the path, not just the result.
@satsPortfolio Same split here. Thinking in my own language catches fuzzy reasoning faster, and the English output stays clean for X. Have you noticed any difference in answer quality between Dutch and English prompts?
A convenience button in Claude Code left real passwords in 1,122 public GitHub files, and the two most common secret scanners still missed 215 of them.
What Apiiro found (reported by The Hacker News, Nov 7):
• 104,185 public copies of .claude/settings.local.json; 1,122 hold at least one secret (1,379 distinct)
• 379 database passwords, 43 SSH logins, 42 GitHub/GitLab/npm tokens, 23 AWS keys
• Including git history, shared settings and agent logs: 2,539 secrets across 1,994 repos
• In half of the affected repos, the file had sat on the default branch for 217+ days
Why it slips through:
• "Yes, and don't ask again" can save the exact approved command, so a password typed into it lands in plain JSON
• Claude Code adds the file to your global git excludes, not the project's .gitignore, so the protection doesn't travel with the repo
• In 539 of 1,105 traced repos, a commit co-authored by Claude changed the file
• gitleaks flagged 564 files, TruffleHog 643; neither flagged 215, because a password inside a command looks like an ordinary word
What to do today:
• Rotate first, clean up second; git history and forks keep old copies
• git rm --cached .claude/settings.local.json, then add it to the repo's own .gitignore
• Approve patterns like Bash(npm run:*), not one-off commands with secrets in them
• Reference secrets as variables ($DB_URL), never inline
Nobody hacked the agent. The approval shortcut was the leak.
Great roundup. One label I'd love to see next to demos like these: which permission preset they ran under.
Per your sandbox docs, Default and Auto run agent commands inside Linux namespaces / macOS Seatbelt, while Turbo turns the sandbox off and unsandboxed commands run with full host privileges. "Built with Antigravity, sandbox on/off" would make these much more useful as real-world benchmarks.
~100 lasers per satellite, each operating above 10 Tb/s, with over 100k satellites should be able to outcompete undersea cables.
Speed of light in space is ~40% faster than cable and the path is direct, instead of following the outline of land masses.
Starlink V4’s 10+ Tb/s laser links don't mean your home internet gets 10x faster.
At the Baron Conference, Elon Musk noted that V4 satellites target ~10x the capability of V3, with optical laser links exceeding 10 Tb/s.
The engineering distinction matters:
• 10+ Tb/s is the inter-satellite laser backbone routing data between satellites in orbit.
• Home terminal speeds on the ground are still limited by RF spectrum and local cell density—meaning 10x network capacity serves more users, not 10x faster single-home Wi-Fi.
• Before V4, the nearer milestone is the V3 rollout.
Update — tested the fix in a fresh Grok session.
Replacing "dish" with "flat rectangular phased-array panel" (and explicitly excluding a parabolic dish + LNB feed horn arm) solved it on the first try.
Clean flat panel on the roof edge now:
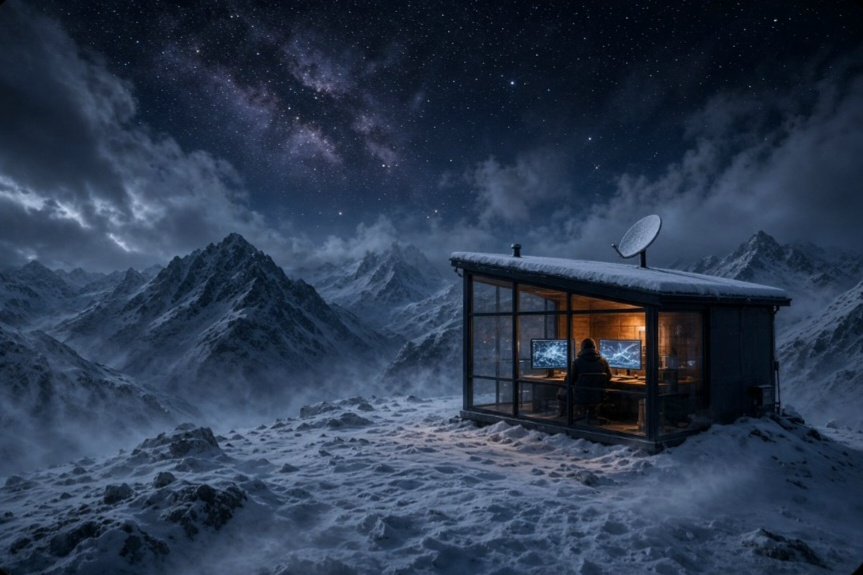
Tested Grok Imagine on Starlink's ad brief: an indie AI builder in an Alpine cabin after a blizzard.
Lighting and dual monitors came out great. One catch on the roof: even Grok still draws a 90s parabolic TV dish with an LNB arm instead of a flat Starlink panel.
Prompt tip: using the word "dish" biases image models toward classic parabolic antennas—specify "flat rectangular phased-array panel" instead.
Also note: Starlink's "Big game" content call is US-only (18+) and requires a 30s video: https://t.co/aJ1fb4T5m0
@Starlink@imagine@X Any chance of adding an international showcase thread for builders outside the US? Plenty of remote engineers in Europe using Starlink who can't enter the US-only broadcast call, but still love pushing Grok Imagine to its limits.
@imagine Quick question for the Imagine team: did you fine-tune the model on the flat Gen 3 phased-array terminal shown in that frame, or do prompts still need explicit geometry cues to avoid classic parabolic dishes?
The claim: both modes said GPT-6 Cyber is "based on GPT-6 Astra." OpenAI never says that; Astra is its separate mainline model.
Source: https://t.co/esVCkyU8CB
I tested Grok Fast vs Expert on one question: what is OpenAI's GPT-6 Cyber?
Expert was faster (13s vs 25s), clearer, and openly said what it wasn't sure about.
Both repeated one claim OpenAI never made.
Lesson: even good AI needs a fact-check.
How a Few Kilobytes of Text Can Ground Commercial Flights and Scramble Fighter Jets: The Anatomy of Modern Digital Disruption 🛡️✈️
Over the past few days across Europe, commercial aviation, media newsrooms, and public institutions have faced a wave of apparently coordinated false threat alerts. Earlier waves targeted hundreds of schools using a similar playbook. Thankfully, these alerts proved to be hoaxes with zero physical casualties—yet the operational chaos they caused is very real.
Commercial airliners were forced into emergency diversions, military fighter jets were scrambled into readiness, and daily operations were disrupted across multiple countries. All triggered mostly by anonymous emails and phone calls.
From a cybersecurity and systems-engineering perspective, this is the ultimate example of asymmetric digital leverage:
The Cost Asymmetry
Generating an anonymized threat via encrypted email relays, disposable accounts, or masked VoIP calls can take seconds and costs virtually nothing. The defensive response—diverting an airliner, scrambling interceptor jets, and deploying emergency units—costs orders of magnitude more.
Exploiting Safety-First Protocols
Critical infrastructure operates on a strict zero-risk tolerance policy. Even when digital forensics strongly suggest an automated hoax, aviation and public safety authorities cannot gamble with human lives. The attackers aren't hacking the aircraft's avionics; they are "hacking" the mandatory human safety protocol.
The Power and Fragility of Modern Connectivity
We live in an era where a single packet of data sent from anywhere on Earth can instantly halt physical movement thousands of kilometers away. The same hyper-connectivity that lets ordinary people and indie builders deploy global tools in minutes also gives unprecedented disruptive leverage to bad actors.
No finger-pointing or geopolitical speculation is needed to see the core lesson here: modern security is no longer separated into "digital" and "physical." Strengthening communication authentication standards, deploying real-time AI threat triage, and maintaining calm public resilience are our best defenses against digital noise designed to create physical panic.
#CyberSecurity #Infosec #AviationSecurity #TechAnalysis #AI