‘Personal data’ is not a static bucket category that data either stays inside or remains outside of in a fixed position.
‘Personal data’ is a dynamic , context-based attribute tag, and the sooner people wrap their heads around this fact, the safer we all can be
Great news this Monday morning for consumers who do not want to be tracked online! The Norwegian Data Protection Authority @Datatilsynet is banning Meta from using behavioural advertising that uses surveillance and profiling of users in Norway.
💪🙌💪🙌
https://t.co/AIdcxQ8NcF
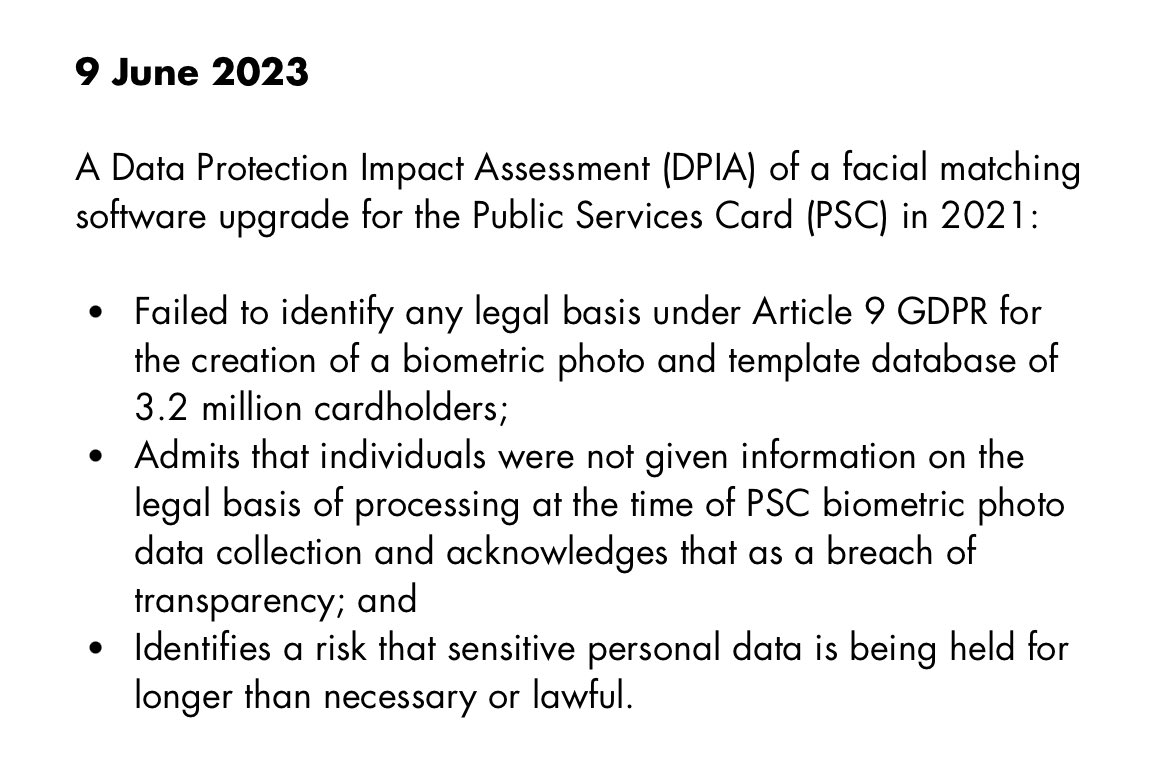
These headlines from the ICCL/Digital Rights Ireland statement on KPMG’s PSC biometric database assessment will give some idea how destructive of the Dept’s defences it is.
This is what they have known, while denying any legal issues exist.
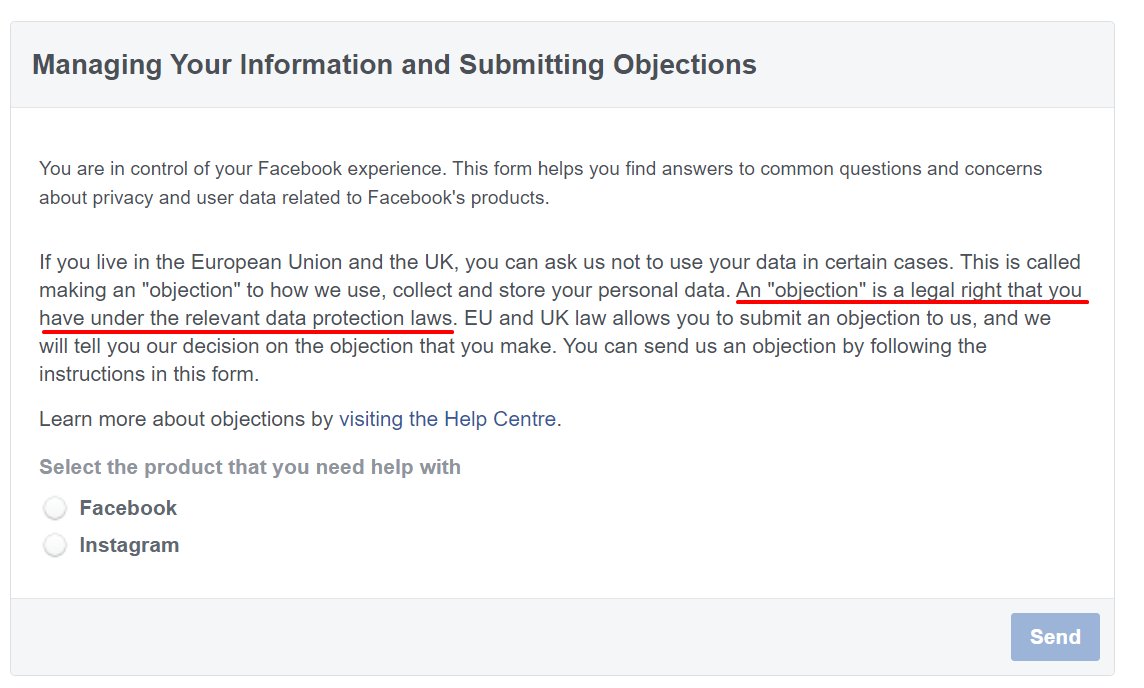
Facebook's new opt-out form is very hard to find.
After a lot of digging and several preliminary clicks, I ended up here.
I'm now going to live-tweet the process of objecting to Meta's ad-targeting.
This is pretty niche stuff. So if you're interested, I like you.
🧵
I just can't get over this.
These startups
-solicited detailed personally identifiable medical information about 100,000 customers
-told them their data is “protected” and “used only” by its care team
-SHARED IT WITH ADVERTISERS FOR YEARS
https://t.co/btXWGgtlgP
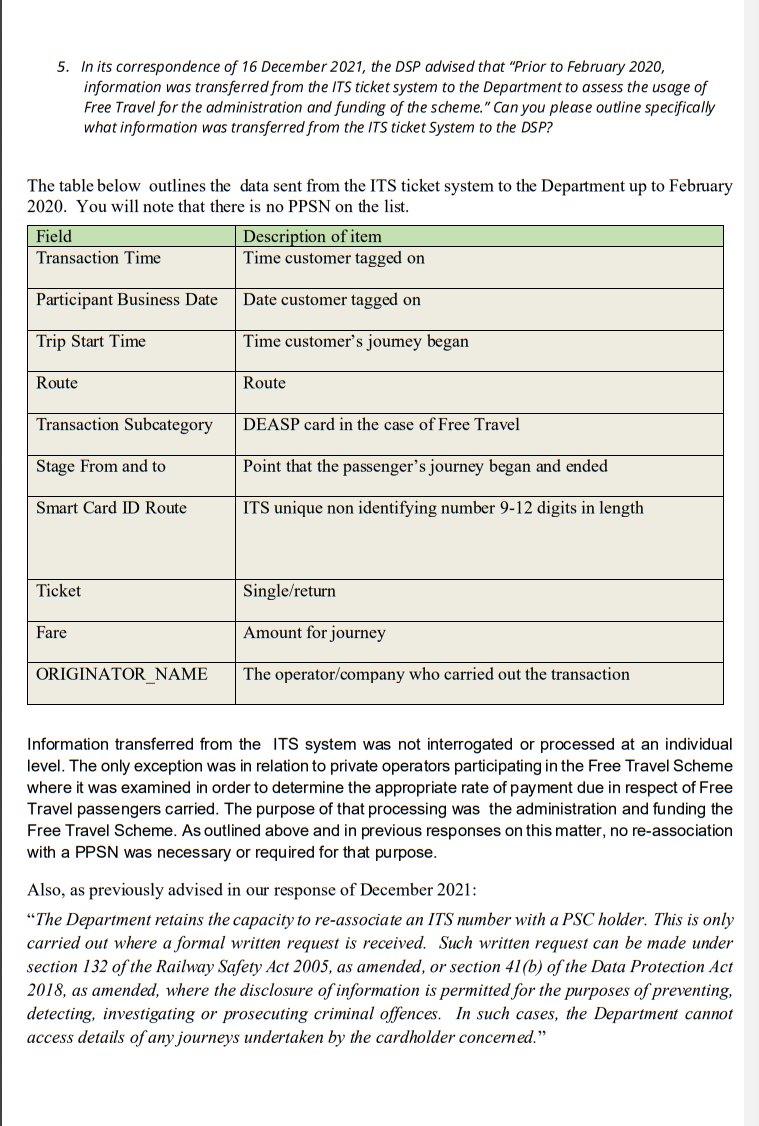
The Public Services Card being used for mass surveillance saga continues.
The latest letter to the DPC from @welfare_ie (`-3) and my reply to it (4) below.
If ur new to this story, catch up here https://t.co/debwExWFlp
The Dutch Data Protection Authority has imposed a fine of €50,000 on the police for using camera cars in Rotterdam to monitor compliance with coronavirus measures without first assessing the privacy risks this might entail. https://t.co/MPe9aRGN6H
This is a significant clarification from the Court on the information data controllers are obliged to provide to data subjects when responding to a Subject Access Request.
➡️ Press release: https://t.co/QLGD5YGytv
➡️ Judgment: https://t.co/P0w3GGfIbV
ℹ️🔴La CNIL prononce une amende de 800 000 euros à l’encontre de DISCORD INC. pour avoir manqué à plusieurs obligations du #RGPD en matière de durées de conservation et de sécurité des #données personnelles 👉 https://t.co/wpNURvzHuB
NEW: The Home Office used location data from an international student’s mobile phone to detain him for allegedly breaking his visa conditions, The Ferret can reveal.
Critics say it may be breaching privacy laws.
https://t.co/afyCoHi5Uz
Very significant from the UN! Four Special Rapporteurs have jointly raised concerns about the Govt's plans to introduce Facial Recognition Technology (FRT) through the Garda (Recording Devices) Bill. UN letter https://t.co/cl9IfS5h3v? and State response https://t.co/NBk2r32B9C
During the negotiations about the #GDPR I warned that the One Stop Shop mechanism was a bad idea to regulate #BigTech. But the European decision makers didn’t want a pan-European regulator. So they should criticize themselves, not @DPCIreland.
https://t.co/1YkzWzl8if #privacy
The Irish Data Protection Commission published its final decision to fine Instagram 405 million €; among the 10 identified violations, 2 of them are individual breaches of Art 25 GDPR Data Protection by Design, amounting to 50 mill € 1/ https://t.co/2il9PkDOfD
This is not a trade law. It did not appear in response to US tech companies.
It is a response to Europe’s terrible 20th C experiences of misuse of personal data.
A US lack of historical understanding as to where the GDPR comes from is not uncommon, but always unforgivable.