🚩 End of an era. Beginning of the future.
The final edition of ASIS CTF is almost here. Join us for one last run in this format:
🗓 Start: Saturday, 14 UTC
⏱ Duration: 24 Hours
We hope you enjoy challenges as much as ever — lets see what the future holds for the world of CTF 🚀
🔍 Security Research: Two (authenticated) vulnerabilities found in the DrayTek Vigor2962 router.
I identified an out-of-bounds write that can lead to password disclosure, and a format-string vulnerability.
Full write-up:
https://t.co/aRLkpOg0hQ
#CyberSecurity#ZeroDay
The CTF just finished! It was a really interesting event covering many fields like Web, Crypto, Boot2Root, Rev, Pwn, Mobile, and more.
Our team, WTN, finished 112th on the global scoreboard. GG to everyone who participated! 🔥
https://t.co/BhECXQNyaD
#BrunnerCTF#CTF
I just released `kuna_mcp`, a Python MCP server that lets AI agents interact with the Kuna decompiler over HTTP.
It can list functions and decompile one or multiple targets without analyzing the entire binary.
https://t.co/zcM4jgee3f
🚀Kuna looks very promising. Autonomous refinement for decompilers is a fascinating idea, and the early results are impressive.
We'll be watching its progress closely for our project as it matures.
https://t.co/Nw5HTUwujm
I'd like to introduce Kuna, a new Rust-based decompiler that explores a highly experimental direction: self-refining decompiler development and usage. Or: a decompiler constantly improved by agents, made for agents.
Kuna rivals the best in structuring now. Let's talk about it.1/
Identified two vulnerabilities affecting DrayTek Vigor X, including a Format String issue and an Out-of-Bounds Read/Write vulnerability.
Reported responsibly to the vendor. More details will be shared after the disclosure timeline.
#0day#ZeroDay#CyberSecurity
Today I am releasing the Binary Ninja Diffing plugin.
It features Control flow graph, disassembly, LLIL, MLIL and HLIL diffing views.
You can Save and restore diffs from the BNDB or json file.
Supports porting function names from one binary to the other
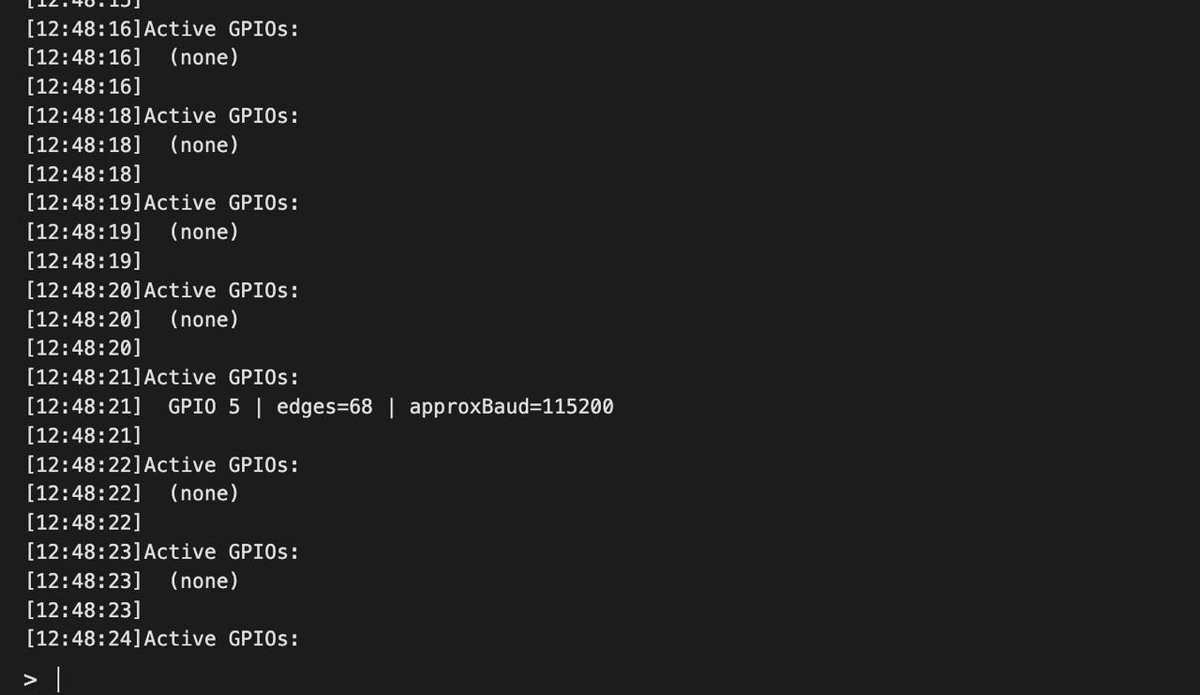
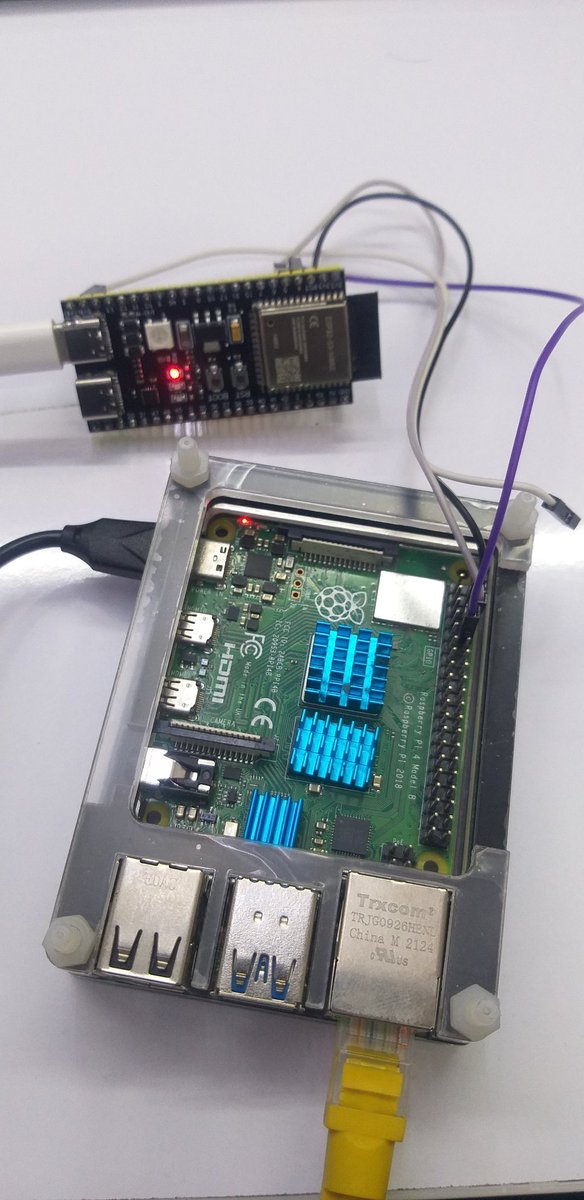
Just compiled and tested ESP32 Bit Pirate on my Raspberry Pi. The UART scanner works great, and it has lots of useful features for hardware debugging.
https://t.co/cPtNQCqwTN
#ESP32#RaspberryPi#UART#OpenSource
⚔️Discovered a zero-day stack overflow in a router firmware.
Now I'm verifying if it affects other models from the same brand.Reverse engineering every firmware?
Buying every model?
No;use the power of symbolic execution.
#CyberSecurity#SymbolicExecution#ZeroDay#RouterHacking
I ran the poc code on my Raspberry-pi against LG-H324t phone. imagine worse scenario's to get initial access by installing malware...
📝Write-up: https://t.co/B1ch5ZKrOW
📂PoC: https://t.co/RxM77wEYae
🔥Bluetooth vulnerabilities in Android, Linux, macOS, iOS and Windows can be exploited to pair an emulated Bluetooth keyboard and inject keystrokes without user confirmation.
#exploit#bluetooth#vulnerability#cybersecurity
Just finished diving into an awesome #Phrack write-up on detecting hidden rootkits in Linux. 🔍 Used the kernel module they provided to explore how stealthy malware can be exposed. Highly recommend for anyone interested in kernel-level security! #CyberSecurity#Linux#Rootkits