Magisk roots via ramdisk surgery. KernelSU lives in the kernel itself — so KernelAVD just swaps your emulator's kernel for a prebuilt GKI+KernelSU build matched to its KMI branch. No magiskboot, fully reversible.
https://t.co/LdPmcB2USz
#Android#KernelSU
After using Python for so long, I've been trying to switch to GoLang over the last two years just to try something new. I'm finally somewhat confident in being able to write I'd try to create a video series to help others. This is the first video: https://t.co/TYWrUSZGvm
🚀 پیادهسازی و اکسپلویت سه آسیب��ذیری جذاب Microsoft SharePoint 🎯
🔹 CVE-2024-38094
🔹 CVE-2024-38024
🔹 CVE-2024-38023
جزئیات کامل و PoC در کانال تلگرام:
📎 https://t.co/hzuyBCmUtd
👾 آماده یادگیری و تحلیل باشید!
#CyberSecurity #GOTOCVE
رایتاپ آسیب پذیری 150,000$
وسوسه انگیزه
رایتاپشو بخون پس
هکر اولش میاد میگه :
ما گاهی وقتا انتظار داریم یه باگ بحرانی ، یه چیز پیچیده و سخت باشه اما در واقعیت کاملا برعکسه
[این جمله خیلی خیلی باارزشه بنظرم]
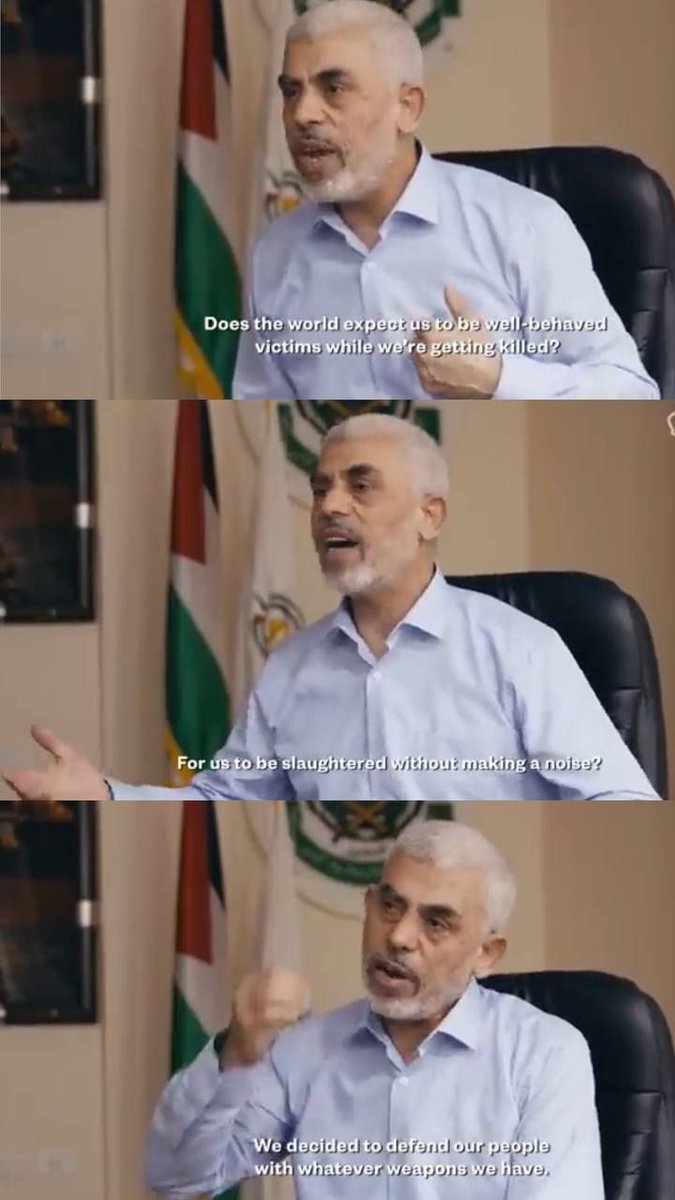
“Does the world expect us to be well-behaved victims while we are getting killed? For us to be slaughtered without making a noise?”
— Hamas leader Yahya Sinwar.
دیدین یه سری تارگت ها هستن که بخاطر ریت لیمیت سفت و سخت نمیزارن ما فاز انجام بدیم ؟
تو این ویدیو اومدیم و بهترین روش هایی که برای دور زدن ریت لیمیت هستن و از همه مهم تر نیاز به هزینه ای هم ندارن رو مورد بررسی قرار دادیم.
https://t.co/UPO9BxFThM
When conducting reconnaissance, identifying the ASNs and CIDRs associated with the target is crucial. To expedite the process and confirm their validity using https://t.co/O3ubGRWkXb, you may utilize this bash function instead of using the main website.
#bugbounty#bugbountytips
started with solidity, played CTF/Challenge(s) such as @hackthebox_eu & @OpenZeppelin's ethernaut (playing until death 🫡), Learned many things and at this point, i want to start Auditing on the past @CodeHawks 's First Flights 🦅✈️
1/2
CVE-2024-4040
SSTI vulnerability just made CrushFTP before 10.7.1 and 11.1.0 on all platforms, to read files with root access and bypass authentication to get admin!
and there is a exploit to perform attack
https://t.co/THeKyddshL
ی ویدیو درست کردم و race condition رو تا حد امکان سعی کردم کامل توضیح بدم (از صفر که تو کد چجور اتفاق میوفته تا انواع مختلفی که داره و متدولوژی پیدا کردنش و پیشرفتهترین حالت ممکنش)
اخر ویدیوهم چندتا لابراتور پورت سوییگر رو حل کردم که مفهومش کامل جا بیوفته
https://t.co/egcaF7vL9i
میخواسم برای مصاحبه تست نفوذ وب آماده شم گفتم یه نوشن درست کنم از مسیری که پیش میرم تا بقیه هم استفاده ک��ن.
این نوشن شامل چند بخشه : یه توضیح مختصر درمورد باگ ها ، ایمپکتش��ن ، روش های جلوگیری و تشخیصشون.
🚀 Unveiling the power of DNS Recon with dnsX v1.2.0!
Get all the DNS data you need for your domain or subdomain list with the new "-recon" option 🔍
🔗 GitHub Release: https://t.co/VRmU7w5qdY
#dns#recon#opensource
💡 Improve your recon game with dnsX! 👨💻👩💻