🎉 Published #QuarkEngine v26.11.1!
Here are 1 major update:
💡Add new Quark rules and analysis reports for the BrainTest, Herodotus, and BTMOB RAT malware families.
👉 https://t.co/S6xnykMz07
#AndroidSecurity
🎉 New report: #BrasDex.
BrasDex is an Android malware family that evades analysis through obfuscation and emulator detection and collects device information including location data, SIM details.
📎 https://t.co/Mt7SJnwBBt
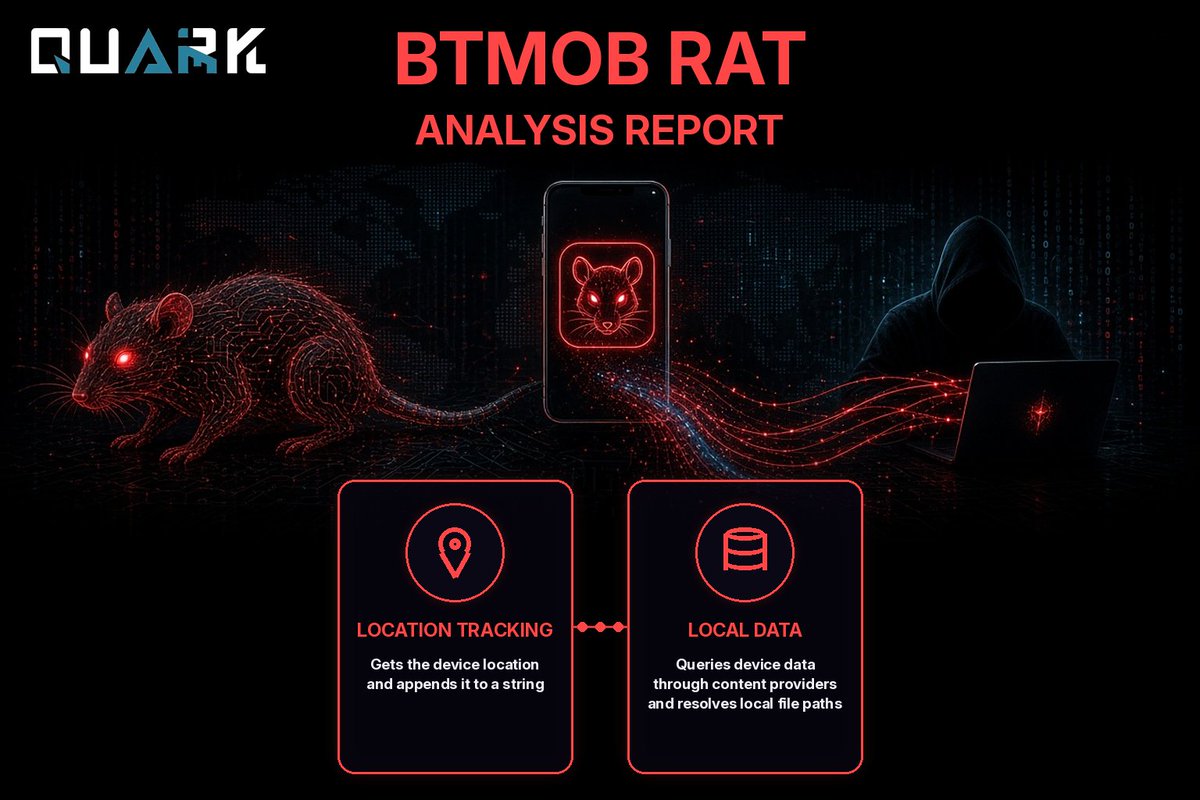
🎉 New report: #BTMOBRAT.
BTMOBRAT is an Android remote access trojan (RAT) designed to compromise infected devices through remote control, surveillance, and sensitive data theft.
📎 https://t.co/Idw48S7Da0
🎉 New report: #Herodotus.
Herodotus is an Android banking trojan that abuses Accessibility Services, steals local data, and controls SMS messages to access sensitive information and compromise infected devices.
📎 https://t.co/eXZE8d2uAp
🎉 Published #QuarkEngine v26.10.1!
Here are 1 major update:
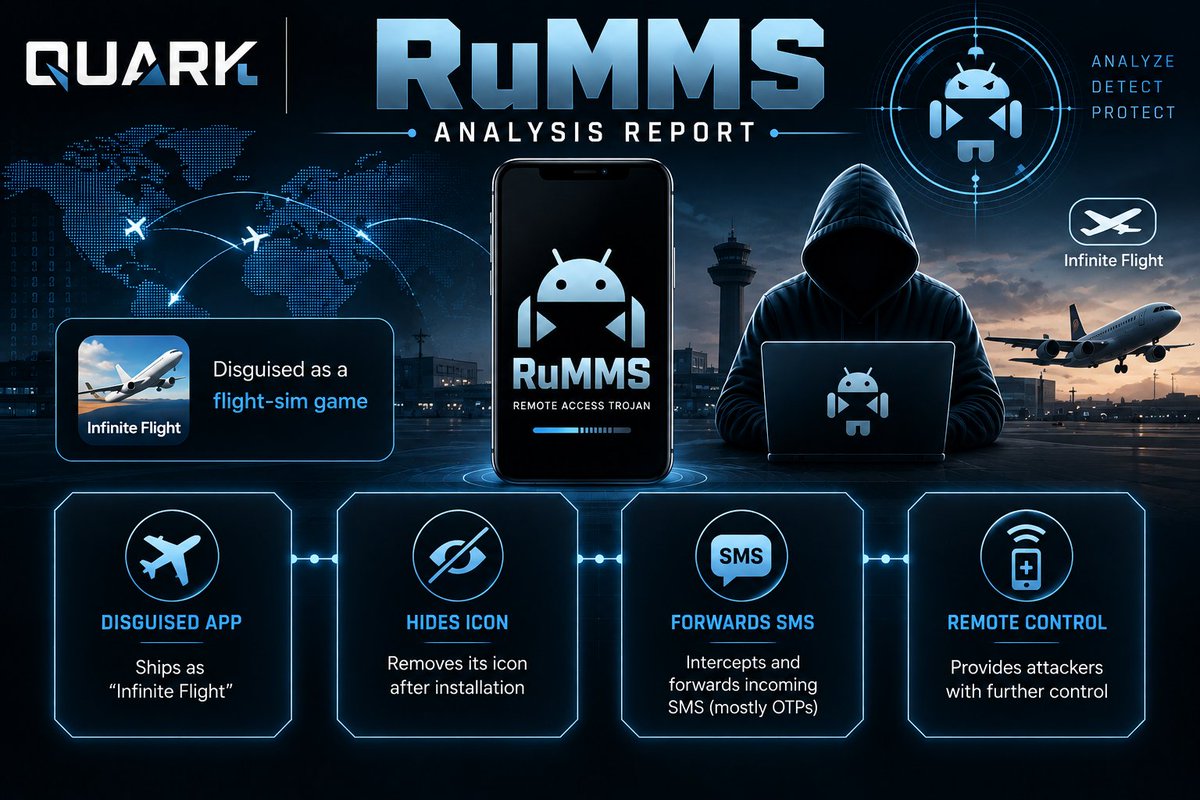
💡Add new Quark rules and analysis reports for the Exodus, RuMMS, and Dendroid malware families.
👉 https://t.co/Xdy4ksmwHo
#AndroidSecurity
🎉 New report: #BrainTest.
It gains root privileges through multiple exploits, installs itself as a system app, and dynamically loads additional code to maintain persistence. Quark detects these behaviors.
📎 https://t.co/YOaUyMzvVx
🎉 New report: #Exodus — with a new Quark detection rule added.
This update expands Quark’s coverage of Exodus, an Android malware family known for collecting device information and exfiltrating sensitive data.
📎 https://t.co/PspqoaF0Pd
🎉 New report: #RuMMS.
It ships as a flight-sim game called "Infinite Flight", hides its icon after install, and forwards incoming SMS — which today mostly means one-time codes. Quark detects these behaviors.
📎 https://t.co/GBP8P0F5pH
🎉 Rules updated for the #Dendroid malware family and new report release.
We're continuing to move toward practical and powerful Android malware analysis tools — thanks for your continued support!
📎 Report: https://t.co/4CTbPX5fHD
🎉 Published #QuarkEngine v26.9.1!
Here are 2 major updates:
💡Add Quark malware analysis reports for
EventBot, Skygofree, and Chrysaor.
💡Set DexTrace as the default analysis library.
👉 https://t.co/NvvxCc3uP0
#AndroidSecurity
🎉 Rules updated for the #Chrysaor malware family and new report release.
We're continuing to move toward practical and powerful Android malware analysis tools — thanks for your continued support!
📎 Report: https://t.co/drGzvlxgcA
🎉 Rules updated for the #Skygofree malware family and new report release.
We're continuing to move toward practical and powerful Android malware analysis tools — thanks for your continued support!
📎 Report: https://t.co/jiDTneMBsS
🎉 Rules updated for the #EventBot malware family and new report release.
We're continuing to move toward practical and powerful Android malware analysis tools — thanks for your continued support!
📎 Report: https://t.co/k7JtsaclVT
🎉 Published #QuarkEngine v26.8.1!
Here are 2 major updates:
💡Add Quark malware analysis reports for
AhRat, AndroRAT, and Sova.
💡Add DexTrace core-library backend.
👉 https://t.co/3p0Jh1tMbw
#AndroidSecurity
🎉 Rules updated for the #SOVA malware family and new report release.
We're continuing to move toward practical and powerful Android malware analysis tools — thanks for your continued support!
📎 Report: https://t.co/AsX4crt5Dn
🎉 1 new rule added and 278 rules updated for the
#AndroRat malware family. We're moving toward practical, powerful tools — thanks for your continued support!
📎 Report: https://t.co/m0XzkThKnw
🎉 Rules updated for the #AhRat malware family and new report release.
We're continuing to move toward practical and powerful Android malware analysis tools — thanks for your continued support!
📎 Report: https://t.co/RXn68brK9w
🎉 Published #QuarkEngine v26.7.1!
Here are one major update:
💡Add new Quark rules and analysis reports for the NGate, Cerberus, and SuperCardX malware families.
👉 https://t.co/pObJlna2Pp
#AndroidSecurity
🎉 1 new rule added and 277 rules updated for the
#NGate malware family. We're moving toward practical, powerful tools — thanks for your continued support!
📎 Report: https://t.co/ldt1kkGZny
🎉 Rules updated for the #SuperCardX malware family and new report release.
We're continuing to move toward practical and powerful Android malware analysis tools — thanks for your continued support!
📎 Report: https://t.co/ezk2MnzRMs