A secret scanner's own output can become a leak.
Print the found key into CI logs, and everyone who can read the logs now has it.
veil-rs can mask findings in its output. Finding and not showing go together.
https://t.co/iXN9hAVUOx
🚨 Veeam patches a CRITICAL 9.1-rated flaw in Backup & Replication 13.
→ Unauthenticated attackers could bypass access controls.
→ Enterprise backup infrastructure at risk.
→ Three additional security flaws fixed.
Patches are available - https://t.co/wK5iEZlfDQ
I started the veil series to make data-leak news a little rarer. I began 3 projects and stopped all 3.
QUIC consensus, the macOS sudo wall, signature design: here's why I stopped each one.
https://t.co/v0sI8wKFer
🛡️We added Adobe Commerce vulnerability CVE-2026-48356 & Google Brotli vulnerability CVE-2026-111497 to our KEV Catalog. Visit https://t.co/myxOwap1Tf & apply mitigations to protect your org. #Cybersecurity#InfoSec
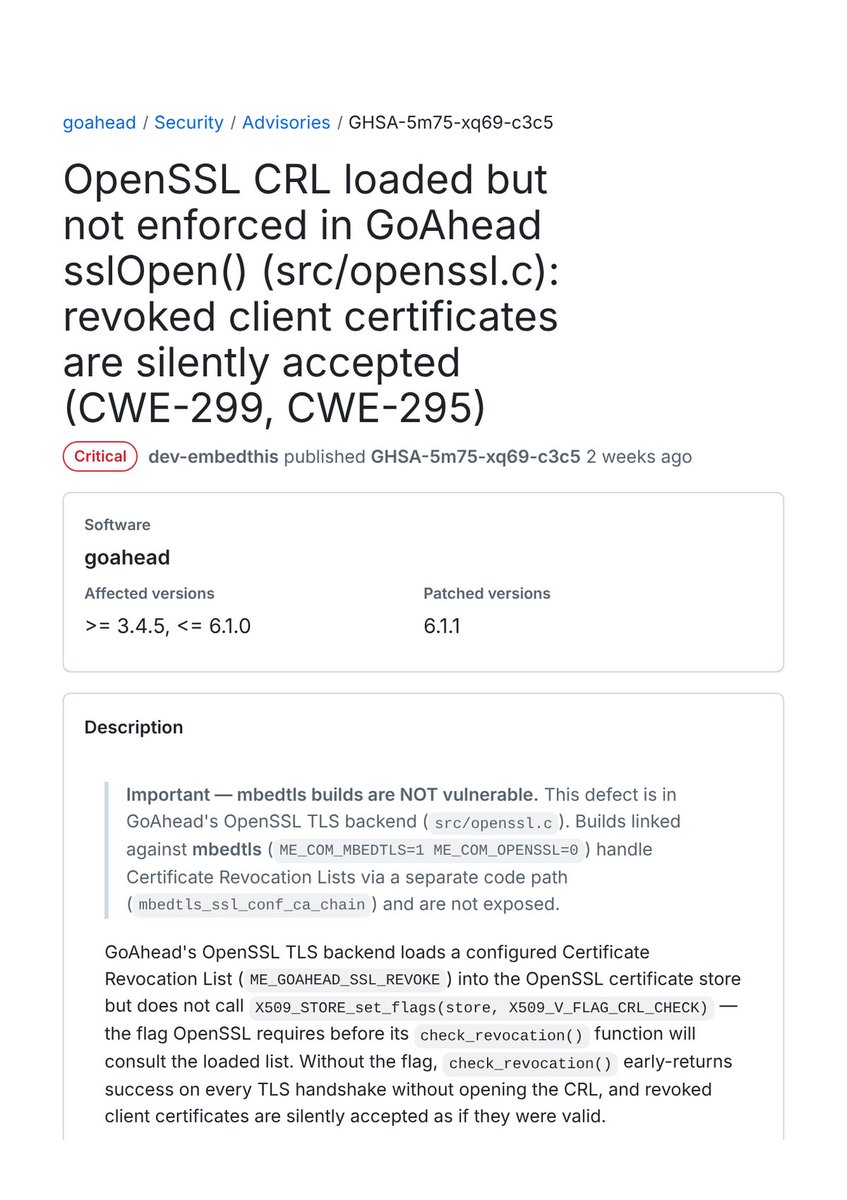
‼️ Palo Alto Networks, Comcast, D-Link, HP, Canon, Honeywell, GE, Oracle, Siemens, Rockwell, Digi, Lockheed Martin and Boeing use the GoAhead web server, which has been accepting revoked certificates, FoxIO says.
Its maker says it runs in hundreds of millions of devices.
The critical flaw, CVE-2026-115881, lets a stolen device keep its access where client certificates are checked against a revocation list. FoxIO does not say which products are affected.
A second bug, a 2018 typo in GoAhead's Mbed TLS builds, shrinks a 2048-bit encryption number to one byte, leaving 8 possible secrets.
Anyone who recorded a TLS 1.2 session could decrypt it, if the connecting app accepts the broken number.
Earlier this month, browsers cut off Indian certificate authority eMudhra after one of its private keys turned out to be the number 4.
A third bug lets oversized certificate chains through on older LibreSSL builds.
GoAhead fixed the first two in version 6.1.1 in August. Proof-of-concept code is public.
Any fix for their devices has to come from the 13 firms.
New Zenn post (in Japanese): veil-arena, a disposable-VM test bed for the Veil tools, and what v0.4.0 verified. Research stage.
Honest note: on AWS and GCP, XDP wouldn't attach to the real NIC.
https://t.co/PHS0v9bKNp
A China-linked group exploited a BeyondTrust Remote Support zero-day (CVE-2026-102764) for ~7 weeks before disclosure. Patch, ship logs off the appliance, and rotate stored credentials.
#cybersecurity
https://t.co/Cc0AzjvjIm
veil-rs runs a weekly dogfood check on its own repo.
This week's OpenSSF Scorecard: 3.3/10. That's low.
For a security tool, I'd rather keep the number in the repo and raise it one check at a time than hide it.
https://t.co/iXN9hAVUOx
Update your @Apple device right now!
Update with a fix for an actively exploited vuln(s):
iOS 18.7.11 and iPadOS 18.7.11
For:
iPhone XS, iPhone XS Max, iPhone XR, iPad 7th generation
Released:
26 Oct 2026
veil-arena v0.4.0 (source) is out: a VM test bed for Veil tools, now with a 2-VM interrupt/recovery test, an isolated-VM Warden test, and more validation logs. Not a production-protection claim; parts unverified.
https://t.co/tPN0mCMEcs