@squeezeandthank I need to know where to place the sticker to help with my left hand, would you respond with a mark up on the picture on where exactly I should place the sticker? I'm a huge fan of the poster you made!! It's helped me tremendously in learning my chord patterns!
YOU GUYS! @ISC2 is offering FREE entry-level Cybersecurity training AND a FREE exam voucher for a certification attempt for a limited time! Sign-up below!
Learn more about One Million Certified in Cybersecurity at https://t.co/tjY8QN5Z4I
#ad
🌟 Meet James Mckee, a developer and security advocate who's reshaping the world of developer security practices! 💻 Join us for an insightful discussion on offensive #AppSec and the role of security in engaging developers beyond the echo chamber. 🚀 https://t.co/ziUWQS5Gjf
2) Perform math if the tested field is an integer:
2) Perform math if the tested field is an integer:
🔹 user_id=1338-1
If there is a sign of an SQL injection, you will see a result with user_id=1337.
🧵 2/8
@StringKing hey y’all, I’m looking for a stringking U tutorial on True Frequency Universal head, do y’all have it up on stringking U? Do y’all plan on adding it if not? Any recommendations on a similar pattern of another head I can follow for a low pocket?
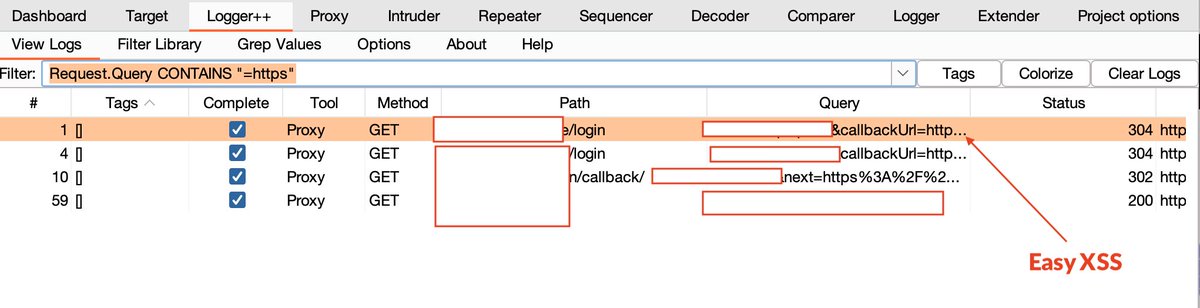
A Simple Tip for #bugbounty, But a Money Maker 🧐💸🫰
Before you finish your day of hunting:
search in all requests and check if the value is equal to `=https`.
-----------------------------------------
Request.Query CONTAINS "=https"
-----------------------------------------
By doing this, you can modify the URL after the parameter to find potential SSRF, XSS, Open Redirects, etc.
#BugBounty #bugbountytips
@EJUpClose@FengelAtl Eric I have listened to your music since I was 14 and I waited all week long so stoked to hear cliffs of Dover live and played by you here in Orlando but I got an email saying the concert is postponed, will you please make it back? #musician
@EJUpClose why is the concert in Orlando PostPoned? It was a dream of mine since I was 15 to hear Cliffs of Dover live and performed by Eric Johnson. Please provide a response, I’m crushed 😓😓😓
In the world of bug bounty hunting, Insecure Direct Object References (IDORs) can be a goldmine. In this thread, we'll share advanced tips to sharpen your IDOR detection skills. Let's dive in! 🌊🔍
#bugbountytip#bugbountytips#CyberSecurityAwareness
1/n
#bugbounty#bugbountytip
One way to find information disclosure vulnerabilities is to change the header.
credit:@jae_hak99
Change the Accept header to:
Accept: application/json, text/javascript, */*; q=0.01
Some vulnerable servers information, stack and route information