Rapid7 is a leader in AI-powered managed cybersecurity operations. 11,500+ customers utilize Rapid7 to disrupt attackers and advance their cyber resilience.
🚨 On 11/17/26, public reports described CVE-2026-114938 as a memory corruption vuln in Java 17 & up that could allow a remote attacker to execute code without authentication.
Rapid7 is actively monitoring the situation, updating here as new info arrives: https://t.co/vFeIjb8tC5
Rapid7 Surface Command now integrates with Claude’s Compliance API, bringing supported organization, user, role, group, and settings information into the same platform teams use to understand other assets and identities.
Keep reading: https://t.co/G6lXdPm8rV
🚨 On 11/6/26, the #Apache Software Foundation disclosed CVE-2026-90436 – a vuln in Axis 1.x that allows for unauthenticated RCE.
Some versions of Atlassian Confluence & N-able N-central use the affected Axis library and are thus at risk.
Read on: https://t.co/5yV6q2Lyys
🔎 As part of Rapid7's ongoing research into #Zimbra Collaboration Suite, our Intelligence team reported 5 findings in #ONLYOFFICE Docs today.
Find the full technical analysis, including a PoC & fix, in our latest blog: https://t.co/k3kTc62tTV
Even with +$2,000 in BTC at stake, a recent capture-the-flag exercise proved that a working PHP2Shell exploit needs to be highly tailored to the environment at hand.
Episode 18 of Hacktics & Telemetry is now live. Keep watching: https://t.co/4QHpBiFhFw
🧐 Most year-end predictions don't get graded. Ours do.
On Dec 10, Rapid7’s experts will reveal their 2027 predictions then check their own 2026 calls. Choose your timezone below 👇
🌎 NA: https://t.co/CJWi4No2QW
🌍 EMEA: https://t.co/adRNmTkEsi
🌏 APJ: https://t.co/fcZRNT0lkw
🚨 On 11/9/26, N-able announced its response to the public disclosure of critical vulns. affecting N-central.
Used widely by MSPs/enterprise IT to administer endpoints & infrastructure, compromise can put downstream managed environments at risk. More: https://t.co/4JTHd3AsEc
Sign #1: Every alert arrives with homework.
Your MDR partner should add capacity and expertise to your team when you need it most – not hand the hardest work right back to your analysts.
Get to know the 5 signs of an MDR arrangement falling short: https://t.co/gQeL4xwisH
Security teams have never lacked vuln data. So when frontier AI reduced the time (& cost) needed to surface even more weaknesses, it was your decision windows that felt the squeeze.
Rapid7 is offering access to a post-Mythos Gartner report. Read it here: https://t.co/7Tr2QScOs5
🚨 On 10/29/26, #Ivanti updated its security advisory for Ivanti Connect Secure (ICS) to include 2 additional vulns.
Exploitation of CVE-2026-111357 & CVE-2026-118527 in the wild has already occurred prior to disclosure. More in our blog: https://t.co/sisxCpZqTH
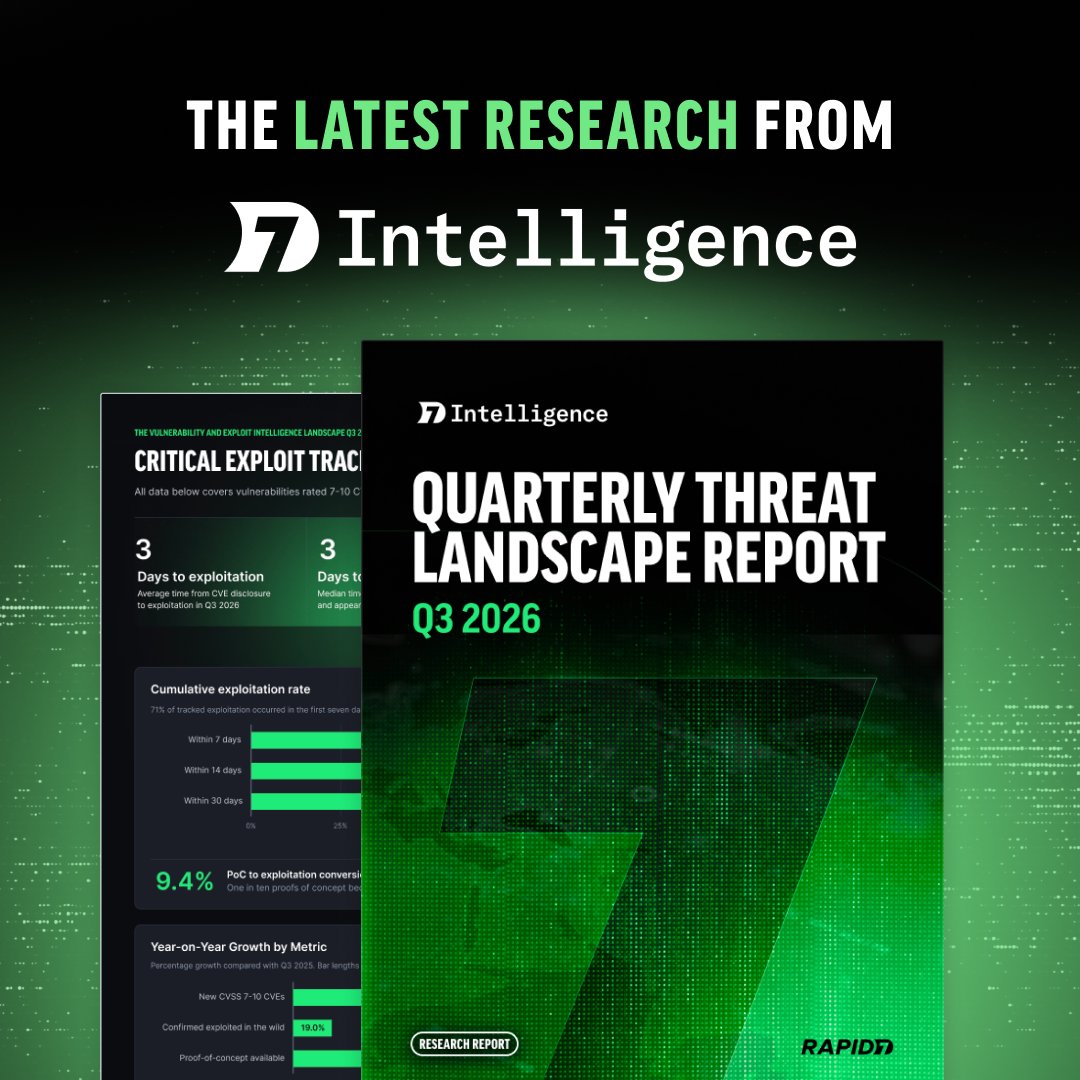
🔓 No login or click needed to break in. That's how 79% of the exploited vulns that Rapid7 Intelligence tracked in Q3 went down.
More ransomware activity, emerging AI threats, and attacker techniques in our new Quarterly Threat Landscape Report: https://t.co/Ns0LQz6PFv
🚨 On 10/21/26, the Node.js Project published a security advisory for CVE-2026-111497, an out-of-bounds write in the Brotli decoder bundled with Node.js.
The vuln has the potential to disclose memory or enable RCE. More in our blog: https://t.co/b7GF1Azv5J
Your team needs to make decisions about PHP2Shell. Conflicting advice makes that harder.
On October 30, Rapid7’s Douglas McKee and Rik Ferguson take the stage for 'PHP2Shell Mythbusters'.
Save your spot here: https://t.co/zkspopvGKB
Everyone is talking about PHP2Shell. There's far more to the story and it might not even be the biggest story this week. Well break it all down next week. Stay tuned...
Need reliable intel 👉 https://t.co/3bMq9a54BX
Episode 17 of Hacktics & Telemetry is live: Zimbra Zero-Days, AI Torture, and Catching Malmons (ft. @LambdaMamba)! Get it here: https://t.co/JWoqkmphaI
🚨 On 10/21/26, the #PHP project announced security releases for 2 critical vulns: CVE-2026-109618 & CVE-2026-109619.
Due to the extremely high deployment of PHP based web applications, exploitation in-the-wild is expected. More in our blog: https://t.co/HkQh3NvXry
79% of newly exploited high- and critical-severity vulnerabilities tracked by Rapid7 in Q3 required no authentication or user interaction.
What does that mean for your exposed assets? Download our newest Quarterly Threat Landscape Report here: https://t.co/Ns0LQz6PFv
🔎 What's YOUR most bothersome security myth?
Ep. 16 of Hacktics & Telemetry was all about #BruCON. We say 👋 to members of Rapid7's Intelligence and Metasploit teams, take in the Mechelen sights, and sign off with a rapid-fire extravaganza: https://t.co/FVUiEIyUaG
🚨 On 10/15/26, #BeyondTrust disclosed a critical auth. bypass vuln. in Remote Support (RS). In-the-wild exploitation of CVE-2026-102764 is confirmed to have occurred prior to this disclosure.
Stay up to date with the Rapid7 blog: https://t.co/DXdfs76qPJ
📧 Compromise of an enterprise mail server might look like unauthorized read access to your inbox, or even communications sent out on your behalf.
Dive into the first of a 4-part blog series concerning #Zimbra Collaboration Suite (ZCS) here: https://t.co/0XPOsk7PRD