Security is holding the entire industry back right now.
There are tonnes of great individuals & teams working on this, and we can't wait to see the maturity of the industry grow.
@bcherny How are you approaching review loops for PRs (review -> apply fixes-> review again)? Do you need to perform this cycle until no findings exist, or does it tend to just one shot the review and required fixes?
Kolan
Protocol Flaw in Kolan buyback hook lets attacker sandwich KLN purchases on Ethereum using a flash loan.
Full Report: https://t.co/qYo5AwzM06
Mechanism:
A 6.7 ETH flash-loaned buy inflated the KLN price, then two `accept()` calls made the hook buy about 2.31 ETH of KLN at that price, and the attacker sold into the extra buy pressure. Nothing in `accept()` limits who can trigger it, how much the price may move, or reads a time-weighted price, so the buyback's value went to the sandwicher.
Vulnerability class:
protocol-flaw (permissionless-buyback-spot-price-sandwich)
Broken invariant:
KolanHook.accept() assumed the V4 pool's spot price at call time was fair when it spent hook-owned ETH buying KLN, but any caller could move that price within the same transaction with flash-loaned capital before triggering the buyback and sell into it right after.
Exploiter: https://t.co/OKXKjABixW
Exploit tx: https://t.co/55l7P469GS
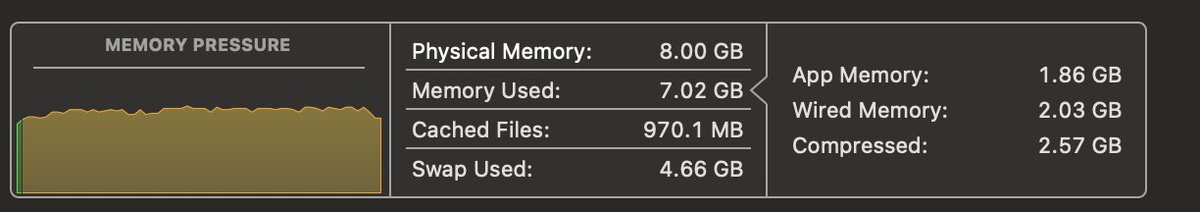
My laptop can’t keep up with the agents I’m running, so I’m about to upgrade.
But I get the feeling that in the next 6 months we will see the rise of agent-first OS. Is it worth waiting?
We have become so desensitised to the sheer volume and size of onchain exploits.
Imagine seeing in the news that someone performed a bank heist and ran off with 250 million? And got away with it?
This has happened multiple times this year in our industry.
Crypto won’t be trusted by normal people until security matures to the point where that’s shocking again.