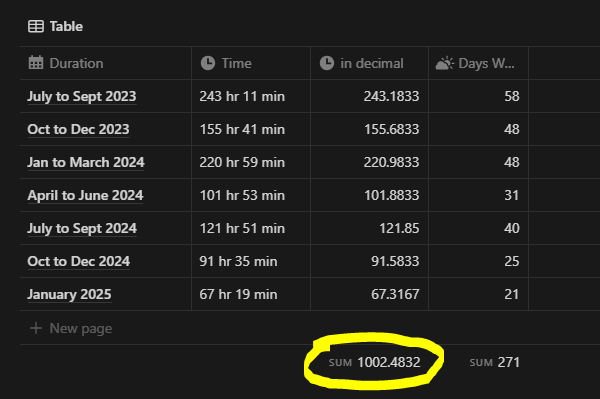
It's been 1000+ hours into bug bounties since the day I started.
Hunting: 1002 hrs
Cyberstudy: 363 hrs
Days worked: 271 days
Here's the top 59 lessons/advice/learning I've been giving myself since day one that have helped me reach where I am today (a thread 1/60):
#BugBounty
open url redirect bypass:
/login?url=https://*.whitlistdomain
bypass:
/login?url={anything}&url={anything}
Then it will jump to the third-party domain name to bypass restrictions.
#bugbountytips ,#bugbountytip
ATO of FB/OC accounts after stealing access_tokens ($44,250)
https://t.co/79z5LwgN2n
DOM-XSS in Instant Games due to improper verifications ($62,500?)
https://t.co/Hf63ib7g4x
ATO in Canvas Games due to weak cross window message Origin validations ($62,500)
https://t.co/BUziBmRbjj
I found a vulnerability that allowed me to unlock any @Google Pixel phone without knowing the passcode. This may be my most impactful bug so far.
Google fixed the issue in the November 5, 2022 security patch. Update your devices!
https://t.co/LUwSvEMF3w
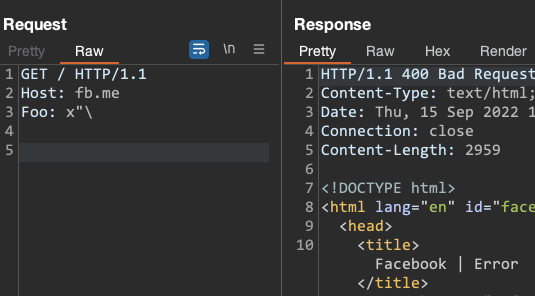
Facebook's servers give a mystery error if you send any HTTP header that contains " and ends in \. But not if you omit the " or the \ isn't at the end 🤔
This cryptic and likely pointless finding was brought to you by Backslash Powered Scanner
https://t.co/JrjhMeUETq