📢 IDA 9.5 is here: more platforms, more agentic power.
→ 3 new decompilers: Android Dalvik, Infineon TriCore and Qualcomm Hexagon
→ IDA MCP and Assist for AI-driven reverse engineering
→ Recursive decompilation across call graphs
→ IDA Home now includes 11 cloud decompilers instead of 2, at the same price
→ And much, much more
It’s one of our biggest releases yet. Active license holders can download it now from the Download Center.
https://t.co/sNYObPyqDz
AI-assisted research is killing embargoes. Coordinated disclosure will never be the same.
The industry used to have the luxury of testing or sitting on a fix for months. Not anymore. When everyone's using the same tools and the same intelligence to find vulnerabilities, you're not the only one finding that bug.
Product security and PSIRT need a serious rethink: less gatekeeping, more proactive evaluation of security posture, and shipping fixes continuously at scale.
The biggest impact will be in firmware and hardware, where disclosure timelines have historically stretched past 12 months. That mindset is a leftover from outdated processes and slow testing and bring-up environments.
My presentation at Hexacon is done ! Time for public disclosure.
Pictured below: remote unauthenticated code execution over-the-air (including the shell) on Proximus BBOX 3V+
Exciting work from @willzhou97 (Fellow, now full time!) and @bucketofkets on the Frontier Red Team. One of the cool parts of the job is seeing a future world early. We think this one is ~pretty underpriced.
"We should aim to harden our systems to make it difficult for such replicators to spread, but also prepare to deal with a world where they are here to stay."
Very excited to share details on the bugs used in our full chain Chrome exploit! We used three bugs (V8 corruption, V8 sandbox escape, and renderer sandbox escape via Crashpad). The third bug is my favorite!
📚 Slide decks from OB1 2025 & 2026 are live!
Catch up on talks you missed, revisit top sessions, or dive into the technical breakdowns. Most slides are up on GitHub:
👉🏻 https://t.co/zKKblw9Nx3
Huge thanks to all our speakers, sponsors, activity partners, and attendees!
To secure open-source software, we’re launching OSS Scanner.
We’ll use our frontier models to periodically scan opted-in open-source projects for vulnerabilities, at no cost. Our reports will provide a proof-of-concept, explanation, and suggested fix.
https://t.co/UFFrLUd25U
We’re expanding our Cyber Verification Program to give security professionals broader access to our most capable models.
Through this program, verified security professionals can access Claude Mythos 5.1, Opus 5.5, and Sonnet 5.5 with safeguards designed for defensive work.
We’re also opening up new tiers to allow for authorized offensive work, like penetration testing and red-teaming.
https://t.co/blaJtvxhJh
Thank you to @UnpromptedAU & @BSidesCbr for inviting me to speak. Being back down under was lovely! You can find the slides for my n-day automated pipeline talk here. I’m at OAIC this week if you want to chat about exploit dev in 2026 and beyond. https://t.co/LVpRd34i33
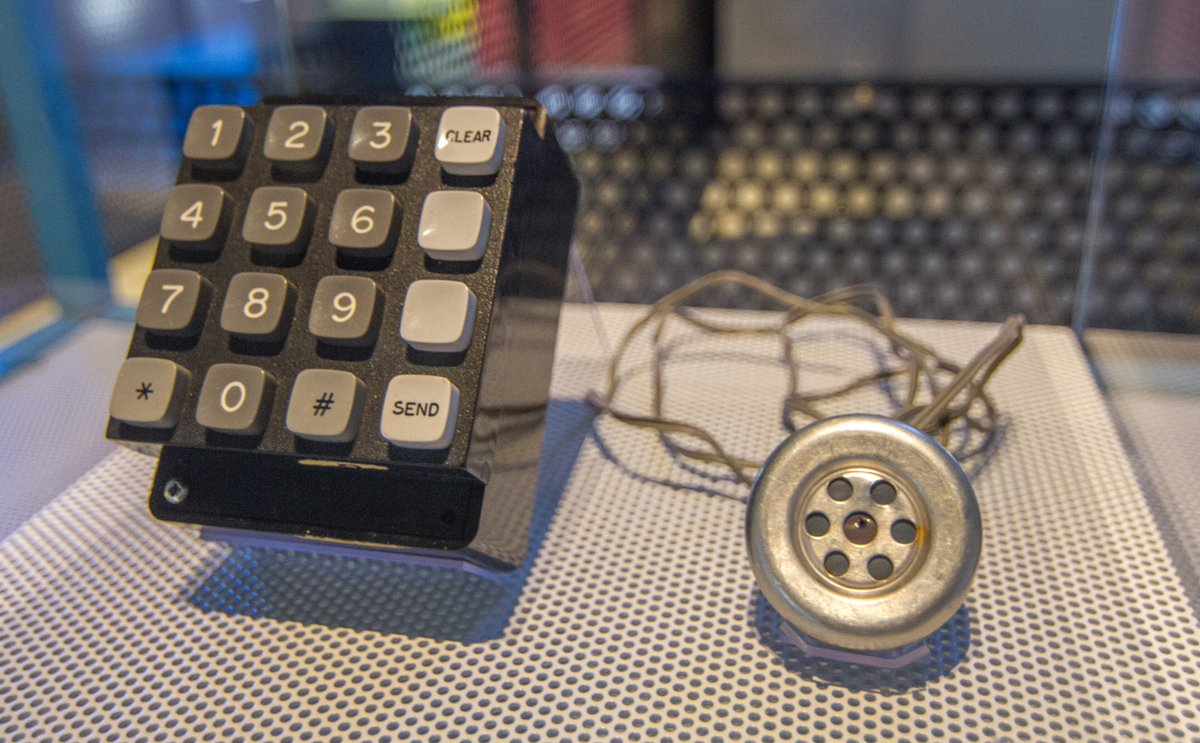
One more Phrack 73 leak for you!
Blueboxing Myths and Feelings: a nostalgic dive into phone phreaking’s golden age.
https://t.co/1BKEANXmEi
by @hackerschoice and @GammaTHC
Agree on verification, but I'd push it further. Memory safety is a symptom, not the cause. We got here because of design decisions and trade-offs we made all along, and you can see it in pretty much every recent Linux kernel disclosure.
Throwing more tokens at the attack surface won't save us either. Nothing we have today is ready for AI-driven vuln research at this scale, and finding and fixing bugs with AI doesn't change that.
What we actually need is redesign and architecture validation with AI, formal methods where we can, and not accepting attack surface at the design phase in the first place. That's just not how we build software today. Patching known bugs doesn't touch the root cause, and hardware has the same problem.