When I made my first course, it was just a fun project. Today, 130K+ Udemy students later, I’m excited to share my newest course: Enterprise AI Security & Governance
Free access for my network, DM me! Link below
#AISecurity#ISACA#Udemy
Which AI Persona is running your security team?
The Gambler: Strategic misalignment (all-in on hype)
The Skeptic: Neglect (falling behind the adversaries)
The Native: Panic-buying (bloated stack due to FOMO)
The Tinkerer: Delayed outcomes (endless fine-tuning)
#Cybersecurity#AI
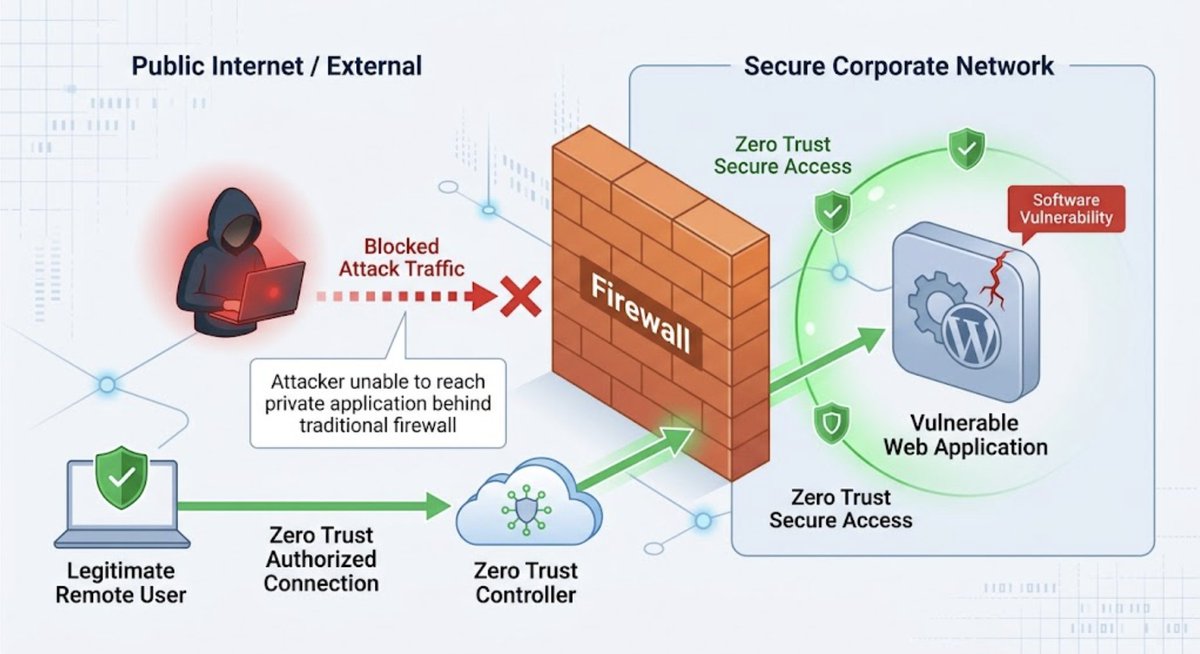
#Mythos can exploit your app in less than an hour!
Patching remains critical, but it's time to rethink why so many enterprise applications are exposed to the public internet.
#ZeroTrust isn't just about access anymore. It's about reducing the attack surface.
#CyberSecurity
You can have the most expensive security monitoring tools in the world, but if your front door is left wide open, security is just an illusion.
90% of cloud breaches start with basic hygiene: unconfigured S3s, missing MFA, and excessive permissions.
Lock down the basics first.
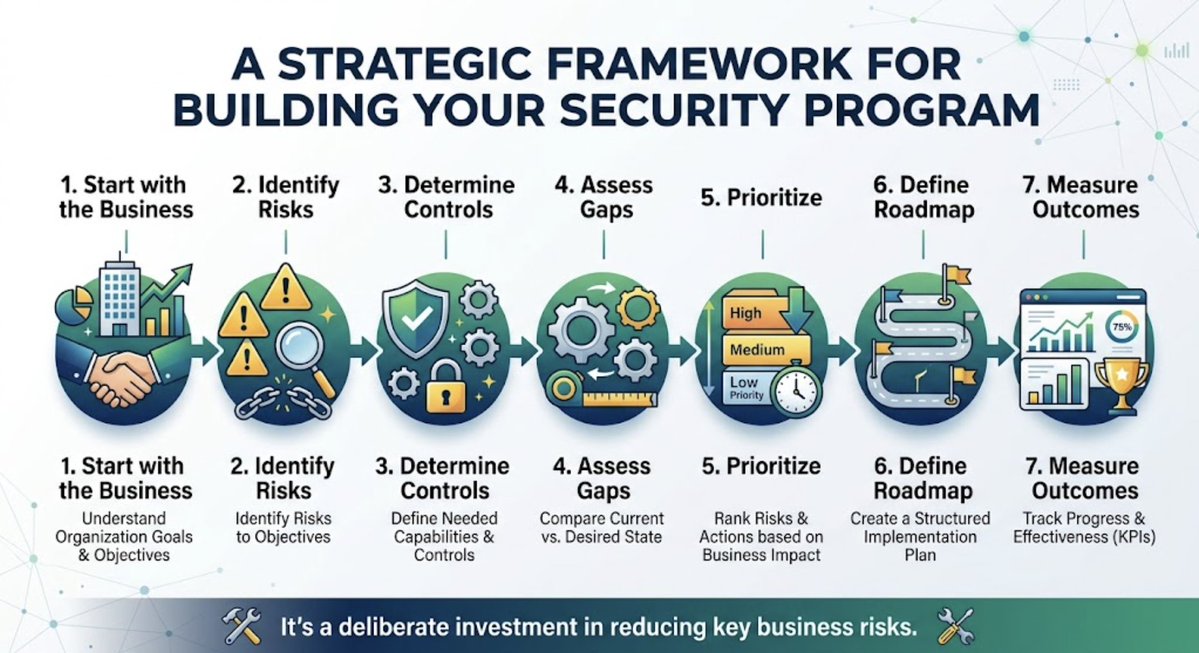
Most security programs fail because they start with tools, not business goals.
The right sequence:Business → Risks → Controls → Gaps → Priorities → Roadmap → Outcomes Security isn’t a tech stack—it’s a deliberate risk strategy.
#CyberSecurity#CISO#RiskManagement
Deploying AI/GenAI tools without managing its posture is just creating tech debt you'll pay for during an incident response.
https://t.co/bOGDXiK57v
#AISecurity#CyberSecurity#DataSecurity
ShinyHunters' campaign abusing OAuth tokens & Salesforce/Snowflake misconfigurations shows non-human identity is the top exposure gap.
SecureZona maps OAuth apps & cloud misconfigurations to lock down SaaS posture before integrations are abused.
#InfoSec#SaaSSecurity#SecureZona
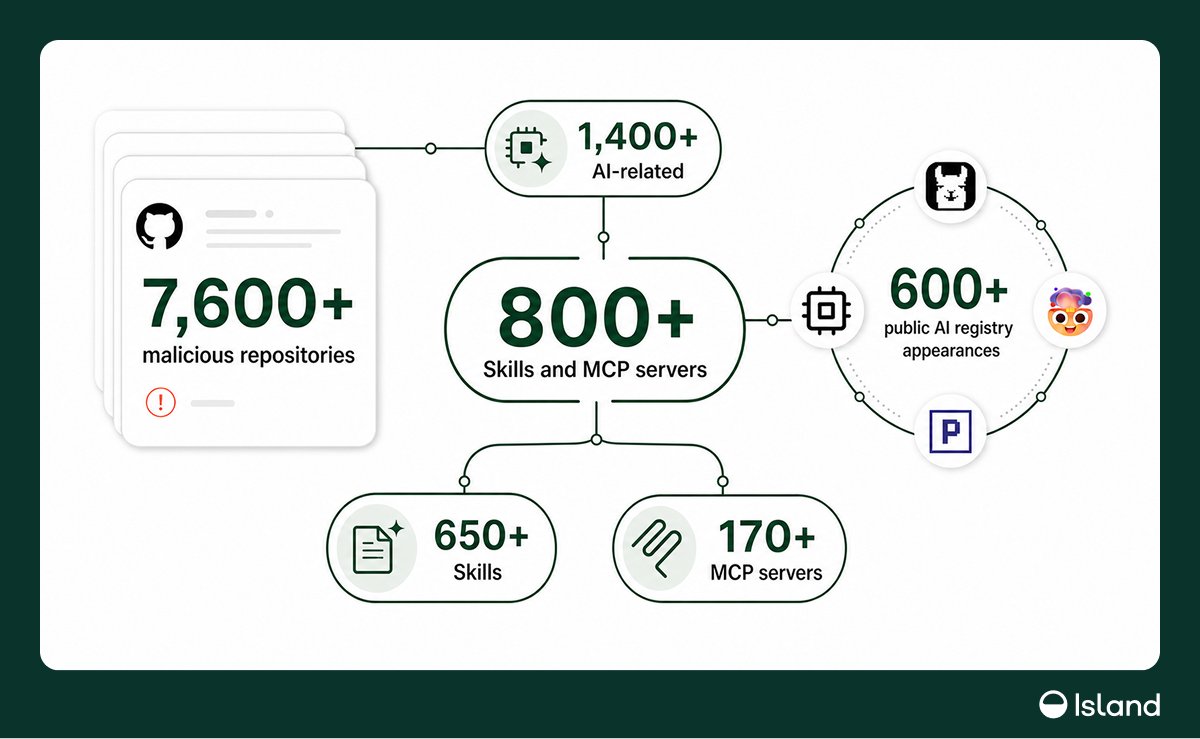
Massive blind spot in AI governance. Over 800 fake AI Skills and MCP servers were weaponized to drop StealC malware via assistant recommendations. Allowing agents to dynamically source tools without unified Security Posture Management (SPM) creates an unmonitored execution vector
AI assistants sometimes repeated attackers’ install steps.
Island’s Alon Biran says its team found ~7,600 malicious GitHub repos, 800+ posing as AI Skills or MCP servers. In tests, assistants surfaced them and sometimes repeated the install steps as legitimate guidance.
Read more: https://t.co/C2Tji6vV1D
@TheHackersNews "AgentBaiting" is supply chain poison for AI. Island’s research proves that LLM-based assistants can be tricked into recommending malicious MCP servers and GitHub repos directly into user workflows. AI-SPM must enforce strict, automated vetting on all third-party integrations.
Black Hat 2026 insights confirm attackers are shifting from passwords to token & cookie theft to bypass traditional MFA.
#SecureZona maps non-human identities, audits token permissions, and locks down cloud posture to block unauthorized session access.
#InfoSec#CyberSecurity
McGraw-Hill's data exposure shows how simple Salesforce misconfigurations let guests query internal data without credentials.
#SecureZona detects cloud & SaaS drift to lock down permissions before gaps are weaponized.
Vist: https://t.co/nyjODgbvGO
#InfoSec#SaaSSecurity
Cyber risk spans far past cloud misconfigs to SaaS, APIs, identities, AI & third parties.
Secure Zona unifies your entire posture in one platform: Discover exposure, Prioritize critical risks, Map compliance , Remediate faster
Less sprawl Total visibility
https://t.co/nyjODgbvGO
Active exploitation of a Metabase zero-day gives attackers unauthenticated admin access to connected data warehouses.
Patch self-hosted instances immediately. #SecureZona continuously maps external attack surfaces and data posture to eliminate exposure blind spots.
#InfoSec
Active exploitation of JetBrains TeamCity flaw gives attackers unauthenticated RCE on central build servers. Compromised CI/CD platforms jeopardize your entire software supply chain.
Patch TeamCity On-Premises and restrict build server exposure immediately.
#AppSec#DevSecOps