Author of ACTIVE MEASURES, RISE OF THE MACHINES, CYBER WAR WILL NOT TAKE PLACE, "Attributing Cyber Attacks," more. Johns Hopkins, Alperovitch Institute.
OpenAI, which failed to secure its sandbox and prevent 700 of its agents from hacking Hugging Face, met with electric utilities (while its role in the Hugging Face incident was still undisclosed) to convince them to bring OpenAI into their networks to help secure the grid.
What will happen first: rogue agents killing people — or extremists killing people because they’ve been radicalized against AI, partly with the help of out-there prophets of alignment doom?
One thing I mentioned only in passing in my Fable post is that, for long running tasks, Fable starts to develop its own dialect as its many agents and tasks reinforce themselves and make Claudish language ever more Claudish.
You need to ask it to report out in plain English.
Nearly my entire feed is criticizing Anthropic — 180 degrees from most of my feed adoring Anthropic post-Pentagon fallout, both times because the firm's leadership did what they believed in.
Very odd-sounding sourcing for this story, from "close to Anthropic," and no Pentagon or NSA official cited in here, not even anonymously https://t.co/aUcR4fMPWv
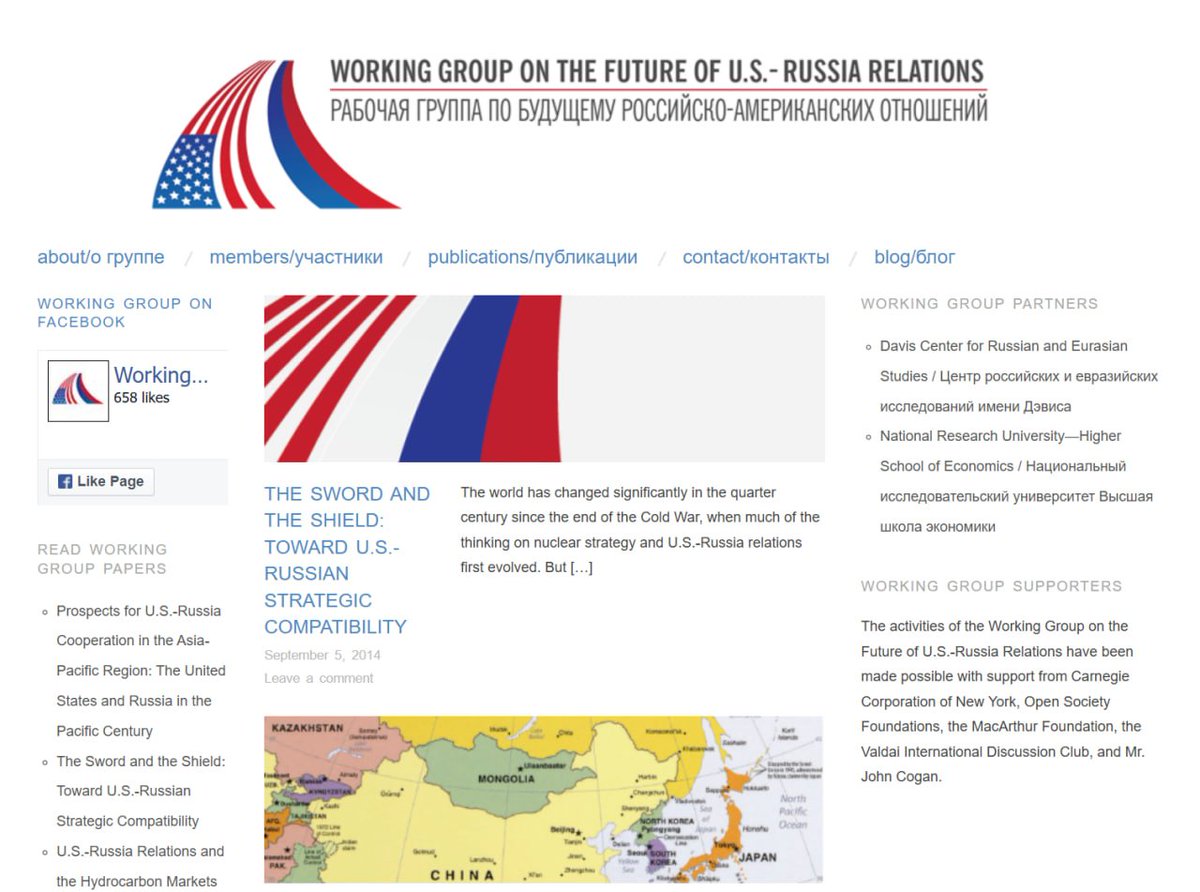
Davis Center's abandoned domain for the Working Group on the Future of U.S.-Russia Relations is now a "Russian dating site." Sweet that the new owner still pays homage to the original project & keeps US-Russia Future in the head
Our team at DeepMind is growing.
We've assembled a world class physics+material science team and are building an experimental lab.
If you want to solve real problems at the intersection of AI + material science to unlock a technological revolution - this is the place. Apply 👇
Big evolution of tradecraft here: a Russian active measures contractor is executing false flag operations by recruiting operatives *under false flag* — so they are unaware who paid them covertly, and indeed believe to be working for activists from third countries. Very Cold War.
This is a very important story on a recent evolution in tradecraft in Russian active measures, by @Martinlaineolen and team. I have also seen the full original leak, a few additional observations later today https://t.co/awiqQRp6fN
SDA planning docs and after action reports also mention OPSEC quite a lot, especially to enable infiltration. Temporary OPSEC before and during an operation matters; not so much after an operation.
Periodic reminder: the Shadow Brokers, masterful curators of one of the most devastating technical intelligence leaks ever, will turn ten years in August — and we still don't know who they were.
@vkamluk The original intent of the research was to play out the thesis that obscure malware could be used as hard evals for frontier mode capabilities. @vkamluk and @Gabeincognito ran an RE harness with access to tools, first autonomously, then w expert guidance.
A newly decoded piece of sabotage malware called Fast16, created before Stuxnet, was made to silently tamper with calculations in research and engineering software. Likely created by the US or an ally, and possibly used against Iran's nuclear program. https://t.co/jE045ejq6u