WP Activity Log started as a side project back in 2013. It was my first real attempt at building a WordPress plugin as a hobby, and it's where the @melapressHQ story started.
Fast forward to 2026, and three of our plugins have been nominated in the Security Plugins category at @thewpweekly Awards! These are WP Activity Log, WP 2FA, and Melapress Login Security.
Also, The Melapress Show has also been nominated in the YouTube Channel category.
There's a lot of work that goes into developing and improving these plugins, and more recently, into producing The Melapress Show. I'm particularly happy and grateful for our team.
Of course, none of this would be possible without the people who use our plugins, share their feedback, and support what we do.
If you use any of our plugins or enjoy watching The Melapress Show, everyone at Melapress would really appreciate your vote:
> https://t.co/aHFVP5obKU
Thanks to everyone who has supported us along the way!
CMSConf is happening this week in Gdynia, Poland!
Looking forward to meeting fellow #WordPress professionals, catching up with friends, and listening to some interesting talks.
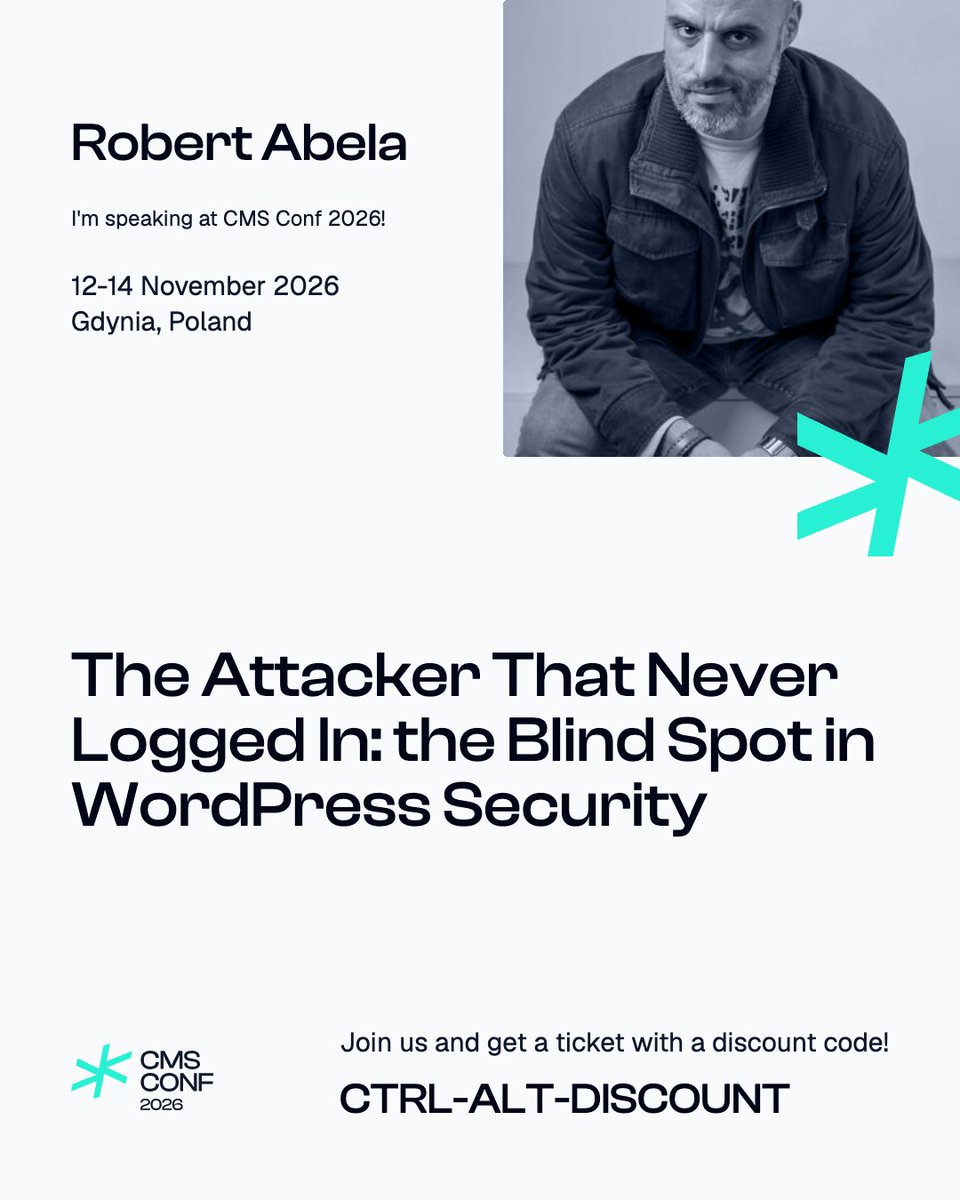
I'll also be speaking on Saturday about WordPress session hijacking.
We have plenty of tools to secure the login process, but what happens when an attacker steals an authenticated session cookie? They may be able to access your website without ever logging in.
I'll explain how this works, why it's difficult to detect, and what we can do to reduce the risks.
Saturday, November 14, Developer Track
If you're attending, come say hello!
And if you still need a ticket, there's a discount available here:
https://t.co/KwtPt7HT27
#CMSConf #WordPress #WordPressSecurity @CMSconf_
We've released another update of the @melapressHQ WP 2FA plugin earlier this week.
It's a maintenance release with several bug fixes, but we've also made a small improvement to the user experience.
You can now relaunch the setup wizard from the plugin settings.
The wizard is normally shown when you first install WP 2FA. It helps you configure authentication methods, MFA policies and requirements, and user exclusions.
While you can always change all these settings individually in the plugin's configuration, the wizard provides a quicker way to go through the main configuration options again.
A small but useful addition. As always, keep the plugin up to date.
#mfa #wordpress #plugin
Soon, I'll be joining @VitoPeleg from @atarim_io for a webinar about AI and WordPress.
We have developed an integration together to allow site admins to keep track of the changes made via AI.
We'll demonstrate AI making changes to a WordPress website, explain how those changes can be tracked, and give you a sneak peek at what we're developing.
Join us 17th November:
https://t.co/s0yjcLwMwu
We all still rely heavily on email, yet email deliverability remains a big problem.
When we launched WP 2FA, I never expected so many support tickets to be about emails not being delivered. And it's a common issue across #WordPress , not just our plugin.
So I invited Ken Simpson, CEO of @MailChannels to The Melapress Show to discuss #spam , SPF, DKIM, DMARC, email reputation, and what website owners can do to improve deliverability.
Plenty of useful advice in this episode. The episode will air later on today, at 4PM CET.
Your website sends a password reset link or a 2FA code, but the user never receives it. The problem isn't necessarily with your website.
In episode 62 of The Melapress Show, @robertabela speaks with @MailChannels CEO Ken Simpson about email deliverability, sender reputation, spam filtering, and how to investigate missing or delayed emails.
🗓️ Watch the new episode on November 5 at 4:00 p.m. CET.
As I explained at WordCamp US, one of the challenges with session hijacking is that it's difficult to detect. Someone could be using your #WordPress website account without you knowing.
That's why we've added a new option in Melapress Login Security to alert users of simultaneous sessions. With the latest update of the plugin users now receive email alerts when their account has simultaneous sessions, with an option to terminate all other sessions.
Simple notifications like these give users more visibility and control over their accounts, thus increasing the chances of detecting hijacked sessions.
A compromised DevOps engineer's laptop may have been the starting point of a security incident at Binance, with an estimated impact of $6.3 billion.
This is a good example of something I spoke about at @WordCampUS earlier this year: security doesn't stop at authentication.
User education, proper access policies, and visibility into what users do after logging in are just as important.
And this applies to any platform, be it WordPress or a Saas, and also to everyone, including experienced technical users.
Here is my WordCamp US talk on this topic: https://t.co/Ai1PHs1PU3
Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.
As an immediate precaution, Binance has:
- temporarily suspended deposits and withdrawals while security checks are completed;
- revoked the affected address authorisation;
- engaged law enforcement and blockchain intelligence partners to trace and recover funds.
Our teams are working around the clock to resolve this issue safely and thoroughly. We are working closely with our law enforcement partners to confirm the identity of these criminals and bring them to justice.
Please rely only on official Binance channels for updates. Please feel free to contact Binance Customer Support if you have any further questions.
https://t.co/ywB2mKFy0p
I really had a great time today on This Week in WordPress, episode #387.
Always a pleasure joining these discussions. Plenty to learn, good conversations, and a few laughs along the way!
I joined Nathan from @wpbuilds - the host, @TacoVerdo, and @i_cirkovic and we covered #WordPress security, AI, the WordPress credit system, PressConf, and most importantly, supermarket fridges!
Watch it here: https://t.co/93QCDB7qud
Going live on @wpbuilds within the next minute. A lot to talk about from the #WordPress world.
Join me and other WordPress people at https://t.co/T1n0yOdNTA
#podcast#WPWeekly
Can someone access your #WordPress dashboard without ever logging in? Unfortunately, yes.
We spend a lot of time securing WordPress logins with 2FA, strong passwords, and firewalls. However, if an attacker manages to steal an authenticated user's session cookie, they may not need to log in at all.
This is what I'll be discussing at @CMSconf_ on November 14.
My talk, "The Attacker That Never Logged In", covers how WordPress sessions work, session hijacking, why these attacks can go unnoticed, and what we can do to reduce the risks.
Saturday, November 14, at 13:20, Developer Track.
Talk details:
https://t.co/sWOgYHTkYI
If you haven't got your ticket yet, use CTRL-ALT-DISCOUNT for a discount.
#CMSConf
Need to give a third party access to #WordPress?
Create a temporary login link with Melapress Login Security. Choose the user role, expiry, number of uses, and post-login redirect.
No permanent WordPress users to remember to delete:
https://t.co/cR0wySx8vp
Is it still worth learning tools such as WP-CLI in the age of AI and agentic tools?
Everyone is talking about how #AI can automate everything, so why bother learning the tools?
Last week, I discussed this with Marcel Tanish on the Melapress #podcast . Marcel highlighted the truth that many people tend to ignore: AI agents can also make mistakes, especially when they lack context or the user doesn't fully understand what they're asking the AI to do.
How did Marcel come to this conclusion? He has years of experience using WP-CLI to manage complex WordPress websites, and he's seen this happen firsthand.
The key takeaway is that AI can do the work for you, but that doesn't mean you shouldn't understand what it's doing.
A very interesting discussion, especially if you're increasingly using AI to manage your #WordPress websites.
#wpcli
AI can generate WP-CLI commands, but do you know what they actually do?
In episode 61 of The Melapress Show, @robertabela and Marcel Tannich discuss WP-CLI, troubleshooting WordPress issues, automation, and using AI safely.
🎥 Watch the full episode:
@rmelogli@checkoutsummit I've been to a lot of summits. The attendees & talks are a big part of what makes them great. However, the atmosphere, the overall feel of an event make a huge difference.
And @checkoutsummit nailed that! It was definitely the best I've experienced.
As promised, here's a short video showing how easy it is to migrate from the discontinued Wordfence Login Security plugin to WP 2FA.
With the new importer in WP 2FA 4.2.0, users are automatically migrated the next time they log in, together with their existing 2FA settings and backup codes.
No downtime, no need to set up 2FA again.
If you prefer written instructions, we've also published a step-by-step guide covering the migration process, how to monitor its progress, and when it's safe to remove the old plugin:
> https://t.co/wxex2eycbU
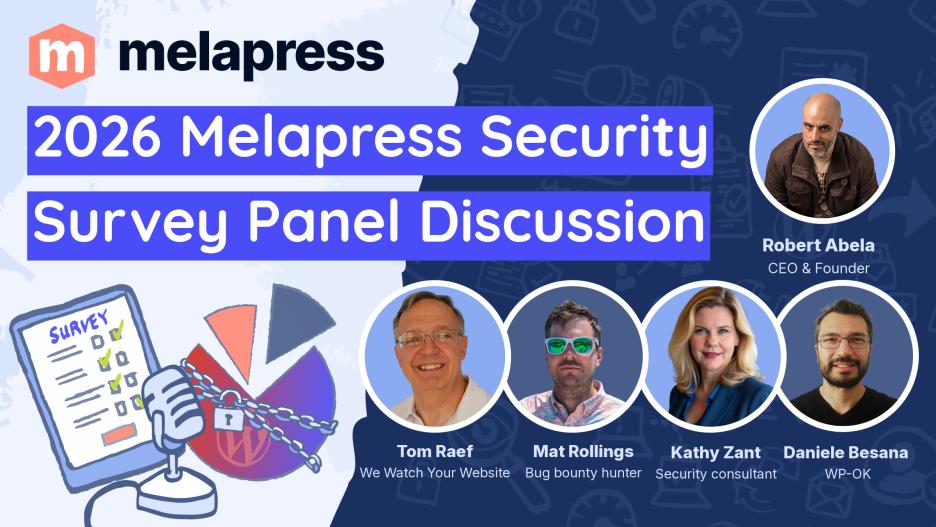
If you missed our panel discussion about this year’s #WordPress Security Survey, you are missing out.
A few days ago, we hosted the discussion with @kathyzant, @danielebesana, @stealthcopter, and Thomas Raef. They all approach website security from different angles: governance, hacked website cleanup, application security, bug bounties & malware.
That meant we could go beyond the survey numbers and discuss how the findings compare with what they actually see in practice.
Here is the panel discussion --> https://t.co/WigrbLxOGv
If you would like to see the 2026 WordPress Security Survey results before listening to the panel discussion, you can find them here --> https://t.co/mcTJicOXtw
What does the state of WordPress security look like in 2026?
Tomorrow, we’re publishing a recorded panel discussion with @robertabela, @WeWatch, @stealthcopter, @kathyzant & @danielebesana on the findings of the 2026 Melapress Security Survey.
🕓 Save the date: Sept 29, 16:00 CET
#WordPress #WordPressSecurity #Cybersecurity #MelapressShow
I'll be speaking at @CMSconf_ in Gdynia this November!
I’m looking forward to meeting new people from other CMS communities, but also to catch up with familiar faces from the #WordPress community, all of whom will be speaking; Mike Miler, @Bovelett, @rmelogli, @RaitisSevelis, @DjevaLoperka, Marcel Bootsman, and many others.
I'll also be giving a talk about WordPress session hijacking, and why securing the login process alone isn't always enough.
If you're attending, come say hello!
And if you haven't booked your ticket yet, you can get €30 off your ticket with this coupon code: CTRL-ALT-DISCOUNT.
#CMSConf #WordPress #WordPressSecurity
Earlier this week we released WP 2FA 4.2.0. It includes a number of improvements and bug fixes, as well as a security fix.
However, the main addition is an importer for Wordfence Login Security.
Wordfence Login Security, a free 2FA plugin, was discontinued a few weeks ago. We don't want users to be left without #2FA, so we've built an importer to make moving to WP 2FA as straightforward as possible, without any downtime.
If you're using Wordfence Login Security, simply install WP 2FA. It will automatically detect the plugin and prompt you to start the migration.
Users are migrated together with their backup codes, so they don't need to configure 2FA again or change how they log in. From their point of view, everything continues working as normal. No user action is required.
Administrators can also follow the migration progress and see how many users have already been migrated.
You can install the free edition of WP 2FA directly from your WordPress dashboard. Go to Plugins, click "Add Plugin", search for "WP 2FA", and install it.
Once activated, follow the step-by-step wizard.
If you need help with the migration, we're also offering one-to-one email support to free edition users until the end of this year.
Don't leave your #WordPress #website users without 2FA. Keep your website secure.
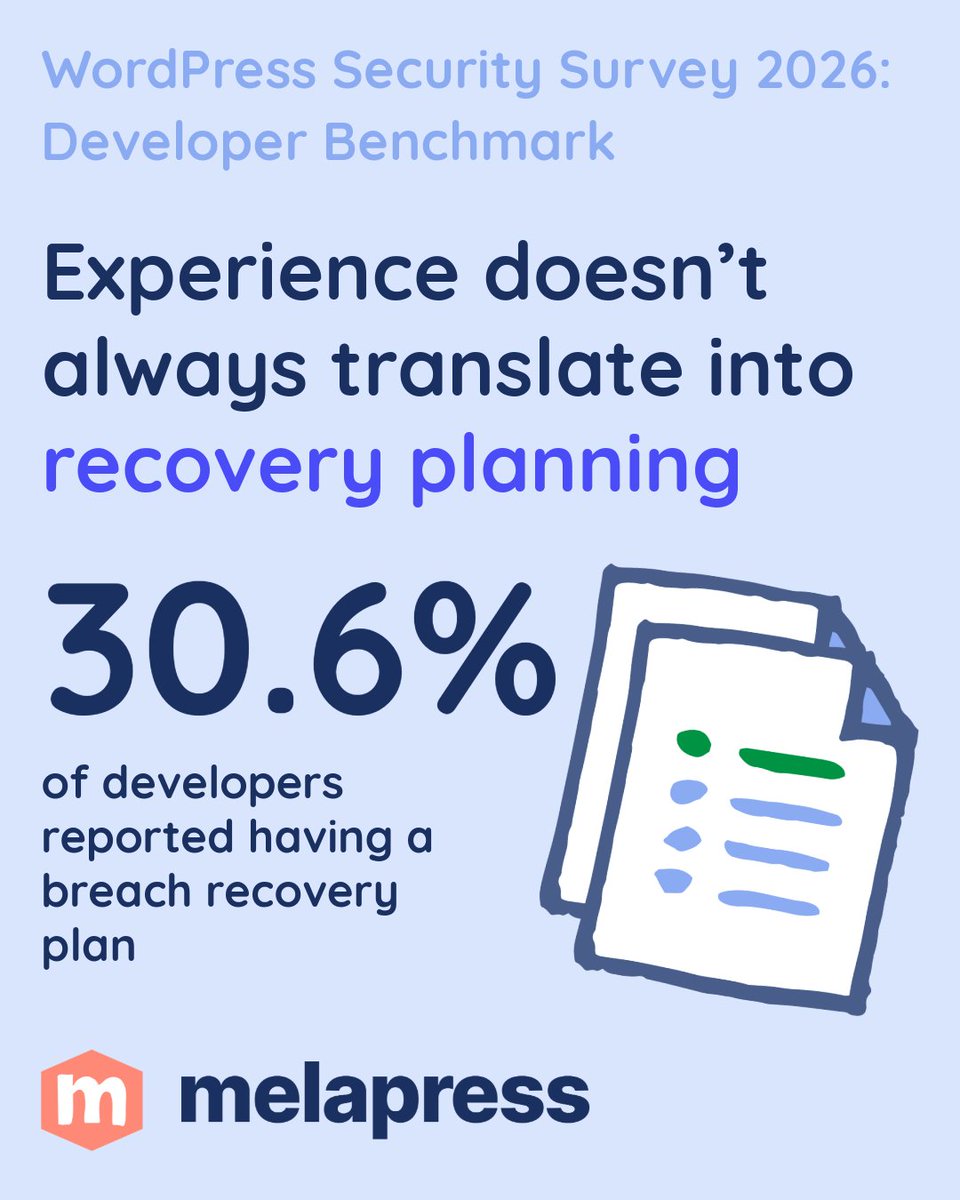
Four in five #WordPress developers in our 2026 Security Survey had experienced at least one known security incident. Of those, 72.2% had experienced two or more.
That doesn't mean 80% of WordPress websites experience security incidents. Developers often work across multiple websites, and some are brought in specifically after a website has been compromised.
What it does show is that security incidents are something many WordPress developers face in their work, even when they know what they're doing.
We've analyzed the findings in our new Developer Security Benchmark:
https://t.co/SWETmA7UtE
WP Activity Log has changed a lot since I first started working on it back in 2013.
What started as a side project is now our main plugin at @melapressHQ, with far more features, settings and options.
Now we're working on its next big change: a completely new UI.
We're at the beta stage and I'd really like feedback from our customers and free plugin users, before we go further and finalize the new UI.
If you'd like to test it, email me at [email protected] and I'll send you the latest beta.