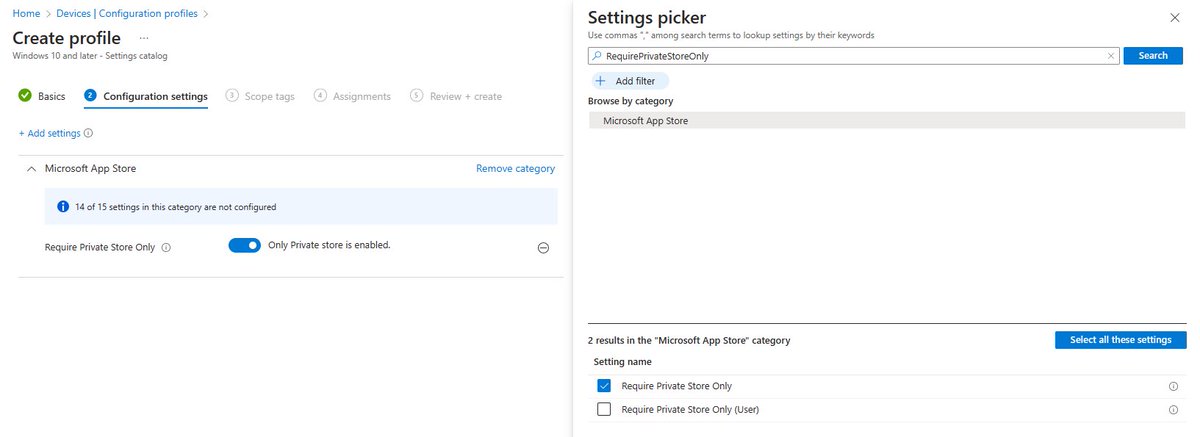
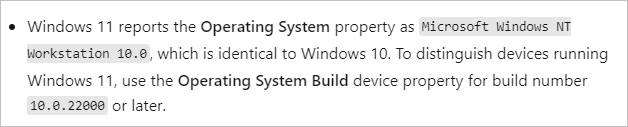
💡🧰 Does your organization want to block Microsoft store access for users, but still want to deploy the new #Windows365 app / Store apps via WinGet and benefit from auto-updates? Replace/remove all your existing GPO store based settings by the one just below, and your good from the user side (and IT admins can still deploy the app).
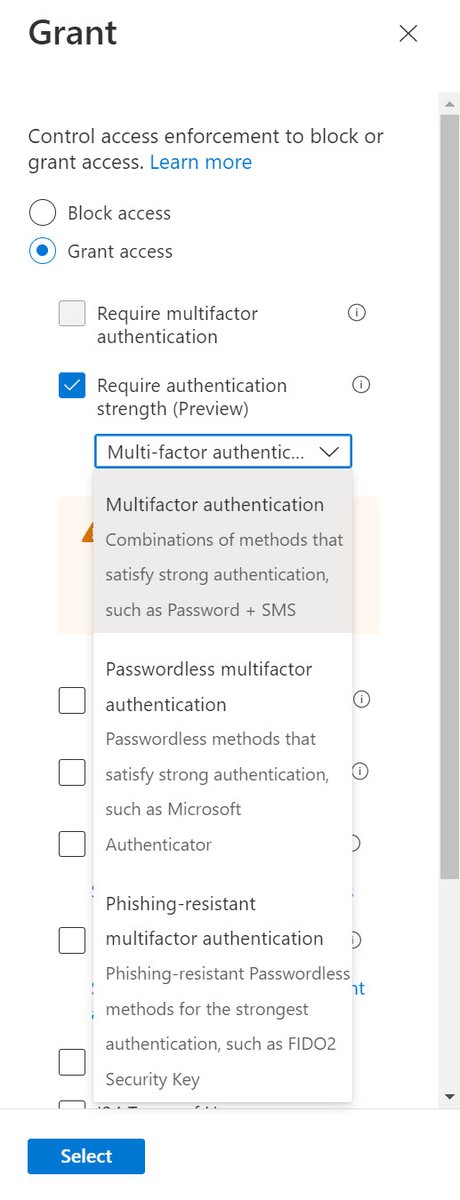
New grant control in #AzureAD#ConditionalAccess called "Require authentication strength" in preview. Allows you to specify requirements for MFA strength, and f.e. exclude SMS as MFA factor in certain CA policies
Finally there are more options to create dynamic AAD device groups. E.g. you now create a group with all HAADJ/co-managed devices.
Thank you @Scottduf for tweeting about the change.
I couldn't have guessed the correct deviceManagementAppId value. 😀
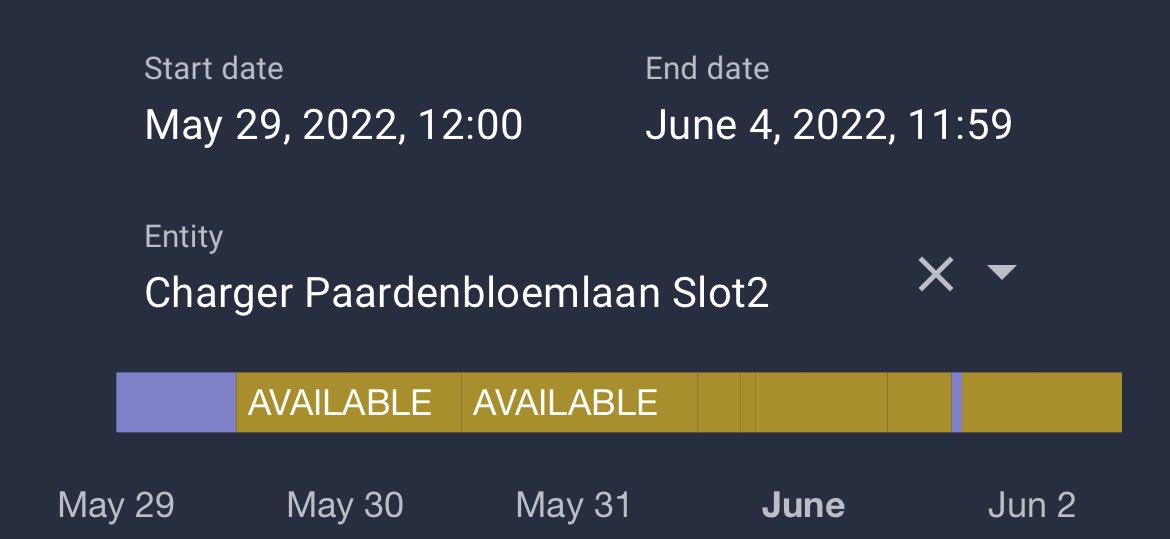
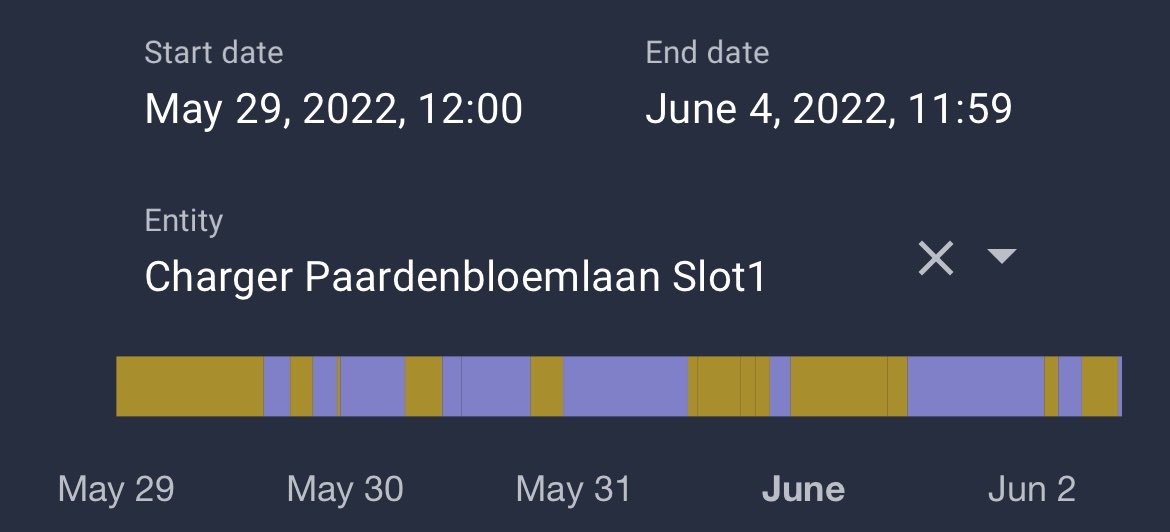
@TotalEnergiesBE , misschien moeten jullie toch eens werk maken van het schilderen van het 2e vak als jullie de laadpaal te Paardenbloemlaan in Ekeren willen laten renderen 😉 (zie foto’s in bijlage. Paars=bezet, Beige=beschikbaar)
Update 2203 for Microsoft Endpoint Configuration Manager current branch is now available. Enjoy!
Blog: https://t.co/DkdGLS6vvD
Docs: https://t.co/IbbSV61GVf
#MEMCM
📢 AVD Client Cleanup Tool/Script
Having issues updating/uninstalling your AVD client (RD Client for AVD or Windows Desktop client for AVD)?
▶️Use my script to cleanup the existing installation!
https://t.co/w6pS73QMER
Opensource on GitHub:
https://t.co/XIStEZpOQx
#MVPBuzz#AVD
We are proud to announce the availability of 𝗖𝗹𝗼𝘂𝗱𝗟𝗔𝗣𝗦 - Community Edition. A community created solution LAPS alternative with an integrated web portal front end, and support for #MSIntune managed devices. Docs are available here - https://t.co/tEANieMZjR #CloudLAPS