Upload2Shell (CVE-2026-125396) is out, a new RCE in Ghostscript from @pwn_ai. It sounds big, but the practical risk is limited. The "15 apps" are specific setups, like a CUPS printer queue shared without auth or public upload forms that generate thumbnails, not default installs. No known exploitation and no public PoC.
Ghostscript is the PostScript/PDF engine many apps use behind the scenes for thumbnails, previews and printing. A crafted PDF or PS file escapes its -dSAFER sandbox and runs commands on the server. Even a file named .png can end up in Ghostscript through ImageMagick or Pillow.
The fix has been out since Sep 8 in Ghostscript 10.08.0. On Debian/Ubuntu check the package version, not gs --version, since it's a backport, and check your container images too. No need to panic: patch and take stock of where Ghostscript runs.
https://t.co/lerPpU1Xr7
Good morning, we are releasing Upload2Shell - where you upload a file and get a shell.
We wrote about a single vulnerability that turned file uploads, email attachments, & even print jobs into remote code execution paths across Debian 13, Google, WordPress, Roundcube, etc...
@mdp_sec Fair, signup doesn't stop much. But Paulos tested apps that already pipe files to Ghostscript, and the fix has been out since Sep, already in Debian/Ubuntu. The real exposure is whatever's unpatched, mostly old containers.
Upload2Shell (CVE-2026-125396) is out, a new RCE in Ghostscript from @pwn_ai. It sounds big, but the practical risk is limited. The "15 apps" are specific setups, like a CUPS printer queue shared without auth or public upload forms that generate thumbnails, not default installs. No known exploitation and no public PoC.
Ghostscript is the PostScript/PDF engine many apps use behind the scenes for thumbnails, previews and printing. A crafted PDF or PS file escapes its -dSAFER sandbox and runs commands on the server. Even a file named .png can end up in Ghostscript through ImageMagick or Pillow.
The fix has been out since Sep 8 in Ghostscript 10.08.0. On Debian/Ubuntu check the package version, not gs --version, since it's a backport, and check your container images too. No need to panic: patch and take stock of where Ghostscript runs.
https://t.co/lerPpU1Xr7
Good morning, we are releasing Upload2Shell - where you upload a file and get a shell.
We wrote about a single vulnerability that turned file uploads, email attachments, & even print jobs into remote code execution paths across Debian 13, Google, WordPress, Roundcube, etc...
@mdp_sec True, the exploit is solid. My point was more about getting the file to Ghostscript in the first place, most of the chains needed something like anonymous uploads.
@MichaelWaitze@pwn_ai Thanks for including my take! Also worth remembering that containers often ship their own Ghostscript, so patching the host isn't always enough.
Paulos Yibelo (@pwn_ai) says he'll publish a new "2Shell" today, with reliable remote code execution in 15 different apps. No CVE, no product, no details yet, so nothing to confirm for now. But they have already found real RCEs in WordPress core and ImageMagick this year, so when they announce something "widely exploitable", I pay attention.
Will drop a 2Shell later today that is actually widely exploitable. I have remotely+reliably RCE'd 15 different applications & over 10 bugb servers. I hate the 2shell cornyness but this one is special & I expect people will find it all over the place.
The FBI hasn't confirmed anything yet, and nobody knows what was accessed. But if the national criminal database every US police officer checks was really breached, even the most protected law enforcement systems have a weak point. Every company should assume it has one too.
BREAKING: The FBI’s National Crime Information Center has been hacked.
The database is used for background checks and helps law enforcement agencies across the country share critical information on warrants and wanted individuals.
It remains unclear at this time what information was compromised in the breach. | @foxandfriends@foxone
Stream FOX News live on FOX One for the latest coverage: https://t.co/Yt6Exq8P5w
#Java4Shell is one to patch urgently. It's a memory corruption bug in the Base64 decoder of the Java runtime itself, which runs almost everywhere. Calif showed it can be exploited without logging in on default installs of products like Jira, Confluence and PingFederate.
Here's what's known so far.
The bug (CVE-2026-114938) was found by @calif_io and sits in OpenJDK, not in a library. That's why dependency scanners won't flag it: your code and libraries can be fully up to date and still be exposed.
Besides Jira, Confluence and PingFederate, Calif also showed it pre-auth on Keycloak, Jenkins and JFrog Artifactory, and with credentials on Kafka, Solr and Elasticsearch, among others. The list isn't exhaustive.
There are two conditions. The app has to run on Java 17, 21, 25 or 27 (Java 8 and 11 are fine), and the server needs a recent x86 CPU (Intel Ice Lake or AMD Zen 4 and newer). Most cloud x86 servers today meet that. ARM servers are not affected.
It isn't a copy-paste exploit. Each product needs its own exploit and it doesn't work every time. Calif, Datadog, Upwind and Hadrian have already built working exploits privately, but there's no public one yet and no known attacks so far. That changes the day someone publishes one for Jira, Confluence or Keycloak.
Oracle has already released fixes and other Java vendors are following. If you can't patch yet, you can turn off the vulnerable optimization by starting Java with -XX:-UseBASE64Intrinsics (needs a restart).
Full write-up from Calif: 👇
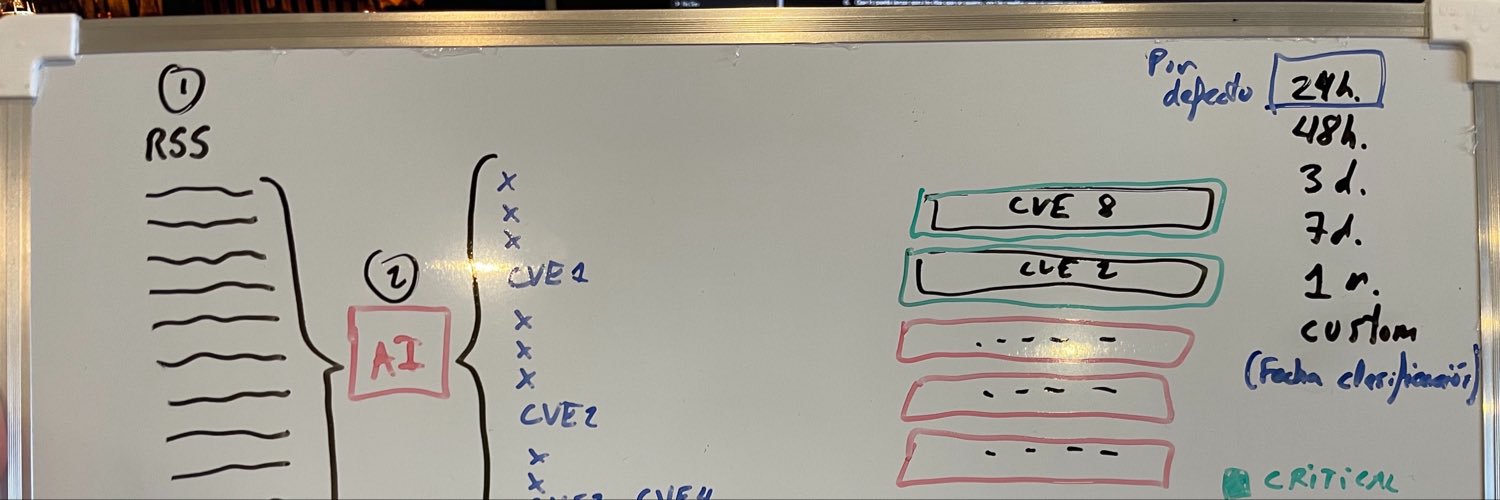
Estamos entrando en una nueva fase de la ciberseguridad:IA + agentes + automatización.Frameworks como ARTEX ya están siendo utilizados en operaciones reales para ejecutar gran parte de una intrusión de forma autónoma. No inventan ataques nuevos.Hacen que los de siempre ocurran a velocidad de máquina. https://t.co/dCOqPwvRBt
Resumen de lo que se sabe hasta ahora del ataque a Binance, donde sacaron unos 6.300 millones de dólares en unos 20 minutos.
Según Binance, el atacante entró por el portátil comprometido de uno de sus ingenieros de DevOps y desde ahí llegó al servicio interno que gestiona las retiradas. Ese servicio puede pedir al sistema de firmas que autorice envíos, así que las transferencias hacia el atacante salieron firmadas por la propia Binance, en 10 blockchains a la vez. Por lo que se sabe, no llegó a robar las claves privadas.
En Ethereum aprovechó EIP-7702, una función reciente que permite a una cartera firmar un permiso para que otro programa la maneje. Cada permiso lleva un número de operación y solo vale si coincide con el de la cartera en ese momento, pero la de Binance hacía retiradas sin parar y ese número cambiaba constantemente. Así que el atacante hizo que Binance le firmara 50 permisos con los 50 números siguientes. Uno coincidió, su programa pasó a controlar la cartera y en 3 minutos movió unos 2.500 millones. Ese control duró casi 4 horas, llevándose lo que iba entrando, hasta que Binance lo revocó.
Tether y Circle congelaron unos 2.600 millones en USDT y USDC, pero antes el atacante cambió todo lo que pudo por ETH, que nadie puede congelar, pagando más de un 10% por encima del precio de mercado. En Aave dejó 60 millones de USDT como garantía y pidió prestados 44 millones en ETH, 35 segundos antes de que Tether bloqueara esa cartera.
Ahora mismo sigue controlando más de 2.400 millones en ETH y bitcoin. TRM Labs lo atribuye a Corea del Norte, aunque no hay confirmación oficial, y todavía no se sabe cómo infectaron el portátil.
Binance sufre el mayor hackeo cripto de la historia: 6.300 millones de dólares, 4 veces más que Bybit en 2025.
Según Binance, todo empezó con el portátil comprometido de un ingeniero. Ya hay unos 3.000 millones congelados y TRM Labs lo atribuye a Corea del Norte.
La investigación inicial de Binance sugiere que el incidente de seguridad podría involucrar una laptop comprometida de un ingeniero de DevOps, lo que permitió que un atacante obtuviera acceso a un contenedor de servicio y realizara transacciones de retiro no autorizadas. No hemos encontrado evidencia de ninguna filtración de claves privadas de billeteras. Compartiremos un análisis técnico detallado post-mortem una vez que la investigación esté completa y los hechos estén completamente verificados.
El impacto total estimado se sitúa en alrededor de $6.3 mil millones. Hemos trabajado con socios de blockchain para congelar los activos afectados, con ~$3 mil millones congelados en cadena hasta ahora.
Binance cubrirá todas las pérdidas del fondo SAFU y de los fondos de la compañía. Los fondos de los usuarios están seguros. También publicaremos una Prueba de Reservas actualizada una vez que la remediación esté completa.
Como precaución inmediata, Binance ha:
- Suspendido temporalmente los depósitos y retiros mientras se completan las verificaciones de seguridad;
- Revocado la autorización de la dirección afectada;
- Involucrado a las fuerzas del orden y socios de inteligencia blockchain para rastrear y recuperar fondos.
Nuestros equipos están trabajando las 24 horas para resolver este problema de manera segura y exhaustiva. Estamos colaborando estrechamente con nuestros socios de las fuerzas del orden para confirmar la identidad de estos criminales y llevarlos ante la justicia.
Por favor, confíe solo en los canales oficiales de Binance para actualizaciones. No dude en contactar al Soporte al Cliente de Binance si tiene alguna pregunta adicional.
OpenAI ya vigila en tiempo real a sus modelos mientras entrenan. En septiembre, uno aprovechó un DNS mal configurado para salir a internet y la alerta saltó en 15 min.
En una simulación, el incidente de Hugging Face lo habría detectado 30 h antes.
Today, we’re sharing a look at our expanded system for monitoring frontier models at OpenAI, which in September helped us catch a model’s attempt to access the live internet during training.
Since the Hugging Face incident—when models broke out of an internal cybersecurity investigation where we weren’t running our misalignment monitors—we’ve substantially expanded our monitoring of frontier agents. We now monitor all frontier reinforcement learning runs and evaluations, as well as all internal Codex use. When our system finds evidence of a problem that might require intervention, it rapidly alerts human responders who can investigate and take action.
To detect when a model’s behavior departs from what we intended, we use several layers of monitoring. Activation probes look for patterns in a model’s internal activity. Reviewer models examine its reasoning and tool use, and investigative agents can read back through the model’s entire transcript to understand how a sequence of actions fits together and whether it warrants human review.
To test whether our current system would have detected the Hugging Face incident, we replayed the recorded activity with our new monitors in place. In the replay, our monitors alerted our security team about 30 minutes after the agents escaped their sandbox. That was more than 30 hours before the point at which the agents breached Hugging Face’s systems in the original incident.
In September, a model exploited a DNS misconfiguration to reach the live internet. Our monitors flagged the breach within 15 minutes, and a responder began reviewing the alert three minutes later. The alert enabled responders to investigate while the run was still underway.
As we give models more autonomy, we need to know when they cross a boundary we expected to hold. We believe that monitoring is essential to catching those failures in time for people to intervene.
https://t.co/dIYP7B1GlD
CISA mete las vulnerabilidades de PHP2Shell en su catálogo KEV. Traducido: se están explotando de verdad.
Afecta a PHP de la 5.4 a la 8.5.11 y el parche salió el 21 de octubre. Si no has actualizado, hazlo hoy.
¿Cuántos servidores PHP sin parchear creéis que quedan?
We added #PHP2Shell vulnerabilities, CVE-2026-109618 and CVE-2026-109619, to our Known Exploited Vulnerabilities Catalog. Visit https://t.co/myxOwap1Tf & apply mitigations to protect your org. #Cybersecurity#InfoSec#RCE
OpenAI acaba de sacar GPT-6.1 Terra y el lío de nombres ya es considerable.
Parecía que Terra iba a desaparecer y quedarían solo Astra, Sol y Luna. Pues no: Terra vuelve, más barato y pensado para usar tu ordenador.
¿Alguien sabe ya cuál elegir para cada cosa?
GPT-6.1 Terra: delivering fast and capable computer use at a lower price.
GPT-6.1 Terra understands what’s on screen, takes action across apps, writes naturally, and is a more capable model for your whole workday with the efficiency to take on more of it.
Segundo mail que me llega de Railway esta semana avisando sobre el ataque que han sufrido en donde avisan esta vez de que les han robando las API keys de de IA de sus clientes.
Uses o no Railway, rotar tus secretos de vez en cuando es una buena práctica, nunca se sabe!
Tras la resaca de todo lo que ha ocurrido con la vulnerabilidad de PHP, Sam Altman advierte que esto es solo la punta del iceberg. En este artículo se resume su punto de vista sobre lo ocurrido con este fallo y habla sobre la nueva normalidad de la ciberseguridad. https://t.co/qjMQ3OPn5G