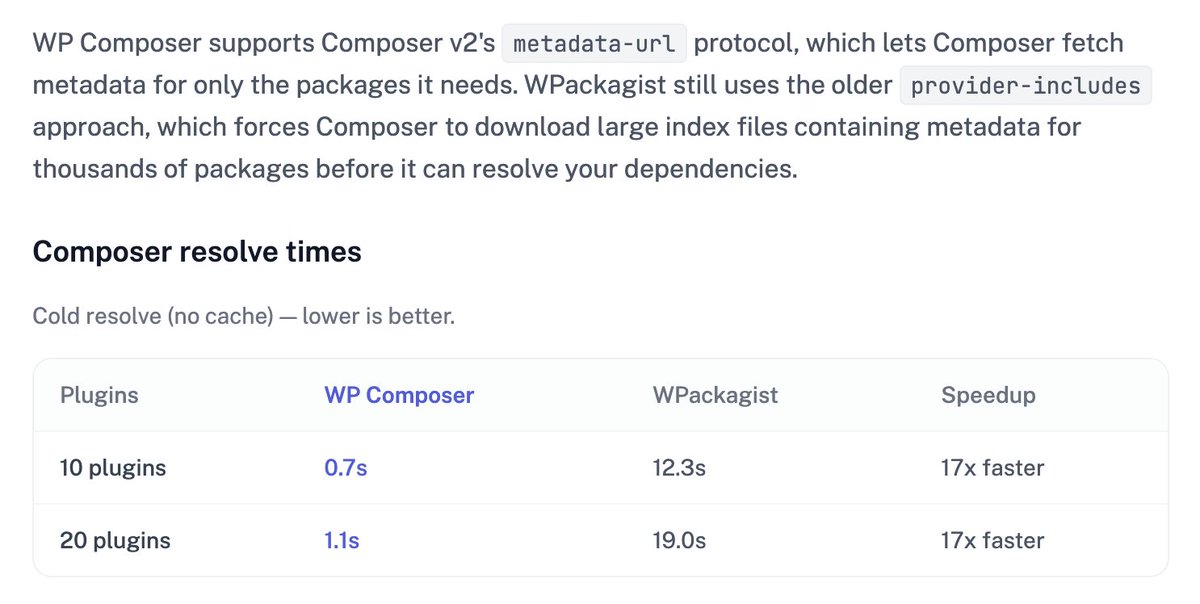
✨ We built WP Composer — an independent, open source Composer repository for WordPress plugins and themes, with 17x faster cold resolves than WPackagist
https://t.co/FbNpebs9me
PHP now recommends keeping session upload progress disabled until the next PHP release (CVE-2026-115560):
Trellis v1.32.2 makes this the default
https://t.co/vAxCR5bejy
PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 are out with fixes for two critical RCE vulnerabilities.
Trellis v1.32.1 switches PHP to https://t.co/aRWdhzZqQw, which had the patched builds first. Here's how to upgrade, or apply just the PHP change:
https://t.co/8jBjM35sVJ
Set session.upload_progress.enabled=0 till next PHP release to block an unlikely RCE vector (CVE-2026-115560). Already recommended for CVE-2026-109619 Wed, keep disabled. Only apps with non-default serialize_handler switching it to "php" at runtime can be affected. #php#phpc
PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 are out with fixes for two critical RCE vulnerabilities.
Trellis v1.32.1 switches PHP to https://t.co/aRWdhzZqQw, which had the patched builds first. Here's how to upgrade, or apply just the PHP change:
https://t.co/8jBjM35sVJ
An unofficial stopgap is going around:
Set session.upload_progress.enabled = Off until you can upgrade
PHP hasn't confirmed it helps, but WordPress and Laravel don't use the feature
Trellis steps are in the thread along with Cloudflare rules
https://t.co/DWi0XrluRf
PHP is shipping a security release tomorrow (Oct 21, 14:00 UTC) for two critical vulnerabilities
Re-provisioning Trellis won't upgrade PHP on its own. Here's how to upgrade once the PPA build is out:
https://t.co/Qcx896uNkQ
PHP's announcement: https://t.co/KngiQ5wVvc
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
PHP is shipping a security release tomorrow (Oct 21, 14:00 UTC) for two critical vulnerabilities
Re-provisioning Trellis won't upgrade PHP on its own. Here's how to upgrade once the PPA build is out:
https://t.co/Qcx896uNkQ
PHP's announcement: https://t.co/KngiQ5wVvc
Installing WordPress core with Composer? Make updates boring:
→ Let Renovate open a PR as soon as a new roots/wordpress version drops (see Bedrock's config)
→ Make sure your e2e tests cover critical paths
→ Automatically run them against seeded data on every dependency PR
WordPress sites on Roots Bedrock now work with every WordPress tool in Ploi. Ploi detects the web/wp core directory, so plugins, themes, search and replace, the WP-CLI console, cronjobs and clones all work. Override the core directory if your fork moved it.
Back when Sage used to be called the Roots Theme, it was one of the first WordPress themes to add a build system
v6.5.0 used Grunt and Bootstrap v3 with Less, and shortly after we added Bower 👴
🚨 PSA for Radicle users: the latest WordPress security releases (7.0.6, 7.1.2) break Blade views that live outside the theme directory. Front-end fatals with memory exhaustion, wp-admin looks fine.
Fixed in Acorn v6.3.0. Update before you update WordPress.
If you're using Radicle with WooCommerce, you'll also need changes applied to the sage-woocommerce package. See this topic for more details:
https://t.co/mOznOn9Lh4