The eMudhra incident has a disturbing detail: one private key was the number 4.
Eight weak CA keys exposed a fundamental failure in cryptographic key generation.
Are we validating security controls—or just trusting the process?
#eMudhra#PKI#CyberSecurity#DigitalCertificates
Your application never imported LiteLLM. The malware could still run.
@LiteLLM 1.107.0 used Python startup hooks to steal AI tokens, cloud credentials and SSH keys. Pandurang Terkar and I break down the attack at Gurucul.
#AISecurity#SupplyChainSecurity#LiteLLM
PHP2Shell: CVE-2026-109618 & CVE-2026-109619 expose critical RCE flaws in PHP core.
The overlooked risk? Exploitation can occur before application code runs.
Are you monitoring the runtime—not just the application?
#PHP2Shell#ThreatResearch
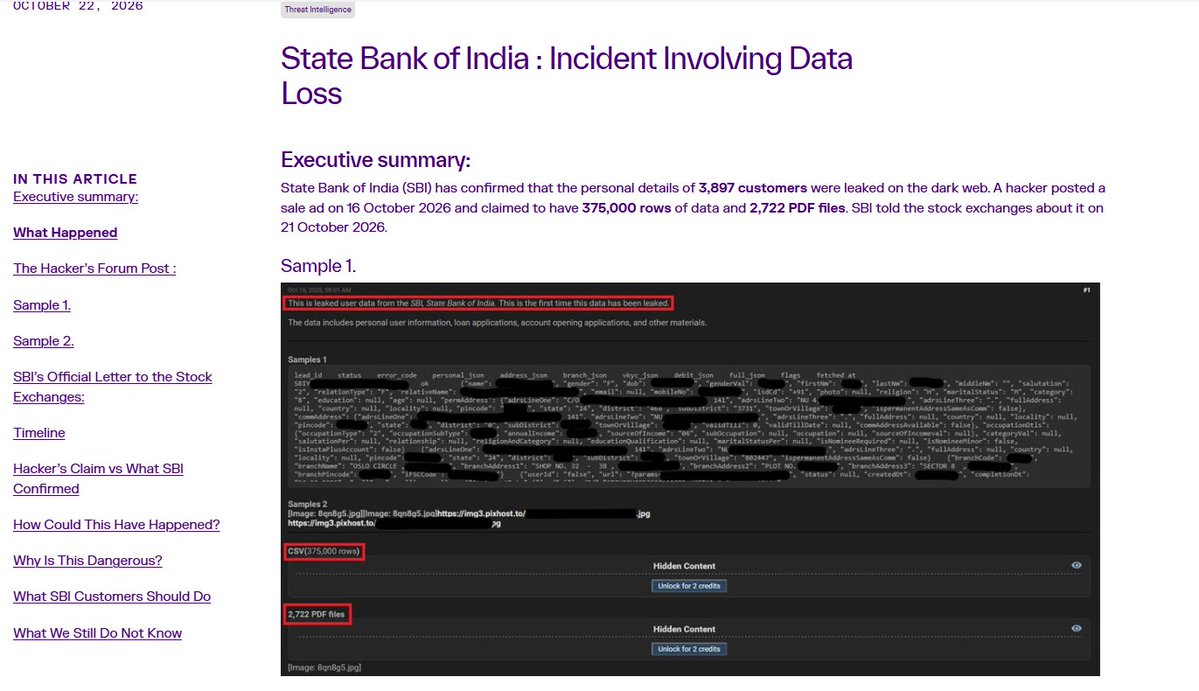
375,000 records surfaced. 3,897 contained customer PII. In breach analysis, that distinction matters.
The bigger risk? Genuine personal details can make phishing and bank impersonation far more convincing.
#ThreatIntelligence#CyberSecurity#sbileak
Read the full technical research on how Deno and SumatraPDF are abused to hide malware and bypass browser security protections:
https://t.co/jSih3eLjch
Attackers are abusing trusted tools like Deno and SumatraPDF to hide malware and steal browser session cookies.
This video breaks down how the attack works. Full research linked below. 👇
#ThreatIntel#MalwareAnalysis
Full technical research on CVE-2026-87491, including the BlueMoon exploit chain, threat actors, targeted countries and sectors, and detection considerations:
https://t.co/OsCQJOlP58
A Chrome zero-day with a public PoC is concerning.
A Chrome zero-day with public PoCs, active exploitation, multiple threat actors, and targets across 6 countries and 9 sectors is a different problem.
CVE-2026-87491 deserves a hunt, not just a patch.
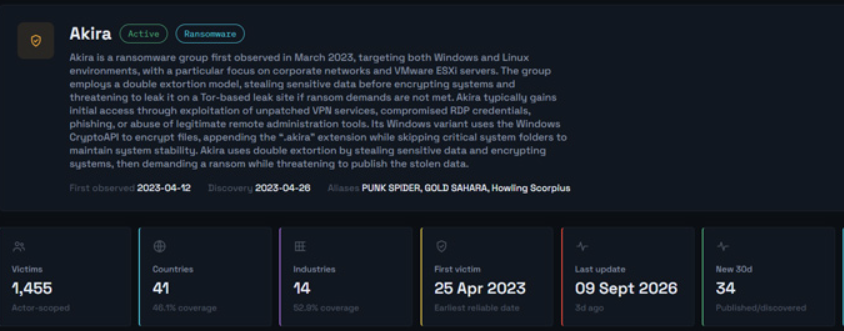
🚨 Akira is showing why modern ransomware demands more than IOC tracking.
RaaS, exploited CVEs, compromised credentials & double extortion are driving a scalable attack model.
Our latest Gurucul Threat Research analysis breaks it down.
#Cybersecurity#Ransomware
Attackers aren’t just appending payloads to images anymore—PureLogs Stealer is hiding inside valid PNG iTXt chunks, then using process environment variables for fileless execution.
If your SOC isn't monitoring environment variable writes, you're missing.
#ThreatIntel#Malware
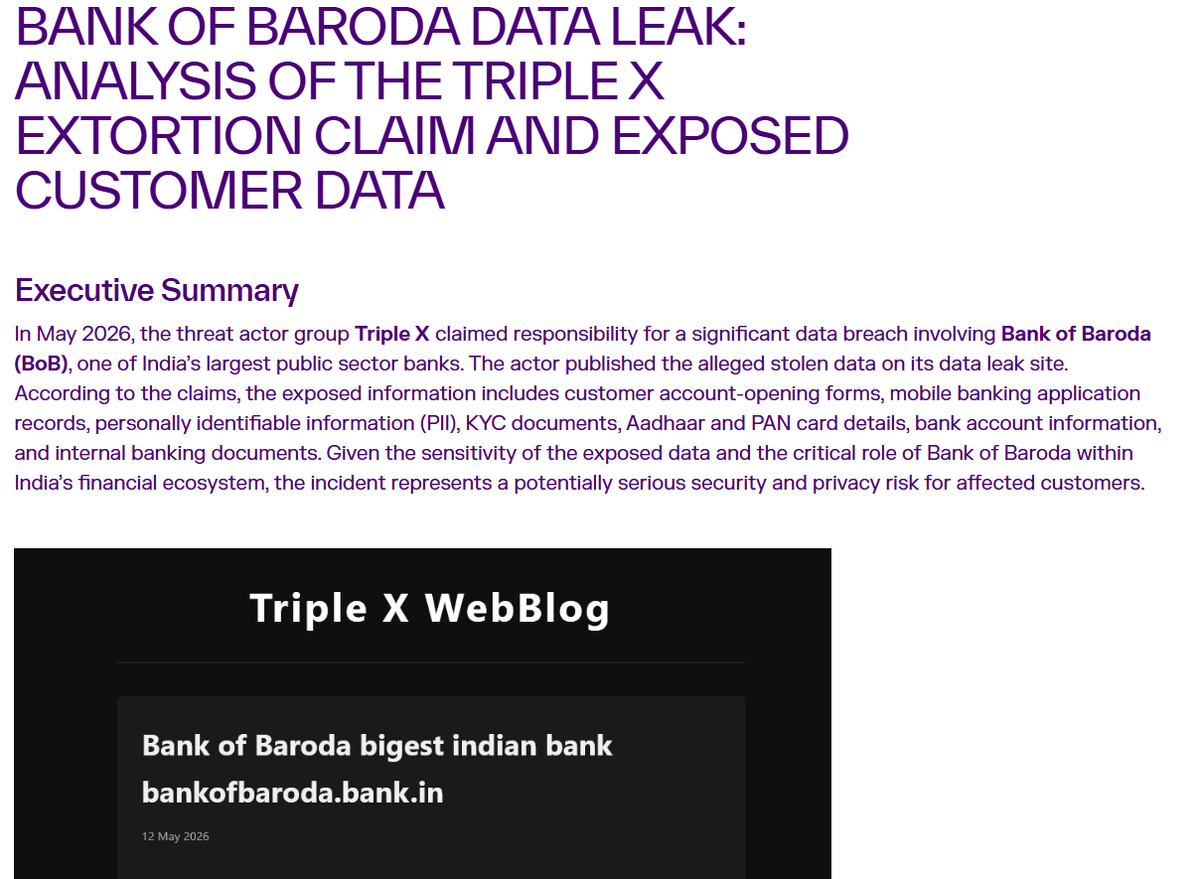
I expected the alleged Bank of Baroda incident to be another data leak story.
Instead, it reinforced something we've known for years:
Attackers don't need to break every control.
They only need to compromise the right identity.
Would your SOC detect that?
#CyberSecurity