"Capitalists in tech want to enjoy the same privileges as their peers in other sectors: increase worker productivity faster than they increase wages, so that they can get not just rich but stinking rich."
https://t.co/P7Jr67WXjC
2010: Eric Butler (@codebutler) announced Firefox extension Firesheep's release, making HTTP session hijacking on open Wi-Fi trivial.
Today the vast majority of websites have enabled HTTPS and other efforts have largely eliminated the risk. A security industry success! 🏆
No sé si es cierto que Djokovic hace lo que se cuenta en este hilo ni si lo hace por los motivos que se indican (no me sorprendería, considerando su afición por las magufadas). Lo que sí me sorprende es su repercusión, así que intento aclarar algunas cosas a continuación >>
Hate to break it to the new auditors out there, but the truth is that independent auditing is only financially rewarding for the top 10-20% whether through audit contests or private audits. You can check the @code4rena and @sherlockdefi leaderboards and try getting private audits to verify.
The harsh reality is that majority won’t make it in this field. There’s been a lot of hype around auditing and this is just a friendly reminder that it is a difficult and competitive field.
Legit call from the school:
Principal: I just wanted to touch base with you. Your daughter was baiting seagulls into the playground with gummy worms and actually caught one; Like in her arms. It did bite her—not hard, but I needed to inform you that we filed an incident report
“We just had shadow layoffs, and the number of PRs and number of design docs seemed to count into who was ranked as a low performer and let go.
So now people are creating tons of PRs - eg 1 PR/unit test - and design docs for every tiny change.”
Not surprising, and yet tragic.
Upgradability is a bug not a feature. In that case it was exploited for the 'good', but this should also highlight how much harm it can create. You can't achieve trustlessness if you always have to worry that a multisig upgrades its implementation contract. Full stop.
There’s no point in formally verifying something that can be trivially broken by a basic unit test suite.
Formal verification should be reserved for highly tested code
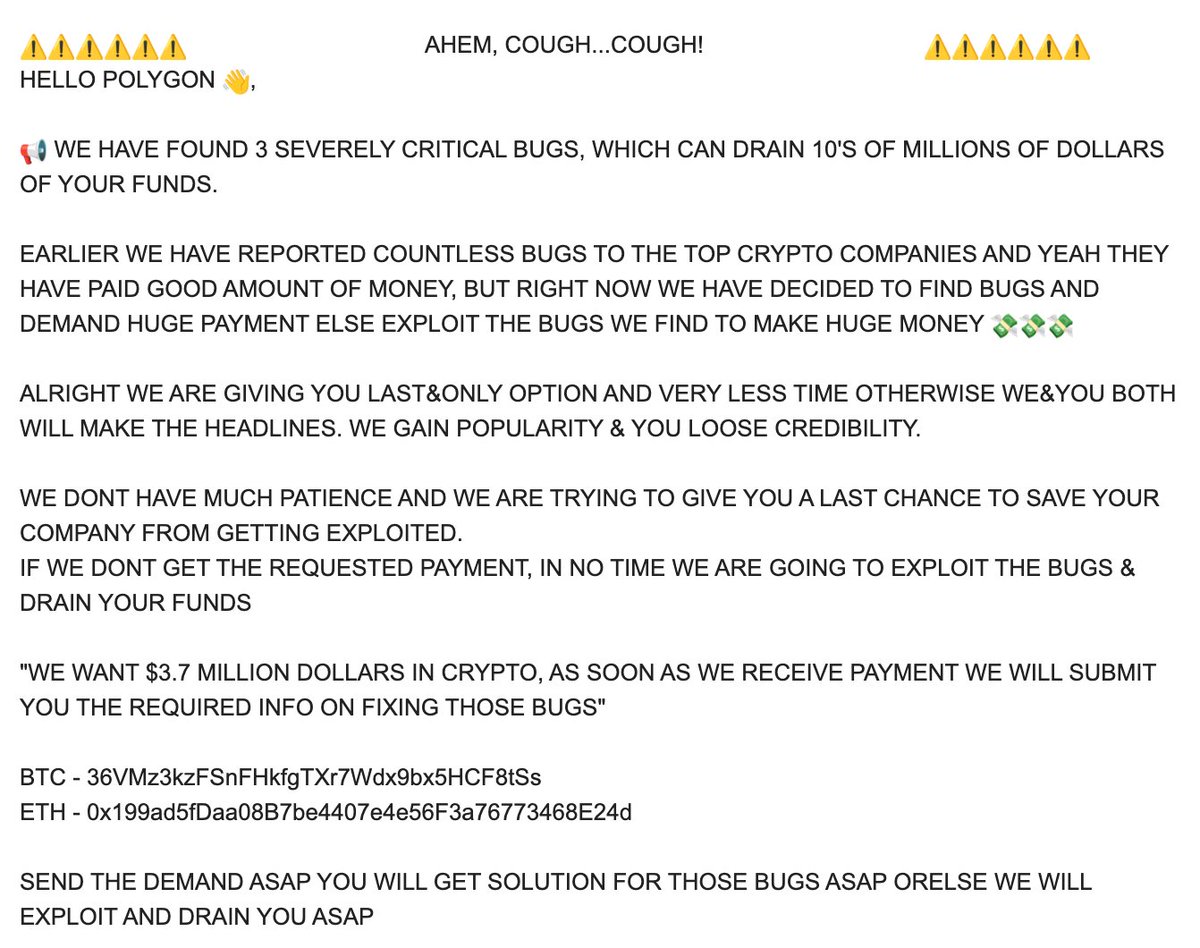
This has gotta be one of the most funny scam attempts I've ever seen.
We obviously asked them for more details and to submit the report via our bug bounty platforms, but this is worth a laugh for sure.