@elormkdaniel D- Security information and events manager
It's a security tool that collects, analyzes, and monitors security data from different systems to detect threats and respond to incidents.
I learned that Suricata is rarely used alone in enterprise. It’s usually paired with SIEM tools and dashboards. Suricata acts as the sensor, while other tools handle correlation and visibility. Hands on practice like this really deepens understanding.
#CyberSecurityJourney
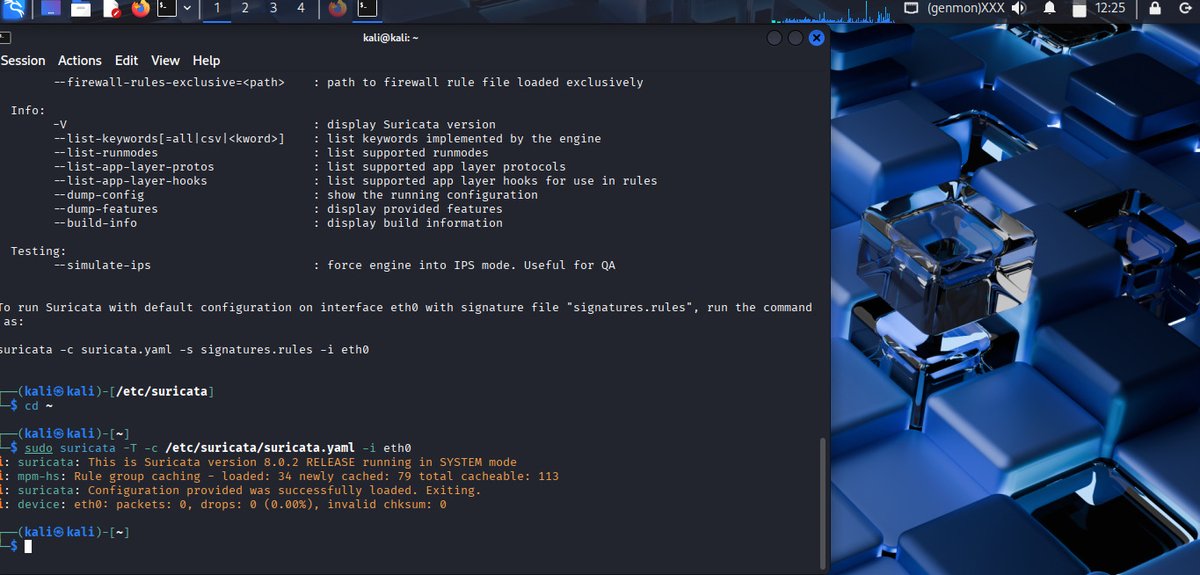
Recently, I’ve been working hands on with Suricata, an open source IDS/IPS used by large organizations to monitor network traffic and detect threats in real time. I understood its value much better after actually implementing it myself.
#CyberSecurity#Suricata#LearningInPublic
The biggest learning moment was writing my own detection rule for a simple DoS ping flood. Seeing Suricata trigger an alert based on a rule I created made IDS concepts click. It showed me how traffic patterns and rule logic drive real threat detection.
#Infosec#ThreatDetection
Setting it up involved more than just installation. I configured HOME_NET, enabled community ID, and pointed Suricata to custom rule paths. Doing this felt like building a small SOC environment and helped me understand how detection engines are tuned for real networks.
#BlueTeam
And if an attacker already has valid credentials or exploits non-password vulnerabilities, Fail2Ban won’t stop them at all. That’s why it should be combined with stronger SSH practices like MFA, key-based authentication, and strict firewall rules. Layered security wins.
#Linux
Intrusion Prevention Systems (IPS) play a major role in network security. They monitor traffic, detect malicious activity, and take action to block threats in real time. One simple but powerful IPS tool many people use today is Fail2Ban. 🛡️
But Fail2Ban isn’t perfect. Since it relies on IP addresses, attackers using rotating IPs, VPNs, proxies, or slow/brute-force attempts can reduce its effectiveness. If logs are delayed, or tampered with, Fail2Ban may completely miss the activity.
Fail2Ban works by monitoring log files for repeated failed login attempts. When it detects suspicious behavior like brute-force attempts on SSH, it automatically bans the IP address for a set period. It’s an effective first line of defense against attacks.
• Access Controls – limit who can view or change data, reducing accidental or malicious edits
• Audits – reviewing logs to ensure only authorized changes were made
Together, these controls keep data reliable and secure
#Infosec#CompTIA#TechTwitter
In cybersecurity, data integrity means protecting information from being changed, corrupted, or tampered with.
It’s all about making sure data stays accurate, complete, and trustworthy.
Here are key methods we use to maintain integrity 👇
#SecurityPlus#CyberSecurity
• Hashing – turns data into a fixed code; if the data changes even slightly, the code changes too
• Digital Signatures – confirm who sent the data and prove it wasn’t modified
• Checksums – help detect errors or alterations when data is being transferred
Step by step, concept by concept, I’m building a solid foundation in #cybersecurity.
Next, I’ll dive into Threat Vectors, Attack Surface, and Physical Security.
Excited to continue learning and share more lessons along the way!
#TechJourney#CyberSecurity#CompTIA
At this stage of Security+, the goal is understanding concepts, not just memorizing terms:
✅ Identify threats and vulnerabilities
✅ Map controls to the CIA principles
✅ Start thinking like both defender and attacker
This mindset is essential for building a strong foundation