Next-gen Privileged Access Governance Platform based on Zero Trust Security, Least Privilege Enforcement, Just-in-Time Access and Continuous Risk Assessment.
𝐀𝐜𝐭𝐢𝐯𝐞 𝐃𝐢𝐫𝐞𝐜𝐭𝐨𝐫𝐲, 𝐋𝐃𝐀𝐏 𝐨𝐧-𝐩𝐫𝐞𝐦. 𝐄𝐧𝐭𝐫𝐚 𝐈𝐃, 𝐆𝐂𝐏 𝐢𝐧 𝐭𝐡𝐞 𝐜𝐥𝐨𝐮𝐝. 𝐏𝐫𝐢𝐯𝐢𝐥𝐞𝐠𝐞𝐝 𝐚𝐜𝐜𝐞𝐬𝐬 𝐢𝐧 𝐛𝐞𝐭𝐰𝐞𝐞𝐧, 𝐚𝐧𝐝 𝐭𝐡𝐚𝐭’𝐬 𝐮𝐬𝐮𝐚𝐥𝐥𝐲 𝐰𝐡𝐞𝐫𝐞 𝐭𝐡𝐞 𝐠𝐚𝐩𝐬 𝐚𝐫𝐞. 🔐
Most enterprises now run hybrid. If your privileged access management tool treats AD and Entra ID as separate worlds, you end up with identity silos, policies that don’t match, and gaps where attackers get in.
That’s why native AD and Entra ID integration matter when you’re choosing a PAM platform. Here’s what it looks like in Securden Unified PAM:
✅ 𝐎𝐧𝐞 𝐢𝐦𝐩𝐨𝐫𝐭, 𝐞𝐯𝐞𝐫𝐲 𝐬𝐨𝐮𝐫𝐜𝐞. Bring in users, OUs, and groups straight from Active Directory, Entra ID, Google Workspace, or LDAP. No rebuilding your organizational structure by hand.
✅ 𝐂𝐨𝐧𝐭𝐢𝐧𝐮𝐨𝐮𝐬 𝐬𝐲𝐧𝐜. Add someone in AD and they’re onboarded automatically. Disable or delete them and that shows up in Securden too, so offboarding gaps close on their own.
✅ 𝐋𝐨𝐠𝐢𝐧 𝐰𝐢𝐭𝐡 𝐭𝐡𝐞 𝐢𝐝𝐞𝐧𝐭𝐢𝐭𝐲 𝐲𝐨𝐮 𝐚𝐥𝐫𝐞𝐚𝐝𝐲 𝐡𝐚𝐯𝐞. Use AD authentication and SSO, or federate through Entra ID SSO over SAML 2.0, alongside Okta, ADFS, Ping, OneLogin and others.
✅ 𝐁𝐮𝐢𝐥𝐭 𝐟𝐨𝐫 𝐡𝐲𝐛𝐫𝐢𝐝 𝐞𝐧𝐭𝐞𝐫𝐩𝐫𝐢𝐬𝐞𝐬. Directly supports AD-only, Entra ID-only, and mixed AD + Entra ID users.
✅ 𝐁𝐞𝐲𝐨𝐧𝐝 𝐨𝐧𝐛𝐨𝐚𝐫𝐝𝐢𝐧𝐠. Discover privileged accounts across your AD domain (local admins, domain accounts, service accounts), then lock them down with vaulting, Just-in-Time access, and recorded sessions.
The aim is simple: one control plane, consistent least privilege, and no standing admin rights, whether the system is in your data center or in the cloud.
https://t.co/VIQbrjfRsQ
#PAM #PrivilegedAccessManagement #ActiveDirectory #EntraID #GoogleWorkspace #ZeroTrust #IdentitySecurity #Cybersecurity #IAM
A failed patch. A suspicious login. An urgent request for admin access.
Three client issues. All before your MSP’s first scheduled support call.
As your client base grows, so does the work of keeping every environment protected. Can your team connect routine maintenance, threat detection, recovery, and access control without leaving gaps?
Our latest blog explores 7 𝐞𝐬𝐬𝐞𝐧𝐭𝐢𝐚𝐥 𝐭𝐨𝐨𝐥𝐬 𝐌𝐒𝐏𝐬 𝐧𝐞𝐞𝐝 𝐭𝐨 𝐦𝐚𝐧𝐚𝐠𝐞 𝐜𝐥𝐢𝐞𝐧𝐭 𝐬𝐞𝐜𝐮𝐫𝐢𝐭𝐲—what each contributes and what to look for when evaluating your stack.
From RMM and EDR to backup and privileged access management, see how these capabilities work together to strengthen protection across clients.
𝐖𝐡𝐢𝐜𝐡 𝐜𝐚𝐩𝐚𝐛𝐢𝐥𝐢𝐭𝐲 𝐧𝐞𝐞𝐝𝐬 𝐦𝐨𝐫𝐞 𝐚𝐭𝐭𝐞𝐧𝐭𝐢𝐨𝐧 𝐢𝐧 𝐲𝐨𝐮𝐫 𝐌𝐒𝐏’𝐬 𝐬𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐬𝐭𝐚𝐜𝐤?
Read the blog https://t.co/FC2wSEx5qS
#MSP #ManagedServices #Cybersecurity #PrivilegedAccessManagement
One technician changes teams, but retains access to previous clients. Another finishes an urgent fix, but their temporary privileges remain.
Now multiply those gaps across 𝟭𝟬𝟬+ 𝗰𝗹𝗶𝗲𝗻𝘁 𝘁𝗲𝗻𝗮𝗻𝘁𝘀.
For MSPs, growth brings more than additional systems to manage. It brings more access decisions, client-specific policies, and permissions to review.
How do you keep control as those responsibilities multiply?
Our latest blog explores 𝘀𝗶𝘅 𝗺𝘂𝗹𝘁𝗶-𝘁𝗲𝗻𝗮𝗻𝘁 𝗣𝗔𝗠 𝗽𝗿𝗮𝗰𝘁𝗶𝗰𝗲𝘀 to help you scope technician access, maintain client isolation, and apply consistent security controls at scale.
Read the blog https://t.co/5azU7QsL6F
#MSP #PrivilegedAccessManagement #MultiTenantPAM #MSSP
“𝐇𝐞𝐫𝐞’𝐬 𝐭𝐡𝐞 𝐩𝐚𝐬𝐬𝐰𝐨𝐫𝐝. 𝐈’𝐦 𝐨𝐟𝐟 𝐟𝐨𝐫 𝐭𝐡𝐞 𝐡𝐨𝐥𝐢𝐝𝐚𝐲𝐬.”
Sounds familiar? A routine holiday handover can be putting your business accounts at absolute risk.
A password pasted into a team chat can outlast the holidays. So can the “𝐭𝐞𝐦𝐩𝐨𝐫𝐚𝐫𝐲” access granted to a contractor.
Meanwhile, someone covering a colleague’s inbox could click an “urgent invoice” link and land on a fake login page.
Holiday coverages like these involve dozens of small decisions to keep work moving. Some can leave behind more access than anyone intended.
We’ve explored 𝟓 𝐰𝐚𝐲𝐬 𝐡𝐨𝐥𝐢𝐝𝐚𝐲 𝐫𝐨𝐮𝐭𝐢𝐧𝐞𝐬 𝐜𝐚𝐧 𝐞𝐱𝐩𝐨𝐬𝐞 𝐛𝐮𝐬𝐢𝐧𝐞𝐬𝐬 𝐩𝐚𝐬𝐬𝐰𝐨𝐫𝐝𝐬—including why even a long, complex password isn’t always enough.
Before you switch on your out-of-office, see what risks might be hiding in your team’s holiday routine.
👉 Read: 5 Reasons the Holidays Create an Opening for Password Attacks https://t.co/dLlFWeFlXT
#PasswordSecurity #Cybersecurity #SecurdenPasswordManager
Password resets constitute up to 50% of all helpdesk tickets. Stop wasting helpdesk personnel’s time on trivial tasks like password resets.
Eliminate the labor costs associated with password resets and free up your IT personnel for more meaningful tasks.
Securden Password Self Service allows users to reset the password and unlock domain accounts by themselves. With multi-factor authentication, empower users to regain access to their Active Directory, Entra ID, and Google Workspace accounts securely and seamlessly.
Eliminate password reset tickets, reduce helpdesk costs, and liberate helpdesk personnel. Try Securden Password Self Service today.
https://t.co/Au4EVSQkYs
#SelfServicePasswordResets #ActiveDirectory #EntraID #Azure #GoogleWorkspace
If you need a compatibility matrix to understand a single vendor's product suite, you aren't buying a platform. You’re buying a puzzle.
The B2B identity market is flooded with "platforms" that are just a collection of acquired tools.
• The demo? Flawless.
• The login page? Shared.
• The first upgrade? Total chaos.
A real platform isn't about product count. It’s about architectural consistency. 𝐎𝐧𝐞 𝐜𝐨𝐝𝐞𝐛𝐚𝐬𝐞. 𝐎𝐧𝐞 𝐜𝐨𝐧𝐬𝐨𝐥𝐞. 𝐎𝐧𝐞 𝐚𝐮𝐝𝐢𝐭 𝐭𝐫𝐚𝐢𝐥. 𝐎𝐧𝐞 𝐜𝐨𝐧𝐭𝐫𝐨𝐥 𝐩𝐥𝐚𝐧𝐞 𝐟𝐨𝐫 𝐡𝐮𝐦𝐚𝐧𝐬, 𝐦𝐚𝐜𝐡𝐢𝐧𝐞𝐬, 𝐚𝐧𝐝 𝐀𝐈.
When things are built from the same DNA, they have nothing to be incompatible with. If the chart is necessary, the seams are real.
That is the bet we made with the Securden 𝐈𝐝𝐞𝐧𝐭𝐢𝐭𝐲 𝐒𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐏𝐥𝐚𝐭𝐟𝐨𝐫𝐦.
Start where you need to—endpoint privilege, password management, or MFA/SSO. When you’re ready for Unified PAM, you flip a license key. Same instance. Zero migration drama.
Don't buy parts shipped separately. Buy a foundation.
#IdentitySecurity #PAM #IAM #SecurityArchitecture #Securden
👇 Checkout this https://t.co/yoGcoh2GDs
Disabling a compromised user account takes 𝐨𝐧𝐞 𝐜𝐥𝐢𝐜𝐤.
Replacing every affected machine credential takes 𝐰𝐞𝐞𝐤𝐬.
Last week, major browsers blocked eight eMudhra intermediate keys in under three days. No breach occurred, but it highlighted a massive industry blind spot.
We’ve structurally solved human identity with SSO, MFA, and automated governance. Yet 𝐦𝐚𝐜𝐡𝐢𝐧𝐞 𝐚𝐧𝐝 𝐀𝐈 𝐢𝐝𝐞𝐧𝐭𝐢𝐭𝐢𝐞𝐬—which vastly outnumber humans—still run on spreadsheets and trusted guessing games. Few organisations govern them as true identities.
That is the seam. And when a crisis hits, that seam rips wide open.
True security requires a single control plane for 𝐇𝐮𝐦𝐚𝐧, 𝐌𝐚𝐜𝐡𝐢𝐧𝐞, 𝐚𝐧𝐝 𝐀𝐈 𝐢𝐝𝐞𝐧𝐭𝐢𝐭𝐲. That is the architectural core of the 𝐒𝐞𝐜𝐮𝐫𝐝𝐞𝐧 platform. No re-installs, no complex migrations—just unified visibility and automated lifecycles.
Stop managing machine identities out of a spreadsheet.
If a root key you rely on disappeared tomorrow, 𝐡𝐨𝐰 𝐥𝐨𝐧𝐠 𝐰𝐨𝐮𝐥𝐝 𝐢𝐭 𝐭𝐚𝐤𝐞 𝐲𝐨𝐮 𝐭𝐨 𝐟𝐢𝐧𝐝 𝐰𝐡𝐚𝐭 𝐛𝐫𝐨𝐤𝐞?
https://t.co/UkLuJ60Evg
#IdentitySecurity #MachineIdentity #NonHumanIdentity #PAM #Securden
𝐏𝐢𝐜𝐭𝐮𝐫𝐞 𝐭𝐡𝐢𝐬: It’s Friday night, and a technician needs emergency access to a critical server. Granting permanent admin rights creates a massive security risk, but delaying access halts operations.
Standing privileged access is one of the biggest vulnerabilities in enterprise security, attackers never hack in, they always just log in. 𝐏𝐫𝐢𝐯𝐢𝐥𝐞𝐠𝐞𝐝 𝐀𝐜𝐜𝐞𝐬𝐬 𝐌𝐚𝐧𝐚𝐠𝐞𝐦𝐞𝐧𝐭 (𝐏𝐀𝐌) solves this using a need-based approach to eliminate the standing privileges that bad actors could exploit, and at the same time fulfilling the user's business needs.
𝐒𝐞𝐜𝐮𝐫𝐝𝐞𝐧 𝐔𝐧𝐢𝐟𝐢𝐞𝐝 𝐏𝐀𝐌 offers powerful 𝐉𝐮𝐬𝐭-𝐈𝐧-𝐓𝐢𝐦𝐞 (𝐉𝐈𝐓) 𝐀𝐩𝐩𝐫𝐨𝐯𝐚𝐥 𝐖𝐨𝐫𝐤𝐟𝐥𝐨𝐰𝐬 that follow well-defined request release controls with automatic password resets.
𝐓𝐢𝐦𝐞-𝐁𝐨𝐮𝐧𝐝 𝐀𝐜𝐜𝐞𝐬𝐬 𝐰𝐢𝐭𝐡 𝐅𝐮𝐥𝐥 𝐂𝐨𝐧𝐭𝐫𝐨𝐥: Enforce temporary, need-based access without slowing down business operations:
• 𝐂𝐮𝐬𝐭𝐨𝐦𝐢𝐳𝐞𝐝 𝐖𝐨𝐫𝐤𝐟𝐥𝐨𝐰 𝐓𝐞𝐦𝐩𝐥𝐚𝐭𝐞𝐬: Easily create multiple JIT workflow templates for privileged accounts and map them to specific users/groups.
• 𝐌𝐮𝐥𝐭𝐢-𝐋𝐞𝐯𝐞𝐥 𝐀𝐩𝐩𝐫𝐨𝐯𝐚𝐥𝐬: Set up to 3 tiers of approvers and require clear business justification before access is granted.
• 𝐅𝐥𝐞𝐱𝐢𝐛𝐥𝐞 𝐄𝐱𝐞𝐜𝐮𝐭𝐢𝐨𝐧: Support on-demand and advance requests, with rules for auto-approvals or exclusion lists for specific roles.
• 𝐀𝐮𝐭𝐨𝐦𝐚𝐭𝐢𝐜 𝐏𝐚𝐬𝐬𝐰𝐨𝐫𝐝 𝐑𝐞𝐬𝐞𝐭𝐬: Once the access period ends, Securden automatically randomizes credentials of the IT asset to block unauthorized reuse.
• 𝐒𝐞𝐬𝐬𝐢𝐨𝐧 𝐌𝐨𝐧𝐢𝐭𝐨𝐫𝐢𝐧𝐠 & 𝐀𝐮𝐝𝐢𝐭𝐬: Monitor active sessions live, terminate risks instantly, and maintain clean audit trails for compliance.
Grant the exact access needed only when required, and only for as long as necessary.
👉 𝐃𝐢𝐬𝐜𝐨𝐯𝐞𝐫 𝐒𝐞𝐜𝐮𝐫𝐝𝐞𝐧 𝐉𝐈𝐓 𝐀𝐜𝐜𝐞𝐬𝐬: https://t.co/PvPTyvmCDY
#AccessApproval #PrivilegedAccess #CyberSecurity #PrivilegedAccessManagement #PAM #JITAccess #Securden #ZeroTrust #LeastPrivilege #ITSecurity
In IT, a breach compromises data. In OT, 𝐚 𝐛𝐫𝐞𝐚𝐜𝐡 𝐬𝐭𝐨𝐩𝐬 𝐚 𝐩𝐢𝐩𝐞𝐥𝐢𝐧𝐞, 𝐝𝐚𝐫𝐤𝐞𝐧𝐬 𝐚 𝐬𝐮𝐛𝐬𝐭𝐚𝐭𝐢𝐨𝐧, 𝐨𝐫 𝐬𝐡𝐮𝐭𝐬 𝐝𝐨𝐰𝐧 𝐚 𝐰𝐚𝐭𝐞𝐫 𝐩𝐥𝐚𝐧𝐭.
Yet, most industrial environments still rely on shared SCADA passwords, ungoverned VPNs, and remote access tool sprawl. When IT and OT security fall through the gap, the risks are physical—and the stakes are massive:
• $𝟐.𝟑𝐌 average hourly cost of unplanned industrial downtime
• 𝟒𝟏% of ransomware attacks start through third-party access
• 𝟗𝟔 𝐝𝐚𝐲𝐬 average time to remediate an ICS compromise
How do you secure critical infrastructure without installing agents on fragile legacy systems or risking downtime?
𝐒𝐞𝐜𝐮𝐫𝐝𝐞𝐧 𝐔𝐧𝐢𝐟𝐢𝐞𝐝 𝐏𝐀𝐌 bridges the IT-OT security divide with a unified, agentless platform:
• 𝐔𝐧𝐢𝐟𝐢𝐞𝐝 𝐂𝐫𝐞𝐝𝐞𝐧𝐭𝐢𝐚𝐥 𝐕𝐚𝐮𝐥𝐭: Discover, manage, and automatically rotate credentials across both human and machine identities from one platform.
• 𝐒𝐞𝐜𝐮𝐫𝐞 𝐕𝐞𝐧𝐝𝐨𝐫 𝐆𝐚𝐭𝐞𝐰𝐚𝐲: Replace risky VPNs with JIT (Just-In-Time), time-bound access for contractors and OEMs—with zero standing privileges.
• 𝐀𝐠𝐞𝐧𝐭𝐥𝐞𝐬𝐬 𝐀𝐫𝐜𝐡𝐢𝐭𝐞𝐜𝐭𝐮𝐫𝐞: Connect seamlessly to legacy ICS, SCADA, and PLCs via RDP, SSH, VNC, and Telnet without touching the target system.
• 𝐅𝐮𝐥𝐥 𝐒𝐞𝐬𝐬𝐢𝐨𝐧 𝐑𝐞𝐜𝐨𝐫𝐝𝐢𝐧𝐠: Capture end-to-end audit trails and playback for every privileged session to meet compliance requirements out of the box.
Don't wait for a breach to secure your critical infrastructure.
👇 𝐒𝐞𝐞 𝐡𝐨𝐰 𝐒𝐞𝐜𝐮𝐫𝐝𝐞𝐧 𝐩𝐫𝐨𝐭𝐞𝐜𝐭𝐬 𝐲𝐨𝐮𝐫 𝐎𝐓 𝐞𝐧𝐯𝐢𝐫𝐨𝐧𝐦𝐞𝐧𝐭:
https://t.co/SVUG8XQrzn
#OTSecurity #IndustrialCybersecurity #ICS #SCADA #PrivilegedAccessManagement #CyberSecurity #CriticalInfrastructure #Securden #Compliance #NERCCIP
Uncontrolled remote access in OT environments isn't just a security risk - it's a threat to continuous production.
When technicians have excessive privileges, a single compromised remote session can trigger lateral movement across your entire network.
𝐒𝐞𝐜𝐮𝐫𝐝𝐞𝐧 𝐒𝐞𝐜𝐮𝐫𝐞 𝐑𝐞𝐦𝐨𝐭𝐞 𝐀𝐬𝐬𝐢𝐬𝐭 𝐛𝐫𝐢𝐧𝐠𝐬 𝐜𝐨𝐧𝐭𝐫𝐨𝐥 𝐛𝐚𝐜𝐤 𝐭𝐨 𝐎𝐓 𝐫𝐞𝐦𝐨𝐭𝐞 𝐚𝐜𝐜𝐞𝐬𝐬:
• Assign technicians and vendors access to specific endpoints through granular policies.
• Always start sessions with standard user rights and elevate privileges only when needed.
• Control which applications can be run or elevated on remote endpoints.
• Maintain accountability with detailed audit trails and privilege-elevation logs.
Alongside OT network segmentation, these controls help limit opportunities for privilege misuse and reduce the potential impact of compromised support accounts.
Give every support session a clear scope: the approved endpoint, the required permissions, and visibility into the work.
Explore Securden https://t.co/sWTgChZfsM
#OTSecurity #SecureRemoteAccess #LeastPrivilege #Cybersecurity #Securden
In our experience working with organizations across all industry verticals to enforce the Principle of Least Privilege, one challenge consistently stands out: pushback form developers against “No Local Admin.”
We understand the frustration.
𝐈𝐦𝐚𝐠𝐢𝐧𝐞 𝐛𝐞𝐢𝐧𝐠 𝐢𝐧 𝐭𝐡𝐞 𝐦𝐢𝐝𝐝𝐥𝐞 𝐨𝐟 𝐝𝐞𝐛𝐮𝐠𝐠𝐢𝐧𝐠 𝐚𝐧 𝐚𝐩𝐩𝐥𝐢𝐜𝐚𝐭𝐢𝐨𝐧, 𝐢𝐧𝐬𝐭𝐚𝐥𝐥𝐢𝐧𝐠 𝐚𝐧 𝐒𝐃𝐊, 𝐨𝐫 𝐜𝐨𝐧𝐟𝐢𝐠𝐮𝐫𝐢𝐧𝐠 𝐚 𝐥𝐨𝐜𝐚𝐥 𝐝𝐚𝐭𝐚𝐛𝐚𝐬𝐞 - 𝐨𝐧𝐥𝐲 𝐭𝐨 𝐛𝐞 𝐛𝐥𝐨𝐜𝐤𝐞𝐝 𝐛𝐲 𝐚𝐧 𝐚𝐝𝐦𝐢𝐧 𝐩𝐞𝐫𝐦𝐢𝐬𝐬𝐢𝐨𝐧 𝐩𝐫𝐨𝐦𝐩𝐭. What should take minutes becomes a helpdesk ticket and a frustrating wait.
At Securden, we believe security shouldn't come at the cost of developer productivity.
With 𝐒𝐞𝐜𝐮𝐫𝐝𝐞𝐧 𝐄𝐧𝐝𝐩𝐨𝐢𝐧𝐭 𝐏𝐫𝐢𝐯𝐢𝐥𝐞𝐠𝐞 𝐌𝐚𝐧𝐚𝐠𝐞𝐫 (𝐄𝐏𝐌), developers can elevate the specific executables, files, folders, and scripts they need without permanent local admin rights.
𝐄𝐧𝐟𝐨𝐫𝐜𝐞 𝐭𝐡𝐞 𝐩𝐫𝐢𝐧𝐜𝐢𝐩𝐥𝐞 𝐨𝐟 𝐥𝐞𝐚𝐬𝐭 𝐩𝐫𝐢𝐯𝐢𝐥𝐞𝐠𝐞. 𝐄𝐦𝐩𝐨𝐰𝐞𝐫 𝐝𝐞𝐯𝐞𝐥𝐨𝐩𝐞𝐫𝐬. 𝐊𝐞𝐞𝐩 𝐞𝐧𝐠𝐢𝐧𝐞𝐞𝐫𝐢𝐧𝐠 𝐦𝐨𝐯𝐢𝐧𝐠.
𝐓𝐫𝐲 𝐒𝐞𝐜𝐮𝐫𝐝𝐞𝐧 𝐄𝐧𝐝𝐩𝐨𝐢𝐧𝐭 𝐏𝐫𝐢𝐯𝐢𝐥𝐞𝐠𝐞 𝐌𝐚𝐧𝐚𝐠𝐞𝐫
https://t.co/RNqEI37ZK5
#EndpointSecurity #LeastPrivilege #DeveloperSecurity #Cybersecurity #PrivilegeManagement
The rise of autonomous AI agents means we are no longer just managing human administrators. With the power to query databases, deploy code, and move money at machine speed, AI agents have become the ultimate non-human administrators—and a critical Privileged Access Management (PAM) blind spot.
In our latest post, we break down why traditional PAM needs to evolve from vault-centric credential management to runtime privilege orchestration, covering:
𝐓𝐡𝐞 𝐀𝐈 𝐏𝐀𝐌 𝐁𝐥𝐢𝐧𝐝 𝐒𝐩𝐨𝐭: Why shared identities, service accounts, and over-permissive access leave organizations exposed.
𝐖𝐡𝐲 𝐀𝐠𝐞𝐧𝐭 𝐏𝐫𝐢𝐯𝐢𝐥𝐞𝐠𝐞 𝐢𝐬 𝐃𝐢𝐟𝐟𝐞𝐫𝐞𝐧𝐭: Autonomous decision-making, machine-speed blast radii, and privilege chaining.
𝐄𝐬𝐬𝐞𝐧𝐭𝐢𝐚𝐥 𝐏𝐀𝐌 𝐂𝐨𝐧𝐭𝐫𝐨𝐥𝐬: From discovering every agent and enforcing least privilege to implementing Just-in-Time access and managing dynamic secrets.
Read the full breakdown here:
https://t.co/rlJ0TgiQ6d
#CyberSecurity #PrivilegedAccessManagement #PAM #AIAgents #NonHumanIdentity #InfoSec #CloudSecurity #Securden
Business passwords become difficult to manage when they are saved across individual browsers, copied into messages, or passed between colleagues. IT needs to know who can access each account—and employees need a convenient way to use it.
The risk is real. In July 2026, Microsoft documented ACR Stealer campaigns that harvested browser-stored passwords and authentication tokens from enterprise environments.
Reducing unnecessary credential exposure is one layer of defense, alongside MFA and endpoint protection.
Securden Password Vault for Enterprises brings centrally managed credential access into everyday browser workflows. Users can find permitted accounts, autofill logins, generate passwords, and save or update credentials through the browser extension.
For shared applications, Open Connection permission lets users sign in using stored credentials while password reveal and copy actions remain unavailable. IT centrally controls access, and teams can work without routinely passing passwords around.
Explore enterprise control for everyday password access. Less friction for users, complete control for IT: https://t.co/rvGzpzOvcb
#EnterprisePasswordManagement #CredentialSecurity #Securden
𝐀𝐥𝐥𝐨𝐰 𝐒𝐭𝐚𝐧𝐝𝐚𝐫𝐝 𝐔𝐬𝐞𝐫𝐬 𝐭𝐨 𝐈𝐧𝐬𝐭𝐚𝐥𝐥 𝐀𝐩𝐩𝐥𝐢𝐜𝐚𝐭𝐢𝐨𝐧𝐬 𝐒𝐞𝐚𝐦𝐥𝐞𝐬𝐬𝐥𝐲
You removed local admin rights for all your users for security and policy related reasons. Now, your team wants to install applications they need to get their job done, or they want to try a new tool that would genuinely improve the quality of work and the team’s efficiency.
What do they do?
If the answer is raising a ticket with the IT helpdesk and waiting for the technician to come and install the application, you are compromising the productivity of your workforce for the sake of security.
There is an alternative where your teams work with security and productivity. No compromises.
𝐒𝐞𝐜𝐮𝐫𝐝𝐞𝐧 𝐄𝐧𝐝𝐩𝐨𝐢𝐧𝐭 𝐏𝐫𝐢𝐯𝐢𝐥𝐞𝐠𝐞 𝐌𝐚𝐧𝐚𝐠𝐞𝐫 allows your users to install pre-approved apps and tools without admin rights and provides a self-service portal using which they can request access to try new tools. Approval happens in seconds, through mobile apps, ticketing systems, or the Securden web app.
Explore how Securden balances productivity and security:
https://t.co/oJQX2i4spm
#InstallApps #AdminRights #EndpointPrivilegeManagement #PAM
“Is compliance becoming the new growth strategy?”
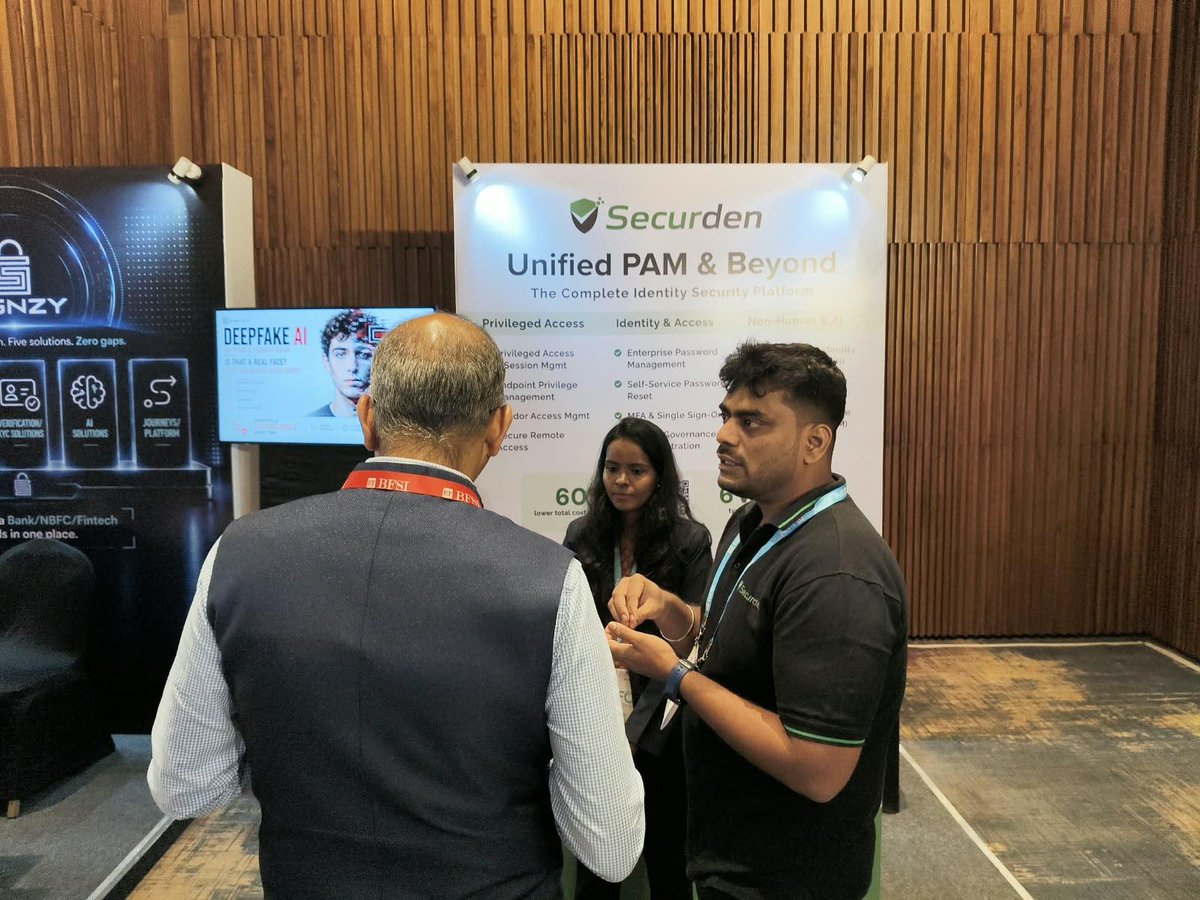
That was one of the questions at the first 𝐄𝐓 𝐁𝐅𝐒𝐈 𝐍𝐁𝐅𝐂 𝐋𝐞𝐚𝐝𝐞𝐫𝐬’ 𝐑𝐞𝐭𝐫𝐞𝐚𝐭 in Lonavala. After three days with 75+ NBFC leaders, our answer is: only if security stops slowing growth down.
Our conversations with CIOs, CTOs, and risk heads kept coming back to the same issues:
🔹 Vendor, fintech-partner, and remote access is growing faster than teams can govern it
🔹 Auditors want proof of who accessed what, when, and with whose approval
🔹 Legacy PAM takes months to deploy and a dedicated team to run
That’s the gap Securden closes:
✅ One platform for privileged access, passwords, endpoint privilege, vendor access, and identity governance
✅ Every privileged session recorded and ready for audit
✅ Up to 60% lower total cost of ownership
✅ On-premises or cloud, deployed your way
Thank you to ETBFSI for an exceptional first edition, and to everyone who spent time with Parthasarathy Dharmalingam, Sathiya Veerasamy, and our partner Meta Infotech Limited at Booth #12.
See how it fits your environment 👉
https://t.co/NtudX5tozp
#Securden #ETNBFCRetreat #NBFC #ETBFSI #PAM #IdentitySecurity #Cybersecurity
𝐘𝐨𝐮𝐫 𝐓𝐞𝐚𝐦𝐬 𝐀𝐫𝐞 𝐀𝐥𝐫𝐞𝐚𝐝𝐲 𝐔𝐬𝐢𝐧𝐠 𝐀𝐈 𝐓𝐨𝐨𝐥𝐬. 𝐃𝐨 𝐘𝐨𝐮 𝐊𝐧𝐨𝐰 𝐖𝐡𝐢𝐜𝐡 𝐎𝐧𝐞𝐬?
AI is helping every team move faster. Naturally, employees are experimenting with new AI tools and agents to boost productivity.
But when users have admin rights, those privileges can be passed on to the AI tools they install, creating a blind spot for IT.
Which AI tools are running?
Are they approved?
What permissions do they have?
Without this visibility, controlling Shadow AI becomes difficult.
Securden Endpoint Privilege Manager helps IT teams discover AI tools across endpoints, control which applications can run, and prevent AI agents from inheriting elevated privileges.
𝐓𝐡𝐞 𝐠𝐨𝐚𝐥 𝐢𝐬𝐧’𝐭 𝐭𝐨 𝐬𝐭𝐨𝐩 𝐞𝐦𝐩𝐥𝐨𝐲𝐞𝐞𝐬 𝐟𝐫𝐨𝐦 𝐮𝐬𝐢𝐧𝐠 𝐀𝐈. 𝐈𝐭’𝐬 𝐭𝐨 𝐦𝐚𝐤𝐞 𝐀𝐈 𝐮𝐬𝐚𝐠𝐞 𝐯𝐢𝐬𝐢𝐛𝐥𝐞, 𝐜𝐨𝐧𝐭𝐫𝐨𝐥𝐥𝐞𝐝, 𝐚𝐧𝐝 𝐬𝐞𝐜𝐮𝐫𝐞.
Control Shadow AI with Securden: https://t.co/xTmi5f29Or
#shadowAI #applicationcontrol #AItool #Discovery
𝐒𝐞𝐜𝐮𝐫𝐝𝐞𝐧 𝐢𝐬 𝐡𝐞𝐚𝐝𝐢𝐧𝐠 𝐭𝐨 𝐭𝐡𝐞 𝐄𝐓 𝐁𝐅𝐒𝐈 𝐍𝐁𝐅𝐂 𝐋𝐞𝐚𝐝𝐞𝐫𝐬’ 𝐑𝐞𝐭𝐫𝐞𝐚𝐭 𝟐𝟎𝟐𝟔.
Banks, NBFCs, and fintechs now manage more users, endpoints, apps, third parties, cloud environments, and machine identities than ever. Securing privileged accounts alone isn't enough anymore. That's why we built Securden Unified PAM, one identity security platform that covers:
✅ Privileged access management
✅ Enterprise password management
✅ Endpoint privilege management
✅ Identity governance
✅ Non-human identity security
✅ AI agent security
✅ Cloud entitlement management
Meet our team at the retreat to see how financial institutions can tighten access security, gain real visibility, and simplify identity security across critical infrastructure.
📅 09–11 October 2026
📍 The Radisson Resort & Spa, Lonavala
📌 Booth #12
See you in Lonavala!
https://t.co/UkLuJ60Evg
#Securden #ETBFSI #NBFC #BFSI #Fintech #UnifiedPAM #IdentitySecurity #PrivilegedAccessManagement #Cybersecurity
Privileged Access Management solutions are notoriously difficult to deploy. This is where Securden solutions differ. The modern architecture and simple product design allow Securden to be one of the easiest Endpoint Privilege Management solutions to deploy.
With a 100% success in deployment, our customers go from evaluation to production in a matter of weeks. The ease of deployment, and exhaustive capabilities are exactly why Securden is ranked among the best 𝐞𝐧𝐝𝐩𝐨𝐢𝐧𝐭 𝐩𝐫𝐢𝐯𝐢𝐥𝐞𝐠𝐞 𝐦𝐚𝐧𝐚𝐠𝐞𝐦𝐞𝐧𝐭 𝐭𝐨𝐨𝐥𝐬 in the list published by Cyber Press.
Explore the latest list of top EPM tools to see how leading solutions compare: https://t.co/arHYYHAGTW
#BestEndpointPrivilegeManagementTools #EPM #LocalAdmin #JustInTime
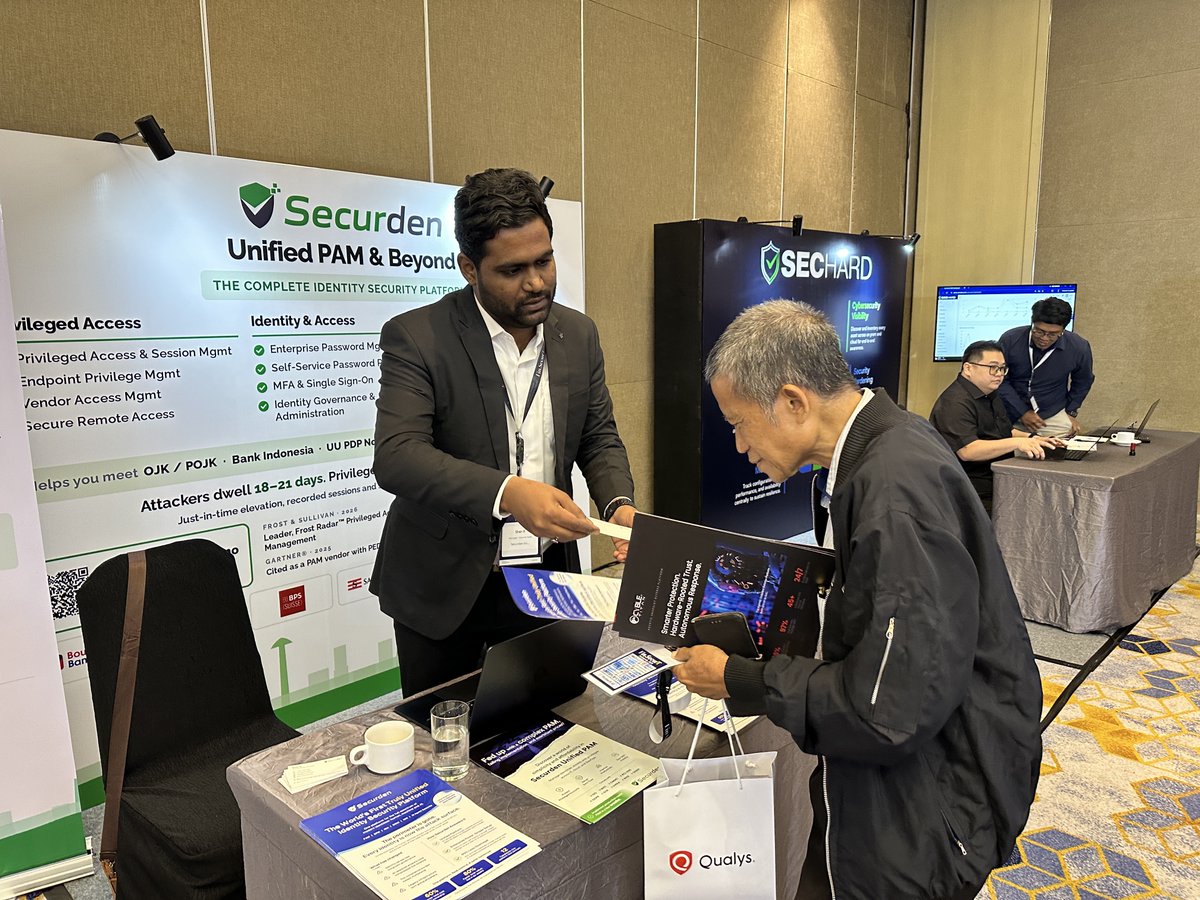
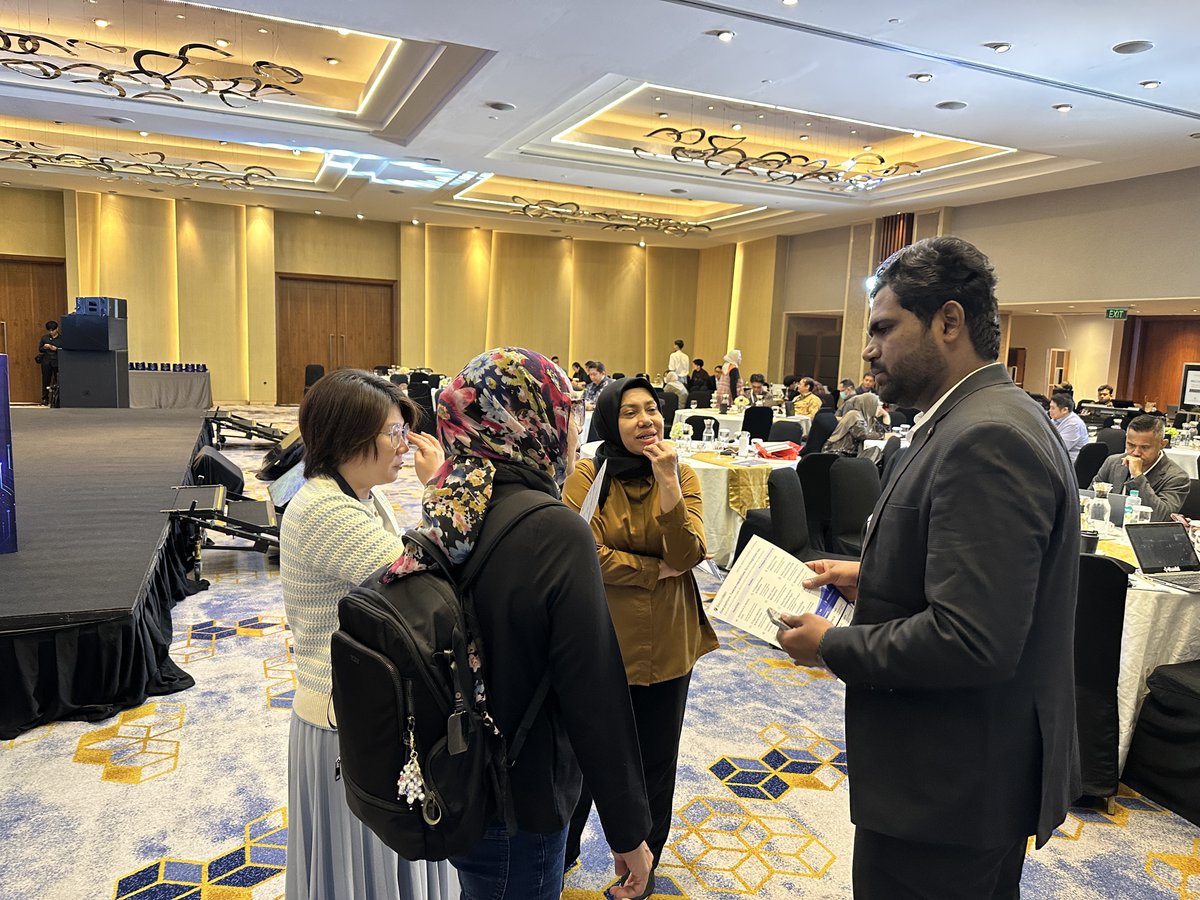
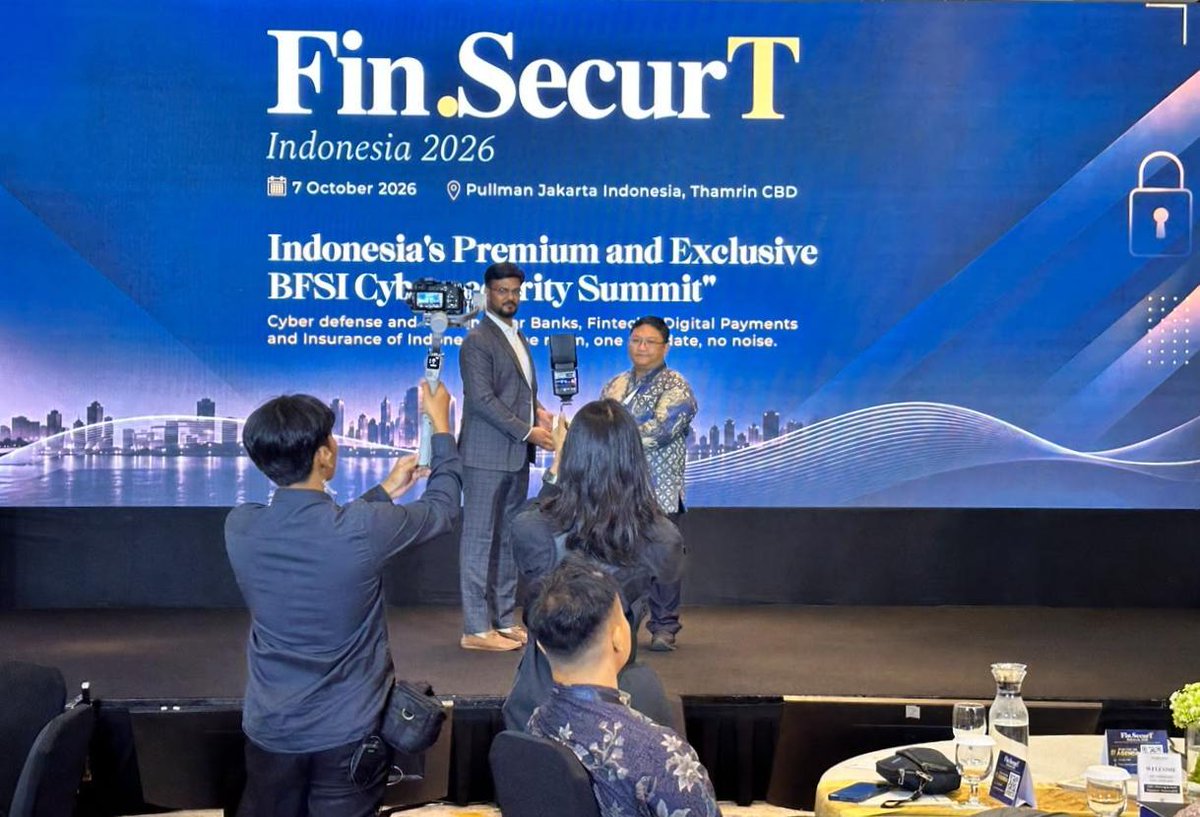
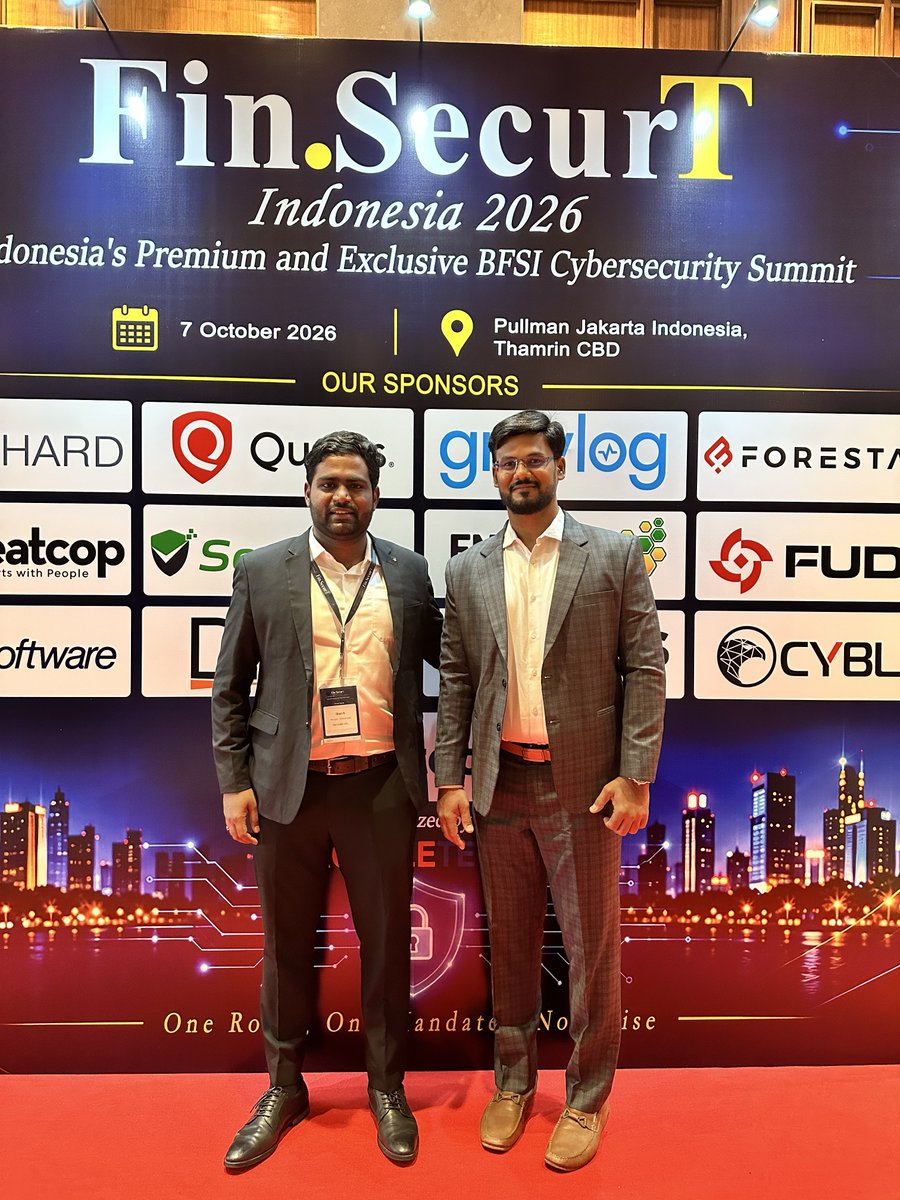
Scenes from 𝐅𝐢𝐧.𝐒𝐞𝐜𝐮𝐫𝐓 𝐈𝐧𝐝𝐨𝐧𝐞𝐬𝐢𝐚 𝟐𝟎𝟐𝟔 📸
Today in Jakarta, we're in a room of security leaders from Indonesia's banks, fintechs, payment providers, and insurers.
Praveen Kumar Kamalanaban took the stage to show how BFSI teams can close the credential attack path. Between sessions, he and Sudharshan Raghunathan, our Channel Sales Manager for this region, talked with security heads about privileged access, OJK / POJK and UU PDP readiness, and moving away from complex legacy PAM.
Thank you to 𝐅𝐢𝐧.𝐒𝐞𝐜𝐮𝐫𝐓 and 𝐀𝐂𝐂𝐄𝐋𝐄𝐓𝐄𝐂𝐇 for bringing this room together, and to every leader who stopped by to talk.
Missed us in Jakarta? See how Securden closes the credential attack path 👉
https://t.co/NtudX5sQJR
#FinSecurT #Securden #PAM #BFSI #Indonesia #IdentitySecurity #Cybersecurity
100 seats. By invitation only. And every seat goes to a security leader from one of Indonesia's banks, fintechs, payment providers, or insurers.
That's the room at 𝐅𝐢𝐧.𝐒𝐞𝐜𝐮𝐫𝐓 𝐈𝐧𝐝𝐨𝐧𝐞𝐬𝐢𝐚 𝟐𝟎𝟐𝟔 in Jakarta, and 𝐒𝐞𝐜𝐮𝐫𝐝𝐞𝐧 is privileged to be part of it as a speaker.
Our Director of Solution Engineering, Praveen Kumar Kamalanaban, will present:
🎙️ Privileged Access: Closing the Credential Attack Path in BFSI
🕙 7 October · Pullman Jakarta Indonesia, Thamrin CBDcredential attack path in your environment
In financial services, stolen or over-privileged credentials are still one of the shortest routes from a foothold to core systems. Praveen will show how BFSI security teams can close that path without slowing down operations or audits. He'll cover vaulting and rotating privileged credentials, enforcing just-in-time access, and recording every privileged session.
He'll be on the faculty with CISOs and security heads from across Indonesia's financial sector and experts from BSSN, the National Cyber and Crypto Agency.
Thank you to 𝐅𝐢𝐧.𝐒𝐞𝐜𝐮𝐫𝐓 and 𝐀𝐂𝐂𝐄𝐋𝐄𝐓𝐄𝐂𝐇 for the invitation.
Not in the room? See how Securden closes the credential attack path in your environment 👉
https://t.co/NtudX5tozp
#FinSecurT #Securden #PAM #PrivilegedAccessManagement #BFSI #Indonesia #Cybersecurity