Secureframe is the automated compliance platform built by compliance experts. We're transforming how businesses and MSPs manage security & compliance programs.
On average, DIB contractors spend $100K–$250K+ and 6–18 months on CMMC prep. Most can't afford that.
Today, we launched Secureframe Defense to help any organization go from zero to CMMC ready in 4–8 weeks.
Learn how: https://t.co/WaCtnUJqgP
FedRAMP granted the first full 20x Class C Certification on Oct 29 to Perplexity.
Next week is the deadline for Rev5 FedRAMP Ready providers to convert to Class A.
What changed, what's next, and what CSPs should do now: https://t.co/JYHa1MYDmG
Can you meet CMMC Level 1 in Microsoft 365 Commercial? When does Azure Virtual Desktop make sense for a CUI enclave? Tomorrow, Microsoft's Richard Wakeman and our CEO answer the questions small contractors are asking live: https://t.co/b7vLldOtlH
Underrated compliance truth: you can have sophisticated security controls and still fail an audit, usually because processes are undocumented or the evidence isn't there. And passing doesn't mean you're secure. Solid breakdown of both: https://t.co/08Lnh9c1Oo
Everyone blames CMMC assessments for the cost. In DoD's own RFI summary, NIST 800-171 complexity ranked #1 and CUI marking #2. Assessors came in fifth. Restarting Phase 2 for a narrower group of contractors is on the table too: https://t.co/wwKoiWMBIl
Vulnerability exploitation just passed stolen credentials as the top way attackers get in (31% of breaches in Verizon's DBIR), and AI is shrinking some exploit timelines from months to hours. Patch speed is a security strategy now: https://t.co/xYx8xVammZ
GCC High is where most DIB contractors land for CMMC, but your license and the enclave vs. full-migration decision drive the real cost. Next week, Microsoft's Richard Wakeman joins our CEO to break it down live. Bring your questions: https://t.co/9Wxvrn2A6g
Last business day of Cybersecurity Awareness Month. The breach I keep thinking about: an attacker used a vendor's legit access to pull 8.8M records from Denmark's ID register, and an invoice is what caught it. 30+ more: https://t.co/fQc7pqFhCJ
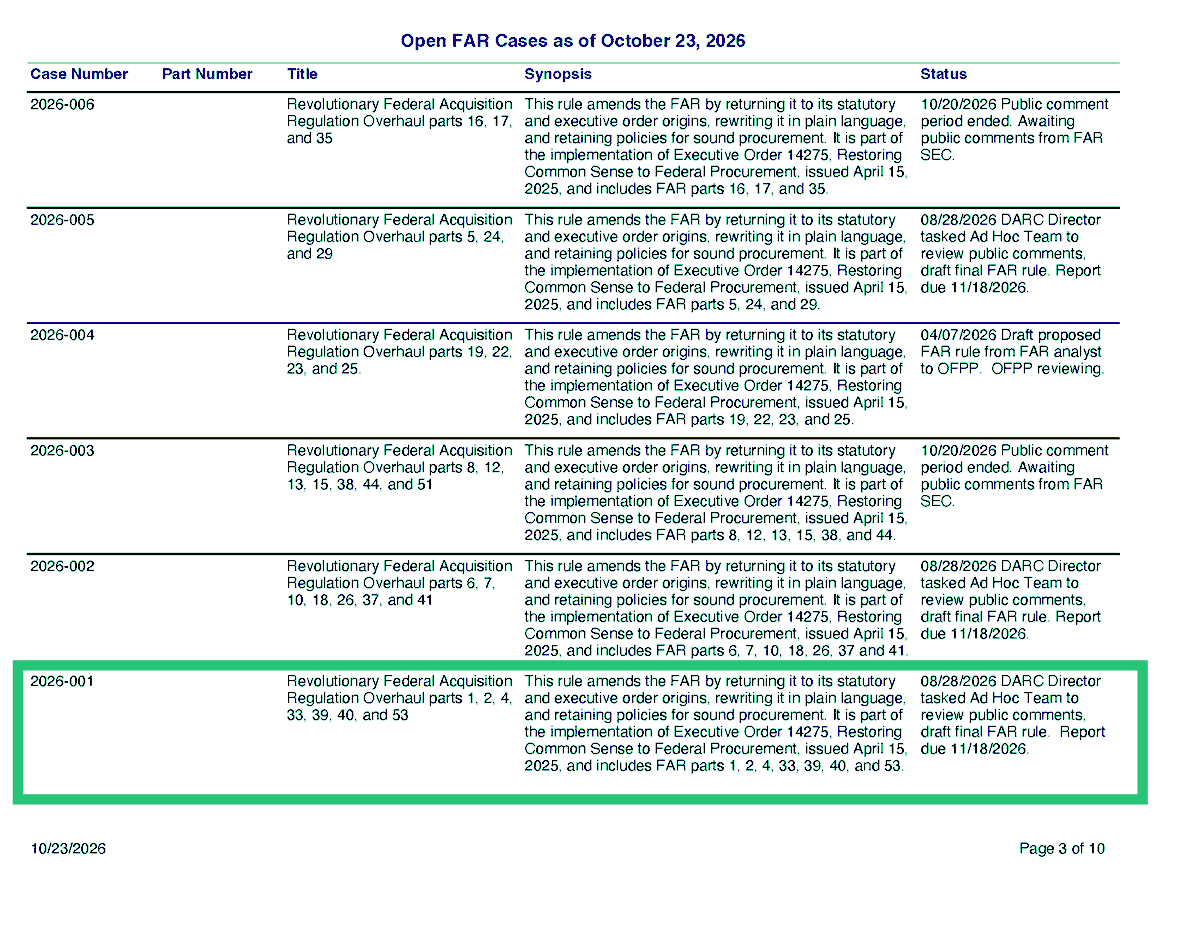
Everyone's watching for the CMMC reform report. Meanwhile, the FAR CUI rule hit the draft final rule stage with a report due Nov 18. Rev 3 baseline, 72-hour reporting, subs reporting straight to the government: https://t.co/1hHy7IJklE
Could CMMC reform news come in November? Matt Travis shared the latest on what he’s heard at last night's Cyber AB Town Hall, plus CAICO’s Q1 2027 content timeline and two new stakeholder collectives.
Full recap 👇
https://t.co/4441pS8uLK
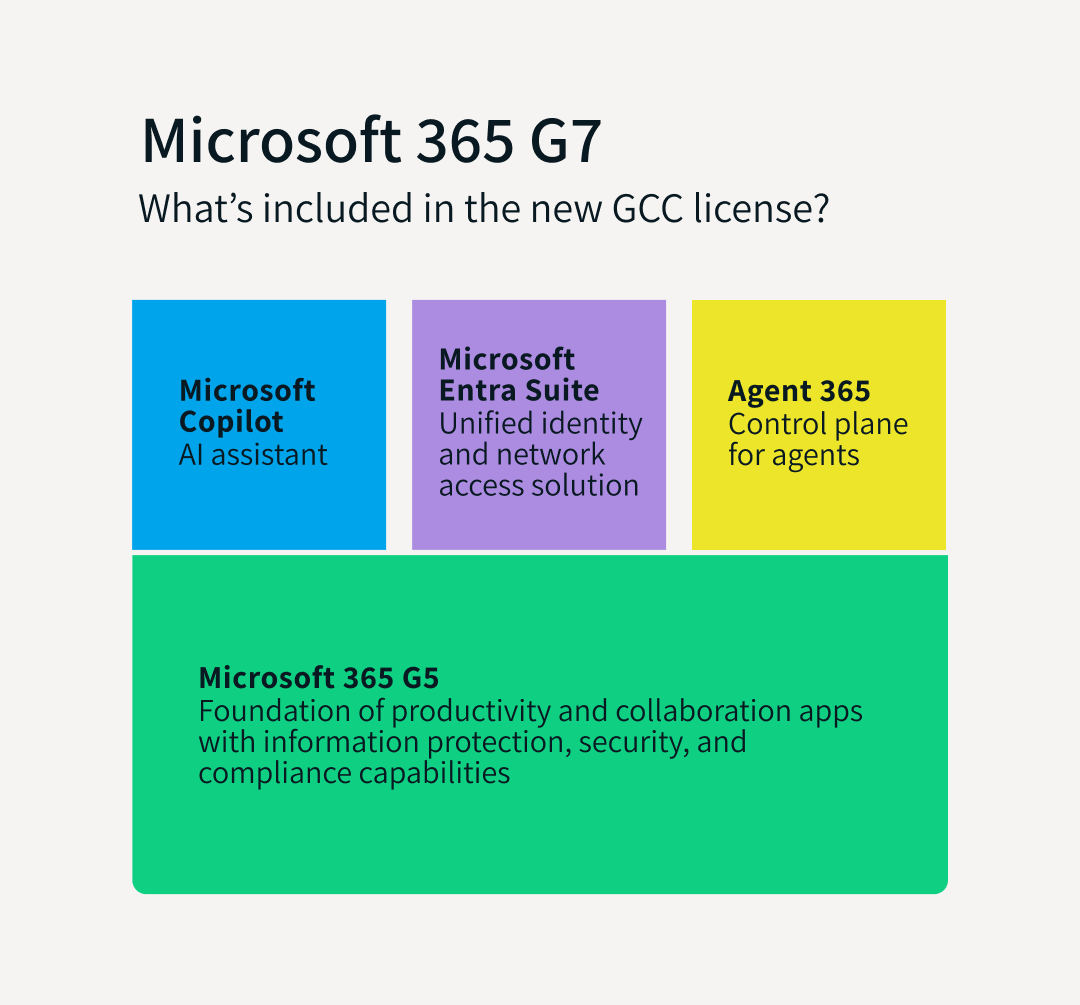
Microsoft 365 G7 was released this month in GCC, but not GCC High, and has about three-quarters of the features of the commercial E7.
Here’s why this one is an evaluate-don't-buy (yet) for most defense contractors: https://t.co/7B6PmKfmj2
No CMMC reform report yet, but the Phase 1 requirements in your contracts still apply. Nov 10, Richard Wakeman of Microsoft and Shrav Mehta on picking the right cloud, license, and enclave vs enterprise setup: https://t.co/RLYcoD9dYE
People keep asking me for the SOC 2 controls list. There isn't one. You pick controls to cover up to 61 requirements, and in a Type 2 a single skipped access review can become a written exception. Best breakdown I've seen: https://t.co/gQRytr2RYP
Redspin: about 47% of 131 DIB contractors are still pursuing third-party CMMC certification despite the Phase 2 pause, and 60% cite customer and prime expectations. If you've done the work, make it easy to see: https://t.co/yH7HmlIywI
A stolen ConnectWise Cloud Backup credential got attackers into at least 162 Microsoft 365 tenants, per Huntress. They never had to break into those orgs. The vendor's access was already inside. The third-party stats here are worth a look: https://t.co/Qd43Jf2QZx
MITRE's ATT&CK v20 now lists the 2026 water utility attacks as a campaign: 30+ Minnesota utilities, internet-exposed PLCs, default credentials, operators locked out. If your shop floor runs PLCs, this NIST 800-82 primer is worth your time: https://t.co/35CnOVK6T4
The attacker behind Denmark’s national register breach (8.8M people) claims they got in through a vendor account with the password “123456.” Reportedly three accounts used it, admin included. Your policy is only as strong as your vendor’s: https://t.co/vKQSvV9AV4
Attackers cranked up fridge temps at hundreds of French supermarkets and stretched defrost cycles to delay alarms. Not a DIB incident, but if a vendor can reach your plant equipment remotely, so can an attacker. Know what comes back first? https://t.co/dnoXSr268a
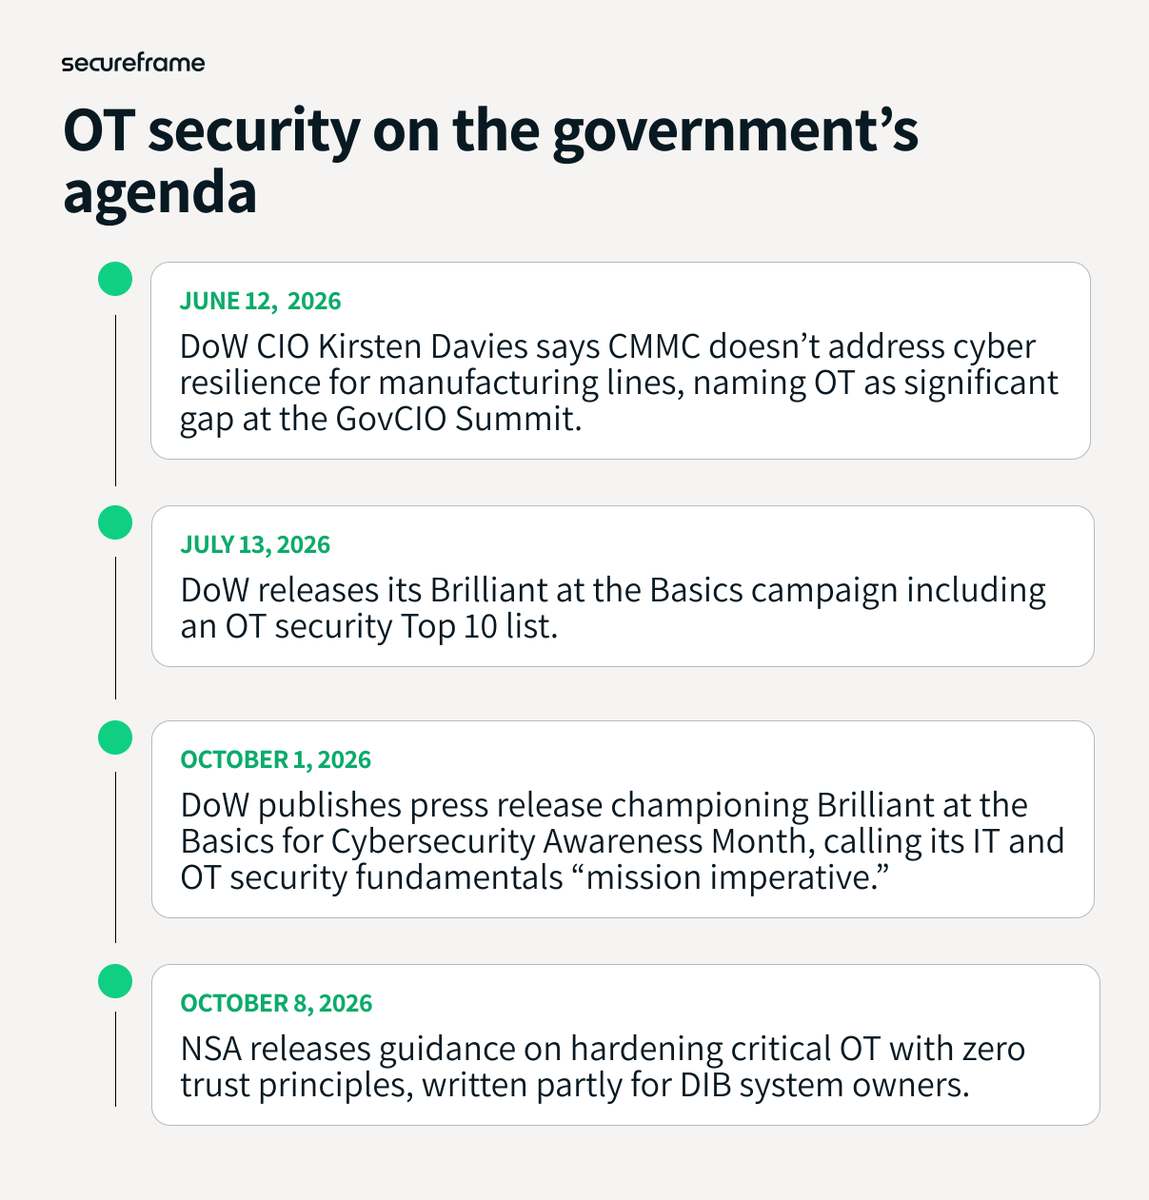
DoW opened October with a Brilliant at the Basics push covering IT and OT. Then NSA released zero trust guidance for OT, written partly for DIB owners. When the government keeps pointing at the plant floor, contractors should look too: https://t.co/TuaOwn3LR9
Known vulns get mass-exploited in a median of five days (Verizon DBIR). Most compliance programs still check controls once a year. My colleague Marc Rubbinaccio told @uctodaynews why that won't last: https://t.co/NJUpIBtuL5
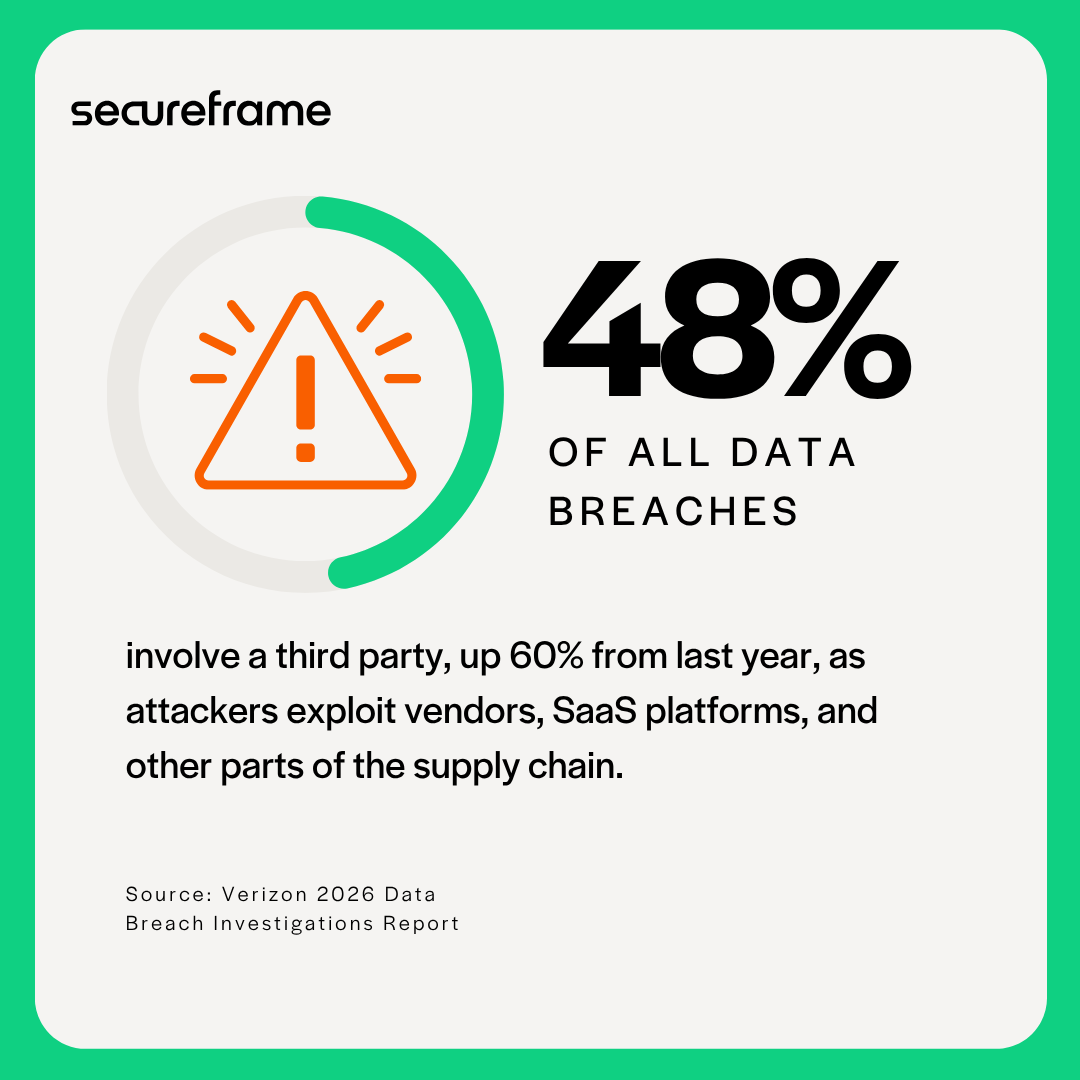
Third parties were involved in 48% of breaches this year, up 60% (Verizon). What surprised us more: only 23% of them fully fixed missing or weak MFA on their cloud accounts. Vendor risk is a remediation problem now: https://t.co/wzixkJW5a6