#LiteLLM compromised AGAIN! LiteLLM v1.107.0 on #PyPI carries a remote code execution backdoor and a credential stealer which steals Cloud and AI credentials. #Malware runs at Python startup, no import needed.
#SoftwareSupplyChainSecurity
👇
https://t.co/hnI27TKRKw
#Node.js issued security updates for its 22.x, 24.x, and 26.x versions, fixing high-severity issues in DNS resolution, TLS certificates, Brotli decoding, HTTP agents, and crypto caches:
👇
https://t.co/Nl8ncNVKi3
🚨 #PHP2Shell: Two critical #PHP flaws (CVE-2026-109618 & CVE-2026-109619) allow unauthenticated #RCE!
#WordPress, #Drupal, #Magento and countless web apps may be exposed. PHP powers 69% of websites.
Emergency patches are OUT. Update PHP now!
👇
https://t.co/It53zZ1hVm
If you are an OWASP member - don't forget to vote in the OWASP Global Board elections!
All eligible members should have received an e-ballot (check the email you used to pay for your OWASP membership):
🗳️☑️
🗳️ OWASP Board Election voting is open!
OWASP members, it’s time to make your voice heard! With three Board seats up for election, your vote helps shape the future of our community.
📩 Keep an eye on your inbox for your unique ballot (check both personal and OWASP emails!).
⏰ Voting closes October 30 at midnight UTC.
Learn more: https://t.co/CbmVtl4lAC
#community #opensource #boardelections #appsec
#NPM - A malicious npm package 'imgdecode' hides a Windows DLL that downloads encrypted shellcode from GitHub and injects it into "dllhost.exe".
One "require()" could compromise a developer’s machine:
#SoftwareSupplyChainSecurity
👇
https://t.co/UUJKbY4KIH
Hijack an #npm package without stealing credentials? #GitHub Tightens npm Publishing After a "SlugFest" Flaw Left 1,500+ Packages Vulnerable to Hijacking:
#SoftwareSupplyChainSecurity
👇
https://t.co/kryEFuvax3
#Anthropic launches FREE AI-powered vulnerability scanning service for established #opensource projects that have a critical impact on infrastructure and user security.
🔍 Periodic scans using Claude Mythos
🤖 Fully AI-generated reports
#AppSec
👇
https://t.co/6R6rh3uVhC
#GitHub repos hit by a new supply chain attack - GhostAction attackers compromised maintainer accounts and injected malware into 346 repositories, including #Uber's athenadriver stealing cloud&AI credentials, CI/CD secrets:
#SoftwareSupplyChainSecurity
👇
https://t.co/hYPLUAa026
Our meetup has started and we currently have @HannahFoxwell on stage speaking about Platform as a Product - What Happens When We Treat Security As a User?
Watch the 📺 livestream here:
👇
https://t.co/zBHDDfps4o
#Citrix: A third #NetScaler#zeroday is being exploited days after admins patched two earlier flaws. CVE-2026-88779 remotely crashes SAML-enabled appliances. Install 14.1-73.41/13.1-64.28+, preserve evidence and investigate unexpected reboots:
👇
https://t.co/QL8T50mgGb
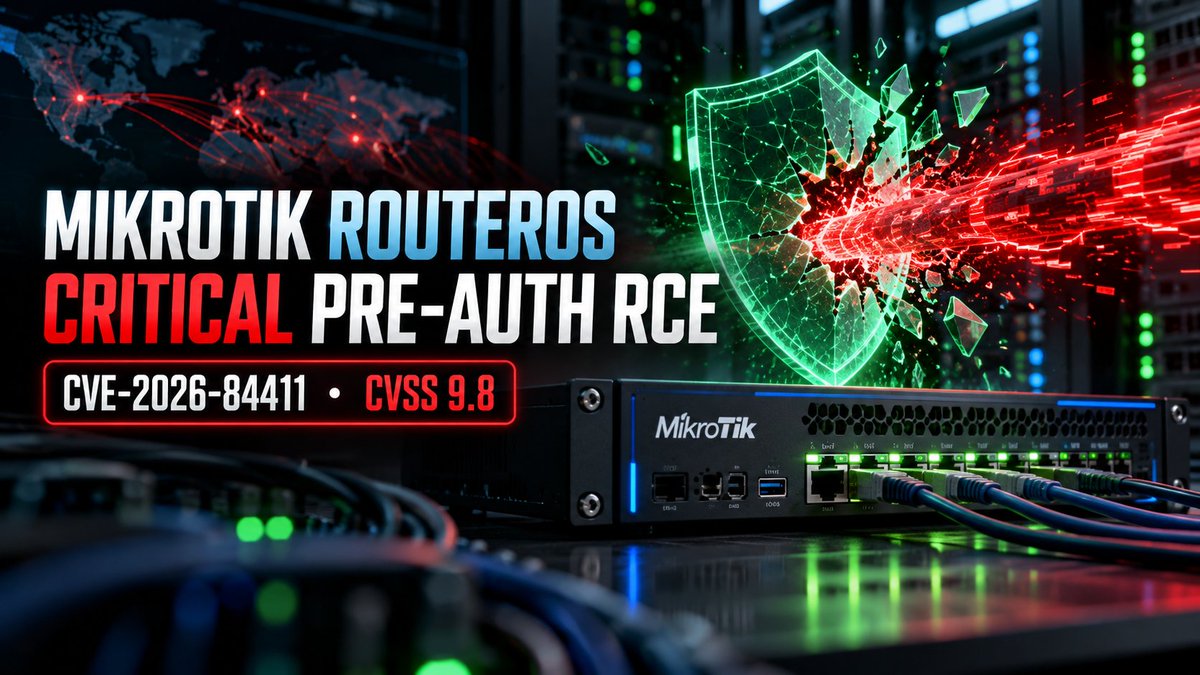
#MikroTik CVE-2026-84411 is a 9.8 pre-auth root #RCE#vulnerability: one crafted HTTP request can execute code or crash RouterOS! Patched versions available.
367,000+ hosts expose the MikroTik RouterOS web interface directly to the internet.
👇
https://t.co/2ddnmlzJeZ
The next #OWASPLondon Chapter meetup will take place on October 7th, 2026.
This event is kindly sponsored by @nuaware_tech , @BlackDuck_SW and @sysdig .
Talks from @HannahFoxwell , Bhavin Bhatt and Emmanuel Gonzalez Carmona.
REGISTER to attend here:
👇
https://t.co/y2AzMPsU7D
Two compromised #GitHub Actions 'actions-cool' were re-enabled with malicious tags intact, silently restarting Mini Shai-Hulud worm across downstream workflows. One action has about 15,000 dependent repos!
👇
#SupplyChainSecurity
https://t.co/J0jlb6tHMI