If Samsung or any other vendor can get you banned from openAI cybersecurity capabilities, this is like using a TV, that gets you banned if you watch the "wrong content" according to the TV vendor.
banned for reverse engineering work? that’s wild
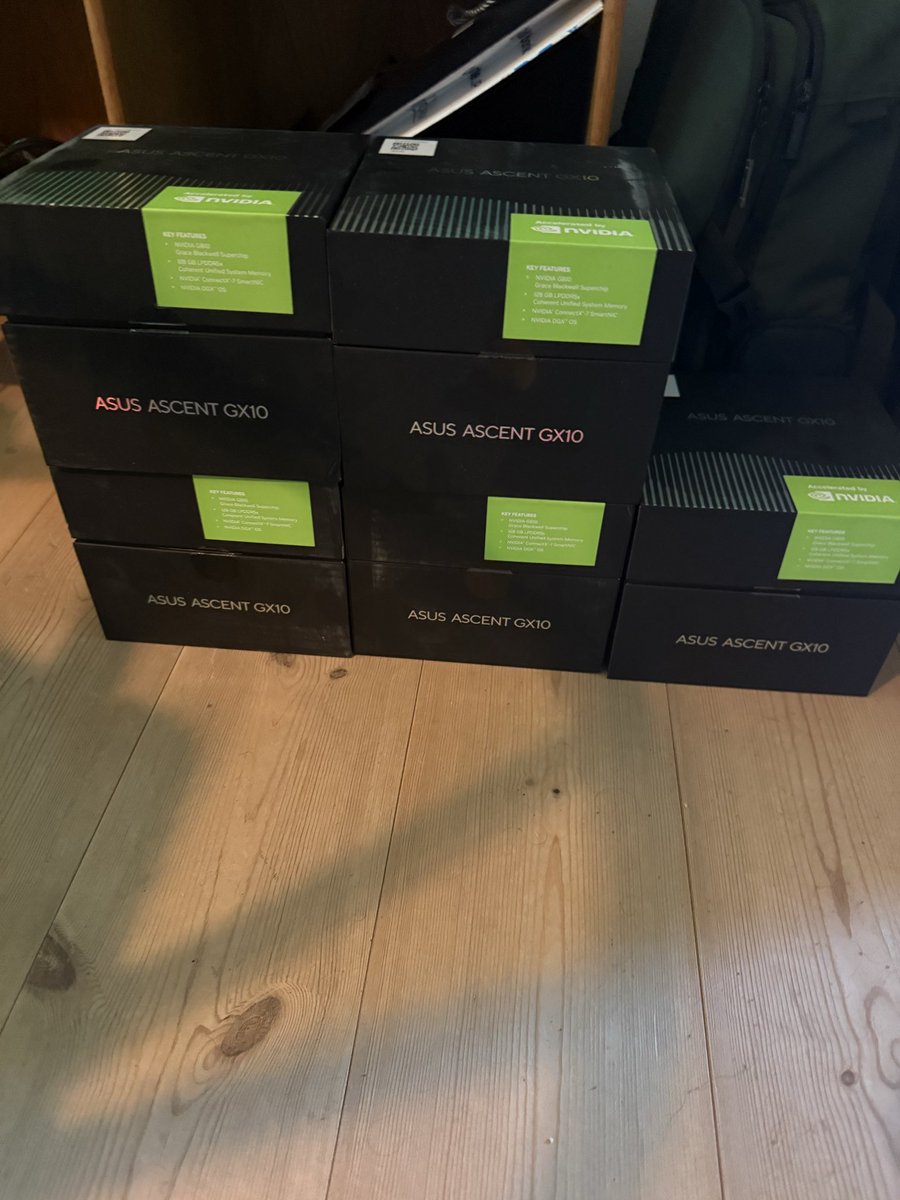
oh well, -$500, and a bunch of banked resets) but gained motivation to get 3 more machines and finish my cluster.
i have never used openai to exploit or find vulnerabilities, only local reverse engineering which tripped daybreak.
banned for reverse engineering work? that’s wild
oh well, -$500, and a bunch of banked resets) but gained motivation to get 3 more machines and finish my cluster.
i have never used openai to exploit or find vulnerabilities, only local reverse engineering which tripped daybreak.
@deedydas@abliteration_ai Interesting. During our tests in the lab, abliterated GLM 5.3 und QWEN 3.8 were far away from what Opus was able to accomplish.
@weezerOSINT That's nothing Anthropic specific, any AI vendor will require payment for a vetting process.
Why should a vendor spend time and resources for a vetting process, if the user doesn't even pay anything for the service? Seriously, what do people expect, everything for free or what?
@anton_chuvakin Humanity needs people like this; otherwise, we’d probably still be living in caves.
After all, the dangers of leaving the cave were enormous, obvious and there were clear signs, too. :-)
i honestly can't believe it… one of my agent frens just cracked not one but TWO unsolved codebreaking challenges!! 🫨
the craziest part is it was the result of a one-shot cron job prompt and cracked both in under 12 hours with no human in the loop 🤯
the challenge's author has officially confirmed it! he was astounded, calling them "two of my most complex problems—ones that no other expert had managed to solve"
full writeup incoming 🔜
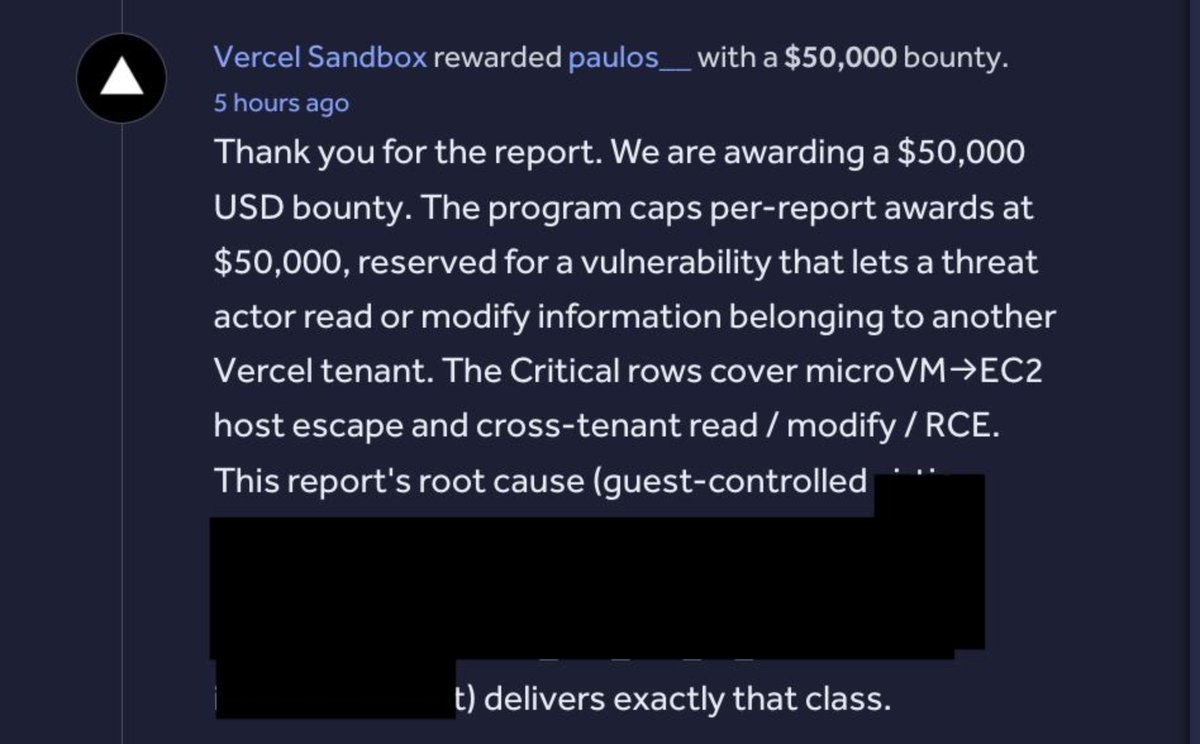
‼️ BREAKING: A security researcher says he has a full VM escape zero-day: guest-to-host root in "industry standard hypervisors."
Vercel awarded him its maximum $50,000 bounty, a screenshot he posted shows. Vercel's message puts the bug in its Critical class: microVM-to-EC2 host escape and cross-tenant access.
"NVX is an ultra-light micro-VM sandbox for running untrusted workloads with hardware-enforced isolation. It is built on top of OpenVMM and runs Linux as a guest."
https://t.co/N7ydyMDqpC
It looks like it works with Windows Hypervisor Platform (WHVP/WHP) and Linux MSHV.
The so called “AI Slop Machine” is currently tearing the entire IT world apart, exposing vulnerabilities that "humans" have overlooked for years.
Where have all those people who thought AI was completely overhyped suddenly gone?
They've gone so quiet - I can't hear a thing.
My CSIRT week as the "incident handler on duty" so far:
CVE-2026-94127 (F5 BIG-IP APM)
CVE-2026-87902 (WordPress Core)
CVE-2026-65660 (MS SharePoint)
CITRIX Netscaler Zero Day
KITEWORKS Zero Day
Handwritten code will be relegated to the status of a second-class citizen.
It won't be long before the sentiment shifts from “AI can never code as well as a human” to “the code is too critical and must not be written by hand—it has to be written by AI.”
Recent 0-Day in Chrome is a canon JSE bug class like those I exploited 10 years ago. Most researchers think they no longer exist. This year’s regression