The FCC proposed a $2 million penalty on a voice service provider for allegedly applying improper attestation levels on calls it originated and authenticated with STIR/SHAKEN. This notice has some lessons for other providers. Read More: https://t.co/qL7gbL05CR
The STIR/SHAKEN ecosystem is soon transitioning to a new Certificate Policy. @SecurityMartini is still awaiting approval to begin issuing under it. With that said we remain hopeful about receiving this approval soon.
In preparation we have updated the STIR/SHAKEN Ecosystem Compliant Report (https://t.co/19scomcgGS) and its associated tests to support these new requirements.
At this time we do not see any certificates issued under this policy. Given past adoption timelines it is hard to predict when that might happen. For example, the first CP was published in 2020, and CAs are supposed to comply with a new CP within 90 days of that. Despite this, many issuers today are still issuing certificates under the this old CP they were originally approved under.
This is noteworthy because there have been 3 other versions since then. To put a finer point on it, it has been 168 days since CP 1.4 was approved and there are no compliant certificates in use from what we can tell.
On a more positive note, it does appear that the STI-PA and PMA have been making some efforts to improve the processes as feedback is flowing more promptly now and there are subtle signs they may be taking compliance issues more seriously moving forward.
With all that said we are proud of our track record of being open, giving back to this ecosystem and being the most compliant CA within this ecosystem.
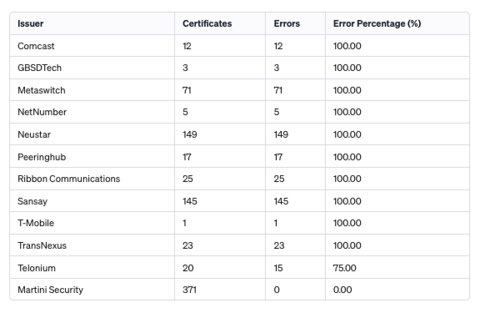
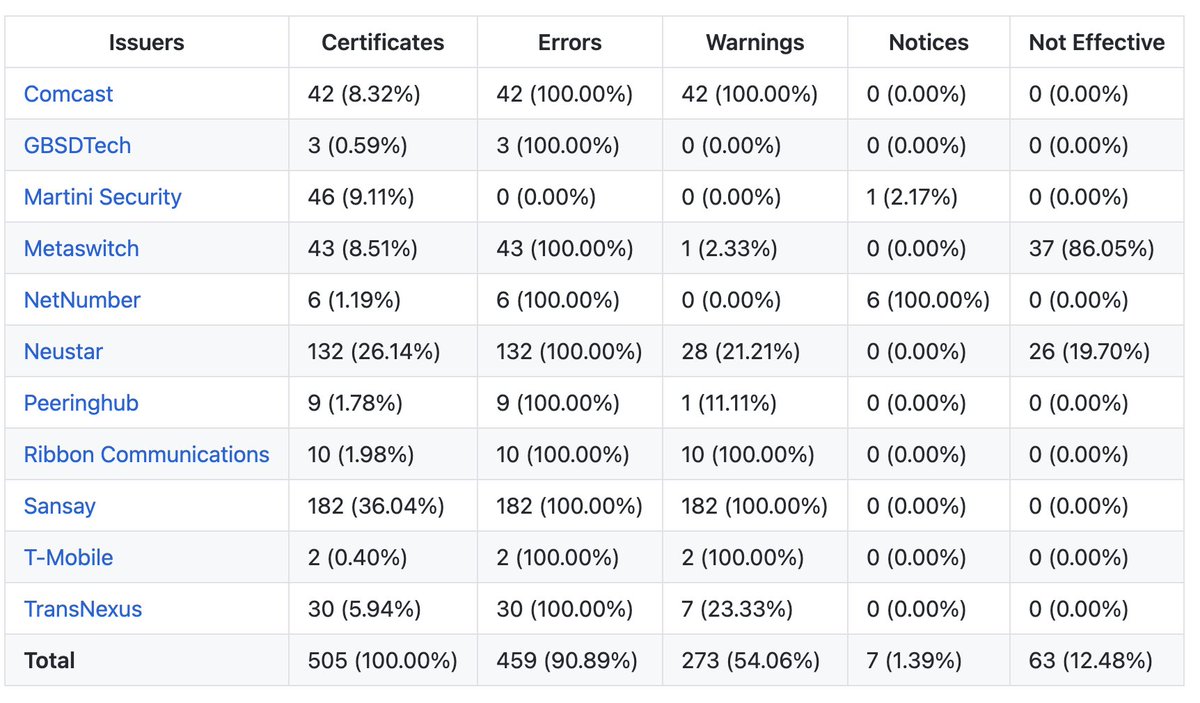
We have concerns about ongoing non-compliance in the CA ecosystem supporting STIR/SHAKEN. We notified the FCC and shared recommended changes. Read our notice ➡️ https://t.co/uG2S3iEMDZ or explore the state of SHAKEN CA ecosystem ➡️ https://t.co/MfSjRde2i8 #STIRSHAKEN#Compliance
This is fantastic! @certifytheweb has become the first general-purpose ACME client that supports STIR/SHAKEN! Now, service providers have the convenience of managing both their STIR/SHAKEN and TLS certificates through the same platform!
How do you leak an OEM private key for a trusted boot system. What kind of incompetence leads to that key ever being in a place where it can leak. And if that key can leak, what secret keys aren’t going to leak?
The large majority of calls received by service providers are still unsigned. All facilities based small service providers have until June 30th to get STIR/SHAKEN compliant. We can help. https://t.co/TbLPUy0tbb
We prioritize security & compliance. No empty promises here. Our #STIR#SHAKEN services are backed by automated tech & policy automation. See our regular reports. #cybersecurity#compliance https://t.co/MfSjRde2i8
🍸Meet Martini Security's complete STIR/SHAKEN & robocall solution! Quick to deploy, open source, handles certificate mgmt, call metadata signing/verification & provides robust robocall mitigation capabilities all for FREE!. 📞🔒🍸 https://t.co/TbLPUy0tbb
🌟 Discover how to to get STIR/SHAKEN compliant with Asterisk in our new white paper! . Don't wait any longer, dive in: https://t.co/WEGGtlgxw9 #STIRSHAKEN#Asterisk#SecureCalls
🚀 Unveiling our latest white paper on achieving STIR/SHAKEN compliance with Kamailio! Master the process and ensure secure calls 📞 with our expert guidance. Ready to get started? Check it out now: https://t.co/WEGGtlgxw9 #STIRSHAKEN#Kamailio#VoIP
Vermouth is the only Open Source STI-AS, STI-VS with built in Certificate Lifecycle Management, and both DNO, and DNC support. Most users are able to get up and running in under an hour! #SHAKENSTIR https://t.co/kYGTHjyIXS
Just in! Martin Security's Vermouth offering now comes with basic robocall mitigation features, including call blocking and labeling for DNO and DNC enforcement. And the best part? It's all free and open source! #robocall#stirshaken#opensource https://t.co/kYGTHjzgNq
On average each STIR/SHAKEN compliant service provider has an average of 7.50 unique unexpired certs. This suggests broad use of cert lifecycle management. We implement ACME to make this as easy as possible for service providers to roll out a reliable and vendor neutral solution.
We just published a new white paper on how to enroll for a STIR/SHAKEN using Olive. Did you know you can give us a shot for only $98? Verification only takes a few minutes and you will be up and running! https://t.co/Tvh3K0DkoK
Have you already deployed STIR/SHAKEN? Did you know you can switch to Martini Security and up to one year free? Just show us your current certificate and we’ll add up to one year to your subscription with us! https://t.co/Ss2GKBoPzX
Approved CAs in the STIR/SHAKEN ecosystem are required to meet technical and policy requirements. We’ve automated testing many of these checks and run them against a large corpus of observed certificates. You can find the highlights here: https://t.co/WKy2ObdbAq