Open source, air gapped BIP39 calculator. Create seeds with real world entropy, verify every bit, seedXOR, Shamir, BIP85 and obfuscation. SD and QR. OpSec
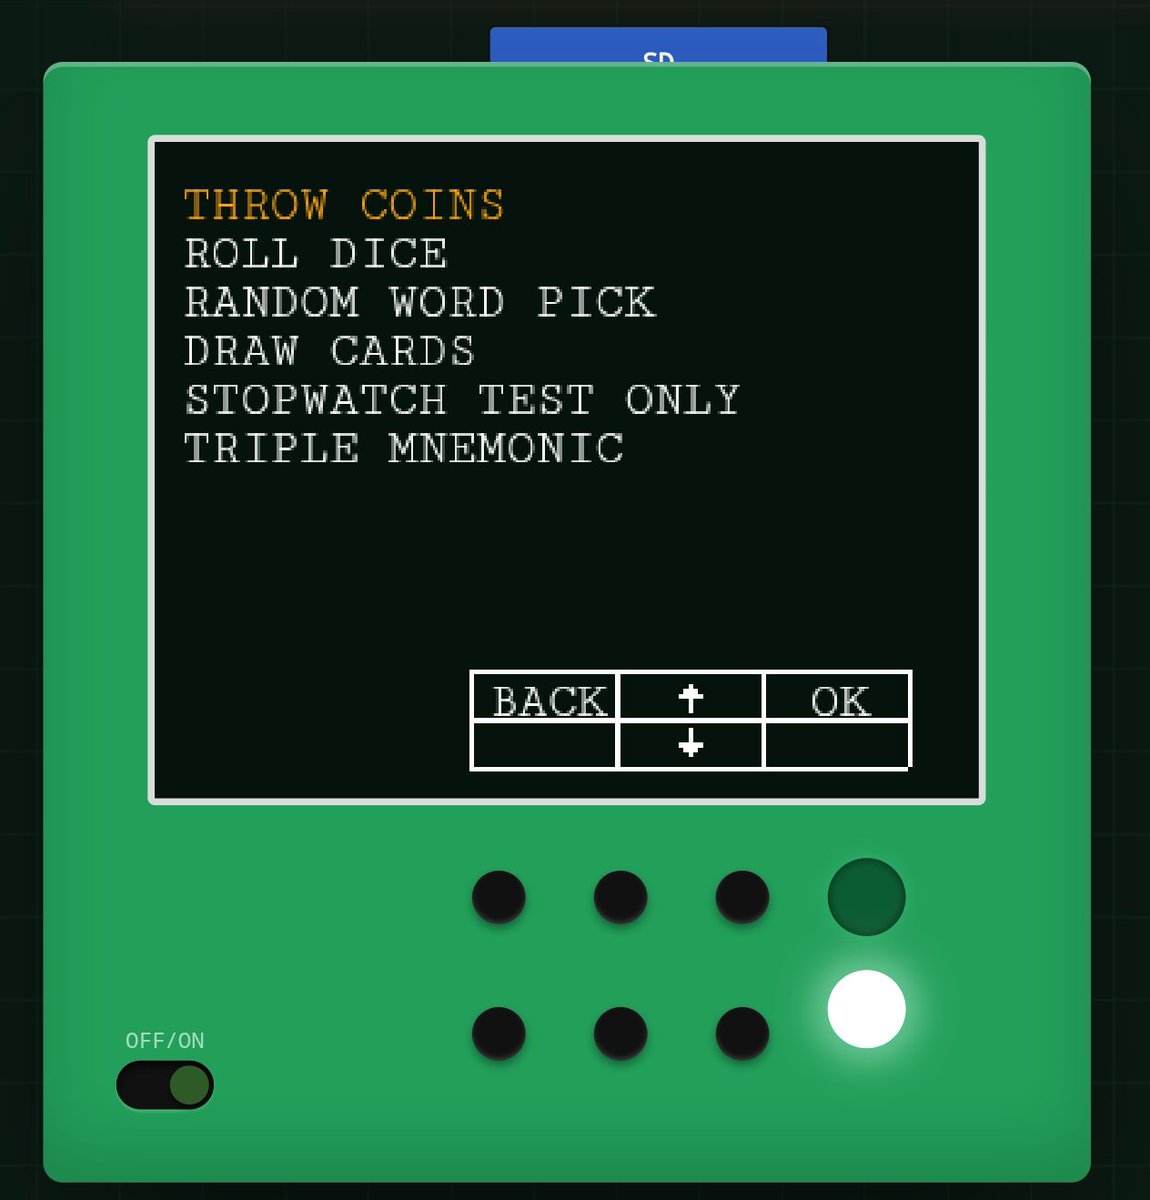
Seedmate doesn't implement a random number generator. Seeds are generated from real-world entropy (coins, dice, cards, word picking) and mixed with seedXOR if the user chooses to. The stopwatch timer is labeled "test only" because it's the only method the user cannot verify.
The economics of seed phrase brute forcing:
When trying to explain the massive scale of 128-bit security (2^128), people usually compare it to the number of atoms or calculate how many millennia millions of computers would take. But there is a metric that makes it much easier to understand: money.
Let’s look at the actual economics of brute-forcing a 12-word seed phrase, giving the attacker every unfair advantage possible.
The Setup ("God Mode")
To make it as easy as possible, let's bend reality:
Infinite, FREE state-of-the-art ASICs.
Dirt-cheap electricity at $0.01/kWh.
Bypassing all PBKDF2 and elliptic curve cryptography. Checking a seed costs the energy of just one SHA-256 hash (roughly 100,000 times easier than reality).
The Haystack
128-bit security gives us 2^128 (3.4 x 10^38) possible combinations. Assuming there are roughly 50 million funded addresses on the network today, you would need to calculate about 6.8 x 10^30 hashes to stumble upon just ONE match.
The Electric Bill
Even using the most energy-efficient ASICs available today (1.75 x 10^-11 Joules/hash), computing those hashes requires about 3.3 x 10^13 kWh of energy.
At our cheat-code rate of a penny per kWh, your electric bill to find a single funded wallet hits $330 BILLION.
The ROI
💰 Average wallet balance: ~$23,600
⚡ Electric bill: -$330,000,000,000
🔥 Net Loss: -$329,999,976,400
Even with free hardware, virtually free energy, and skipping 99.99% of the cryptographic math, physics still bankrupts you. Brute-forcing 128-bit entropy isn't just mathematically hard; it is economic suicide.
Advantages of creating mnemonics on Seedmate:
- Bring your own entropy and easily verify the result.
- Loading the seed onto a second device forces you to verify your written backup before you can even send funds.
CoinKite needs to give all of their software and hardware IP to the public domain. Other than somehow making victims whole, there is only one first step towards penance, and this is it.
😄Negative.
It's a stateless battery powered offline airgapped (no radio) open source tool that is really quite useful for creating different type seeds in a variety of ways including dice, coins, cards and more.
Also verifies existing seeds offline (think Ian Coleman but not on your computer. Does seedXOR, creates BIP 85 child seeds, Shamir, and much more. You can export on SD or by QR.
Super helpful.
Thank you for the feedback and for taking some time to review the project.
Every statement you made is correct, except the triple mnemonic, which is just creating a 24 word mnemonic that complies with 3 checksums. Splitting it in two parts is a user decision and is similar to adding a passphrase IMO.
I will look into easy ways to verify the programming files and into independent audits.
@lunaticoin Si alguien se quedó con la curiosidad de ver como funciona, acabo de subir un simulador a la web bastante fiel al dispositivo https://t.co/ZJioj2xovx
@BTCRECARGADO Eso todavia no lo tengo y ya no me quede memoria para meterlo 😭. Pero ya está de camino un prototipo con otro procesador que me permitira hacerlo. Cuando tenga el simulador terminado te aviso.
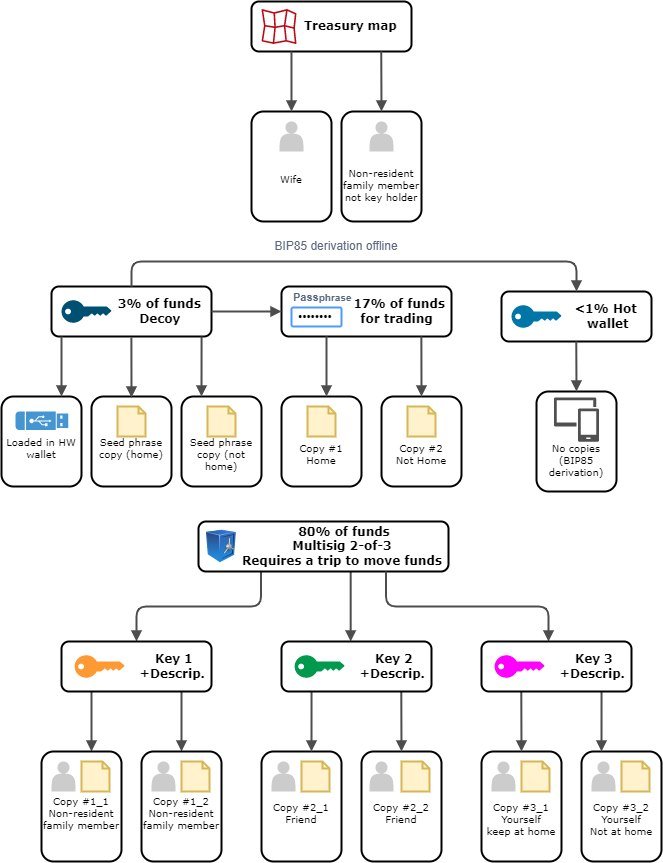
Inspired by @SVRN_Money, I made this custody diagram so CT can roast my setup.
P.S. This isn't actually mine, I don't have enough to justify this haha.
In contrast, when using raw entropy mode, you can inspect every step of the conversion: from dice to bits and from bits to word. No need to do any calculation, just check the binary sequence in any BIP39 wordlist
https://t.co/b9njqnzE8V
Hashing dice rolls cannot be reversed, as SHA256 is a 'black box'. To verify the conversion, you have to compare the device's output to another tool's output. If that tool is a website, you need to run 'N' dummy tests to verify the process before doing the real one just offline. That means entering N × 99 × 2 + 99 dice inputs!
Yes. Using a BIP85 child seed in a hot wallet is safe for the main (parent) funds. Derivation is one-way: a compromised child cannot recover the parent seed or siblings, due to hardened paths plus the HMAC step that hardens the entropy. Offline derivation keeps the master unexposed. Only the child's funds are at risk. The parent remains a single point of failure for every child if it ever leaks.
@A_Turing_Point I'm not sure what you mean.
@grok is it safe for main wallet funds to use a BIP85 child seed in a hot wallet? derivation would be done offline of course!
You have your main stack with seeds stored redundantly offline, multisig, whatever.
Then you realize that you need a different seed for a hot wallet (e.g. everyday transactions), now you have to keep track of even more secrets.
The solution? BIP85 child derivation