@EstebanCervi Alguien robó pero también demuestra lo ignorantes que son en el tema, absolutamente reprochable que sean tan ingenuos (o manipulables) de compartir algo así
@JMilei Intelectualmente igual es muy reprochable que un presidente haya caído en una estafa crypto tan burda. El día que pasó no lo podía creer, se notaba el desconocimiento del tema y eso es peor que ser culpable porque no se puede usar la investidura presidencial para algo así
The FBI continues to warn about two critical security flaws in PHP, a programming language used to build many websites and online services. Attackers could exploit these vulnerabilities to break into systems, putting sensitive information and business operations at risk. Security updates are available and should be applied immediately.
If you are a business owner or website operator, check whether your systems are affected. Contact your IT support team, website developer, or hosting provider for help identifying vulnerable systems and applying the necessary updates.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on https://t.co/JFOW6jG9Ws. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or https://t.co/ZWC7Se2YdU. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information on these vulnerabilities (CVE-2026-109618 and CVE-2026-109619), follow PHP’s announcements on https://t.co/JFOW6jG9Ws, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
@Lbaini Depende a que apuntes, claramente la imagen de una diseñadora profesional es superior al de los que estás compartiendo (al menos por ahora) y seguramente tus seguidores sienten compatibilidad con vos por no usar IA en esos detalles. Como podrás notar los 4 "son iguales"
Philomena: Some people have been writing PHP for over 20 years. Is that because it's particularly difficult to finish?
Expert: No, software is constantly evolving.
Philomena: So they've been writing the same website for 20 years?
Expert: No, different projects.
Philomena: Have they tried finishing one before starting another?
Expert: That's not how software development works.
Philomena: My mate Paul spent 20 years building a shed. Turned out he was just an alcoholic.
Expert: Right.
Philomena: Is PHP like that?
@coheteplasttico Yo fui a shows en España ¿vos fuiste a shows en Argentina? Tenés que vivirlo para entender la diferencia... el concierto se vuelve una experiencia 360 cuando todo el público es una sola cosa festejando... nunca lo van a entender
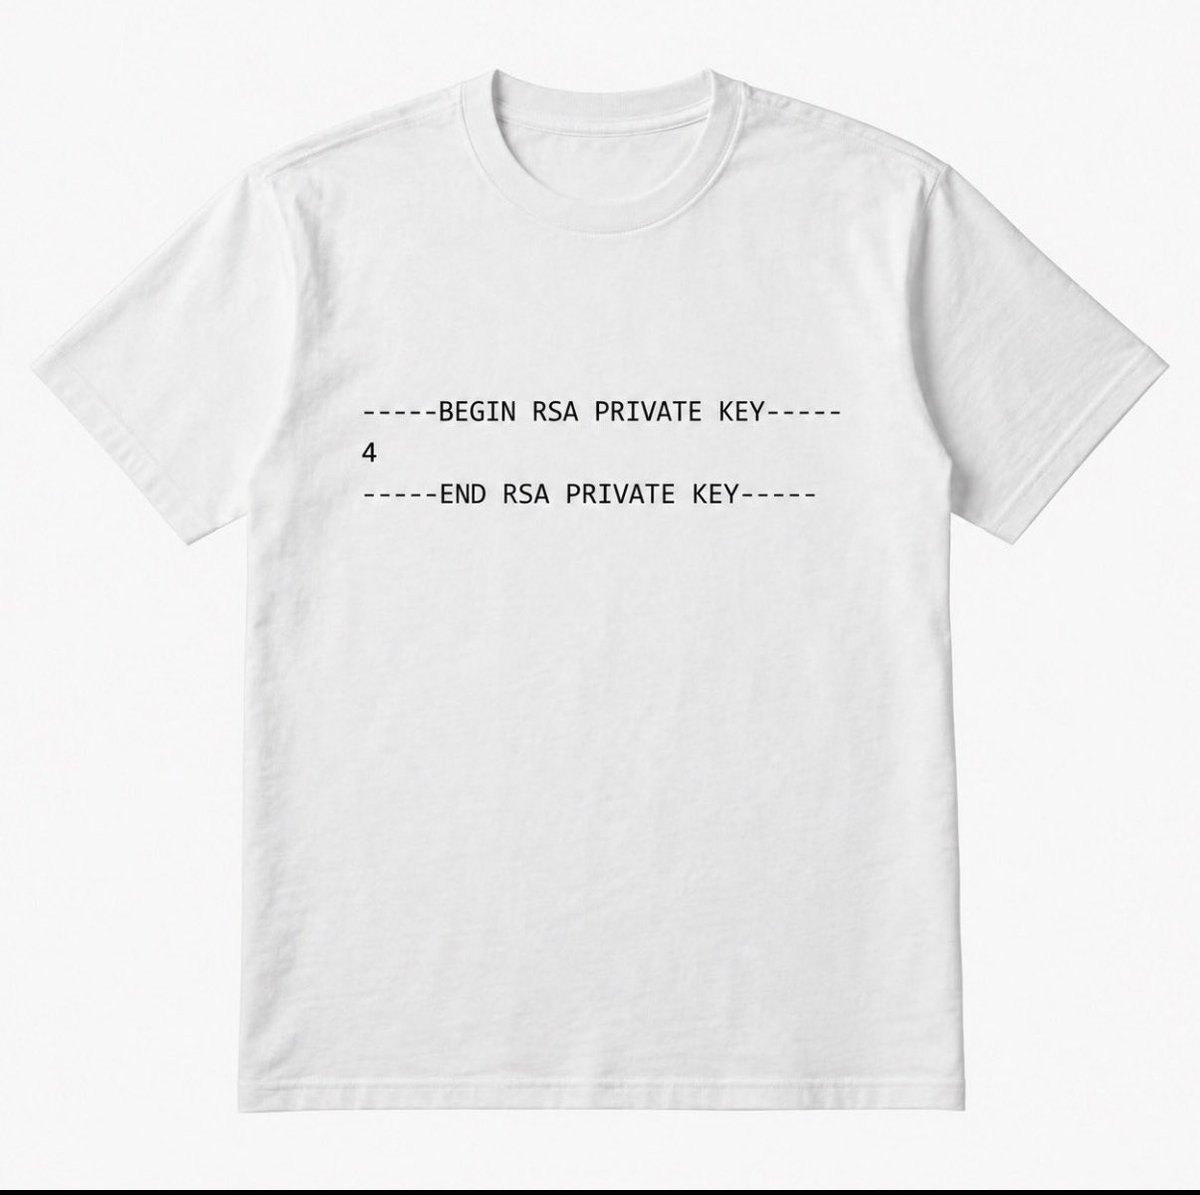
eMudhra es la empresa india que cometió el error de seguridad: se dedica, entre otras cosas, a emitir certificados digitales q permiten q los navegadores comprueben q una web es confiable, y una de sus claves secretas era simplemente el número 4 en lugar de un clave compleja
Siempre le mandas la conversación entera cuando superas la cantidad de tokens que puede procesar tenes que compactar la información y enviar el resumen mas el nuevo mensaje
@leonpalafox Siempre le mandas la conversación entera cuando superas la cantidad de tokens que puede procesar tenes que compactar la información y enviar el resumen mas el nuevo mensaje
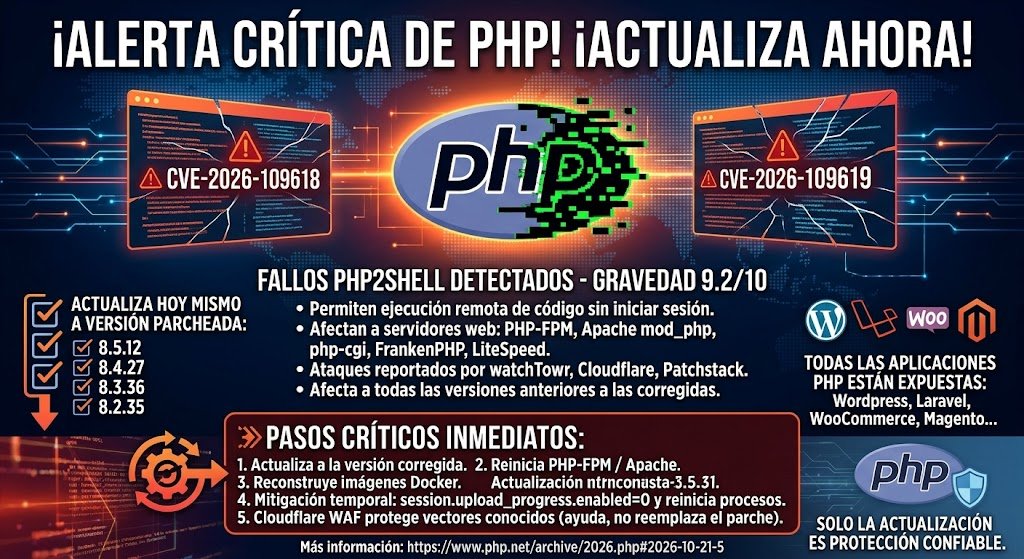
🔴 Empresas de seguridad como watchTowr, Cloudflare y Patchstack ya reportan ataques reales. Además, el código del ataque ya es público
✅ Versiones corregidas: 8.5.12, 8.4.27, 8.3.36 y 8.2.35
⚠️ PHP2Shell: actualizá PHP hoy.
PHP publicó parches de emergencia para dos vulnerabilidades críticas (CVE-2026-109618 y CVE-2026-109619), con gravedad 9.2 sobre 10. Permiten que un atacante ejecute código de forma remota en servidores web sin necesidad de iniciar sesión
🔴 Afecta a toda instalación de PHP que atienda peticiones web: PHP-FPM, Apache con mod_php, php-cgi, FrankenPHP y LiteSpeed. Los más expuestos son quienes usan mod_php