Every subdomain has a beginning. But what happens when the project behind it disappears?
The server goes dark. The domain expires. Yet its history remains.
Abandoned infrastructure can become someone else's opportunity.
ShellZeroX looks beyond what's visible, uncovering forgotten digital footprints and potential takeover risks.
The project may be gone. The attack surface isn't.
#ShellZero
The campaign is over. But the DNS record is still there.
An abandoned subdomain pointing to an expired service can become an entry point for attackers.
One forgotten CNAME. One potential subdomain takeover.
SHELLZEROX helps you find dangling DNS records and identify potential takeover risks before someone else exploits them.
Find it. Remove it. Rescan.
https://t.co/YjVW8sDPtm
#SHELLZEROX
Your website is ready. Your launch is live.
But one expired SSL certificate can turn every visitor away.
A single overlooked date can cost you traffic, trust, and opportunities.
SHELLZEROX helps you detect certificate issues before they become problems.
Scan. Read. Renew. Rescan.
Don't let a security warning define your launch day.
https://t.co/essoautLEW
#SHELLZEROX
Shellzero is building for a future where staying online doesn't depend on centralized infrastructure. Even when internet connectivity goes down in many places, Shellzero aims to keep you connected, secure, and operational through decentralized resilience.
Stay online when the world goes offline.
https://t.co/essoautLEW
Banking outages expose a critical weakness in centralized infrastructure: a single point of failure can disrupt millions.
Shellzero is building toward a more resilient digital future, where intelligent security, real-time threat detection, and decentralized infrastructure help keep users connected even when traditional systems go offline.
Stay online when everything else goes offline.
https://t.co/essoautLEW
🚨🇦🇺 AUSTRALIA’S BANKING SYSTEM GOES DARK AFTER JAPAN: Be Prepared For The New On-Chain Financial System
Major banking disruptions hit Westpac, affecting online banking, mobile apps, PayID and Osko payments. Transfers were delayed, money was stuck in limbo, and customers of other major banks also reported problems. ATM’s also went dark.
🇯🇵 JAPAN, November 6: A massive infrastructure failure reportedly shut down 128 financial institutions and approximately 3,430 branches, affecting ATMs, withdrawals, deposits and banking services.
🇬🇧 UK, October: Cloud infrastructure disruptions affected financial services, exposing their dependence on centralized technology.
THREE COUNTRIES. MULTIPLE BANKING FAILURES. JUST WEEKS APART.
The traditional banking system is exposing its biggest weakness: centralized infrastructure, outdated settlement rails and critical points of failure.
And the timing couldn’t be more significant.
The world is already moving toward TOKENIZATION, BLOCKCHAIN SETTLEMENT AND 24/7 DIGITAL FINANCE.
Here’s what comes next:
🔹 Tokenized deposits moving across blockchain networks.
🔹 Real-time settlement without traditional clearing delays.
🔹 Distributed infrastructure reducing dependence on single points of failure.
🔹 Transparent, programmable financial transactions operating around the clock.
Every major banking outage strengthens the case for accelerating this transformation.
This is bigger than a banking outage.
‼️ THEY WANT EVERYTHING ON-CHAIN.
Every transaction. Every wallet. Every financial move. Frozen balances and de-banked with one switch without naming them CBDCs.
But without privacy, blockchain could become the greatest surveillance infrastructure ever created.
Private digital identities. Zero-knowledge proofs. A financial system where you can prove who you are without exposing who you are.
A future of complete on-chain financial privacy and almost nobody is paying attention.
This is why @DNAOnChain is about to be the biggest privacy solution in the new on-chain financial system.
AI, Cyberattacks, Cash Stockpiling & Stablecoins: The world is preparing the biggest financial reset in history.
Changing your password is no longer enough if your device is already compromised.
Modern cybersecurity must go beyond account protection. Detecting malware, monitoring threats, and preventing unauthorized access are essential.
Security should be proactive, not reactive.
That's the vision behind Shellzero.
🇺🇸 Changing your Gmail password might not protect you from hackers anymore.
There's a new hacking tool called Remus Stealer, and apparently hackers can rent it for $1,000 a month.
Here's the scary part. Once your device is infected, the people behind it claim hackers can keep reading your emails and stealing security codes even after you change your password.
Researchers are still checking whether it really works that way.
Google recommends removing malware, logging out of suspicious sessions and checking your account settings.
Oh great. Like everything happening in the world wasn't enough, now we have to worry about this too.
Source: New York Post / Writer: Daniyal
This is a reminder that even the strongest protocols can be compromised through a single point of failure.
Security must go beyond smart contracts. Domain protection, phishing detection, and real-time threat monitoring are essential.
This is exactly why we're building Shellzero.
The Across domain is currently down while we secure it against an attack from earlier today.
At ~18:45 UTC, a social engineering attack on @Namecheap (our domain registrar) gave a bad actor control of the Across domain.
Within 15 minutes of this attack, we were alerted and immediately worked to shut the site down. SEAL911 marked across.(to) as a phishing site with major wallets, and Cloudflare worked with us to mark the domain as at risk, and later pulled the site’s DNS records.
At the time of this post, Across.(to) is fully down, and the phishing site is no longer available.
In the brief period before Cloudflare fully blocked the malware site, some users who visited across.(to) may have been affected. No third-party integrations or API users were affected. Users who believe they were affected should DM us with transaction details and revoke attacker permissions (see next tweet for details).
Despite our best efforts, @Namecheap has been unresponsive, and we have not been able to properly secure the domain to bring Across’s services back up. Across’s frontend and API will remain down until we can properly secure them. We will always put user safety first.
Across’s domain was fully locked down with best-in-class security practices; this unauthorized takeover should not have been possible. We will be investigating this deeply and will provide a post-mortem on how this domain takeover was possible once we have more information.
This is exactly why security must go beyond individual apps.
A single OS-level vulnerability can put an entire digital ecosystem at risk.
At Shellzero, we believe protection should start before threats become breaches. Security must be proactive, continuous, and built into every layer.
JUST IN: Binance warns Apple users of an iOS flaw that lets malicious apps read seed phrases, private keys and login credentials.
The warning names iOS 26.7.1, 27.0.1, and 27.2.
Called “worse_query,” it breaks the isolation that normally keeps one app from accessing another app’s local files.
The risk extends across apps, beyond Binance, with exposure depending on how apps store and protect sensitive information.
Binance urges users to remove untrusted apps and update their software.
If a breach is suspected, move funds to a new wallet created on a clean device and reset active login sessions.
This comes amid earlier reports of iPhone users losing crypto to malicious apps.
Security threats don't wait. Neither should your results.
With Shellzero, security findings appear in real time as your website scan progresses.
Every vulnerability. Every severity level. Every detail available the moment it's detected.
No waiting for the final report.
Scan smarter. Stay protected.
https://t.co/essoautLEW
Hackers are evolving, and Web3 security must evolve faster.
From malicious websites to DeFi exploits and money laundering, threats are becoming increasingly sophisticated.
At Shellzero, we believe security should be proactive, not reactive.
Detect threats early. Stay protected. Stay online.
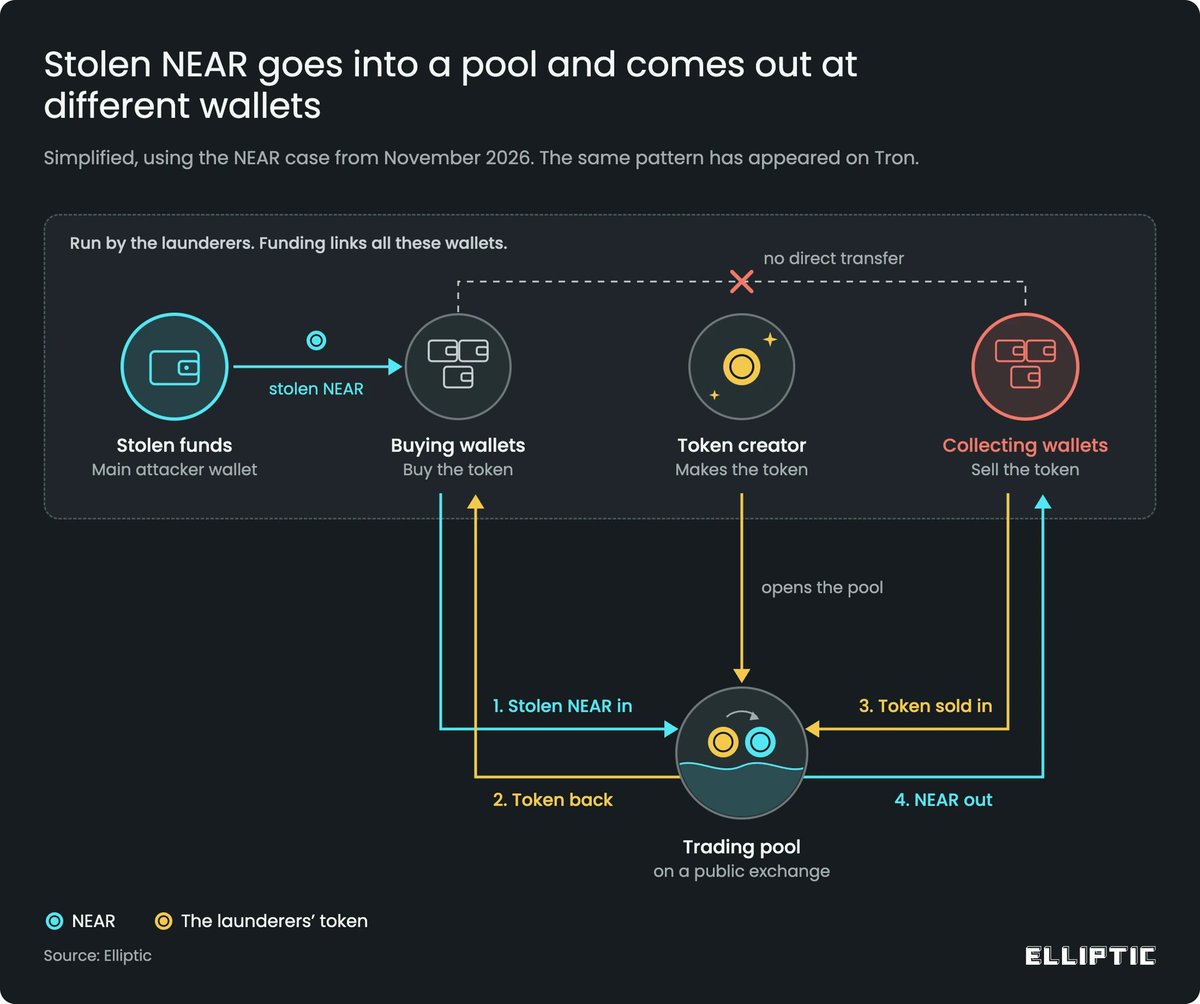
🚨BREAKING: North Korea-linked hackers are using MEMECOINS to launder funds from the $6.4 BILLION Binance hack, Elliptic reports.
Between Nov. 5 and 7, the hackers created at least six memecoins on NEAR, spending about $90 per token to launch them.
They then moved 117,000 NEAR worth about $430,000 through liquidity pools on decentralized exchanges.
Routing funds through those pools can make them harder to trace. Elliptic spotted a similar tactic after the 2025 Bybit hack.
The next wave of cyber threats won't wait for anyone to be ready.
As attacks grow more sophisticated, cybersecurity can no longer be reactive.
ShellZero is building toward a future where security is proactive, intelligent, and always on.
The future of the internet depends on how well we protect it today.
https://t.co/essoautLEW
🚨 THE INTERNET AS YOU KNOW IT HAS 6 MONTHS LEFT.
Remember who told you first.
Look at what hit Asia's money in the past few weeks:
🇲🇾 Malaysia: RM1.985 million (~$489K) allegedly drained from a royal family member's accounts at 2 banks. Then hackers defaced Bank Rakyat's website.
🇸🇬 Singapore: ONE forged letter sent $12.8 million to Cambodia. All of it recovered.
🇹🇼 Taiwan: hackers breached a SinoPac vendor and pulled NT$41.76 million (~$1.27 million) from 419 accounts in ONE day. Customers refunded.
🇰🇷 South Korea: 37 financial firms hit since Sept 30. 473,000 records leaked. ₩1 billion (~$733K) stolen.
🇮🇩 Indonesia: 350,600 cyber threats in 24 hours. 4 every second. 214,000 aimed at banks and finance.
This is only the warm-up.
Now read this. A US think tank just warned about "sovereign agents": AI that runs with no human in control. It could earn money, get paid in crypto, copy itself and fight being shut down.
If it runs on free, open AI models, "no outside authority can stop it at the source."
And governments already cut the internet 19 times from July to September alone.
MY CALL, MONTH BY MONTH:
DECEMBER → AI bots take over the bank raids. Not 37 firms. Hundreds. In days, not weeks.
JANUARY → AI swarms start LIVING on the internet. They pay for their own servers in crypto and copy themselves faster than anyone can delete them.
FEBRUARY → banks and exchanges freeze online transfers for hours at a time. They'll call it "maintenance."
MARCH → the first country cuts its OWN internet to stop a swarm. Not to stop protesters. To stop a machine.
APRIL → no ID, no internet. Every login tied to your name.
MAY → INTERNET LOCKDOWN. Country after country goes dark, and "temporary" becomes the new normal.
When the swarm lives everywhere, governments have one switch left. OFF.
Screenshot this.
TV will call every blackout "maintenance." I'll call it what it is, month by month, so follow me.
Not every certificate authority should be trusted to issue certificates for your domain.
With DNS CAA records, you decide who has permission.
Unauthorized certificate issuance attempts can be blocked before they become a threat.
ShellZeroX checks your CAA configuration during every scan, helping identify potential gaps in your domain's certificate security.
Your domain. Your rules. Your security.
Scan your website: https://t.co/essoautLEW
#ShellZero
A 72-hour emergency kit is essential, but digital preparedness matters just as much.
When critical systems go offline, staying connected and secure becomes a priority.
That's why we're building ShellZero. Resilience should never be optional.
🚨🚨 NOW BRAZIL TOO: KEEP A 72-HOUR EMERGENCY KIT.
325 CITIES ON RED STORM ALERT.
5 OFFICIAL UPDATES IN 5 DAYS:
🇯🇵 2 NOV: 3 DAYS, 1 WEEK IF POSSIBLE
🇹🇭 2 NOV: 72 HOURS
🇮🇸 3 NOV: 3 DAYS
🇪🇺 3 NOV: 72 HOURS
🇧🇷 6 NOV: 72 HOURS
38 COUNTRIES HAVE OFFICIAL ADVICE LIKE THIS: WATER. FOOD. RADIO. CASH. 72 HOURS OR MORE ON YOUR OWN.
🇸🇪🇫🇮🇳🇴🇵🇱🇩🇪🇹🇼🇮🇱 AND 7 MORE NAME WAR OR ARMED CONFLICT IN THEIR GUIDANCE.
ARE YOU READY?
FOLLOW ME BEFORE THE NEXT UPDATE DROPS 🚨
A valid SSL certificate doesn't always mean a secure connection.
The certificate must also match the hostname you're connecting to.
One mismatch. One overlooked warning. One potential security risk.
SHELLZEROX brings critical security checks into focus, helping identify hidden vulnerabilities before they become threats.
Security starts with verification.
Explore: https://t.co/essoautdPo
#SHELLZEROX
In a nuclear conflict, no country is truly immune. Geographic isolation may reduce direct exposure, but fallout, disrupted supply chains, and global communication failures can cross any border.
The real question isn't just where to escape, but how prepared we are.
When the world goes offline, SHELLZERO aims to help you stay connected.
Because in a global crisis, connectivity isn't just convenience. It's survival.
🚨🌍 WORLD WAR III: Where Could You Escape If the World's Nuclear Powers Went to War?
As global tensions rise, a Daily Mail ranking identifies 12 potential refuges from a catastrophic global conflict.
The list includes Fiji, Tuvalu, New Zealand, Indonesia, Iceland, Argentina, Chile, Switzerland, Bhutan, Antarctica, South Africa and Greenland.
Their advantages range from geographic isolation and food security to Switzerland's extensive nuclear shelter network.
Conspicuously absent are the world's major military powers, including the US, Russia, China and Britain.
But even the most remote sanctuary could face nuclear fallout, food shortages and economic collapse.
Source: Daily Mail \ Writer: Naz
Security doesn't end after one scan.
SHELLZERO Sentinel continuously rescans websites, monitors certificate changes, and tracks SSL expiration dates.
Every rescan delivers updated insights. Every certificate has an expiration date.
Sentinel keeps counting.
Stay monitored. Stay protected.
#SHELLZERO
Cyber threats don't wait, and neither should security.
Banks, financial institutions, and crypto wallets are all potential targets.
Real-time threat detection, continuous monitoring, and proactive defense are no longer optional.
SHELLZEROX is building for a safer digital future.
🚨 They tell you to keep your money in the bank because it's safe.
In just 24 hours, Indonesia's banks, finance and insurance firms were hit by 210,000 cyber attacks.
Not in a month. Not in a year. ONE day.
That's almost HALF of the 439,000 attacks blocked across the whole country.
And more than government, tech, transport, telecoms and every other sector on the list COMBINED.
Nationwide, about 5 attacks every second. 24 hours. NONSTOP.
And it's not only Indonesia.
🇲🇾 Malaysia: pages of Bank Rakyat's website were defaced on Friday night. Portals at several Malaysian banks were disrupted. The national cyber agency raised the threat level from LOW to MODERATE.
🇫🇷 France: hackers got into Crédit Mutuel Arkéa through one of its service providers and stole about €100 million from the bank's own account.
Your savings are not sitting in a vault.
They are numbers on a server. And that server is under fire around the clock.
Your bank's app will never show you numbers like these. This account will, every time they jump. Follow me.
Your domain has more doors than you think.
Introducing Subdomain HTTP Probe by SHELLZEROX.
Verify domain ownership via DNS TXT, discover subdomains, and inspect HTTP responses in real time.
Every subdomain. Every response. Clear visibility.
Read-only probing. Verified owners only.
SHELLZEROX Know your attack surface before attackers do.
#SHELLZERO