Two vulnerabilities in Advantech were found by our team during the SPIRITCYBER-24 IoT / OT Hackathon in Singapore: CVE-2025-48466 and CVE-2025-48470.
Our Poc for CVE-2025-48470: https://t.co/87HG6SvHF0
Advisory: https://t.co/T9p64iuJpx
Are bug bounties dead in 2026?
Not even close. @simonkoeck just found an RCE in Google.
A Flask session cookie on https://t.co/qNoDdIoM01 was signed with a secret key, and that same key let him forge a session into deserializing a malicious pickle payload, straight to code execution across Google's dev sites.
Google paid him $90,000.
Bug bounties aren't dead. You just need the mindset to look for angles nobody else has checked yet.
I wrote a full guide on how to start (or come back to) bug bounties in 2026
Link below, plus Simon's write-up. 👇
All my friends in India
Positive Hack Talks soon in Goa
By @PTsecurity_EN / @ptsecurity
For all who interested in cybersecurity talks , amazing talks
Totally completely free
Now you can apply , if you have a nice talk you can apply as well
All from here
https://t.co/MuMxpkmGl9
Or you can chat directly to @amoshkov
#Cybersecurity #bugbounty #infosec #goa
What was that. @rootconorg was straight-up WILD.
That moment when your camera roll has almost nothing that's appropriate to post 😅
See you next year, ROOTCON. SHOT SHOT SHOT!
LET'S GO INDIA! 🇮🇳 #PHTalks is coming back: Goa, Dec 10!
CFP is OPEN: talks, community stand-ups, villages. Grassroots communities are VERY welcome!!
Speakers: travel & stay on us. Entry is free.
Beach resort, chill vibes... and sunset:
https://t.co/9w7laUcpeB
OpenWrt One WB receive-only SDR. MT7981 Wi-Fi radio taps raw 14-bit IQ @ 40 MSps, streams VITA 49 over 2.5GbE to a browser spectrum/waterfall. Flashable release + one-command setup. v0.1
feedback and critique welcome:
https://t.co/zCW8Wuzaid
In a few minutes I will be giving a talk on deobfuscation at the Virus Bulletin conference in Seville. If you are hanging out at #VB2026, come watch it to learn some new things about IDA!
W00t!! It took three attempts and lots of drama, but HaeJung Yang (@haehaeYang) of Out of Bounds (@oobs_io) successfully exploited Dynamo in the AI Infrastructure category. Once they regain their breath, they head off to the disclosure room to provide details. #Pwn2Own
We're hiring an FPGA & embedded engineer to join our hardware team. Can you make a CAN core from scratch in VHDL?
Email [email protected] with cool projects you've built!
The full schedule for #Pwn2Own Ireland 2026 is now live! You can find it at https://t.co/Q0JMHtgIOb. And check out https://t.co/slZjCeq2Jv for live leaderboard updates throughout the day. #P2OIreland
It seems that many Samsung Galaxy S26 & Pixel 10 bugs have been submitted to Pwn2Own this year. There are a lot of Koreans too. Good luck to all participants.
👀👀
Pixel 10 Remote : 3 exploits
Pixel 10 USB : 1 exploit
Samsung Galaxy S26 Remote : 7 exploits
https://t.co/9a3I4ZvBfC
And just like that, twenty is in the books.
For a few days, we filled Clark with hackers, ideas, experiments, questionable decisions, new friendships, old stories, blinking badges, packed rooms, and exactly the kind of chaos we’ve learned to love.
To everyone who came through the doors of ROOTCON 20—thank you.
Whether this was your twentieth ROOTCON or your first, you brought something to the con. You asked questions. You shared knowledge. You met people. You tried something new. You stayed curious. And somewhere between the talks, villages, contests, hallway conversations, parties, and late-night hacking, you became part of this chapter of ROOTCON.
To our Goons: you absolute legends.
Months of preparation became two very long days of moving, fixing, coordinating, improvising, and making sure the show kept going. Much of what you do happens where nobody sees it, and that’s exactly why everything works.
To our speakers, trainers, villages, contest crews, partners, sponsors, and everyone who helped us put this thing together—thank you for trusting us with your time, knowledge, and support.
Twenty editions is a hell of a milestone. But the number isn’t what matters most. It’s the community that somehow keeps finding its way back.
The gear is packed. The halls are quiet again. The con hangover is real.
ROOTCON 20 is over. The community isn’t.
Stay curious. Stay weird. Keep hacking.
We’ll see you on the next one.
ROOTCON ❤️ you!
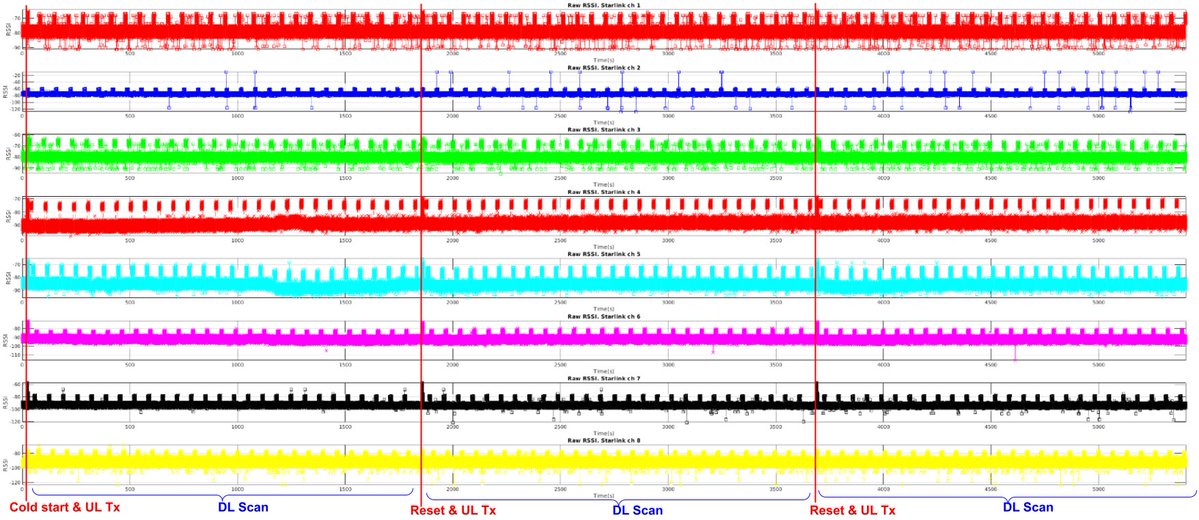
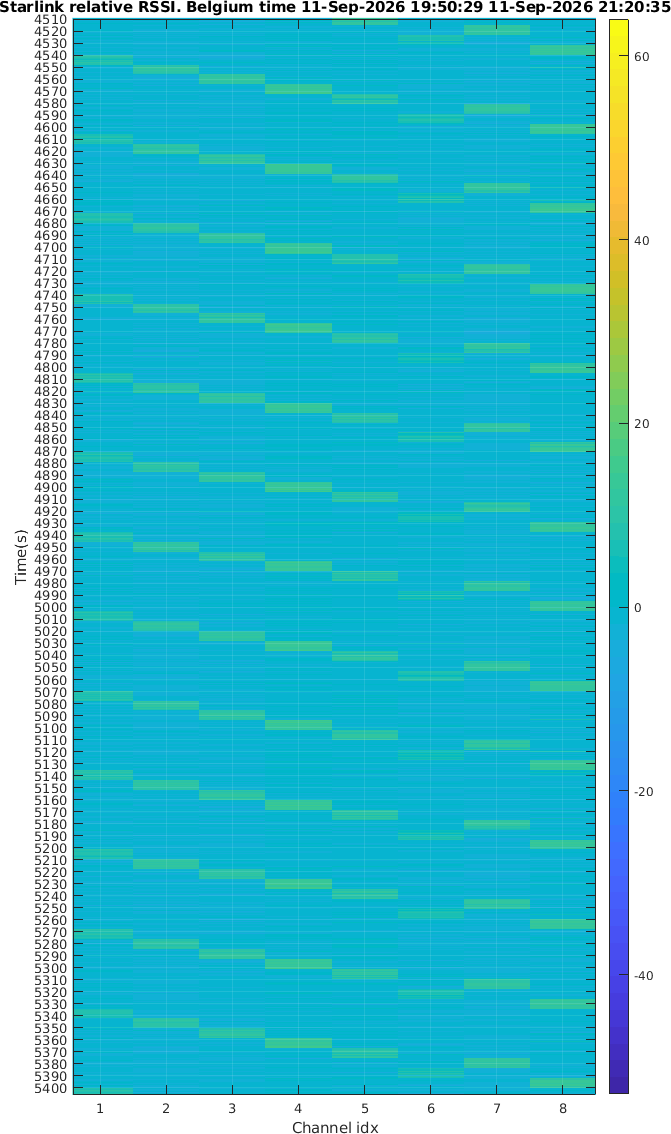
(4) Mysterious Starlink RF signal appears after a “deep cold start” — turn ON after several days OFF. https://t.co/UJG7wJJPPP . Lasts only ~8–10 min across subsequent cold starts, then disappears until another multi-day power-off. It sweeps around carrier, then suddenly vanishes.
If biological brain models can learn through reinforcement learning with dopamine-like rewards, could hackers one day hijack those reward signals to manipulate robot behavior? 🤔
#PhysicalAI#NeuroAI#Drosophila#FruitFlyBrain
With Satellites Blocked, the Starlink Terminal Keeps Searching and Reboots Periodically
https://t.co/cM6EB6pgVQ
It scans 8 DL Ch, dwell 8.26s/Ch, until it rebooted after ~1834s. Then one time 8-channel UL scanning (discovered before), then DL scan again. A fixed firmware timeout?